ghostlock-oppo-watch3pro

Complete exploit research for CVE-2026-43499 (GhostLock) on OPPO Watch 3 Pro, including kernel UAF analysis, disassembly, and exploit chain…

Complete exploit research for CVE-2026-43499 (GhostLock) on OPPO Watch 3 Pro, including kernel UAF analysis, disassembly, and exploit chain…

Analysis and ARM64 reproduction of Copy Fail (CVE-2026-31431)

7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap

Root-cause analysis and reachability PoC for CVE-2026-64747, a buffer overflow in the AppleAVE2 kernel extension. Includes reversed IOKit wire…

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…

Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor

CVE-2026-31431 (Copy Fail) — Análisis y desarrollo en Ensamblador x86-64 | Analysis and development in x86-64 Assembly

Malware analysis from the domain goxlr.net

Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…

Comprehensive reverse engineering and exploitation of CVE-2019-17147, a stack buffer overflow in TP-Link TL-WR841N routers. Includes firmware…

Firmware diff analysis, root-cause writeup, and working PoC for the unauthenticated NetScaler ADC command injection (CVE-2026-88771) leading to root…

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…

Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…

Analysis for stage1 shellcode loader from hacking

Disassembles PE/ELF x86/x64 binaries, resolves indirect branches via GOT, jump tables, and register tracing, and exports the full control flow graph…

Android kernel CVE analysis and PoC for a MediaTek ION allocator type confusion, covering root-cause diffing, unprivileged trigger, and…

Technical research on a UEFI Secure Boot bypass caused by an unsafe custom PE loader, including root-cause analysis, exploitation workflow, and an…

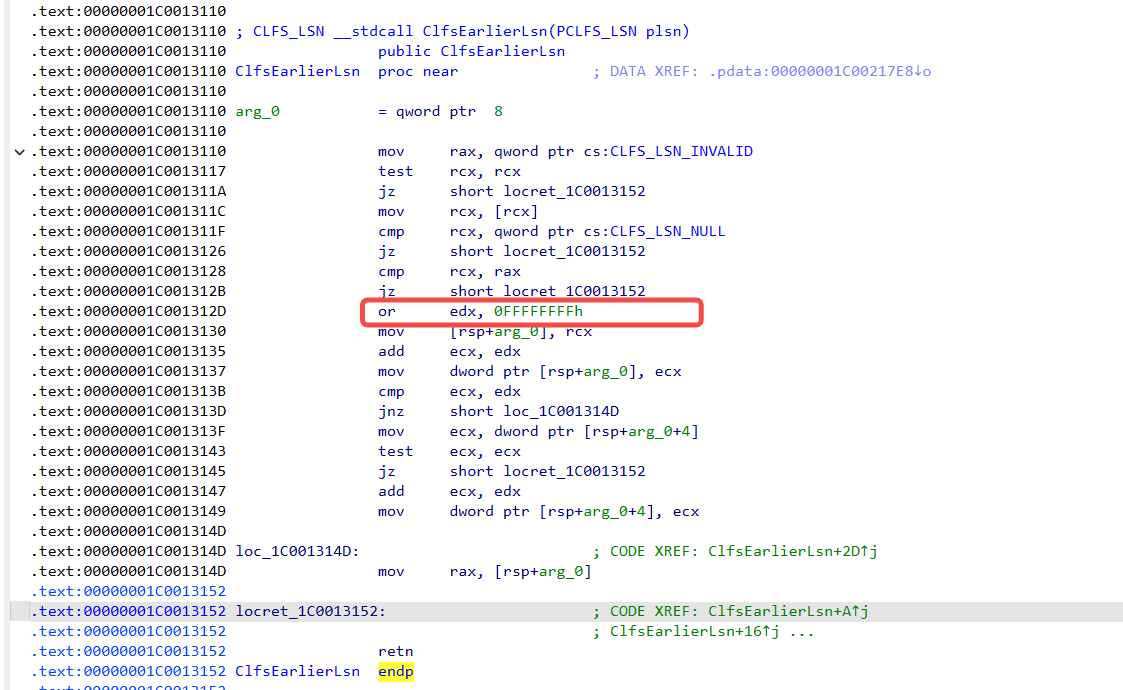
Deep-dive analysis of Windows CLFS type confusion (CVE-2022-24481) with root-cause explanation, exploitation flow, kernel gadget details, and working…