Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
327 results
CVE-2023-6241-Pixel7_Adaptation preview

CVE-2023-6241-Pixel7_Adaptation

GitHubilgobbo00/cve-2023-6241-pixel7_adaptation

Adaptation of CVE-2023-6241 for Google Pixel 7 from Google Pixel 8 taken from securitylab/SecurityExploits/Android/Mali/CVE_2023_6241

android-securitybinary-exploitationdebuggers+5
15

1 year ago
shellcide preview

shellcide

GitHubzer0x64/shellcide

Shellcode IDE

binary-analysisdebuggerseducation+6
154 months ago
Rogue-Framework preview

Rogue-Framework

GitHubthisistfs/rogue-framework

Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…

binary-analysisdebuggersdynamic-analysis-sandboxing+4
211 month ago
om-research preview

om-research

GitHubalkersan/om-research

Documenting Osmo Mobile BLE protocol

bluetooth-securityeducationhardware-iot-security+3
238 months ago
dae preview

dae

GitHubejfkdev/dae

Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…

android-securitybinary-analysisdebuggers+6
1118 days ago
wiremax preview

wiremax

GitHubinfobyte/wiremax

Lua-based Wireshark postdissector that decrypts and parses Ubiquiti AirMAX/RouterBoard 802.11 vendor IEs into filterable fields.

forensicsgeneral-purpose-utilitiesnetwork-security+2
112 months ago
VulnFanatic-NG preview

VulnFanatic-NG

GitHubmartyx00/vulnfanatic-ng

BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.

ai-assisted-reversingbinary-analysiscode-analysis+9
184 months ago
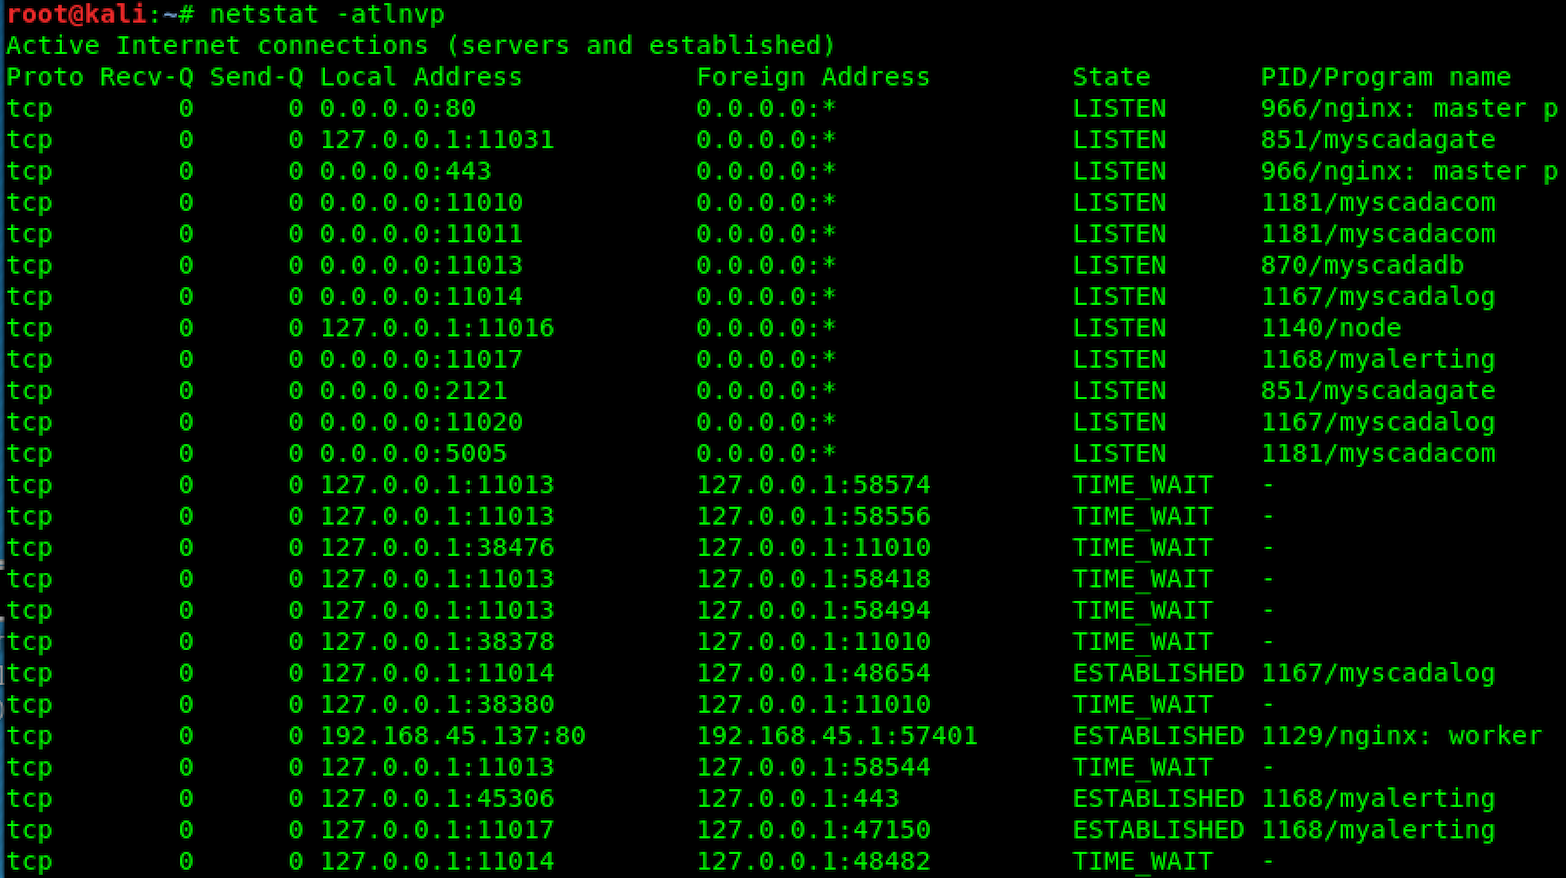
mySCADA-myPRO-7-Hardcoded-FTP-Username-and-Password preview

mySCADA-myPRO-7-Hardcoded-FTP-Username-and-Password

GitHubemreovunc/myscada-mypro-7-hardcoded-ftp-username-and-password

CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability

embedded-systems-securityexploitationhardware-iot-security+4
128 years ago
hermit preview

hermit

GitHubxv4l3x/hermit

Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…

android-securitybinary-analysiscode-analysis+7
68 days ago
apkSneeze preview

apkSneeze

GitHubhumoud/apksneeze

A tool that automates the mundane tasks of pentesting Android apps. It uses APKTool and Dex2Jar.

android-securityinformation-gatheringmobile-app-pentesting+2
116 years ago
POCO-M7-Plus-Jailbreak preview

POCO-M7-Plus-Jailbreak

GitHubaniketlab/poco-m7-plus-jailbreak

Temporary Root Research on Poco M7 Plus (SM6375) via Qualcomm GBL Exploit (CVE-2026-24088) + GhostLock Kernel Analysis (CVE-2026-43499)

android-securitybinary-exploitationeducation+7
313 days ago
sc2elf preview

sc2elf

GitHubdump-guy/sc2elf

Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF

binary-analysismalware-analysisreverse-engineering+1
103 years ago
GZDoom-Arbitrary-Code-Execution-via-ZScript-PoC preview

GZDoom-Arbitrary-Code-Execution-via-ZScript-PoC

GitHubchainmanner/gzdoom-arbitrary-code-execution-via-zscript-poc

Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.

binary-exploitationeducationexploitation+5
131 year ago
KeyPatchX preview

KeyPatchX

GitHubgmh5225/keypatchx

KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…

binary-analysisbinary-exploitationdebuggers+4
97 months ago
linux-root-kit preview

linux-root-kit

GitHubic3-512/linux-root-kit

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…

command-and-controldigital-forensicseducation+8
101 year ago
cve-2026-1668-poc preview

cve-2026-1668-poc

GitHubwuyou6956-glitch/cve-2026-1668-poc

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

binary-exploitationembedded-systems-securityexploitation+6
22 days ago
mauidll preview

mauidll

GitHubbishopfox/mauidll

Extract the managed (.NET) assemblies out of a MAUI Android assembly store.

android-securitybinary-analysisdynamic-code-analysis+4
228 days ago
N0xis preview

N0xis

GitHubstructio-labs/n0xis

AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).

ai-assisted-reversingbinary-analysisbinary-exploitation+7
27 days ago
Previous1…151617…19Next