

 downwithup/cve-2018-16711
PoC code for CVE-2018-16711 (exploit by wrmsr)
 wzhdgithub/ghostlock
CVE-2026-43499 futex PI stack UAF ???????? - Android GKI 6.1~6.12 ??????? pselect() + futex PI ????????????,??? root ??? SELinux??? OPPO Find…
 wadingporque/apkprobe
APK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…
 diyiqiuye/ghostlock-pfem10
GhostLock (CVE-2026-43499) for OPPO Find X5 Pro (PFEM10) — OPlus watchdog & heap-spray detector reverse engineering
 r3n3r0/cve-2026-27280
In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 australeo/cve-2021-28476
Proof-of-concept for CVE-2021-28476, a Hyper-V vmswitch.sys arbitrary pointer dereference allowing guest-to-host denial-of-service and potential RCE.
 fusiondrive/cve-2026-43499-a36
Standalone CVE-2026-43499 port for Galaxy A36 5G SM-A366W A366WVLS3AYG1 with KernelSU late-load
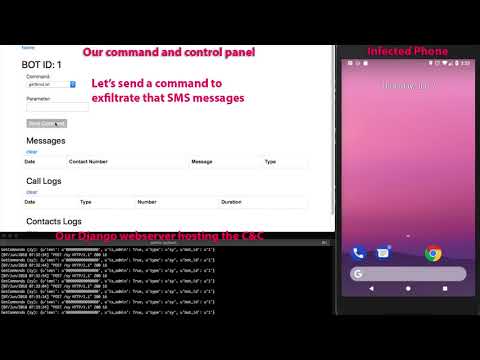 bizdak/silverboxcc
Reverse engineered android malware, and this is a C&C server for it
 crackercat/rootsmart-v2.0
Android Ransomware Development - AES256 encryption + CVE-2019-2215 (reverse root shell) + Data Exfiltration
 pealeap/cve-2026-21045_and_cve-2026-21048
Generates crafted TIFF/DNG files to trigger out-of-bounds writes in Samsung's libimagecodec.quram.so, including binary analysis and reproduction…
 catxiaoshi/cve-2026-43499
PD2229B的43499(ghostlock)可行性研究
 murf-xd/cve-2023-20768
Android kernel CVE analysis and PoC for a MediaTek ION allocator type confusion, covering root-cause diffing, unprivileged trigger, and…
 acloudinthebluesky/cve-2019-6447-es-file-explorer
Technical analysis and safety-conscious research harness for CVE-2019-6447 in ES File Explorer for Android
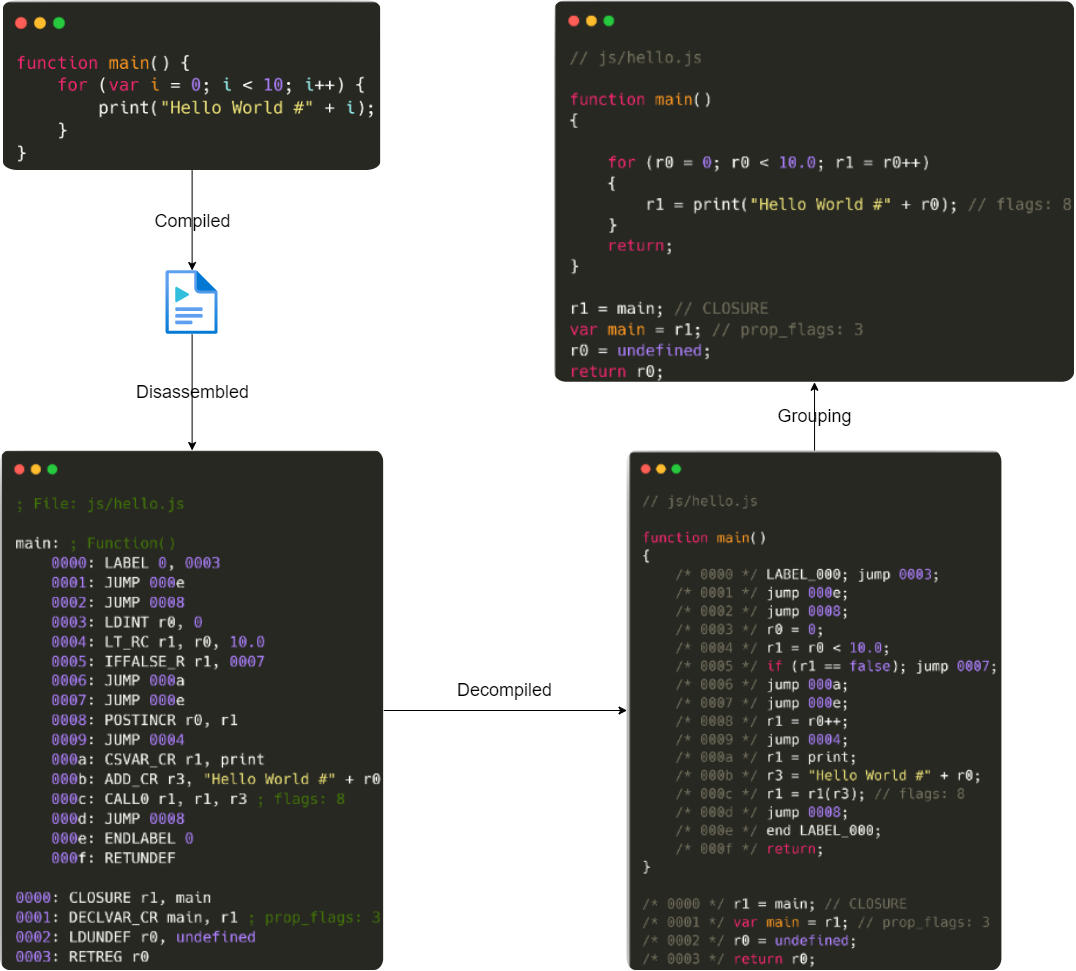 nccgroup/detaped
Detaped is a Python disassembler and decompiler for Duktape. The intended use is for source code review and analysis in situations where you only…
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
 pealeap/cve-2026-21018
Minimal PoC for a Samsung SveService buffer overflow, demonstrating an out-of-bounds write via Binder to crash the Android system service without…