

Process-Dump
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k7 days ago
glmcdona/process-dumpWindows tool for dumping malware PE files from memory back to disk for analysis.
 google/bindiff
Quickly find differences and similarities in disassembled code
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 caoweiquan322/notenough
This tool calculates tricky canonical huffman histogram for CVE-2023-4863.
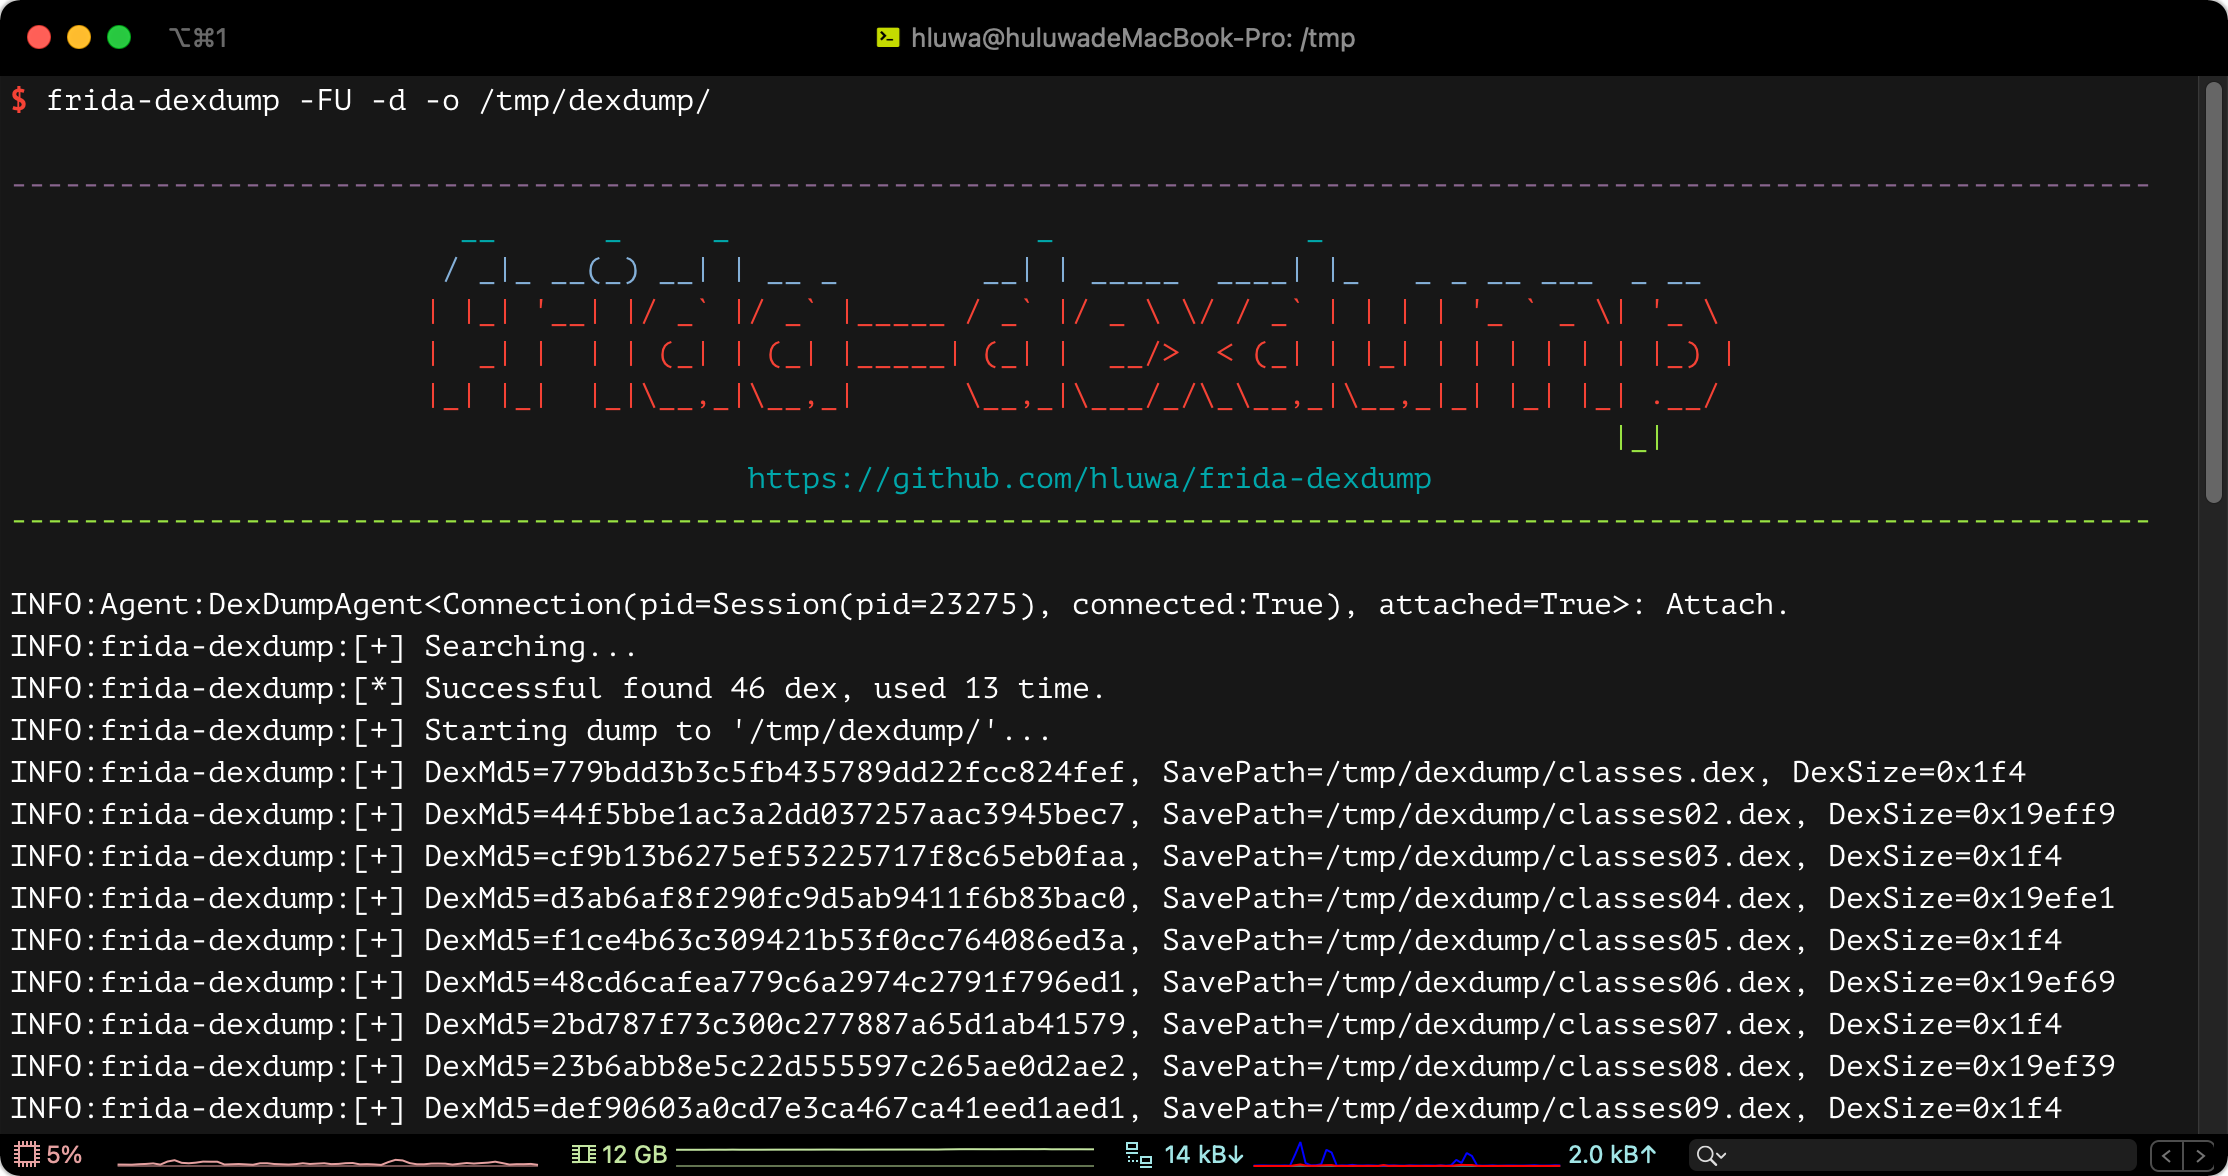 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.