
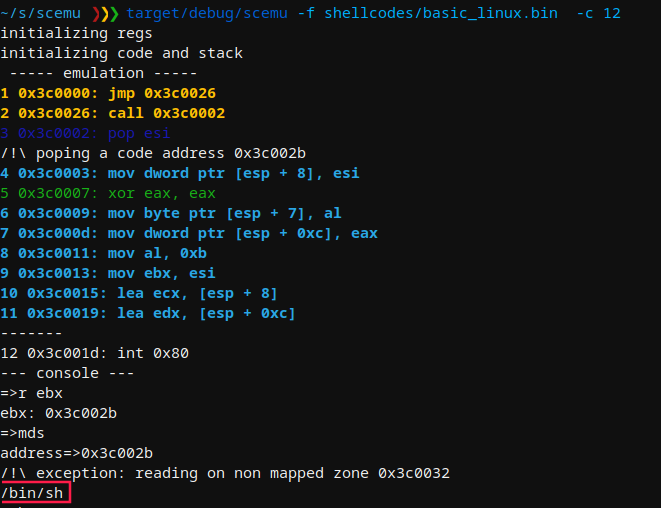
mwemu
 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
binary-analysisexploit-frameworksmalware-analysis+2
315
mwemuorg/mwemuPure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
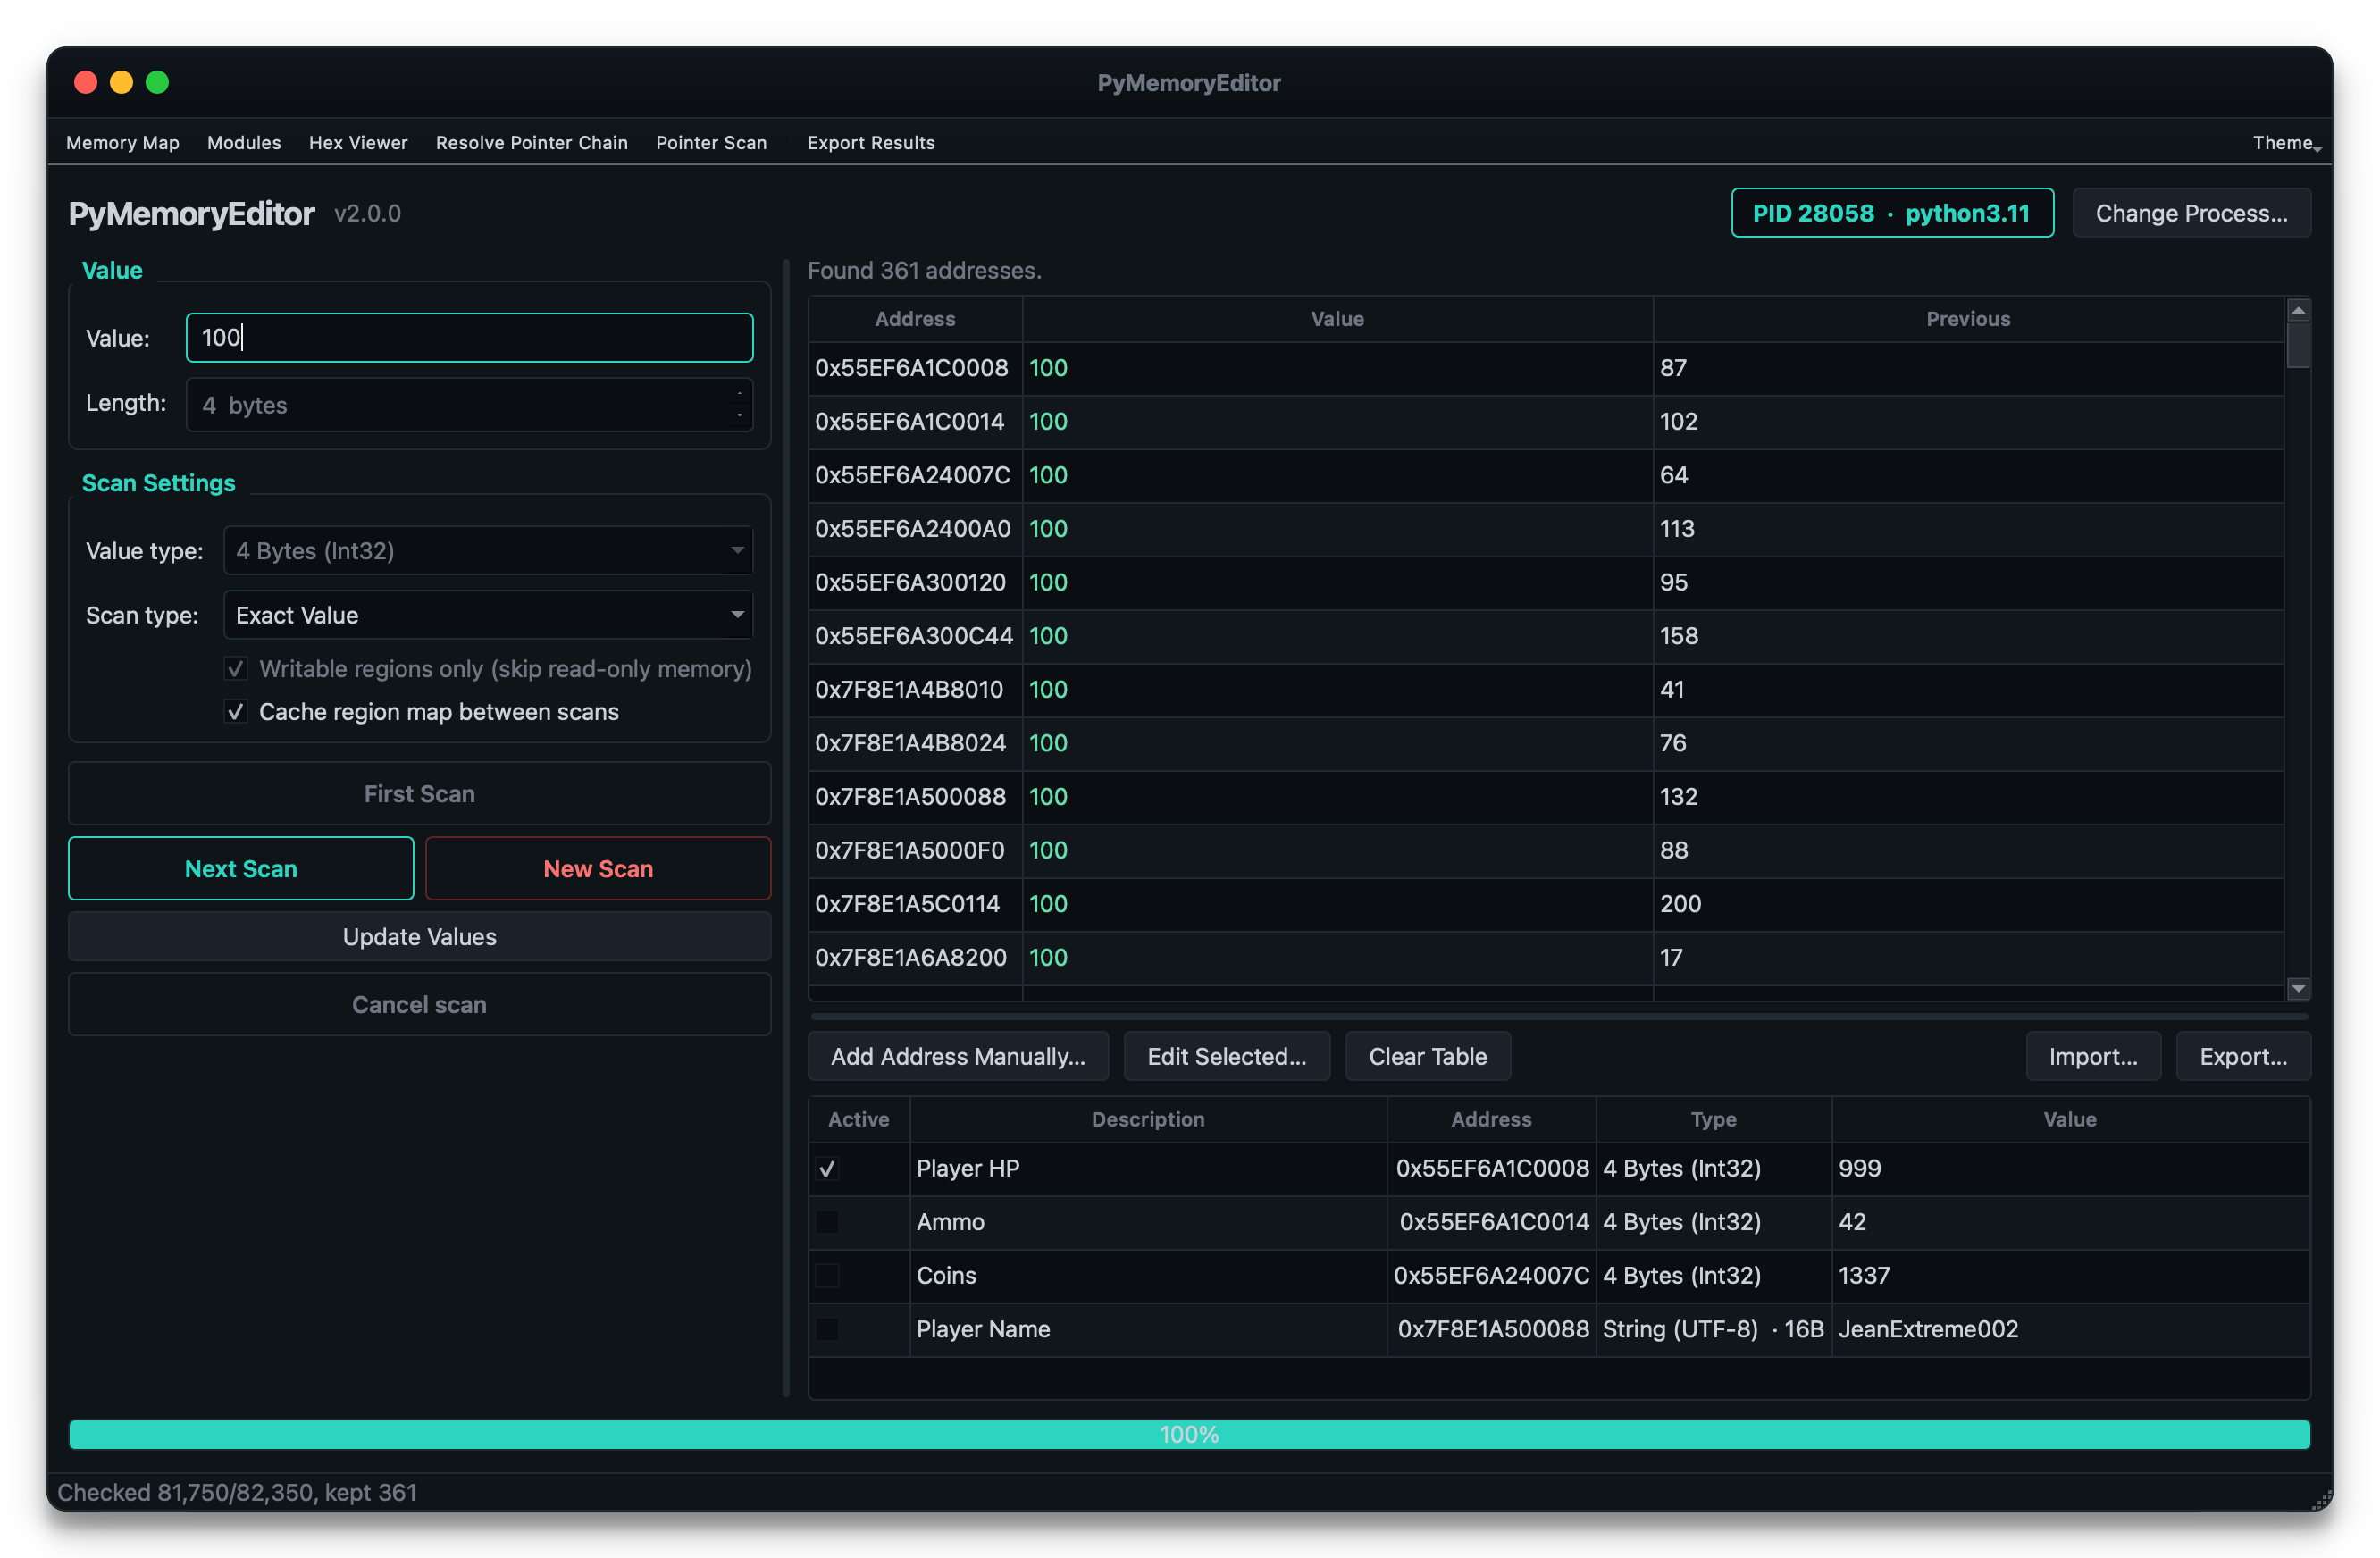 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 securing/iossecuritysuite
iOS platform security & anti-tampering Swift library
 airbus-cert/etl-parser
Event Trace Log file parser in pure Python
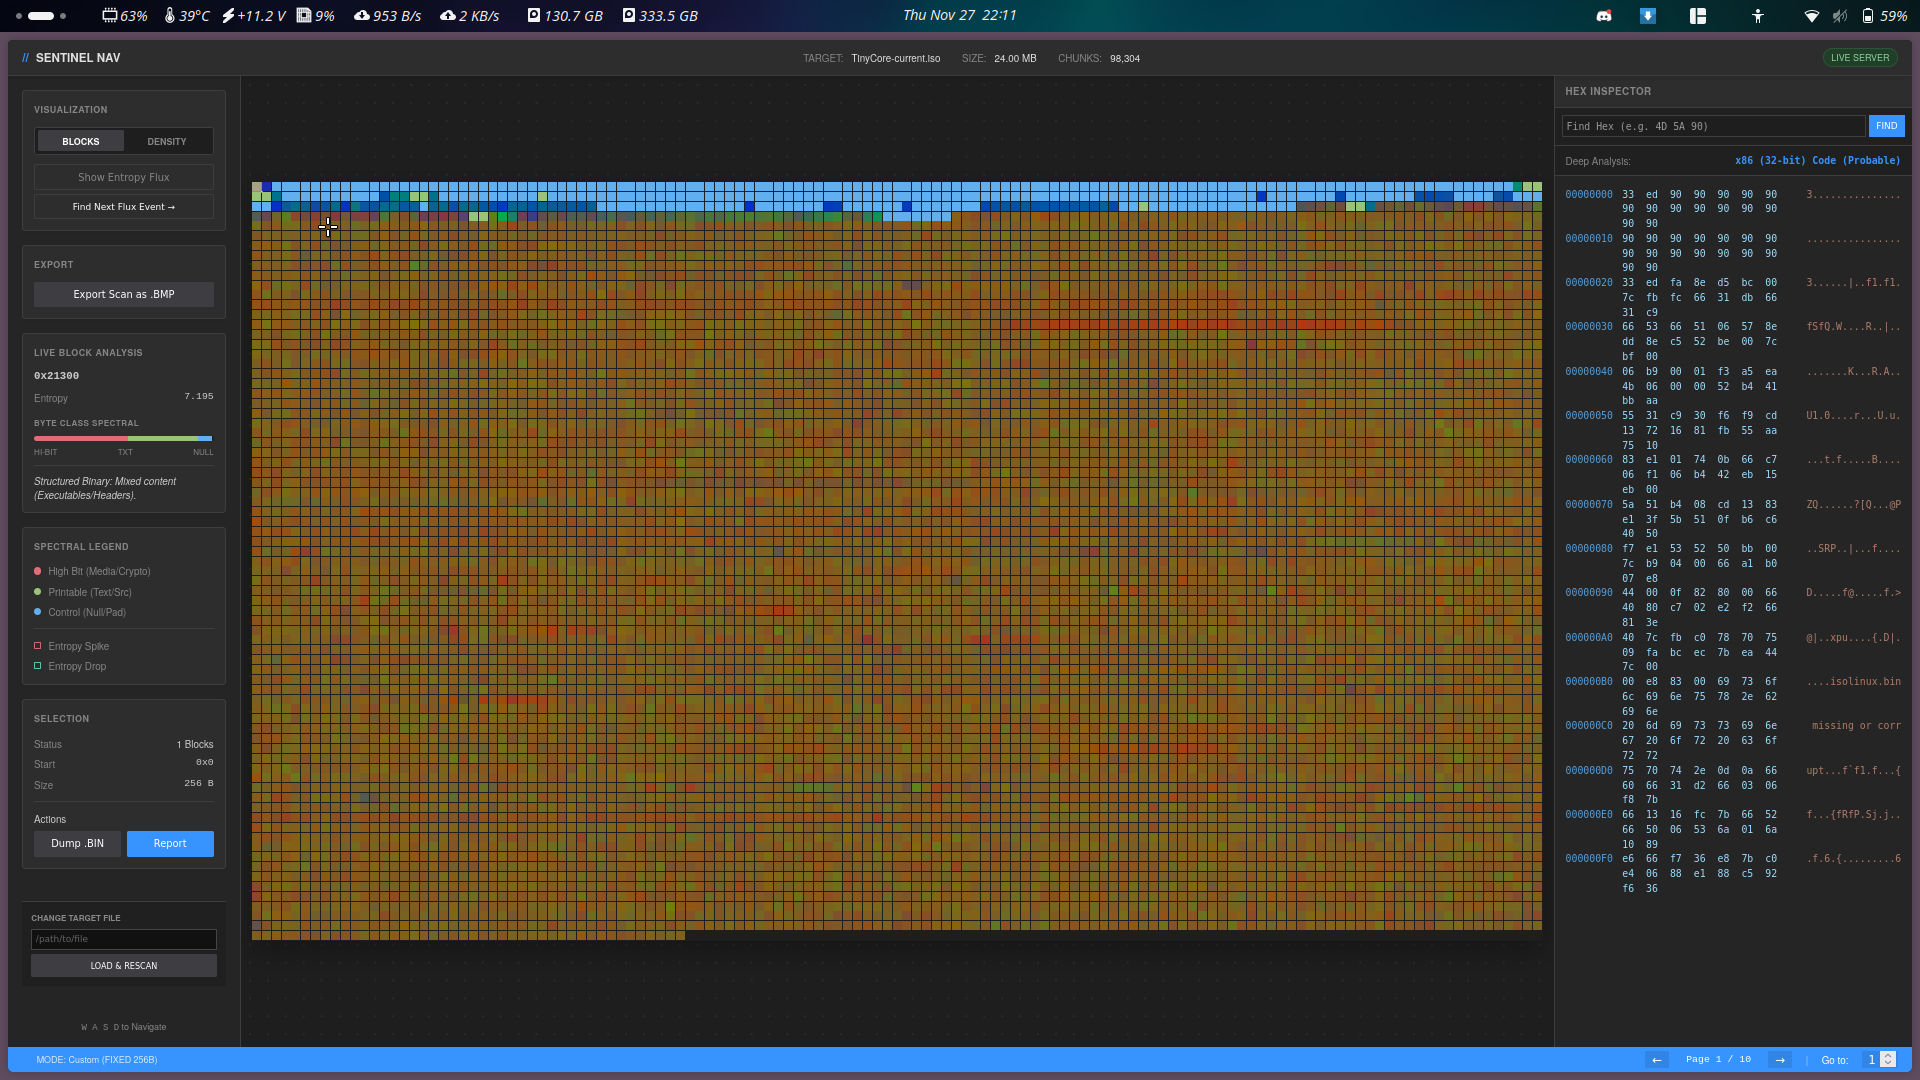 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
 flopz-project/flopz
Pure Python assembler toolkit for creating shellcode, dynamically patching binaries, and instrumenting firmware images for debugging and fuzzing on…
 jonathansalwan/vmprotect-devirtualization
Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.
 nccgroup/pythia
A tool to extract RTTI information from Delphi executables, written in pure Python