Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
108 results
Detect-It-Easy preview

Detect-It-Easy

GitHubhorsicq/detect-it-easy

Program for determining types of files for Windows, Linux and MacOS.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.6k
18h 19m ago
unblob preview

unblob

GitHubonekey-sec/unblob

Extract files from any kind of container formats
binary-analysisdata-recoveryembedded-systems-security+3
2.6k2 days ago
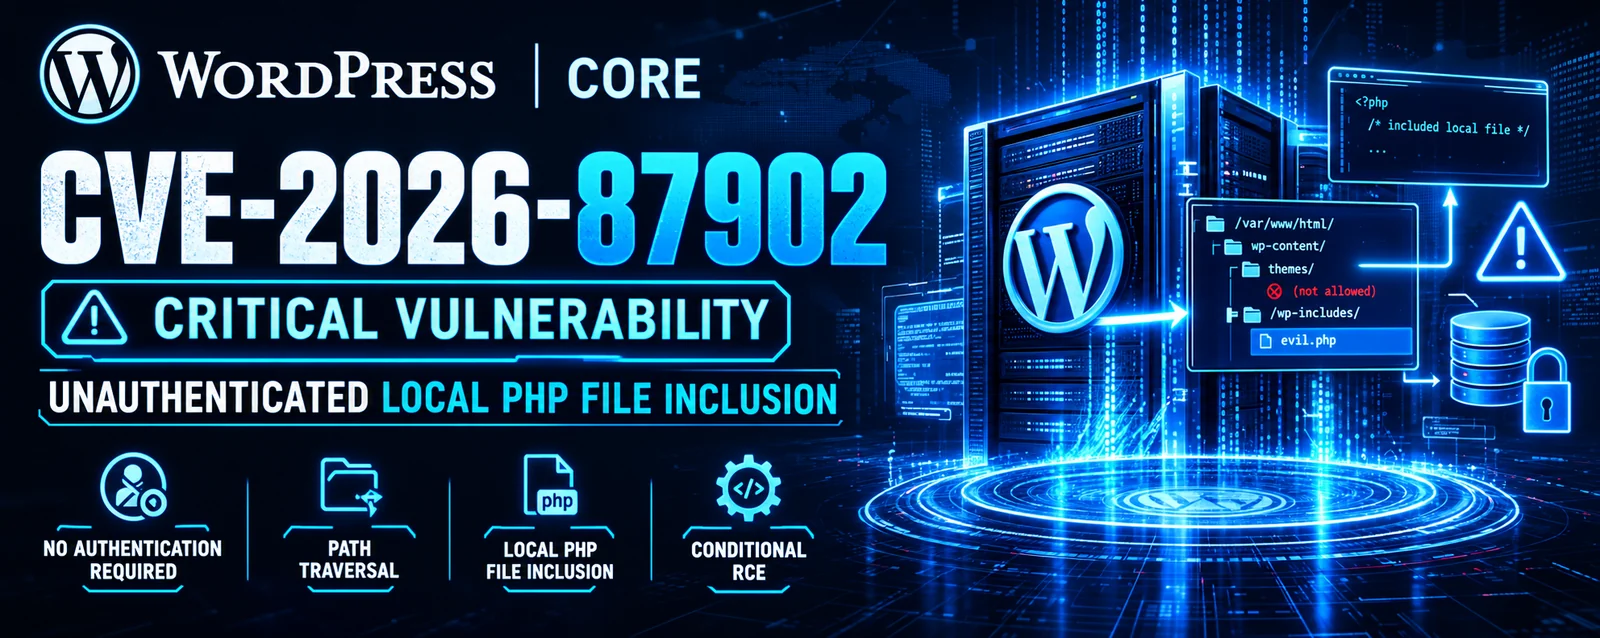
CVE-2026-87902-Toolkit preview

CVE-2026-87902-Toolkit

GitHubtc4dy/cve-2026-87902-toolkit

WordPress CVE-2026-87902 LFI-to-RCE toolkit with a weaponized exploit chain (PEAR RCE, webshell, admin creation, loot) and a non-intrusive…

defensive-toolseducationexploitation+8
12 days ago
ImHex preview

ImHex

GitHubwerwolv/imhex

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

ai-assisted-reversingbinary-analysisbinary-exploitation+10
54.9k3 days ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…

binary-analysiscommand-and-controldefensive-tools+6
5 days ago
CVE-2026-28609-matroska-pcm-oob preview

CVE-2026-28609-matroska-pcm-oob

GitHubdevrodt2/cve-2026-28609-matroska-pcm-oob

Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
android-securitybinary-exploitationexploitation+5
5 days ago
rhabdomancer preview

rhabdomancer

GitHub0xdea/rhabdomancer

Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
binary-analysisreverse-engineeringstatic-analysis+1
1356 days ago
XPEViewer preview

XPEViewer

GitHubhorsicq/xpeviewer

PE file viewer/editor for Windows, Linux and MacOS.
binary-analysisreverse-engineeringstatic-analysis
1.2k6 days ago
MemProcFS preview

MemProcFS

GitHubufrisk/memprocfs

MemProcFS

digital-forensicsforensicshardware-security+5
4.4k11 days ago
NtTrace preview

NtTrace

GitHubrogerorr/nttrace

An strace-like program for the Windows 'native' API
api-security-testingdebuggersdynamic-code-analysis+2
39012 days ago
HexWalk preview

HexWalk

GitHubgcarmix/hexwalk

Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
binary-analysisdata-recoverydebuggers+7
1.0k13 days ago
jadx-magic-strings preview

jadx-magic-strings

GitHub0rshemesh/jadx-magic-strings

JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.

android-securitybinary-analysiscode-analysis+5
4417 days ago
Sandroid_Dexray-Intercept preview

Sandroid_Dexray-Intercept

GitHubfkie-cad/sandroid_dexray-intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

android-securitycryptographydynamic-analysis-sandboxing+8
918 days ago
vxlang-page preview

vxlang-page

GitHubvxlang/vxlang-page

Code obfuscation, virtualization, and anti-tamper protector for x86-64 Windows binaries (EXE/DLL/SYS) and .NET modules, with beta ELF support.…
reverse-engineering
77523 days ago
CVE-2026-27280 preview

CVE-2026-27280

GitHubr3n3r0/cve-2026-27280

In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
android-securitybinary-exploitationexploitation+5
129 days ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
binary-analysisdata-recoverydigital-forensics+8
431 month ago
quokka preview

quokka

GitHubquarkslab/quokka

Quokka: A Fast and Accurate Binary Exporter
binary-analysiscode-analysisreverse-engineering+2
2271 month ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.

binary-analysisdata-recoveryforensics+3
1321 month ago
Previous123456Next