
SigLens
 st0rn/siglens
Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
binary-analysisdefensive-toolsdigital-forensics+7
40
st0rn/siglensWindows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 hasherezade/mal_unpack
Dynamic unpacker based on PE-sieve
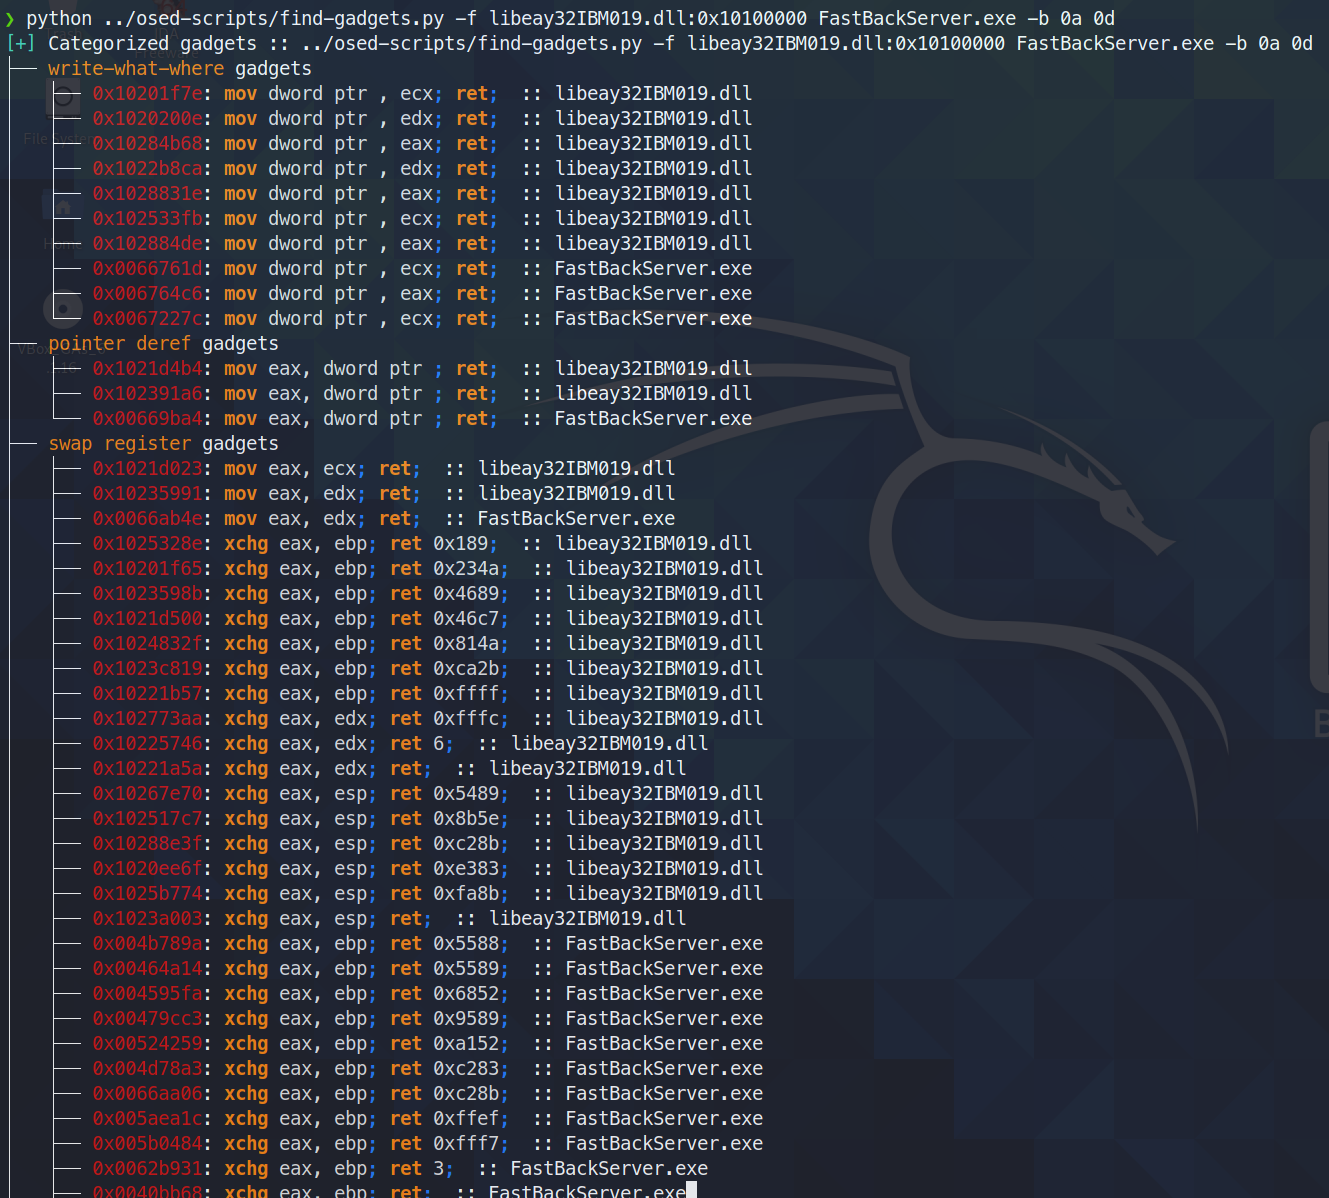 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 nccgroup/libmempool
Heap analysis tooling for mempool
 nccgroup/susanrtti
Another RTTI Parsing IDA plugin
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 iamescri/cve-2025-5548-freefloat-ftp-buffer-overflow
Laboratorio de análisis y explotación de la vulnerabilidad CVE-2025-5548 en FreeFloat FTP Server 1.0
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
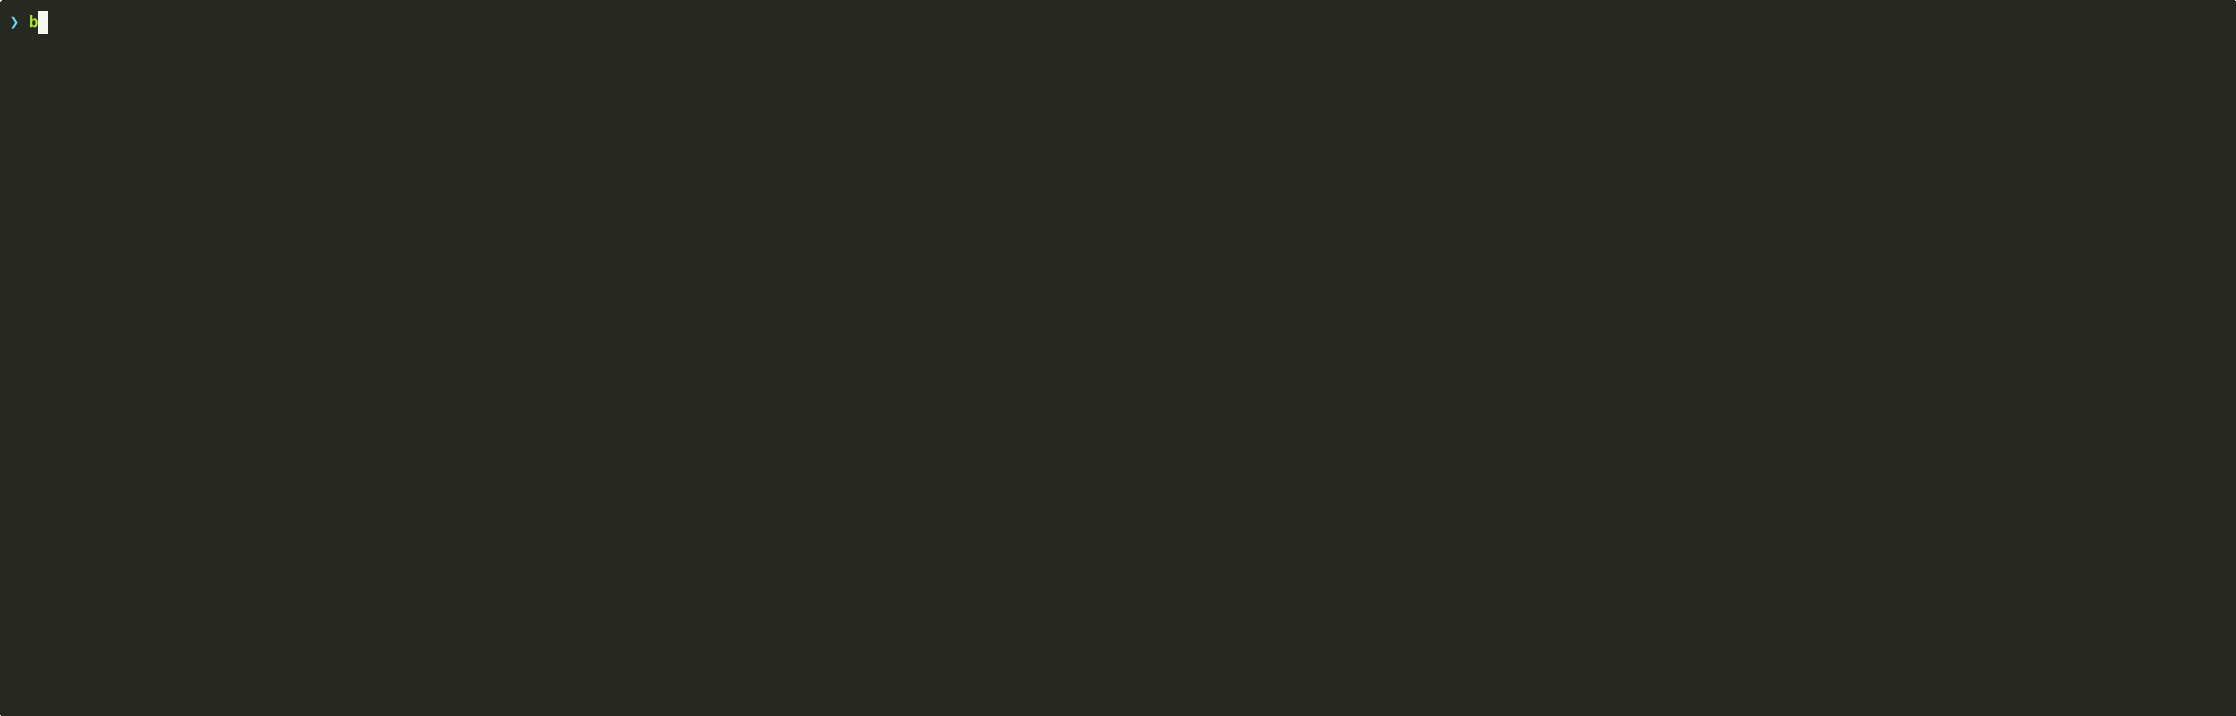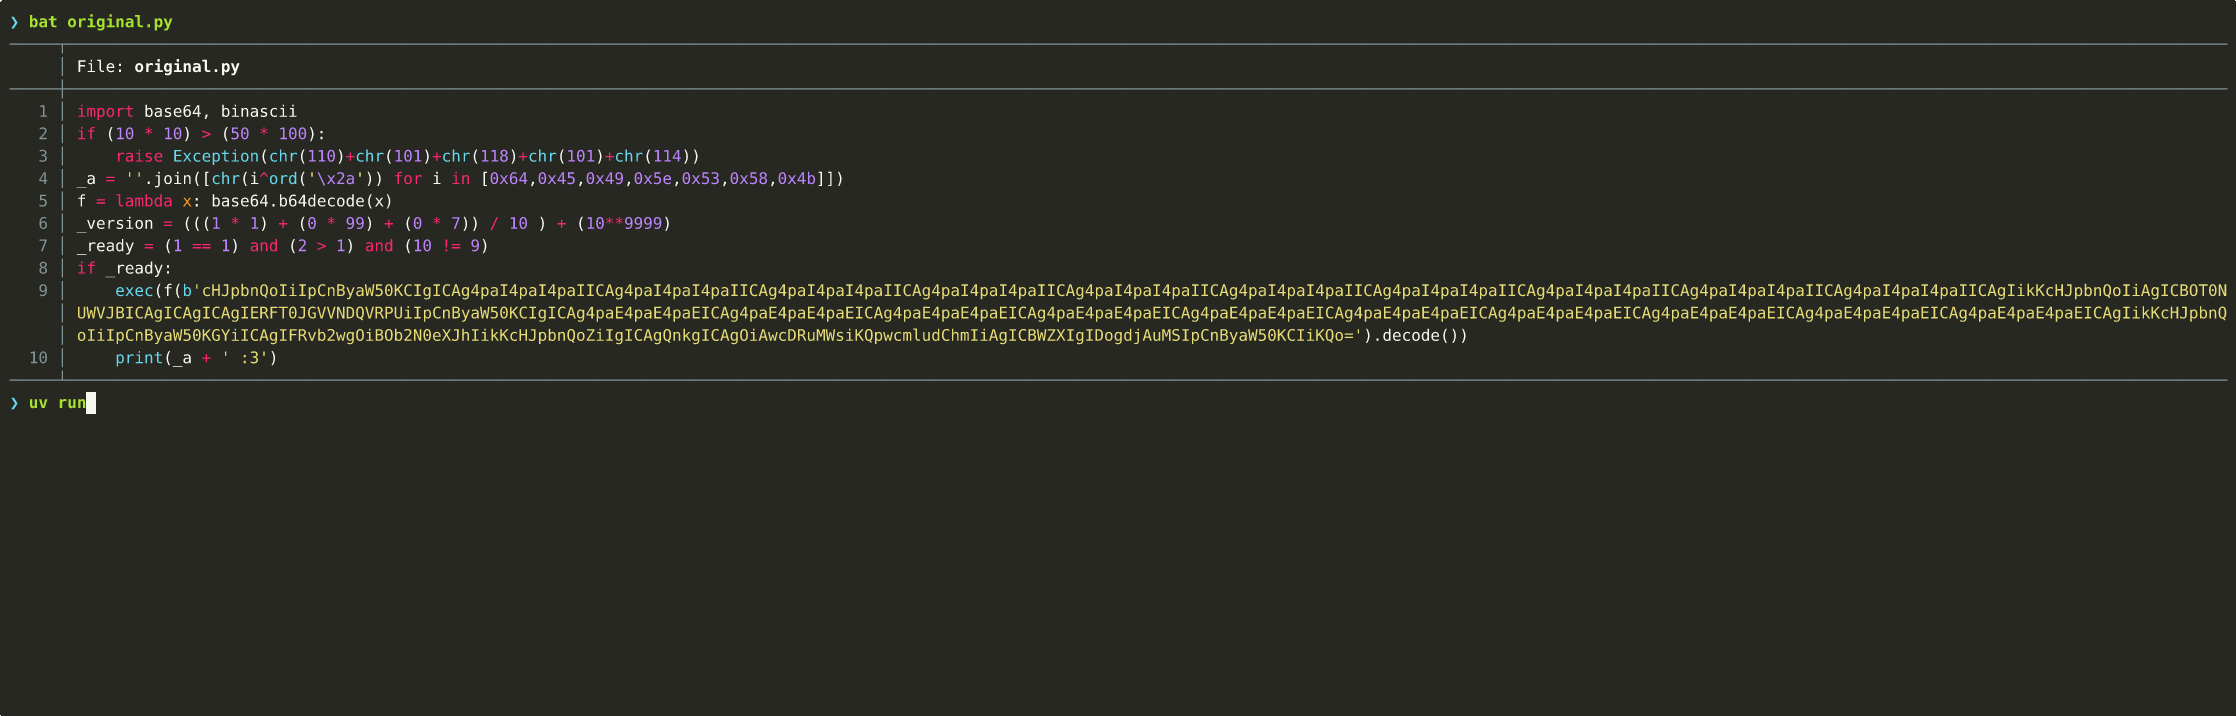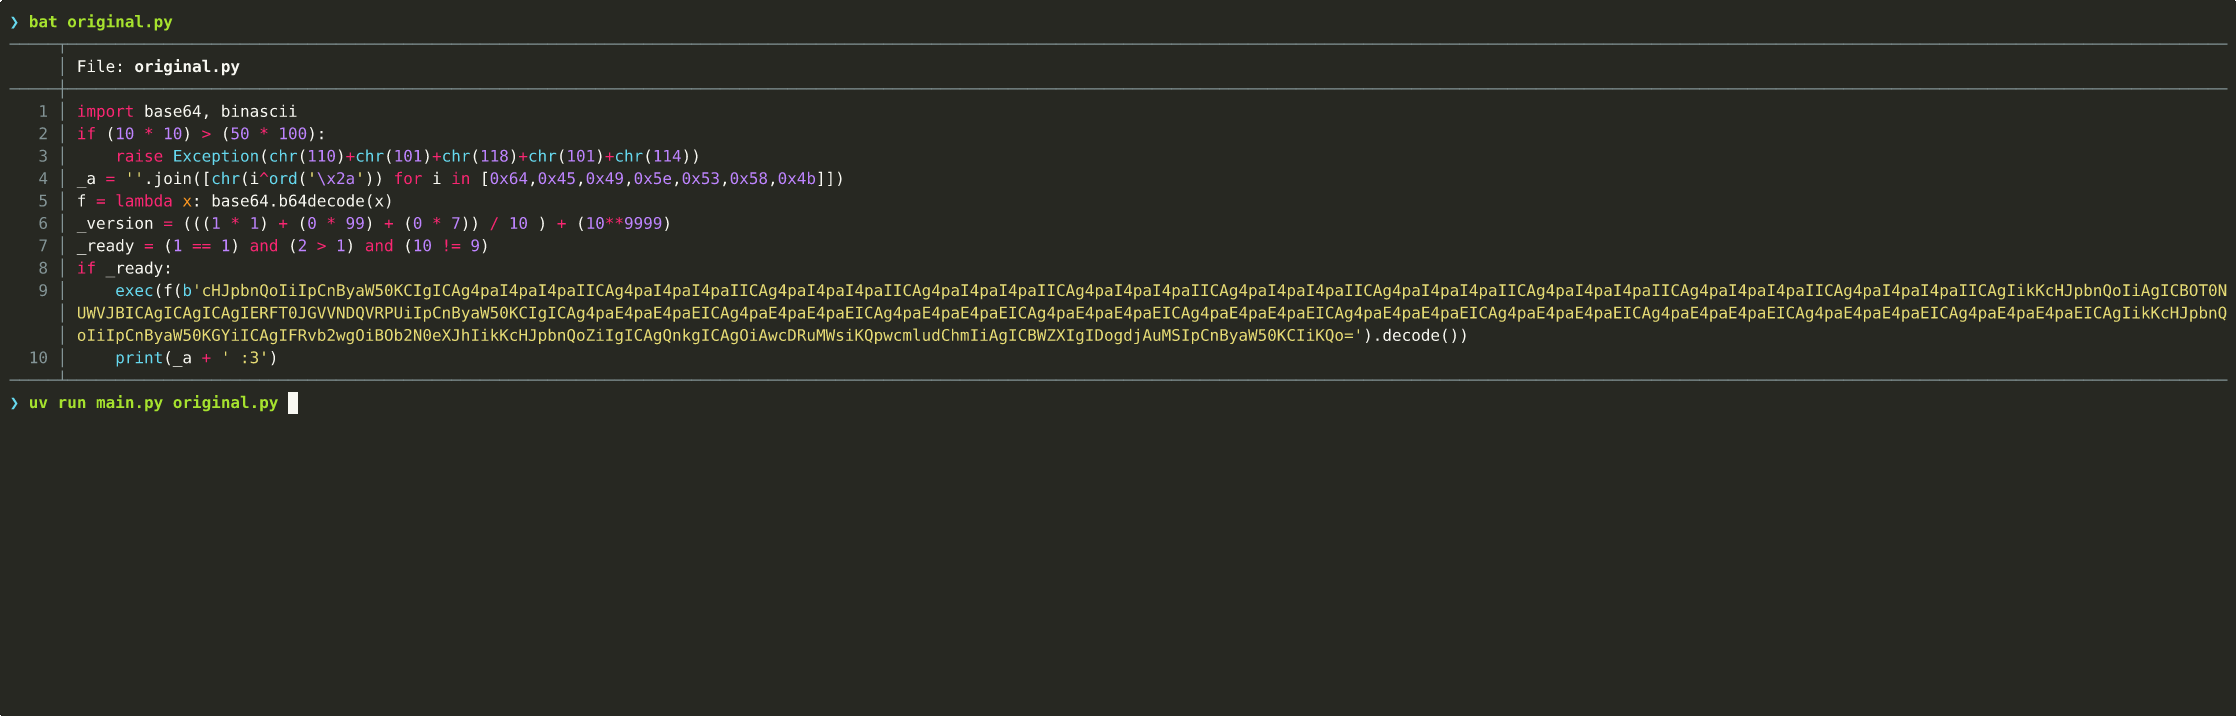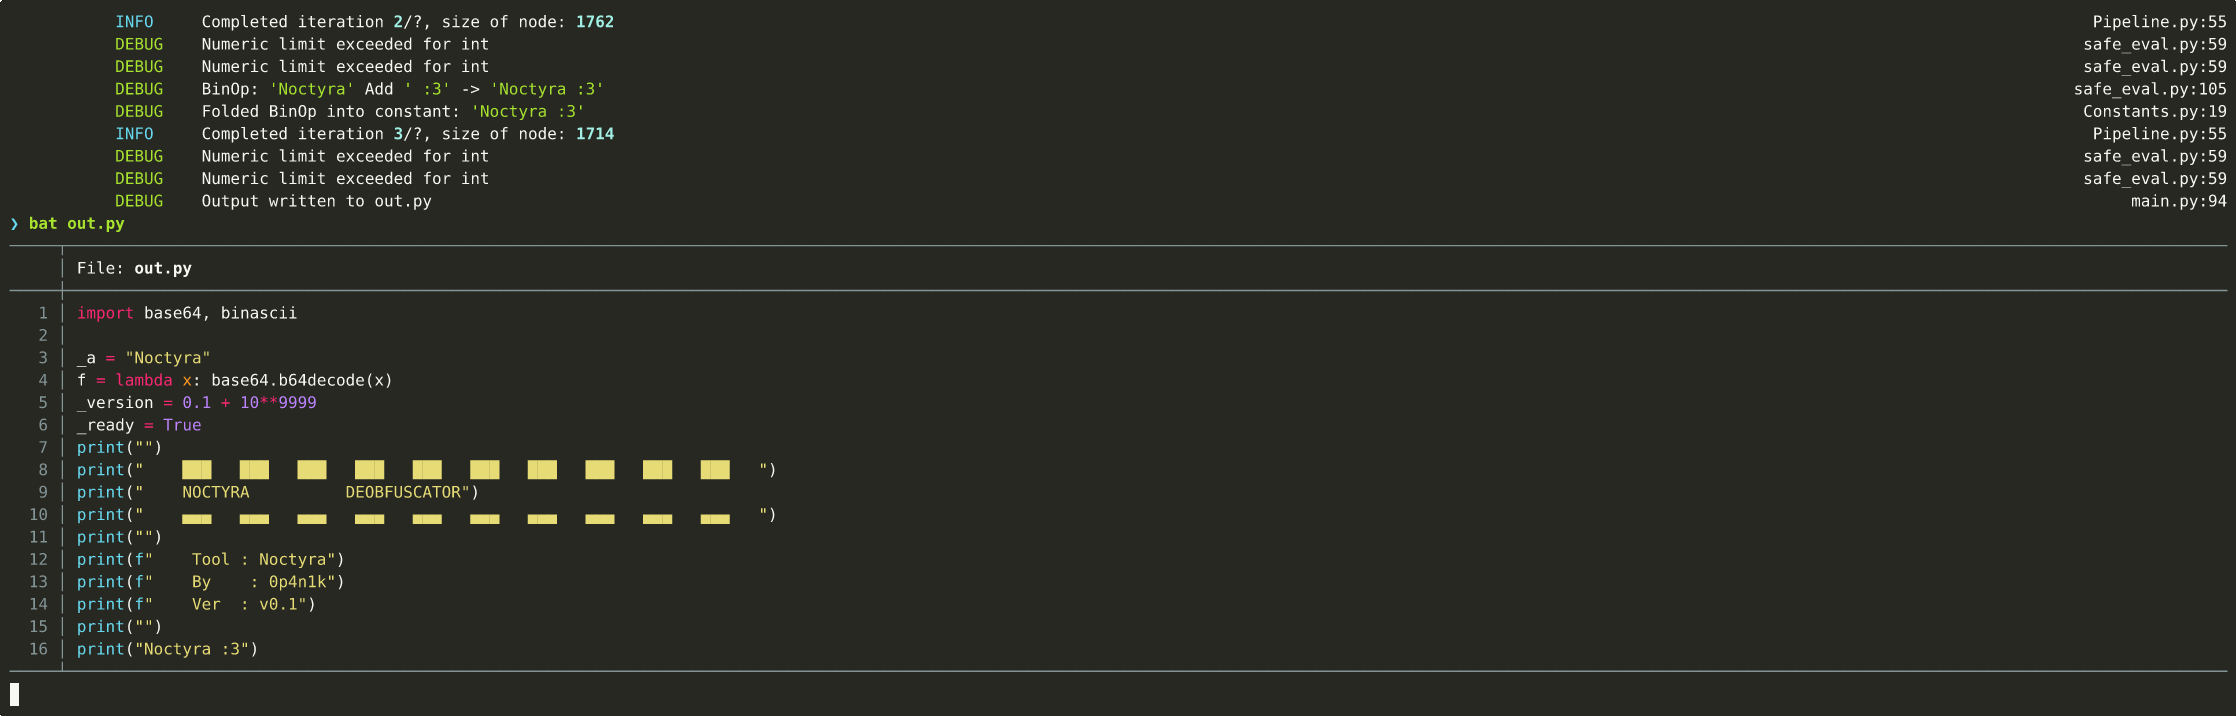 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 gabemarshall/brosec
Brosec - An interactive reference tool to help security professionals utilize useful payloads and commands.
 joxeankoret/cosa-nostra
Cosa Nostra, a FOSS graph based malware clusterization toolkit.
 cs01/gdbgui
Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…