

KnockGiga
 mein-0/knockgiga
Proof-of-concept local privilege escalation exploiting Gigabyte gdrv3.sys IOCTLs to write the SYSTEM token into a user process via an unchecked…
binary-exploitationexploitationhardware-security+3
3
mein-0/knockgigaProof-of-concept local privilege escalation exploiting Gigabyte gdrv3.sys IOCTLs to write the SYSTEM token into a user process via an unchecked…
 not-matthias/amd_hypervisor
Rust AMD SVM hypervisor framework with customizable vmexit handlers (MSR, CPUID, RDTSC) and NPT hooking for kernel-level monitoring and research.
 valium007/cve-2026-56129
Proof-of-concept exploiting the Toshiba qiomem.sys driver to achieve arbitrary physical memory read/write from ring 3, with a companion writeup.
 wqsv/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 themalwareguardian/cve-2026-79298
Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…
 sunnypatell/basalt
World's first hazard checker for NVIDIA Blackwell (sm_120), with an assembler and scheduler matched against their own compiler byte for byte. The…
 ggfuchsi-oss/lg-webos-kexec
Boots a custom Linux kernel on rooted LG webOS TVs via kexec, with reverse-engineered SoC watchdog support, framebuffer payloads, and an initramfs…
 gmh5225/anti_suspend
Protect process by shellcode
 xoreaxeaxeax/skitter-creek-bath-salts
Unlocking _everything_ on the CPU with DRAM scrambling
 xoreaxeaxeax/mmiotic
Latency x-ray for undocumented hardware
 tobss8/gigabyte-h510m-k-v2-bios-smm-reverse-engineering-cve-2025-7026-7027-7028-7029-research
Static reverse-engineering of a GIGABYTE H510M K V2 (`H510MKV2.F3`) BIOS image: full UEFI firmware-volume extraction analysis of the PI-spec SMM Core…
 chip-red-pill/microcodedecryptor
Decrypts Intel Atom microcode updates and unpacks XuCode with recovered RC4 keys, revealing internal CPU microcode structures for hardware security…
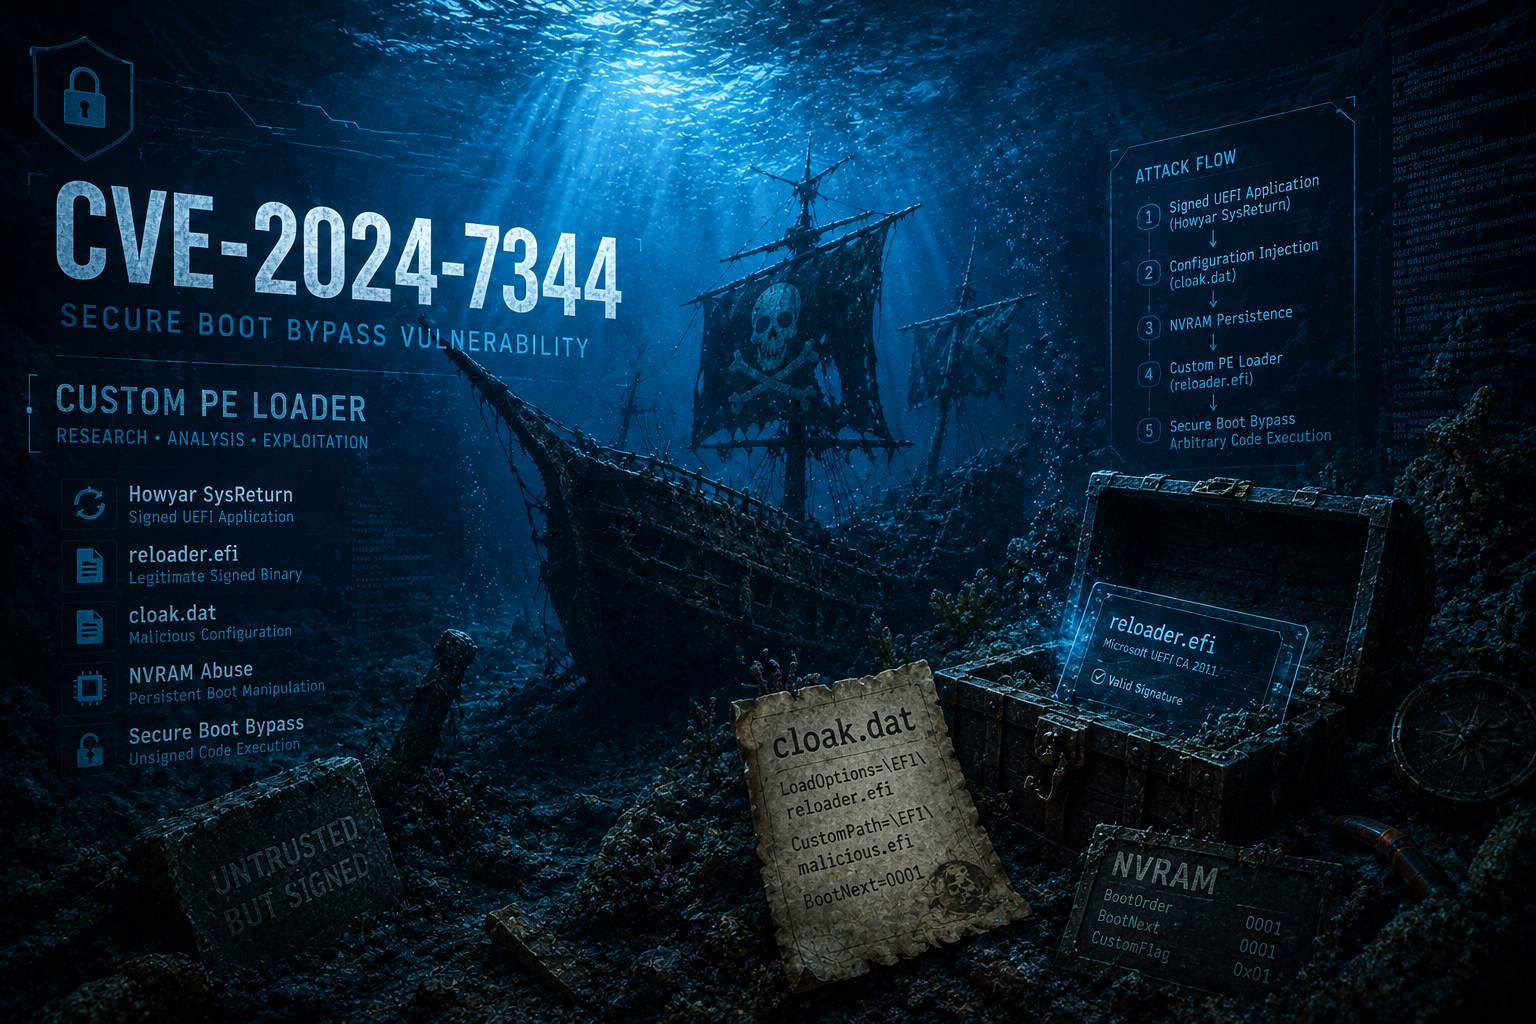 themalwareguardian/cve-2024-7344
Technical research on a UEFI Secure Boot bypass caused by an unsafe custom PE loader, including root-cause analysis, exploitation workflow, and an…
 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…