

ablation
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
ai-assisted-reversingandroid-securitybinary-analysis+7
66
ablation-tool/ablationReverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
 eddinos2/cve-2026-64747
Root-cause analysis and reachability PoC for CVE-2026-64747, a buffer overflow in the AppleAVE2 kernel extension. Includes reversed IOKit wire…
 amorcool/ios26.6-cve-2026-65343
CVE-2026-65343 PoC — AppleKeyStore OOB read → KASLR defeat (iOS 26.6 / 23G71)
 kaleth4/cve-2026-4747-
Remote kernel exploit for FreeBSD CVE-2026-4747, leveraging a stack buffer overflow in kgssapi.ko to achieve RCE with a reverse shell. Includes…
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 233laoliu/mt6985-cve-2026-43499
CVE-2026-43499 exploit adapter for MT6985 MediaTek Dimensity 9300 (vivo PD2241)
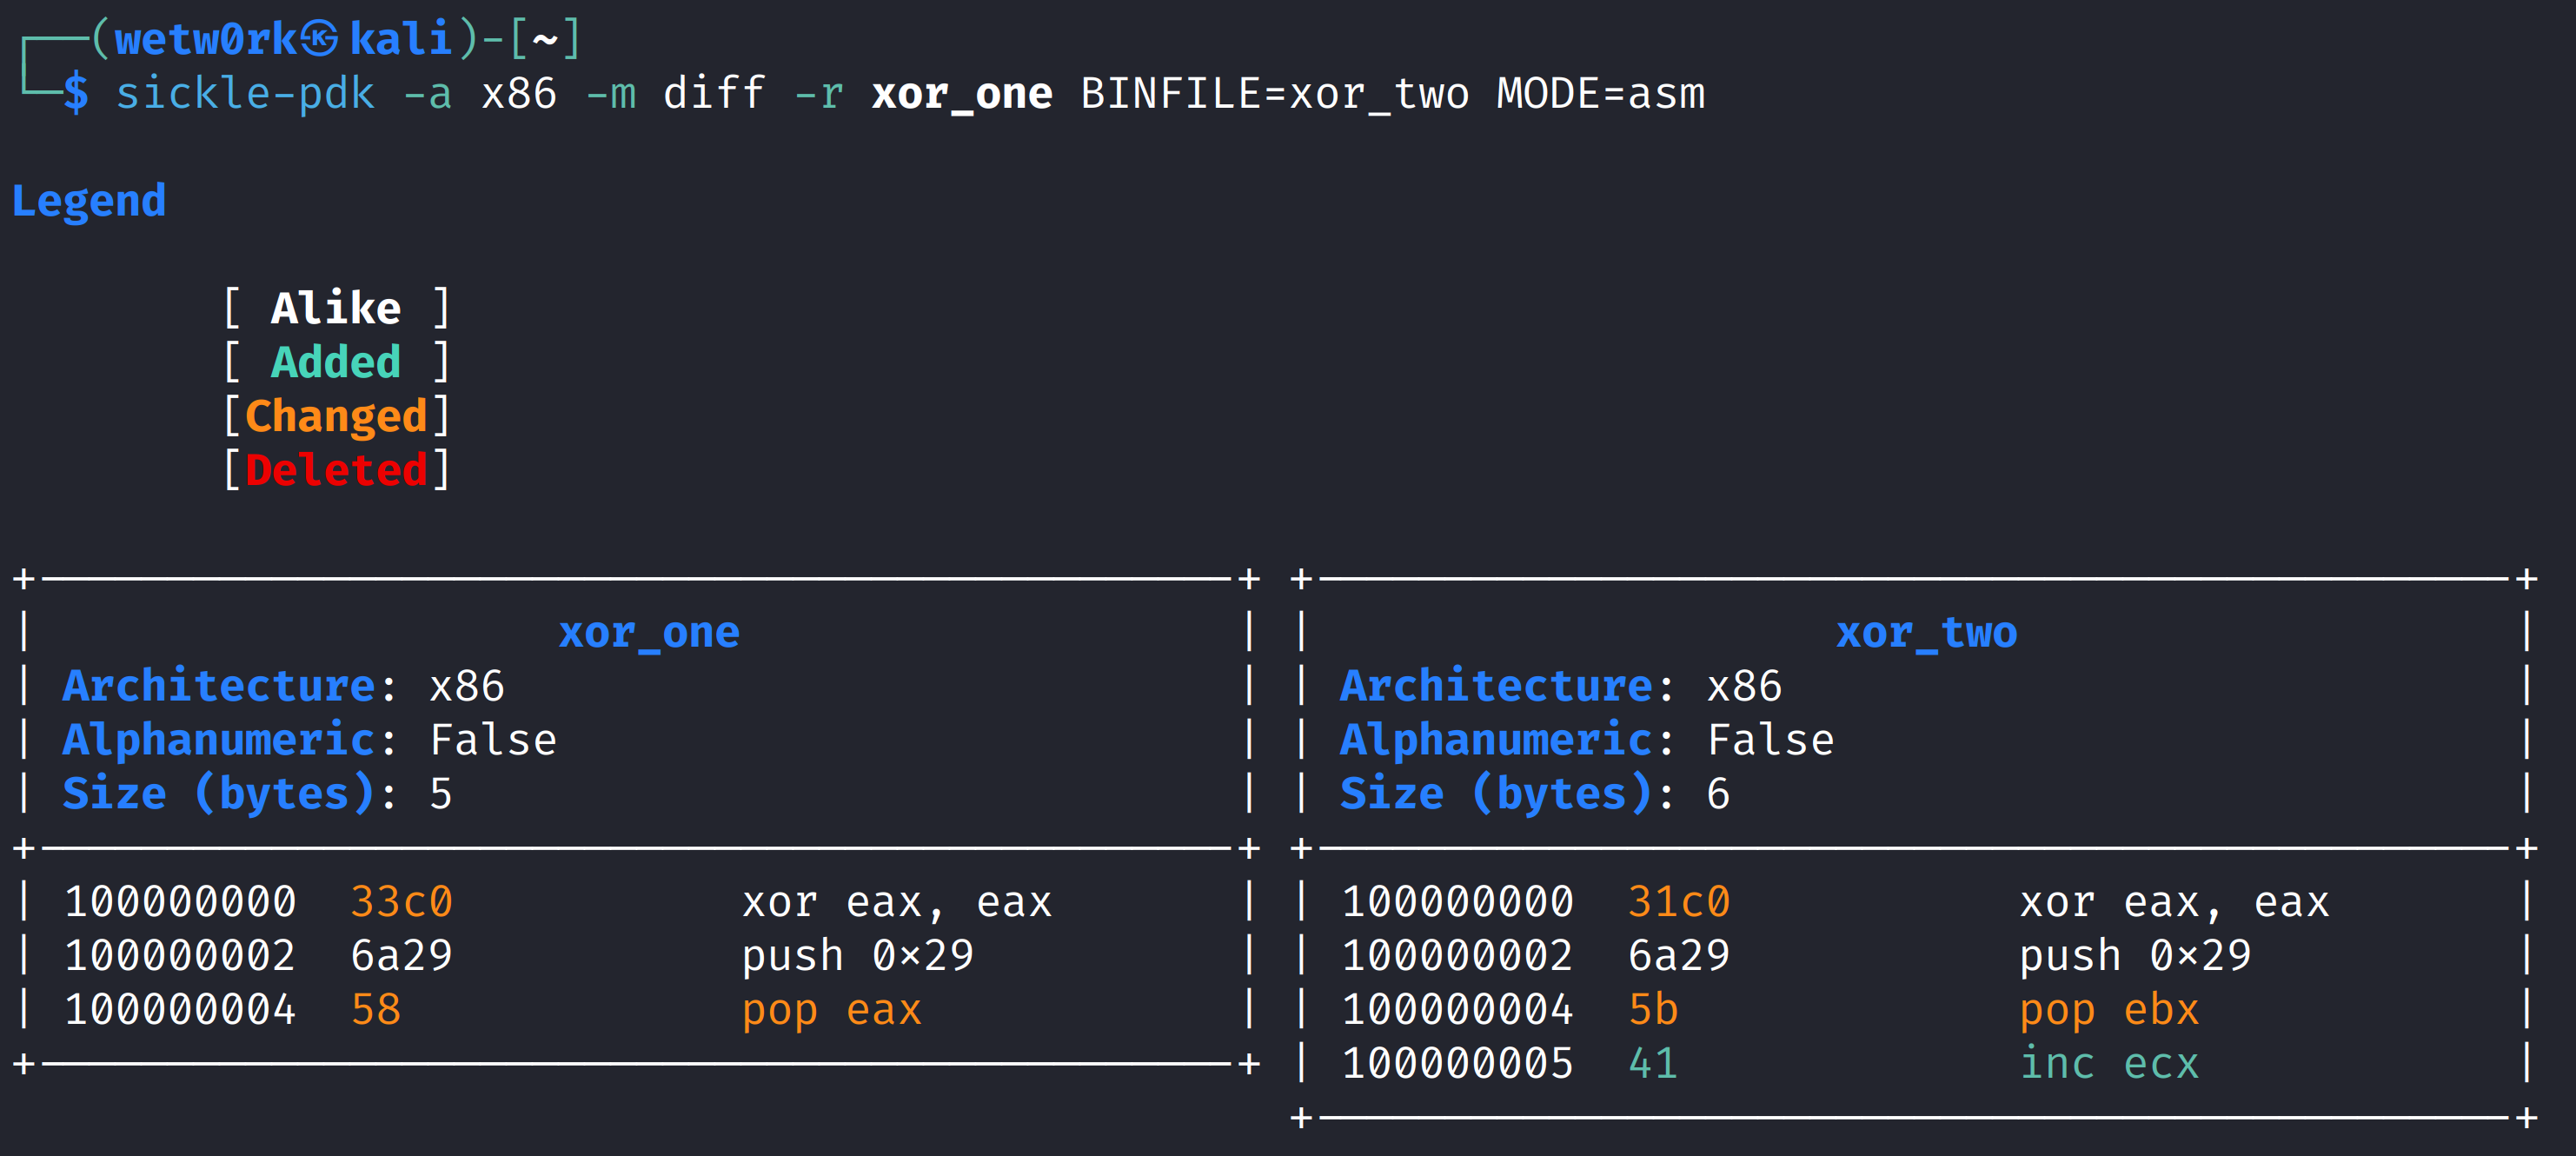 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 secretsquirrel/bdfproxy
Patch Binaries via MITM: BackdoorFactory + mitmProxy.
 jacobsoo/amtracker
Android Malware Tracker
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
 payatu/cve-2018-14442
PoC for Foxit Reader CVE-2018-14442
 genericcoding/pois0nsword
A demonstration of read write using cve-2025-43529 and userland PAC bypass on iOS 26.1
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
 sofianehamlaoui/lockdoor-framework
🔐 Lockdoor Framework : A Penetration Testing framework with Cyber Security Resources
