UEFI-Security-Research-Howyar-SysReturn-NetCopy

Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…

Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…

Tutorial and source code for building a custom YARA module in C to extract malware configurations, with a practical Danabot example and reusable…

SecurityTube Linux Assembly Expert x86 Exam

Analysis of public exploits or my 1day exploits

This repository contains a IDA Python script to recover PrideLocker ESX encryptor strings and a YARA rule

Detailed write-up of a CTF challenge: reverse engineering a React SPA, parsing SVG images, building an automated solver with greedy matching, and…

Proof-of-concept code for beating Google's ZK proof of quantum cryptanalysis

Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers

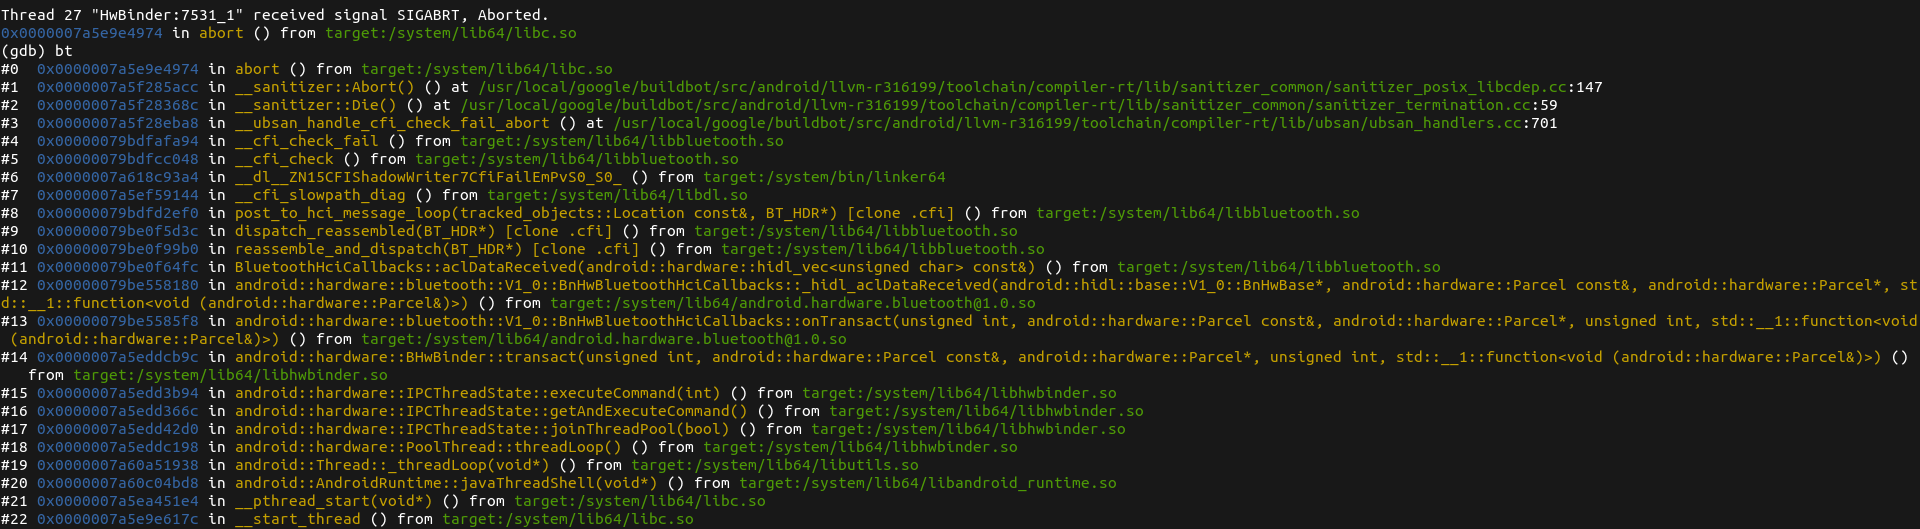
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)

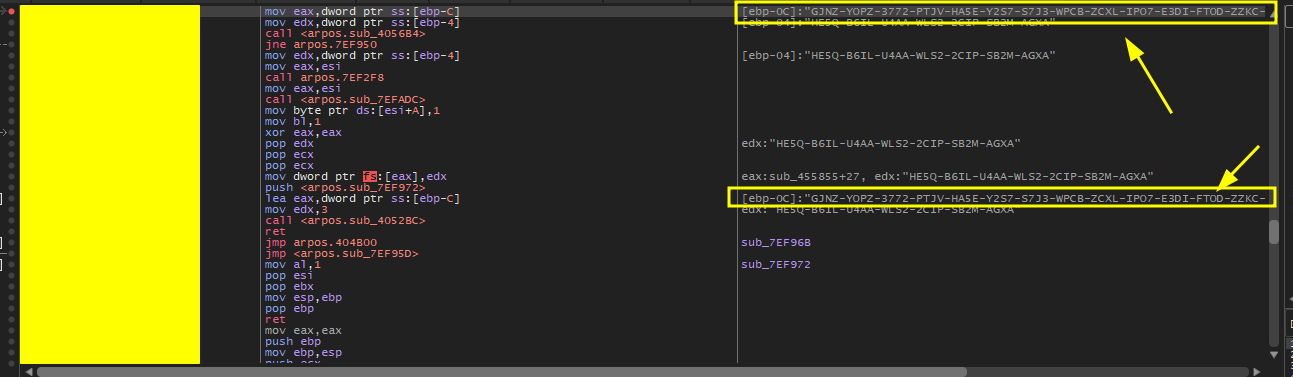
CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…

Executes at the silicon boundary

Test harness for CVE-2024-20696 Windows libarchive RCE vulnerability, enabling binary analysis and exploitation testing of archiveint.dll with custom…

Demonstrates cleartext storage of license keys in memory in Abacre Restaurant POS, enabling license activation bypass via debugger and memory dump…

Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…

SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…

Injects code into ELF executables post-build

A fully functional DanderSpritz lab in 2 commands

k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.