
CAPEsolo
 capesandbox/capesolo
Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
defensive-toolsdynamic-analysis-sandboxingforensics+7
28
capesandbox/capesoloStandalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…
 snyi001/cve-2026-79551-tenda
Tenda Technology Co., Ltd NVR_4H: CH3 v2.1.V27.5.58.6 was discovered to contain a hardcoded cryptographic key.
 gavmor/x86-cpp-reversing-skill
Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)
 kaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis
Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 lmx-071028/cve-2024-30350-research-notes
Research notes documenting CVE-2024-30350, an out-of-bounds read in Foxit PDF Reader annotation handling, covering triage, disclosure, and defensive…
 wadingporque/apkprobe
APK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 australeo/cve-2021-28476
Proof-of-concept for CVE-2021-28476, a Hyper-V vmswitch.sys arbitrary pointer dereference allowing guest-to-host denial-of-service and potential RCE.
 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS .pkg app…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
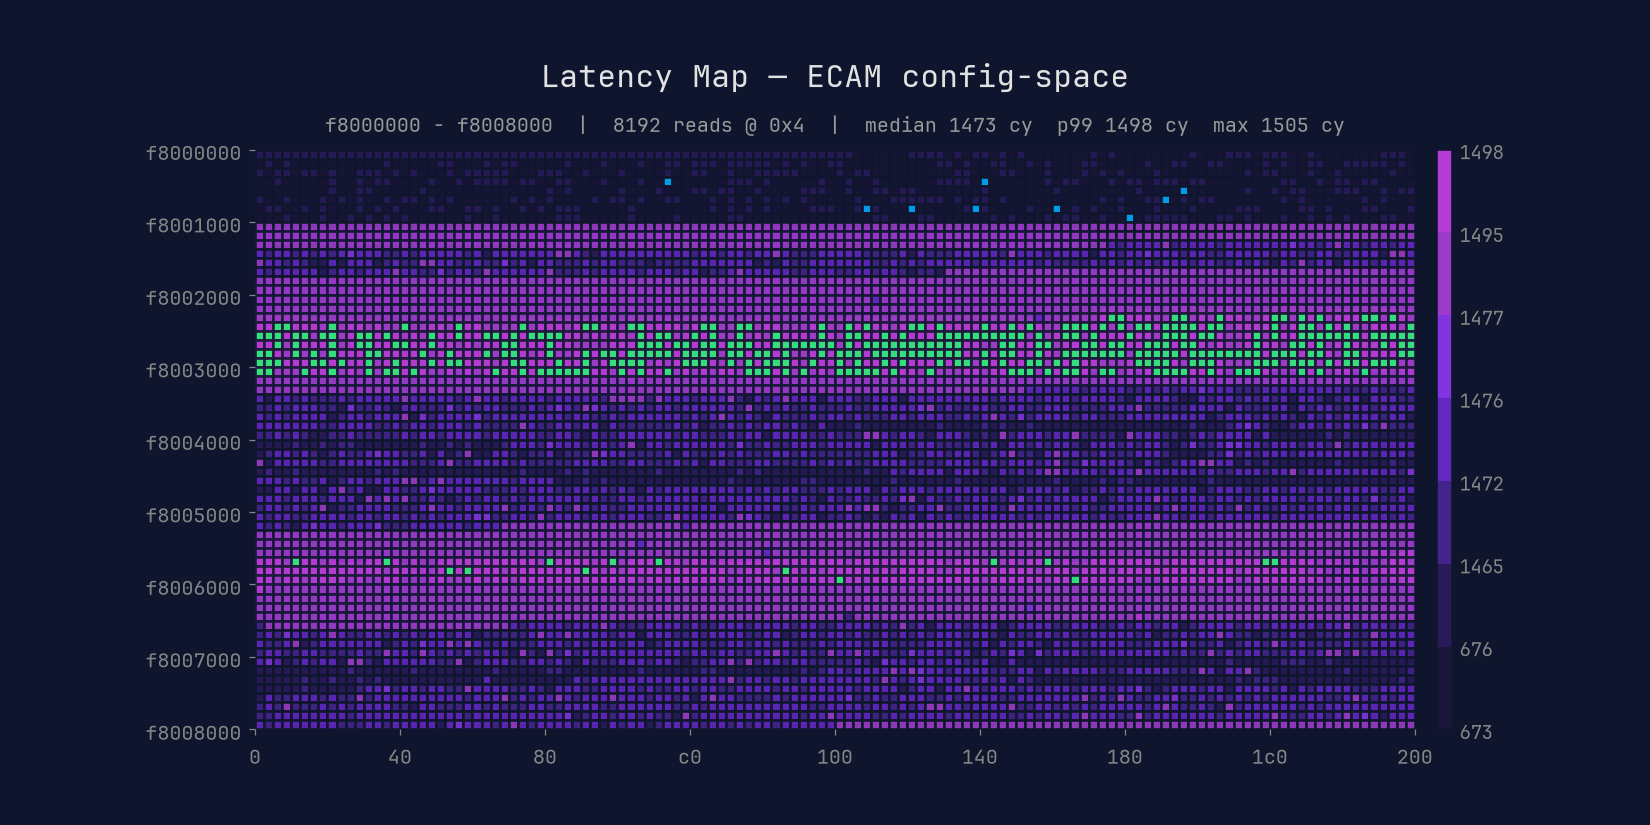 xoreaxeaxeax/mmiotic
Latency x-ray for undocumented hardware
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more