
Enigma-
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
ai-assisted-reversingai-securitybinary-analysis+5
1
gmh5225/enigma-C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
 c3rb3ru5d3d53c/mwcfg
A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
 infobyte/wiremax
Lua-based Wireshark postdissector that decrypts and parses Ubiquiti AirMAX/RouterBoard 802.11 vendor IEs into filterable fields.
 p0dalirius/pdbdownload
An utility to download PDB files associated with a Portable Executable (PE).
 nccgroup/pip3line
The Swiss army knife of byte manipulation
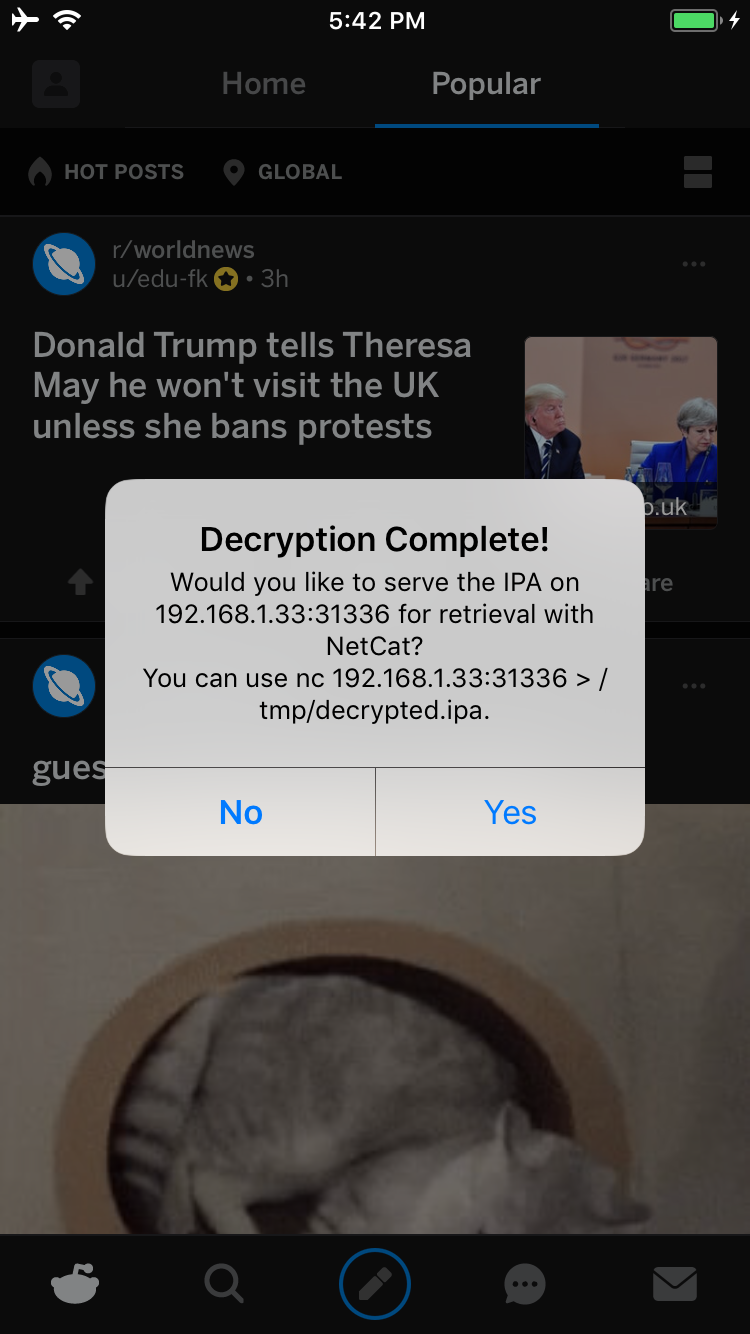 bishopfox/bfdecrypt
Utility to decrypt App Store apps on jailbroken iOS 11.x
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 bkerler/mtkclient
Mediatek Flash and Repair Utility
 c0mposer/c-game-modding-utility
A game modding utility that makes injecting C/C++ code easier.
 gabemarshall/brosec
Brosec - An interactive reference tool to help security professionals utilize useful payloads and commands.
 upx/upx
UPX - the Ultimate Packer for eXecutables
 zznop/drow
Injects code into ELF executables post-build
 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.