
apkprobe
 wadingporque/apkprobe
APK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…
android-securityinformation-gatheringmobile-security+5
5
wadingporque/apkprobeAPK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 janhalendk/react
A OSINT project that explores how to dump data from React
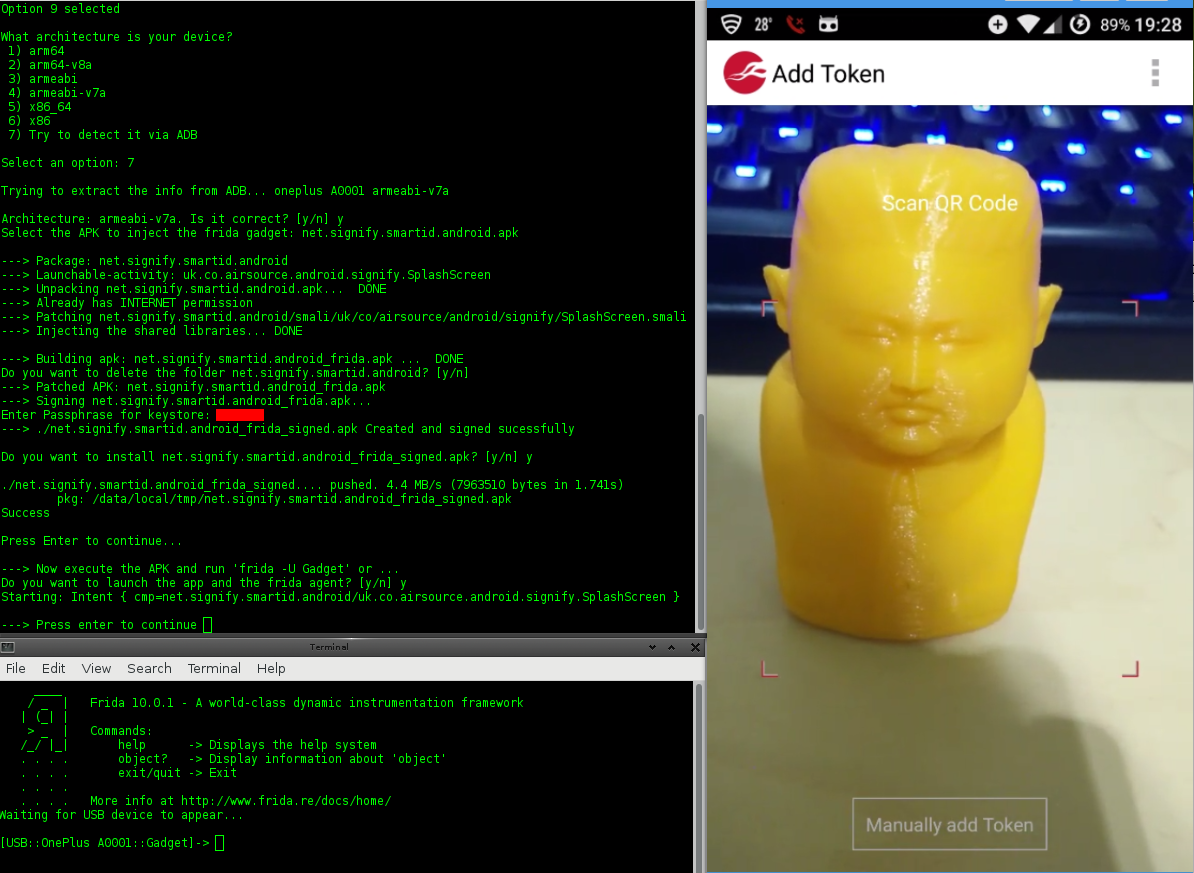 nccgroup/lazydroid
bash script to facilitate some aspects of an Android application assessment
 adamlaurie/hdmi-sniff
sniff HDMI DDC (I2C) traffic
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
 gabemarshall/brosec
Brosec - An interactive reference tool to help security professionals utilize useful payloads and commands.
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 reverseclabs/gwtmap
Maps attack surface of GWT applications by extracting obfuscated RPC endpoints and generating serialized request payloads for security testing.
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
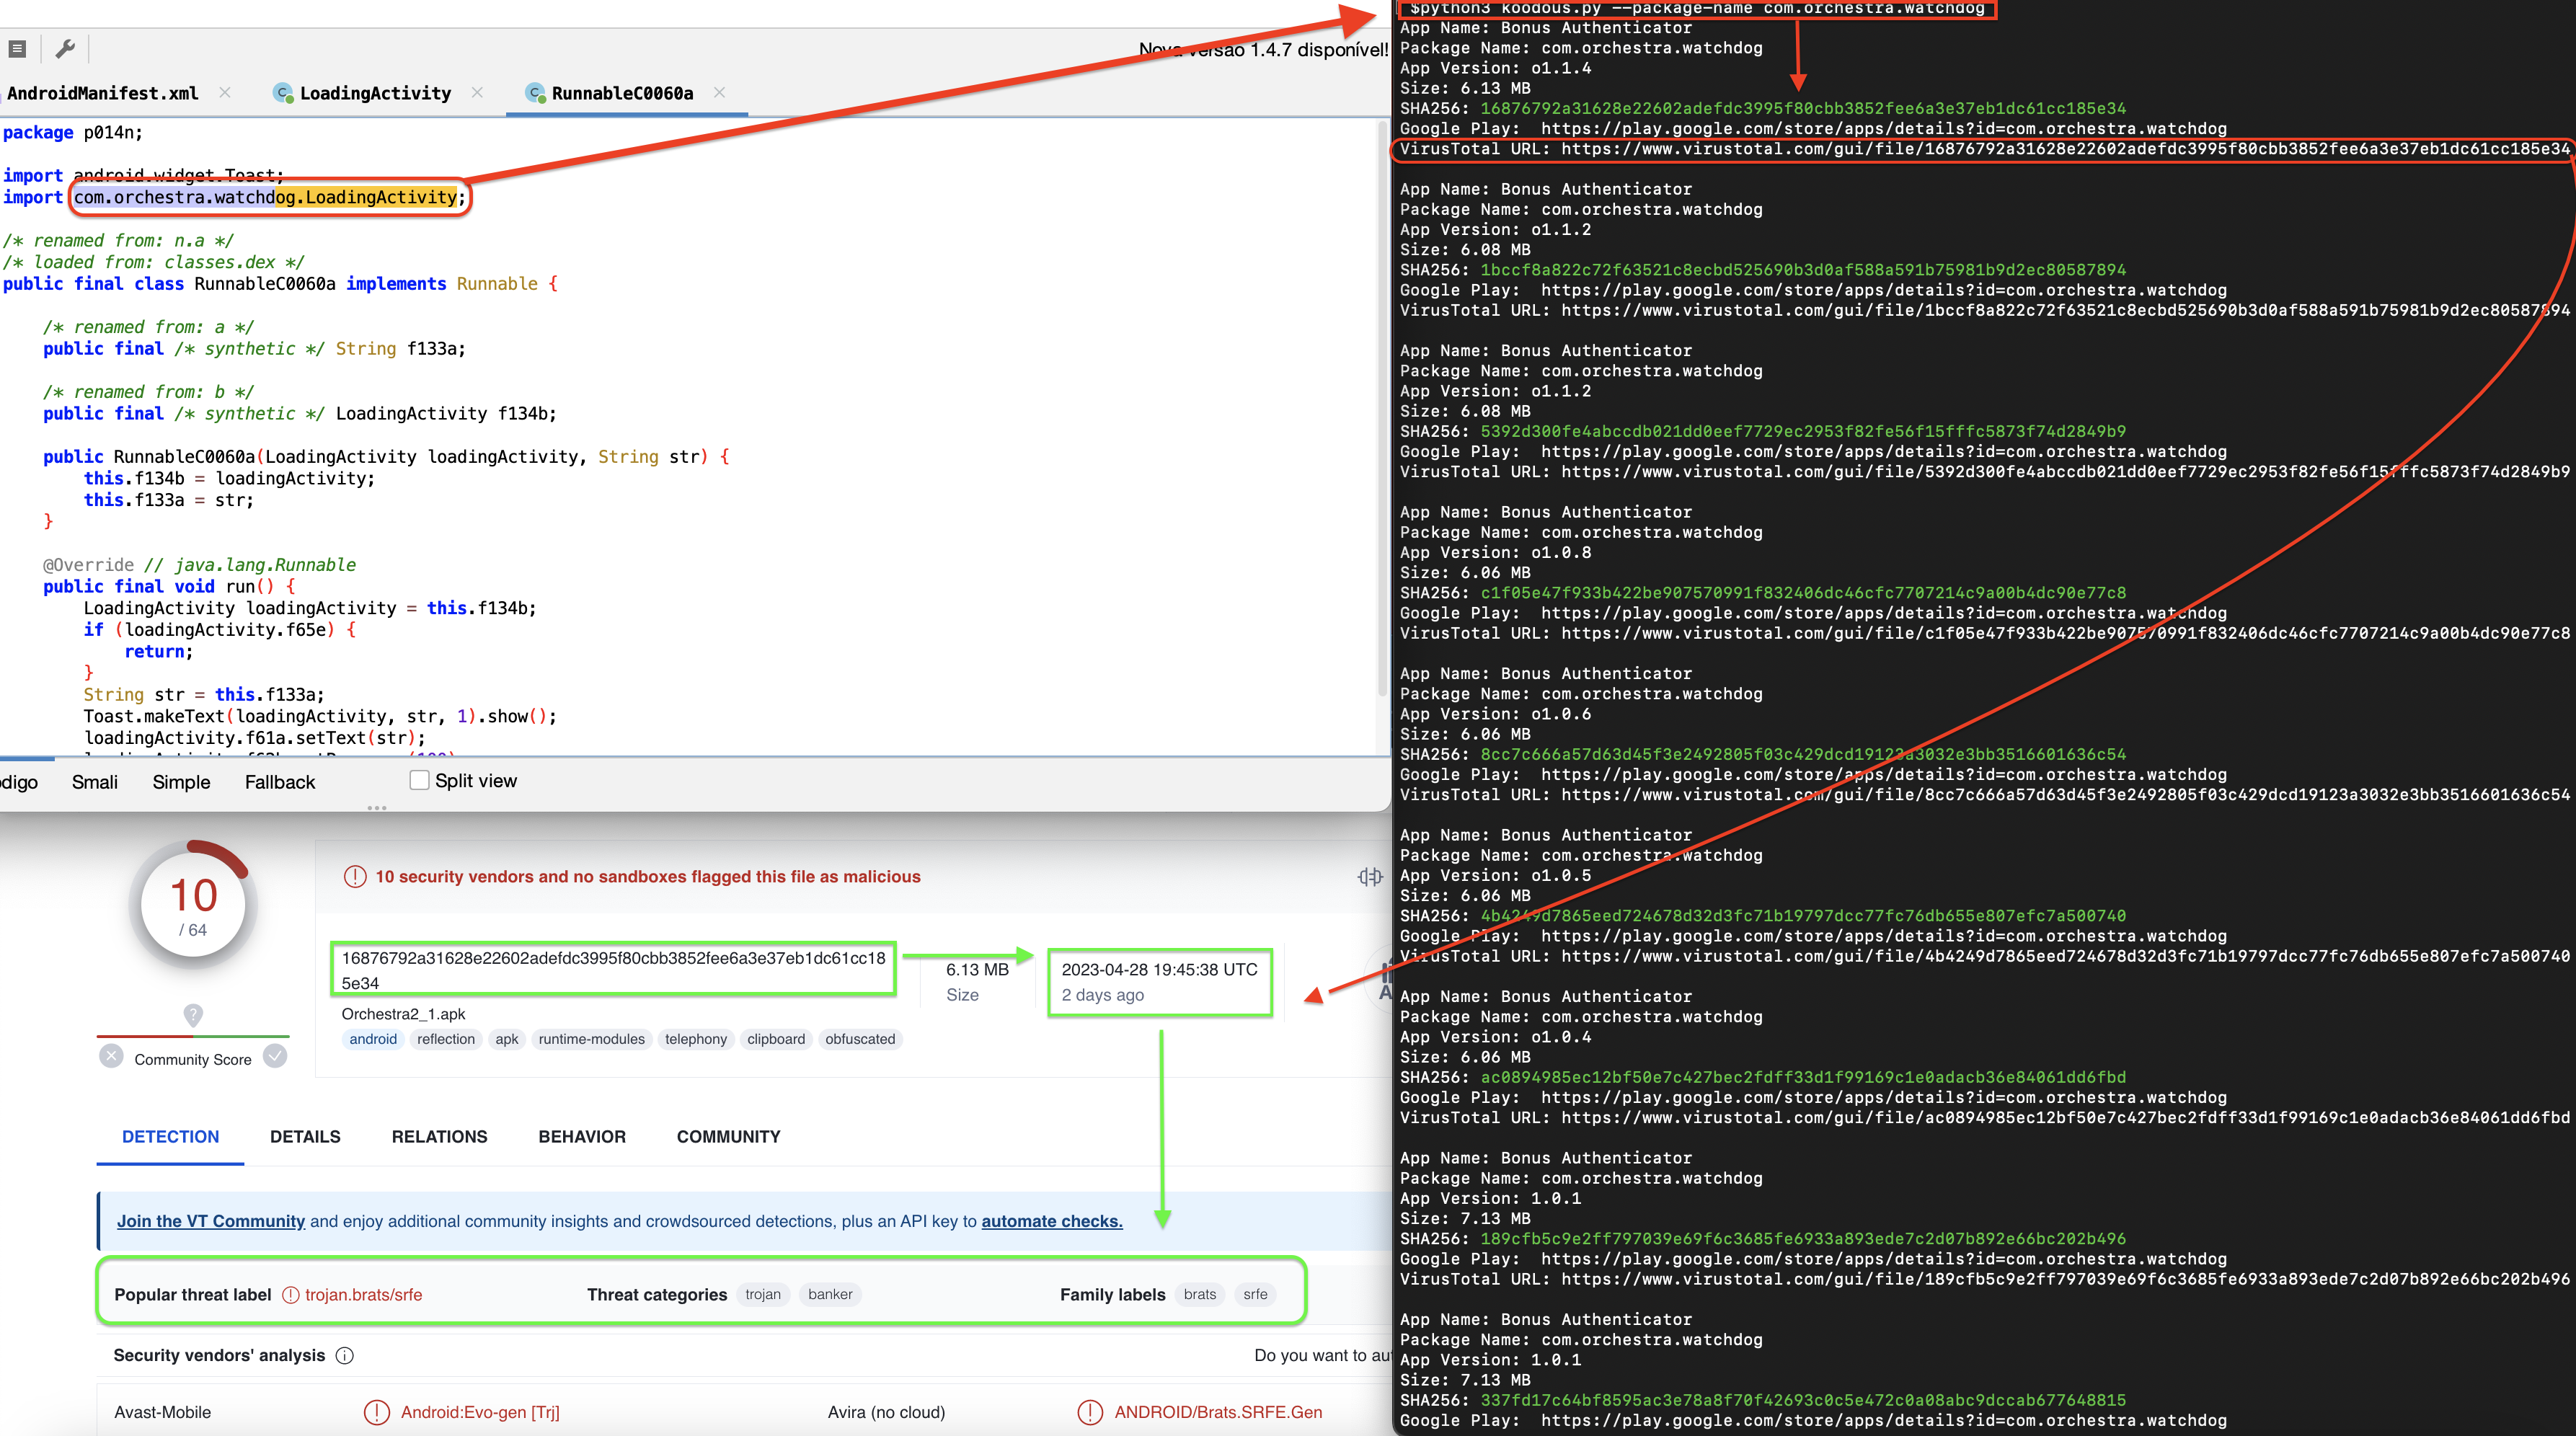 huntdownproject/koodousfinder
A simple tool to allows users to search for and analyze android apps for potential security threats and vulnerabilities
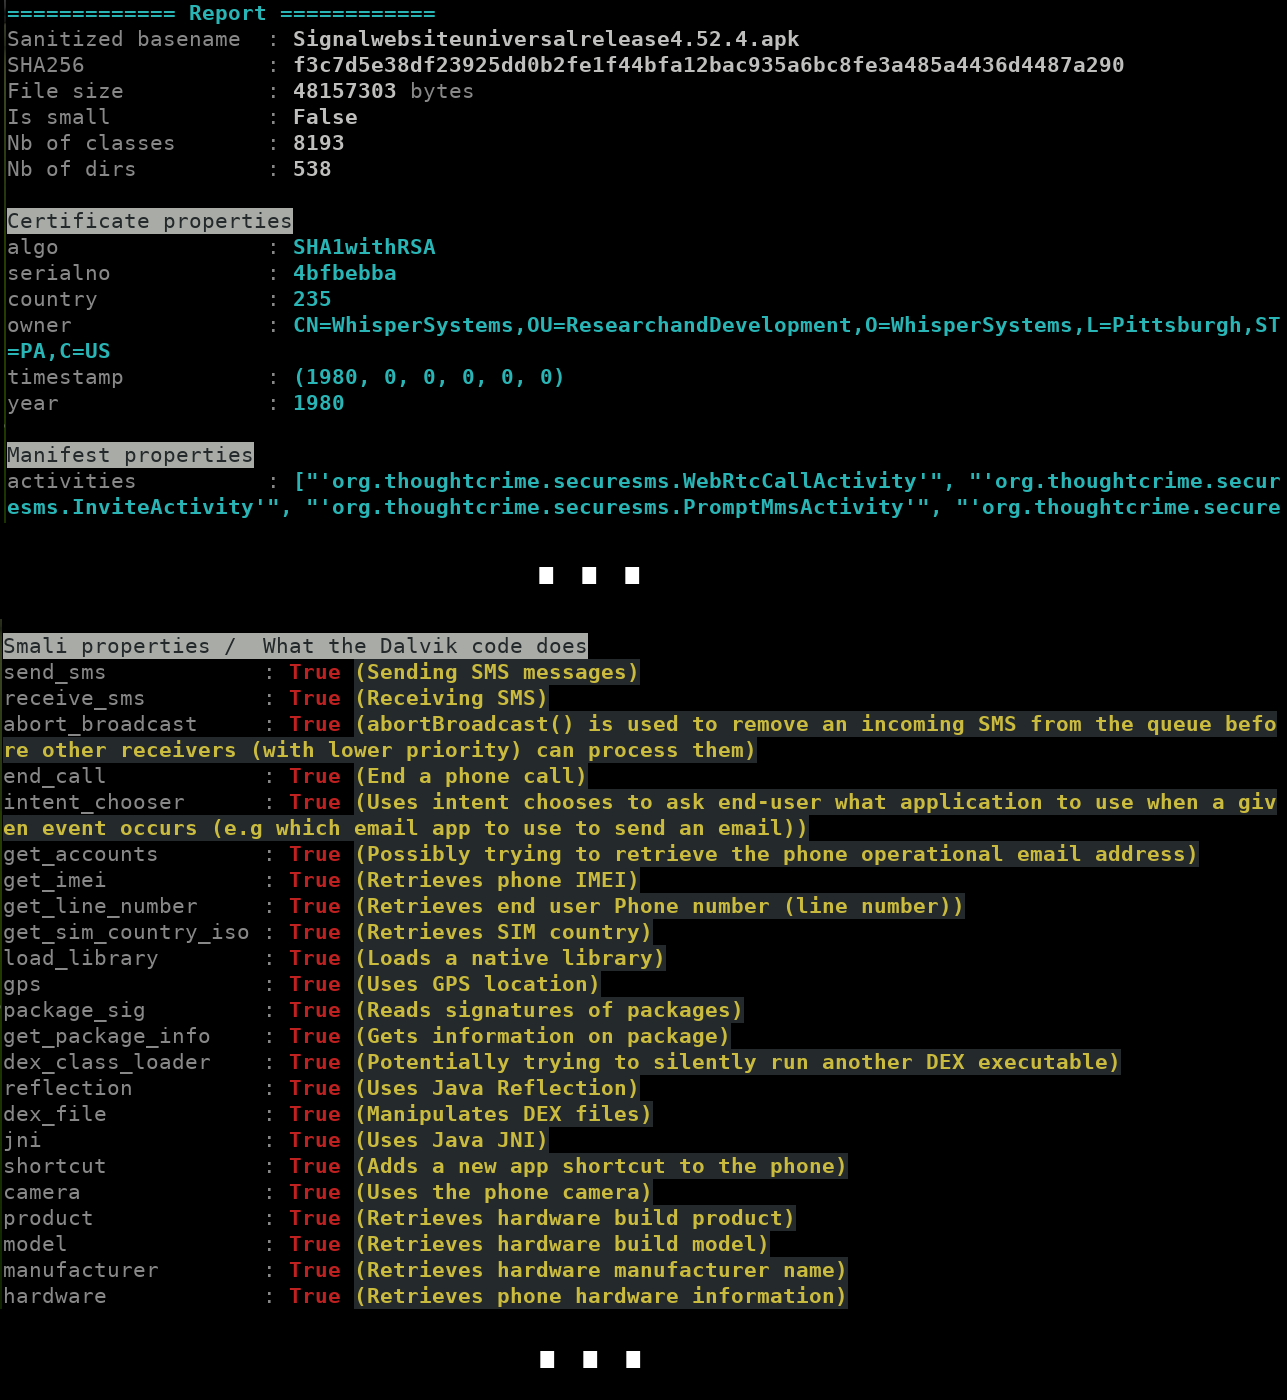 cryptax/droidlysis
Automated pre-analysis tool for Android apps that disassembles samples, extracts properties via configurable pattern matching, and organizes output…
 gonzosint/gvision
Reverse image search tool using Google Cloud Vision API to detect landmarks, web entities, and geolocation data from images for OSINT investigations.
 thelicato/secbutler
The perfect butler for pentesters, bug-bounty hunters and security researchers
 alufers/mitmproxy2swagger
Automagically reverse-engineer REST APIs via capturing traffic