
avdroot
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
android-securitybinary-analysismobile-app-pentesting+6
316 days ago
ejfkdev/avdrootRoot an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
 ejfkdev/ddc
DEX → Java decompiler in Rust — fast, progressive analysis, bilingual CLI
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 newliver666/apk-reverse
Agent skill for Android APK reverse engineering: dex patching, unpacking, repacking, ad and paywall removal, native .so analysis, and runtime…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
 yutori-natsu/cve-2023-6931-pipa
Kernel LPE exploit for CVE-2023-6931 on Xiaomi Pad 6 (pipa), chaining a perf read_size overflow to root and disabling SELinux via data-only…
 mke84/neo8-ghostlock-adaptation
iQOO Neo8 (PD2301, 5.10.246 GKI) CVE-2026-43499 GhostLock 适配 · 48 宏 target.h + offsets.json + 15 轮实测 log · 只缺 write layer
 deancyl/s9180-rootmygalaxy
RootMyGalaxy for Galaxy S23 Ultra SM-S9180 (FZG1) - temp root via CVE-2026-43499, KernelSU late-load, no partition flashing, no Knox
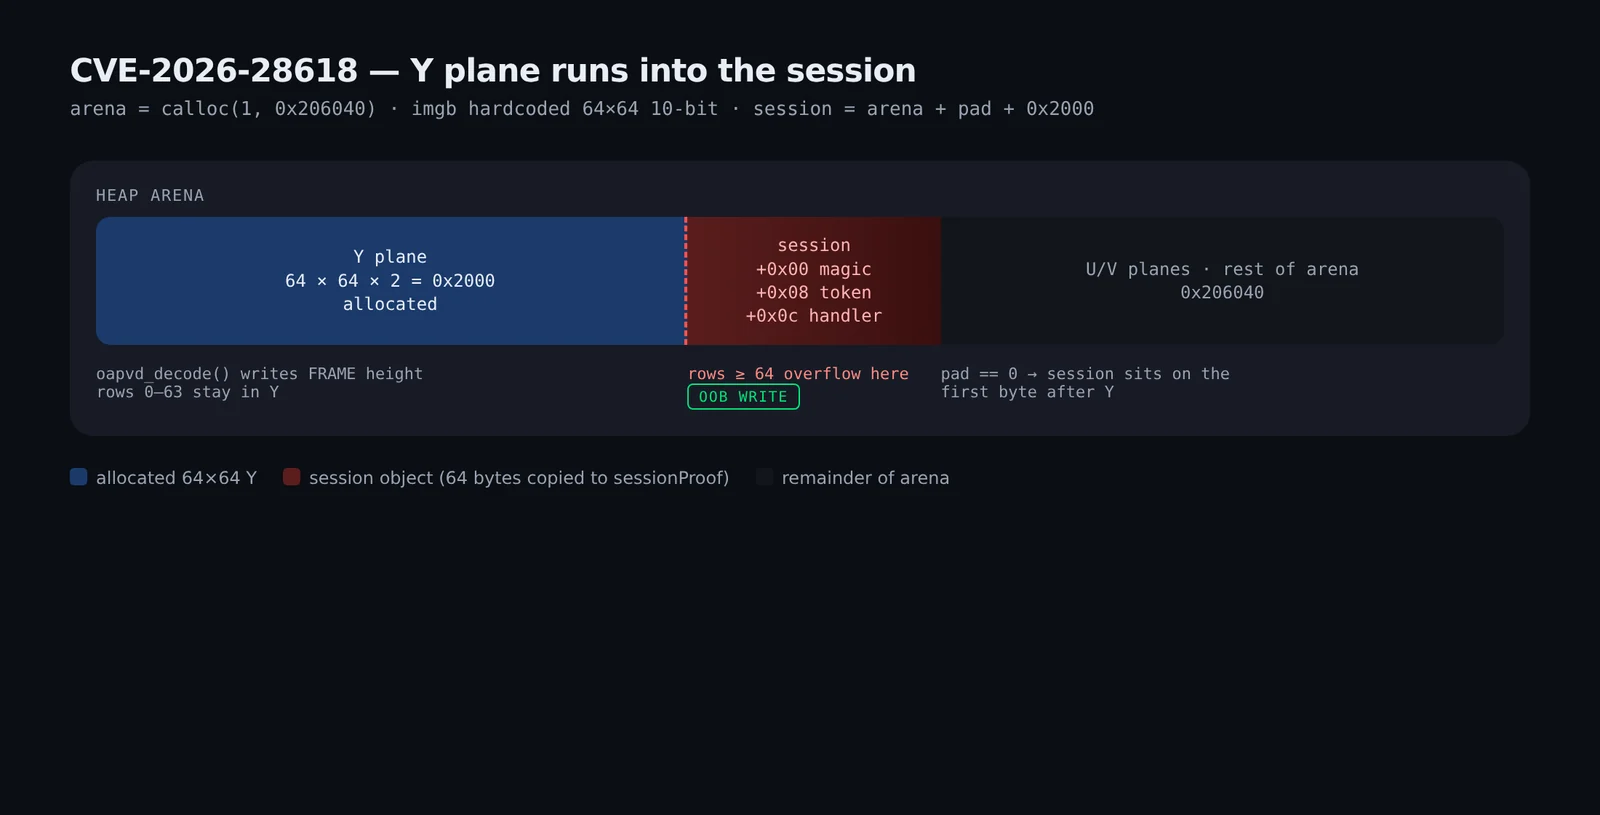 raafatabualazm/streambox-cve-2026-28618
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch
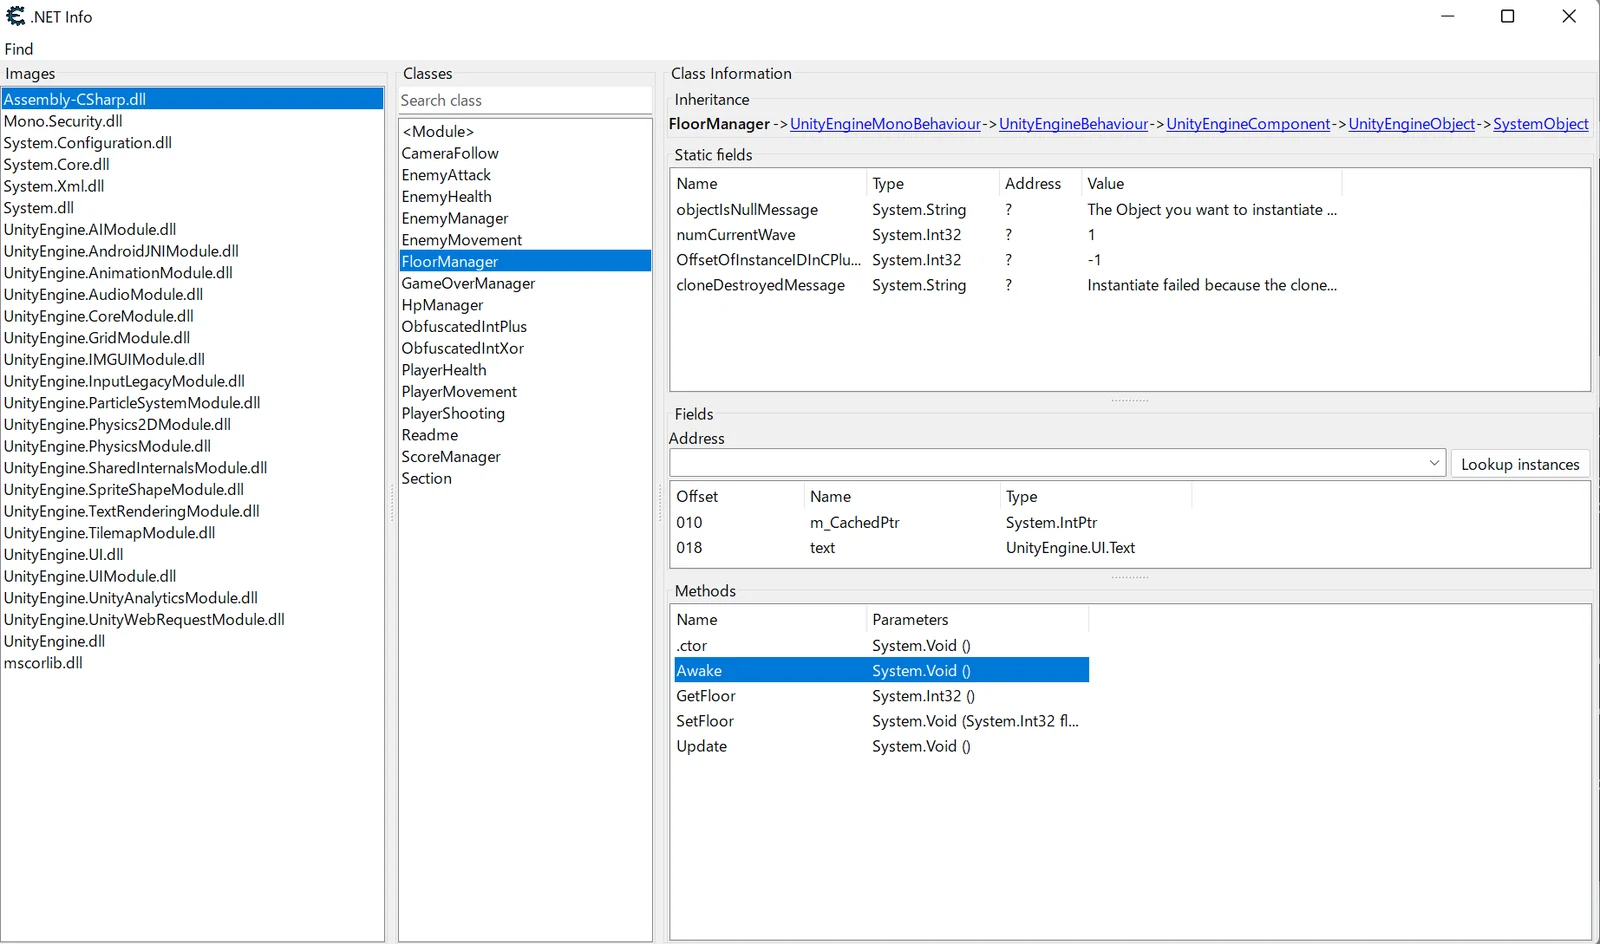 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 gmh5225/frida-vmprotect-bypass
Frida script that bypasses VMProtect runtime protections on mobile platforms, enabling dynamic instrumentation and analysis of protected binaries.