

ghostlock-app
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
android-securitybinary-analysisexploitation+4
2.4k4 days ago
yukonga/ghostlock-appGhostLock One-Tap Execution App (CVE-2026-43499)
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 frida/frida
Main repo for hosting release binaries
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 vaib25vicky/awesome-mobile-security
An effort to build a single place for all useful android and iOS security related stuff. All references and tools belong to their respective owners.…
 firerpa/lamda
Android Full-Stack Device Control Platform: WebRTC/H.264 remote desktop, UI/OCR/image-matching automation, one-click MITM, built-in Frida,…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 xiaohj233/ghostlock-x200-root
GhostLock-X200 v1.0 - temporary root toolchain for vivo X200 (PD2415 / b57 kernel) based on CVE-2026-43499. For authorized security research only.
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 danieldev23/frida-ssl-bypass
Frida toolkit that bypasses SSL/TLS certificate pinning on Android apps, hooking Java TrustManager, OkHttp, Conscrypt, and native OpenSSL/BoringSSL…
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
 bishopfox/mauidll
Extract the managed (.NET) assemblies out of a MAUI Android assembly store.
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
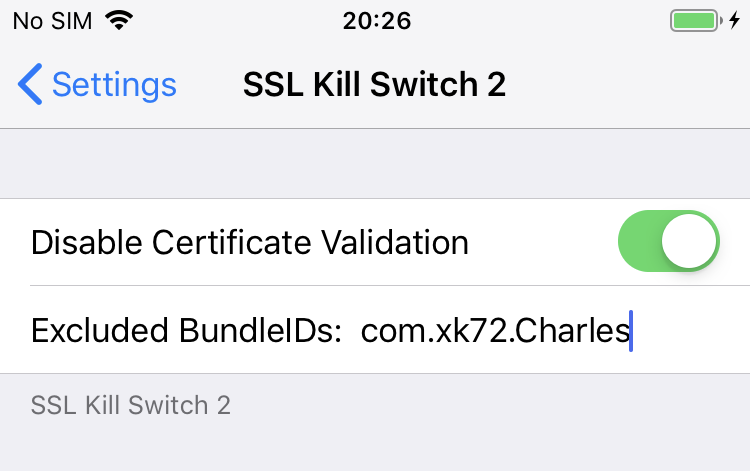 nabla-c0d3/ssl-kill-switch2
Blackbox tool to disable SSL certificate validation - including certificate pinning - within iOS and macOS applications.
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.