

rea
 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
ai-assisted-reversingai-securitybinary-analysis+5
morluto/reaReverse engineer anything with agents, from app behavior down to native binaries.
 ngwg/ceasta
Disassembler, decompiler and x64dbg-style debugger for PE/ELF binaries with IDA-style listing, function graphs, Lua plugins, CLI, and a built-in MCP…
 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 rasetsuu/vmp-devirt
Trace-assisted VMProtect devirtualization research platform: version front-ends feed a shared Remill/LLVM backend to lift handlers, recover dataflow,…
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
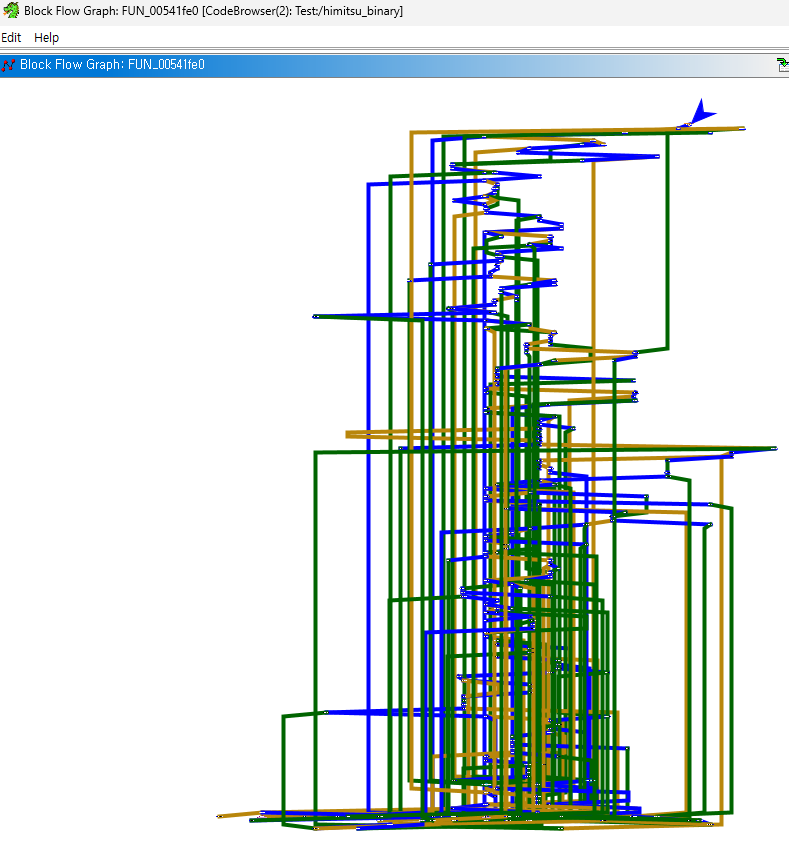 himitsushell/himitsushell
shell script protector (obfuscation, embedded interpreter, DRM) - invisible to kernel tracing