ipatool
 majd/ipatool
Command-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
information-gatheringios-securitymobile-app-pentesting+2
11.9k
majd/ipatoolCommand-line tool that allows you to search for iOS, iPadOS, tvOS, watchOS, visionOS, and macOS apps on the App Store, and download .ipa or macOS…
 drk1wi/modlishka
Modlishka. Reverse Proxy.
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 kaandemir993/darktortilla-rat-telegram-exfiltration-payload-extraction-analysis
Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…
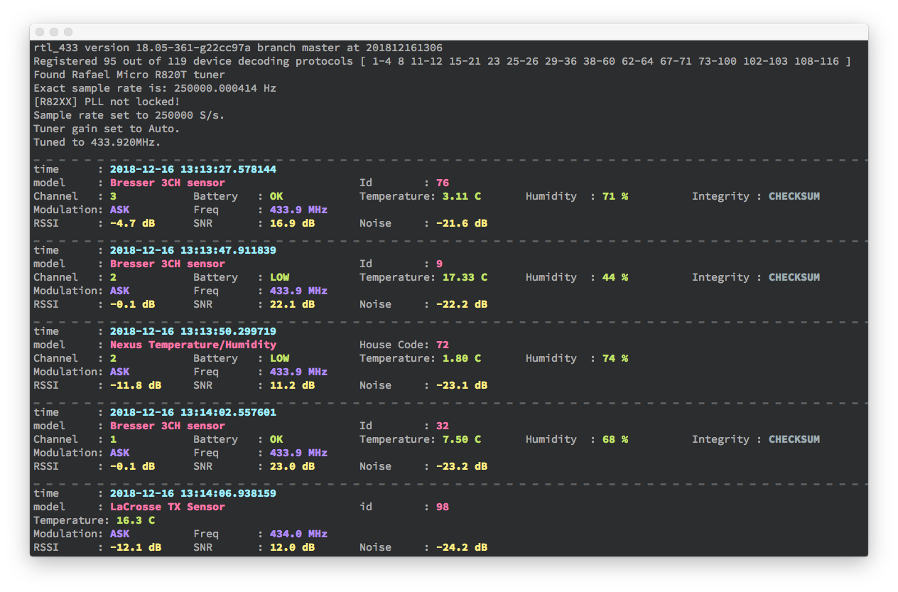 merbanan/rtl_433
Program to decode radio transmissions from devices on the ISM bands (and other frequencies)
 lautarovculic/frida-ipa-extract
Robust Frida-based tool to dump decrypted iOS apps as .ipa from a jailbroken device supports App Store, sideloaded and system.
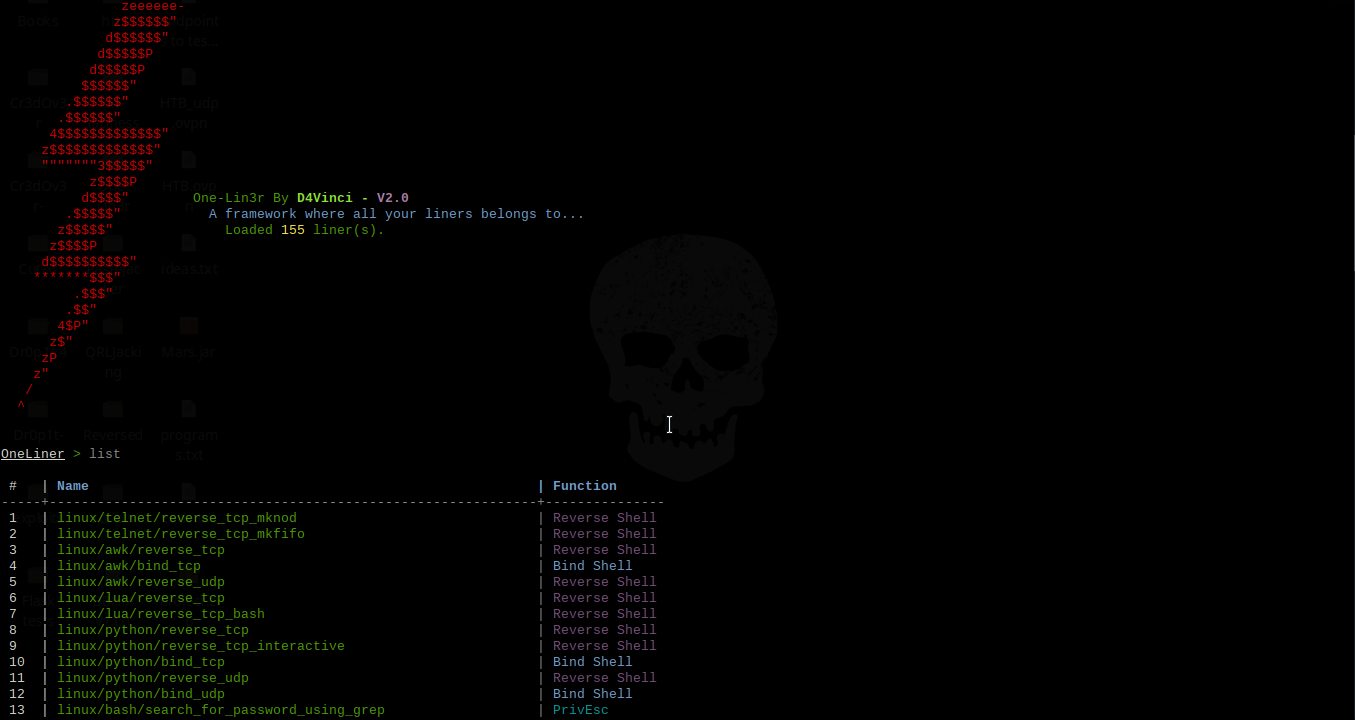 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 kaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis
Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.
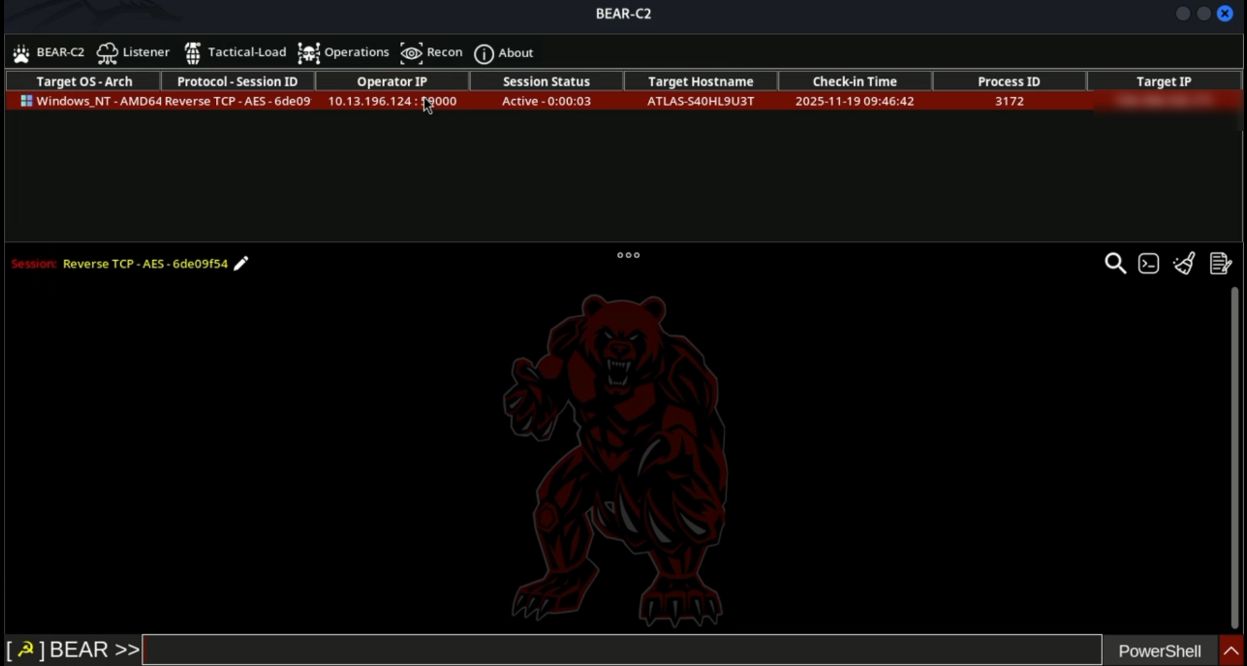 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
 reverseclabs/gwtmap
Maps attack surface of GWT applications by extracting obfuscated RPC endpoints and generating serialized request payloads for security testing.
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 stonelinks/react-cve-2025-55182
Analysis of malware found on a server compromised via CVE-2025-55182, including obfuscated dropper, C2 communication, persistence mechanisms, and…
 kaandemir993/agent-tesla-apc-injection-token-manipulation-registry-persistence-analysis
"Reverse engineering analysis of Agent Tesla, a .NET-based info-stealer that uses APC injection, token manipulation, and registry persistence.…
 alufers/mitmproxy2swagger
Automagically reverse-engineer REST APIs via capturing traffic