

awesome-canbus
 idoka/awesome-canbus
:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…
curated-resourceseducationembedded-systems-security+7
3.5k
idoka/awesome-canbus:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…
 123wwwa/flowname
Next-generation JavaScript identifier recovery with LLMs.
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
 sofianehamlaoui/lockdoor-framework
🔐 Lockdoor Framework : A Penetration Testing framework with Cyber Security Resources
 lt-asset/resym
For our CCS24 paper 🏆 "ReSym: Harnessing LLMs to Recover Variable and Data Structure Symbols from Stripped Binaries" by Danning Xie, Zhuo Zhang, Nan…
 lucamassarelli/yarasafe
SAFE embeddings to match functions in yara
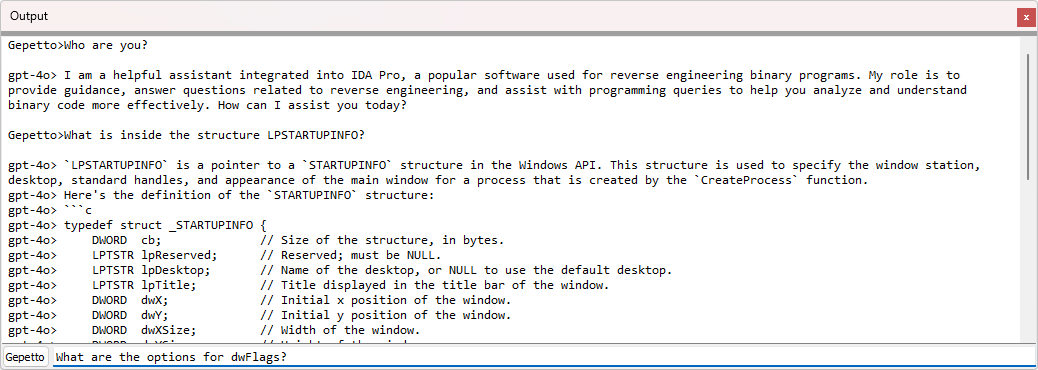 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering
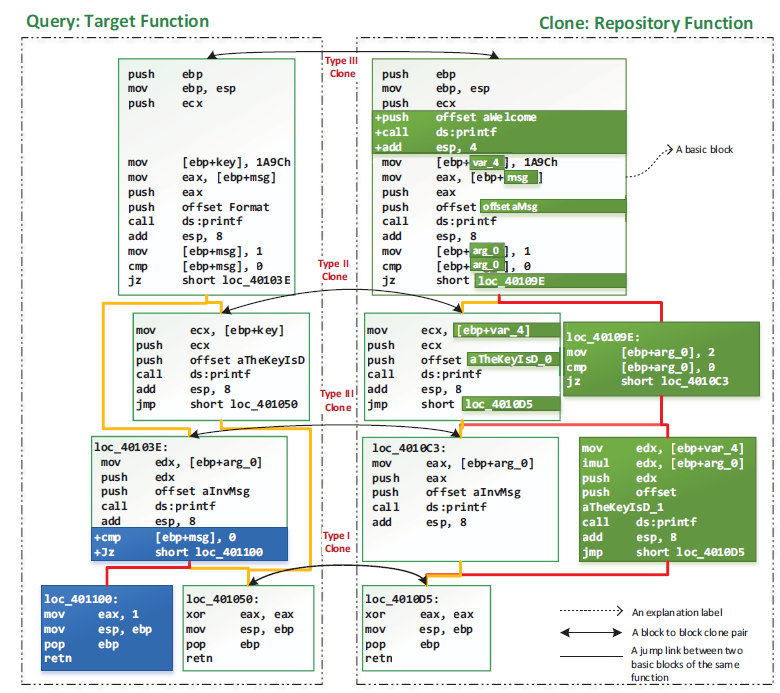 mcgill-dmas/kam1n0-community
Scalable assembly analysis platform for indexing, clone search, and executable classification using static, dynamic, and machine-learning techniques…
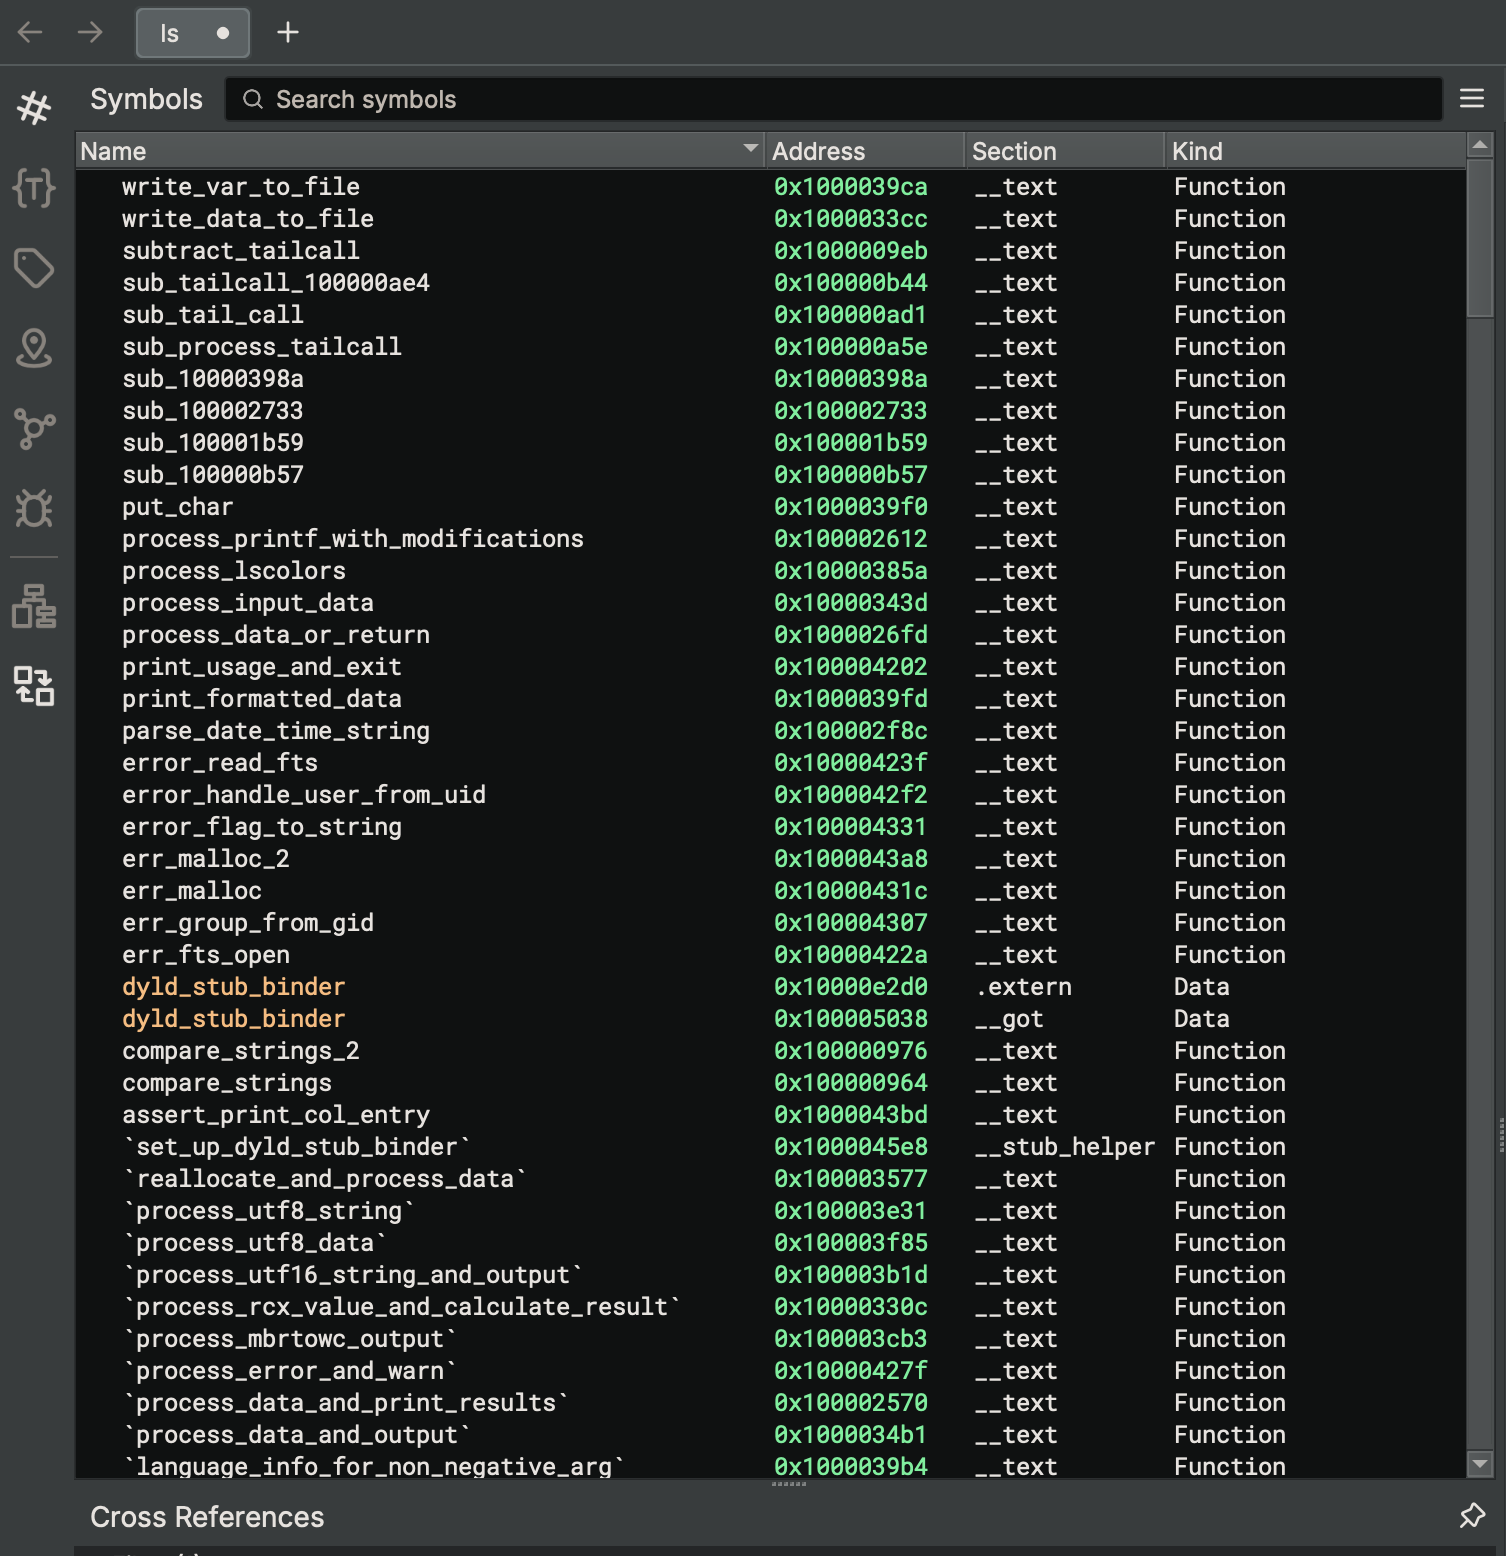 ahaggard2013/binaryninja-ollama
Plugin for Binary Ninja that integrates local Ollama models to rename functions and variables in decompiled HLIL code, preserving privacy by keeping…
 secdevops-cuse/cyberrange
The Open-Source AWS Cyber Range
 perkins-fund/malware-bible
Free educational courses in cybersecurity, reverse engineering, malware analysis, and programming designed to expand access, build practical skills,…
 neuromancer/rats-re
Reconstructs legacy Windows binaries into C source by pairing Ghidra decompiler exports with local LLMs, producing compile-checked candidates and…
 gadiluna/safe
SAFE: Self-Attentive Function Embeddings for binary similarity
 jhuapl/codecut
A Ghidra plugin for locating object file boundaries.