Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
108 results
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.

binary-analysisdata-recoveryforensics+3
132
1 month ago
Xiaomi-C200-Firmware-Analysis preview

Xiaomi-C200-Firmware-Analysis

GitHubh3xdum/xiaomi-c200-firmware-analysis

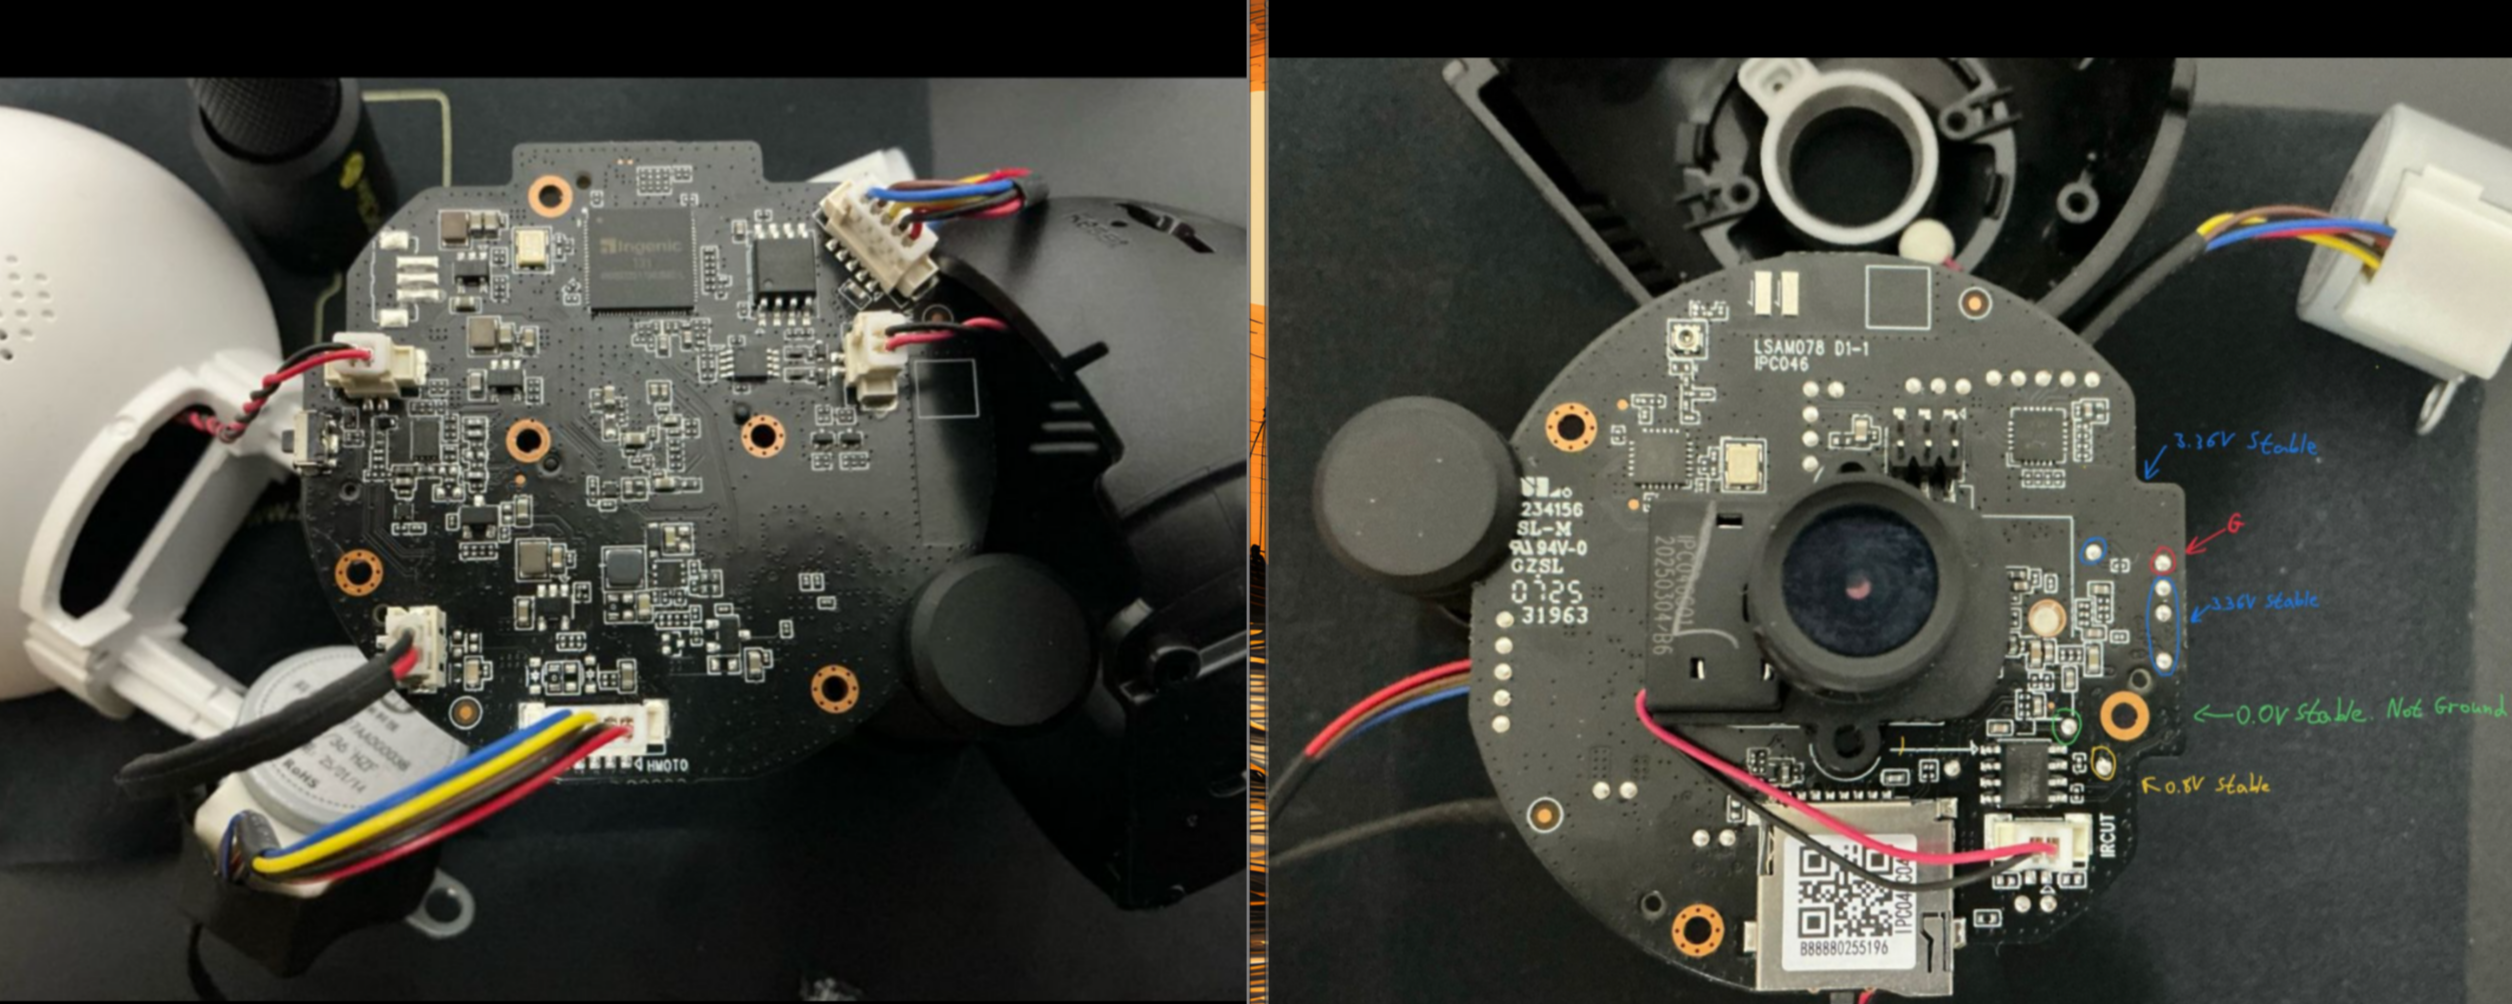
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot

data-recoveryembedded-systems-securityexploitation+6
119 months ago
USB Spy preview

USB Spy

GitLabchristophe.duvernois/usb-spy

Intercepts and analyzes USB Mass Storage traffic at the block and file level, emulates USB devices, and supports custom Python stubs for security…

digital-forensicsexploitationfirmware-analysis+6
32 months ago
LFISuite preview

LFISuite

GitHubd35m0nd142/lfisuite

Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner

exploitationpayload-generationpenetration-testing+3
2.0k8 years ago
functrace preview

functrace

GitHubinvictus1306/functrace

A function tracer

binary-analysisdebuggersdynamic-analysis-sandboxing+2
927 years ago
ImHex preview

ImHex

GitHubwerwolv/imhex

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

ai-assisted-reversingbinary-analysisbinary-exploitation+10
54.9k3 days ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…

binary-analysiscommand-and-controldefensive-tools+6
5 days ago
MemProcFS preview

MemProcFS

GitHubufrisk/memprocfs

MemProcFS

digital-forensicsforensicshardware-security+5
4.4k11 days ago
unblob preview

unblob

GitHubonekey-sec/unblob

Extract files from any kind of container formats

binary-analysisdata-recoveryembedded-systems-security+3
2.6k2 days ago
hobbits preview

hobbits

GitHubmahlet-inc/hobbits

A multi-platform GUI for bit-based analysis, processing, and visualization

binary-analysisdata-recoveryforensics+1
7511 year ago
Nodejs-Tracer preview

Nodejs-Tracer

GitHubcheckpointsw/nodejs-tracer

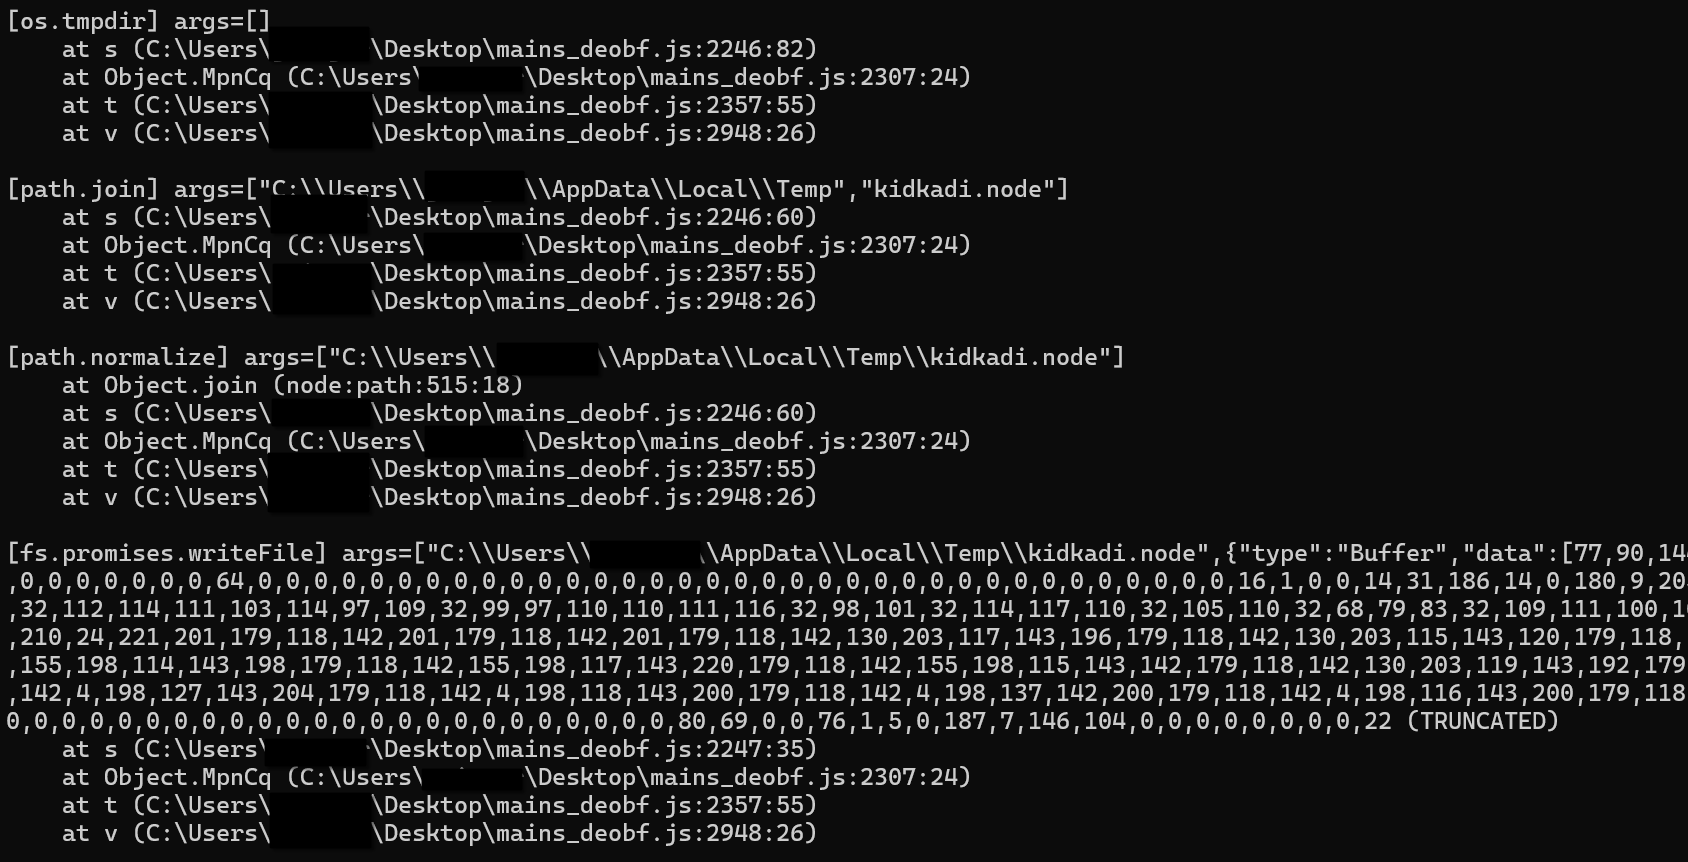
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…

anti-botdynamic-analysis-sandboxingids-ips-evasion+3
818 months ago
wcw-cyberring-pav-decryptor preview

wcw-cyberring-pav-decryptor

GitHubblakebratcher/wcw-cyberring-pav-decryptor

Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…

binary-analysiscryptographydata-recovery+5
258 months ago
Ropper preview

Ropper

GitHubsashs/ropper

Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…

binary-analysisbinary-exploitationctf+3
2.2k1 month ago
dwarf2json preview

dwarf2json

GitHubvolatilityfoundation/dwarf2json

convert ELF/DWARF symbol and type information into vol3's intermediate JSON

binary-analysisdigital-forensicsmemory-forensics+2
1611 year ago
DriverBuddy preview

DriverBuddy

GitHubnccgroup/driverbuddy

DriverBuddy is an IDA Python script to assist with the reverse engineering of Windows kernel drivers.

binary-analysisreverse-engineeringvulnerability-analysis
3826 years ago
pe-signgen preview

pe-signgen

GitHubforentfraps/pe-signgen

Universal signature generation for any system function from all Windows Builds using Winbindex

binary-analysisforensicsmalware-analysis+3
209 months ago
vmlinux-to-elf preview

vmlinux-to-elf

GitHubmarin-m/vmlinux-to-elf

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)

binary-analysisembedded-systems-securityfirmware-analysis+1
1.8k3 months ago
etl-parser preview

etl-parser

GitHubairbus-cert/etl-parser

Event Trace Log file parser in pure Python

digital-forensicsforensicslog-analysis+1
1574 months ago
Previous123456Next