
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
50 results
Discord-Rat preview

Discord-Rat

GitHubgmh5225/discord-rat

Python-based Discord RAT with remote command panel for webcam capture, audio recording, keylogging, file exfiltration, and persistence via Discord…

command-and-controldata-exfiltrationencryption-decryption-tools+7
1
1 year ago
JSRat-Py preview

JSRat-Py

GitHubhood3drob1n/jsrat-py

This is my implementation of JSRat.ps1 in Python so you can now run the attack server from any OS instead of being limited to a Windows OS with…

command-and-controlexploitationpayload-generation+3
30110 years ago
Remote-Access-Trojan-Database preview

Remote-Access-Trojan-Database

GitHubrainkin1993/remote-access-trojan-database

A database of RAT collected from Internet

curated-resourceseducationforensics+3
1606 years ago
merlin preview

merlin

GitHubne0nd0g/merlin

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

command-and-controldata-exfiltrationexploit-frameworks+10
5.6k19 days ago
gh0st3.6_src preview

gh0st3.6_src

GitHubigh0st/gh0st3.6_src

Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
command-and-controldata-exfiltrationpayload-development+3
16912 years ago
PyIris preview

PyIris

GitHubnot-sekiun/pyiris

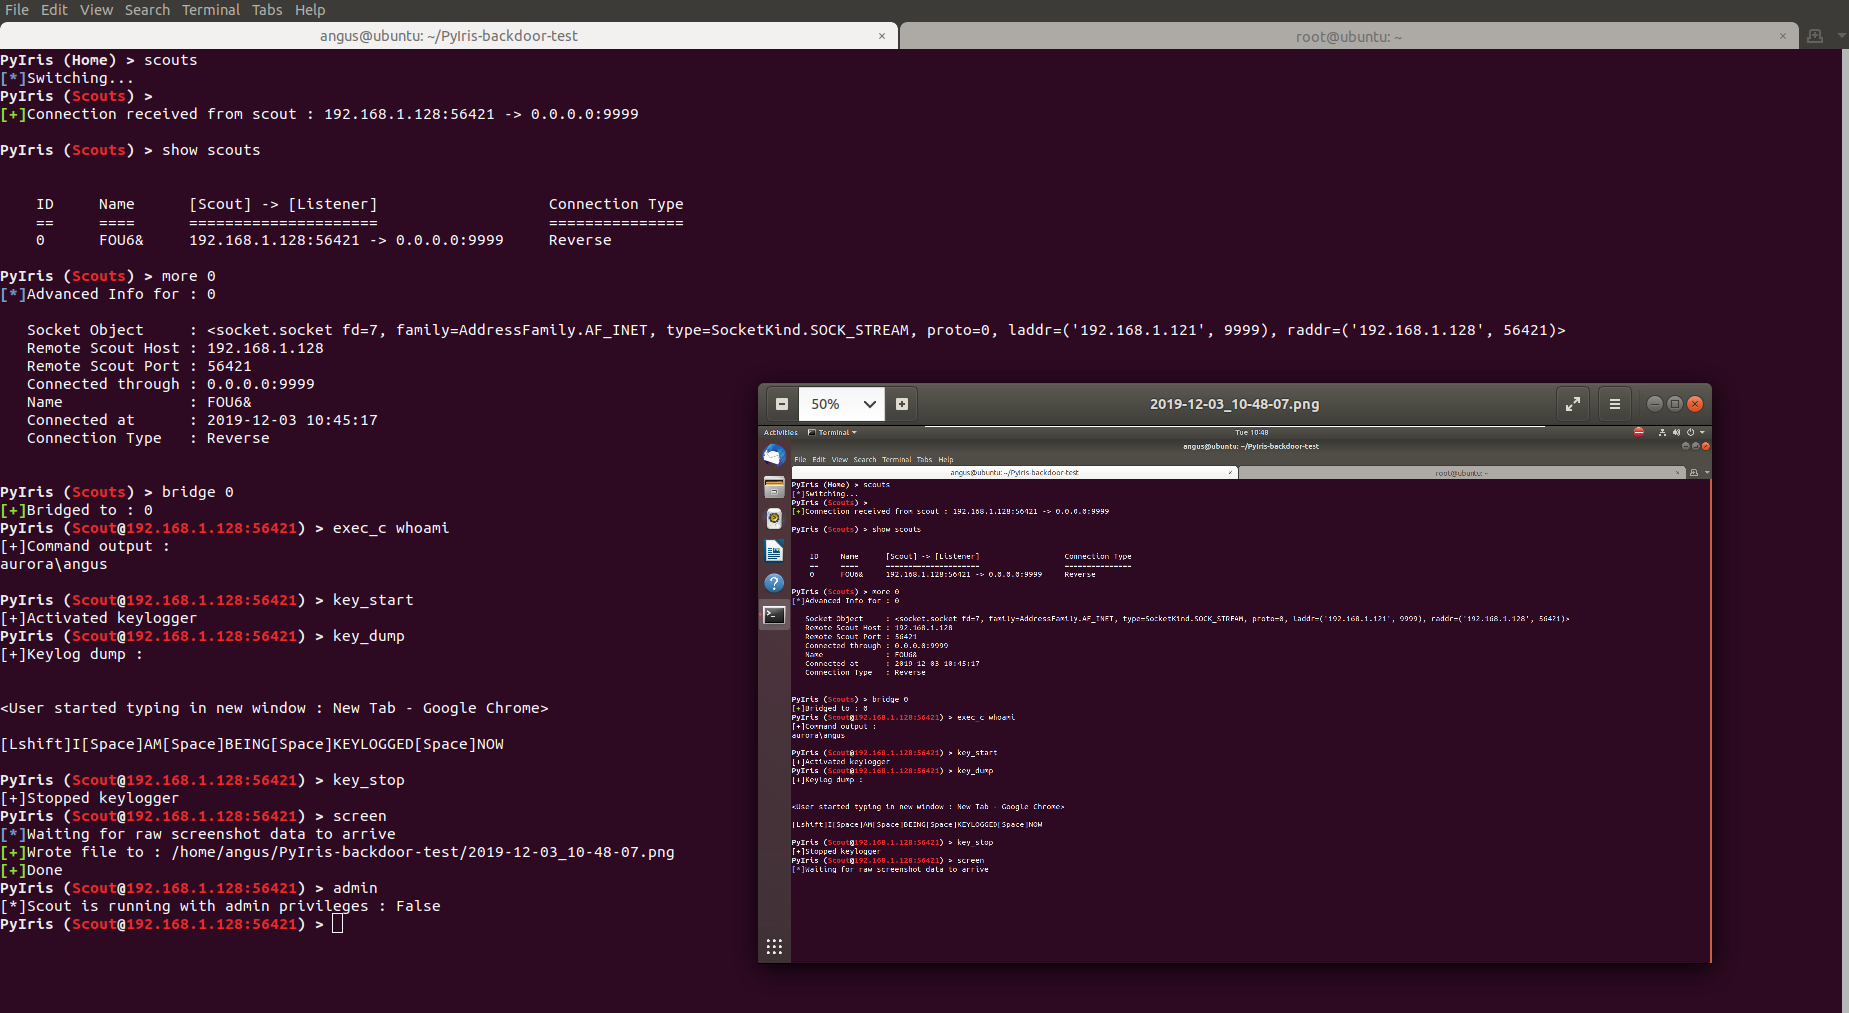
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.

command-and-controlexploitationpayload-generation+4
3251 month ago
SubSeven preview

SubSeven

GitHubdarkcodersc/subseven

SubSeven Legacy Official Source Code Repository
persistence-mechanismspost-exploitationremote-access-tool+1
6502 years ago
gcat preview
Archived

gcat

GitHubbyt3bl33d3r/gcat

A PoC backdoor that uses Gmail as a C&C server

command-and-controlexploitationpayload-development+4
1.4k7 years ago
metasploit-framework preview

metasploit-framework

GitHubrapid7/metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

command-and-controldatabase-securitydata-exfiltration+20
38.8k6h 15m ago
impacket preview

impacket

GitHubfortra/impacket

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
authenticationcommand-and-controldatabase-security+17
16.0k6h 51m ago
chisel preview

chisel

GitHubjpillora/chisel

Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…

command-and-controldata-exfiltrationgeneral-purpose-utilities+8
16.4k23 days ago
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
11.7k9 days ago
sshuttle preview

sshuttle

GitHubsshuttle/sshuttle

Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…

command-and-controldata-exfiltrationdns-analysis+6
13.5k1 day ago
Mythic preview

Mythic

GitHubits-a-feature/mythic

A collaborative, multi-platform, red teaming framework

command-and-controldata-exfiltrationexploitation+9
4.7k23 days ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.2k1 month ago
ligolo-ng preview

ligolo-ng

GitHubnicocha30/ligolo-ng

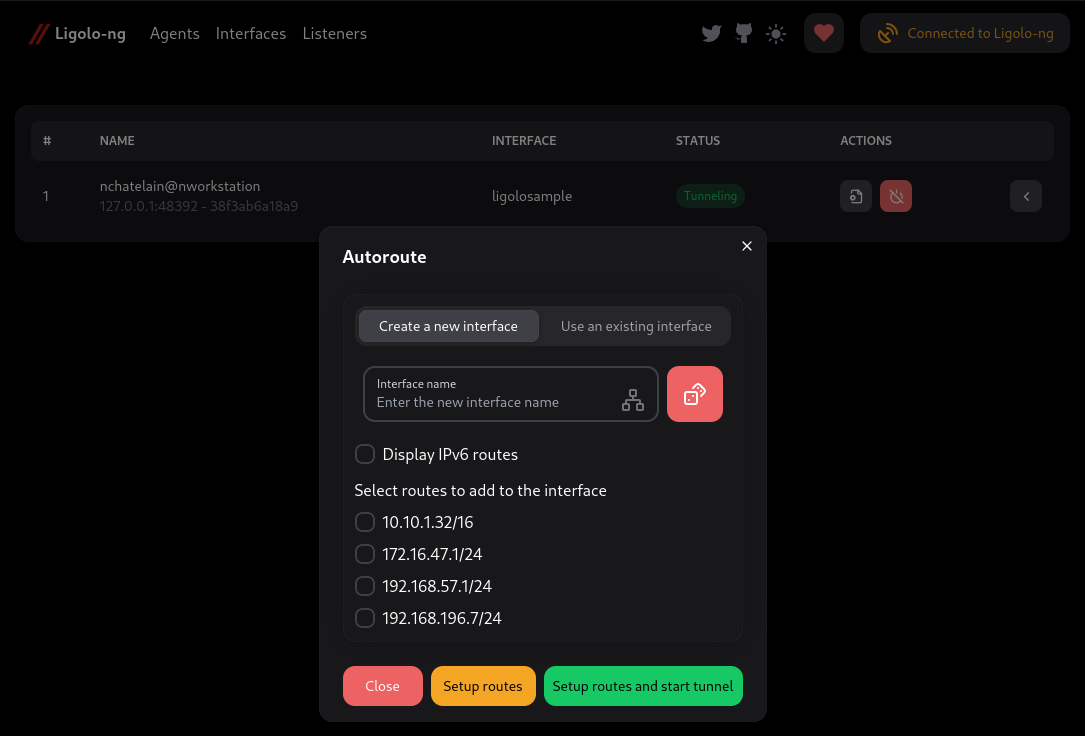
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
data-exfiltrationgeneral-purpose-utilitiesids-ips-evasion+6
4.8k1 month ago
AsyncRAT-C-Sharp preview

AsyncRAT-C-Sharp

GitHubnyan-x-cat/asyncrat-c-sharp

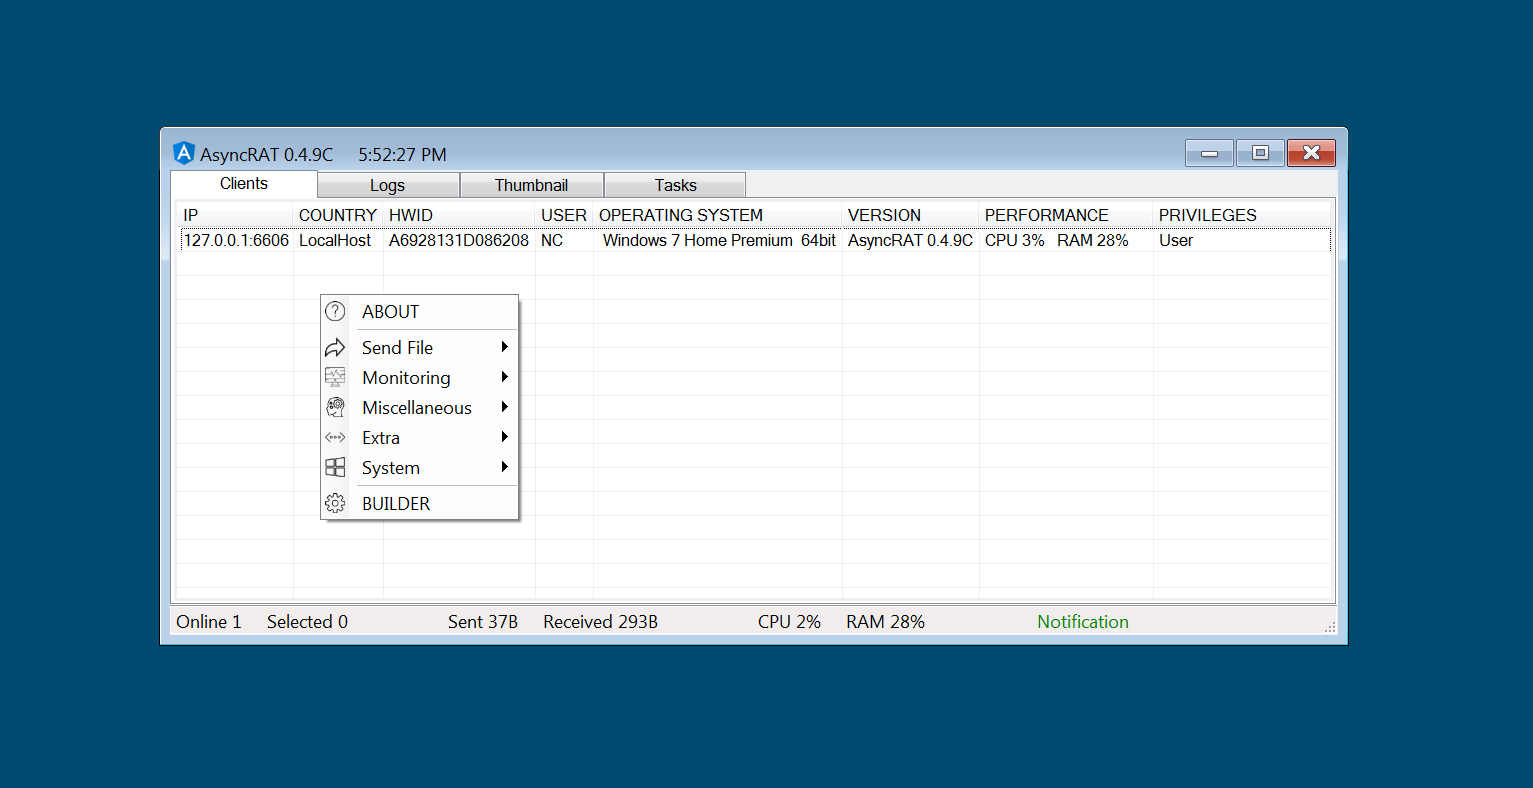
Open-Source Remote Administration Tool For Windows C# (RAT)

command-and-controldata-exfiltrationpassword-cracking+5
3.0k3 years ago
Heroinn preview

Heroinn

GitHubb23r0/heroinn

A cross platform C2/post-exploitation framework.

command-and-controldata-exfiltrationlateral-movement+8
7127 days ago
Previous123Next