

DarkFox
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
command-and-controlmalware-analysispayload-development+2
25
federicochieregato/darkfoxRemote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
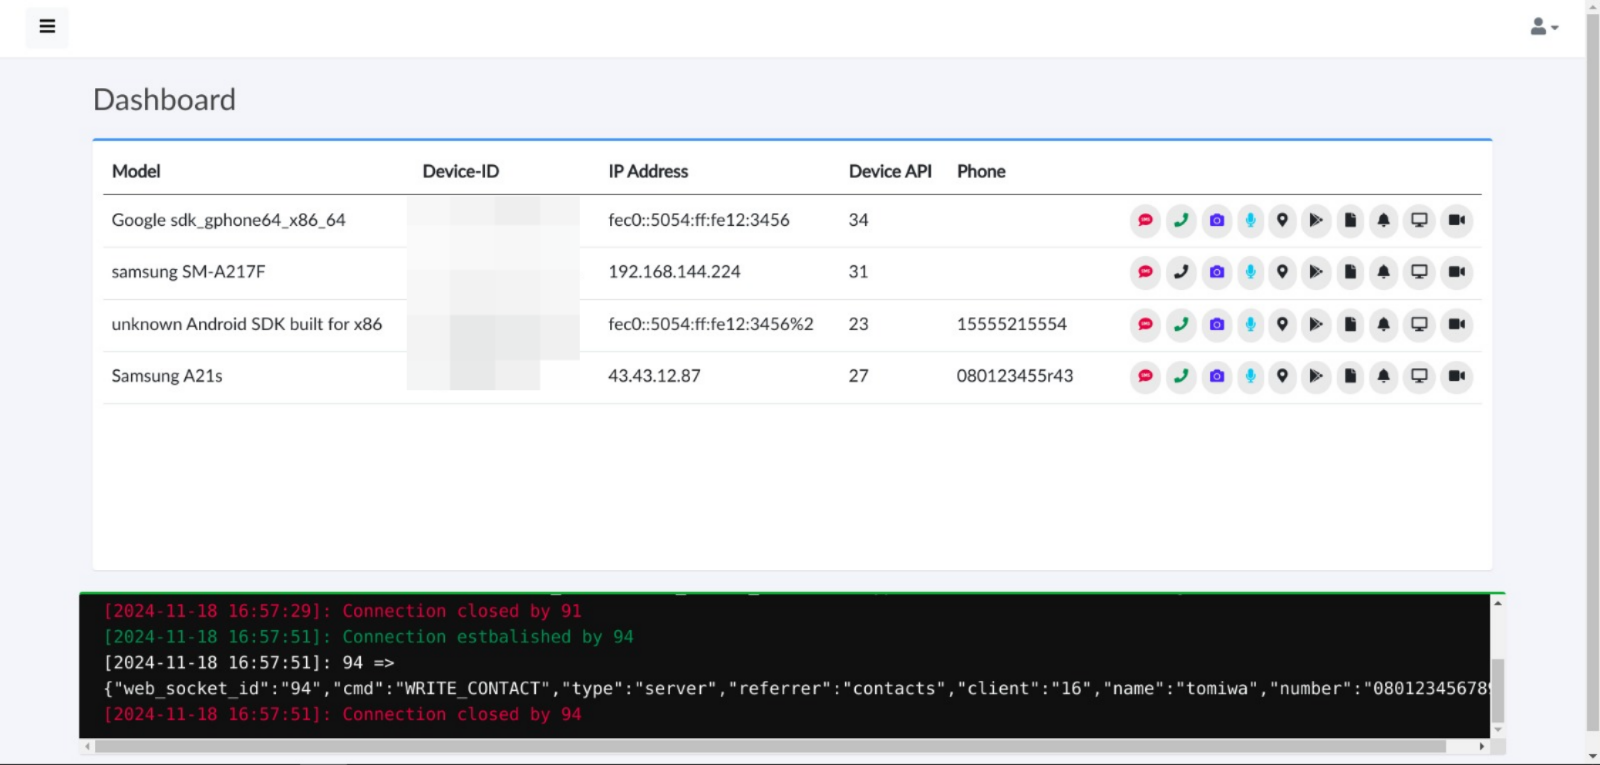 tomiwa-ot/moukthar
Android remote administration tool
 mwsrc/betterandrorat
Android Remote Access Trojan
 parsingteam/teleshadow2
TeleShadow - Telegram Desktop Session Stealer (Windows)
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
 mranonymoustz/cve-2019-11932-whatsapp-exploit
Double-free vulnerability in DDGifSlurp in decoding.c in libpl_droidsonroids_gif can read more…
 illwill/sub7
Source code for SubSeven 2.1.3
 infiniteloopers/cve-2019-2107
Proof-of-concept exploit for CVE-2019-2107, demonstrating remote code execution via crafted HEVC video on Android media framework. Includes crash…
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.