Powershell-RAT
 viralmaniar/powershell-rat
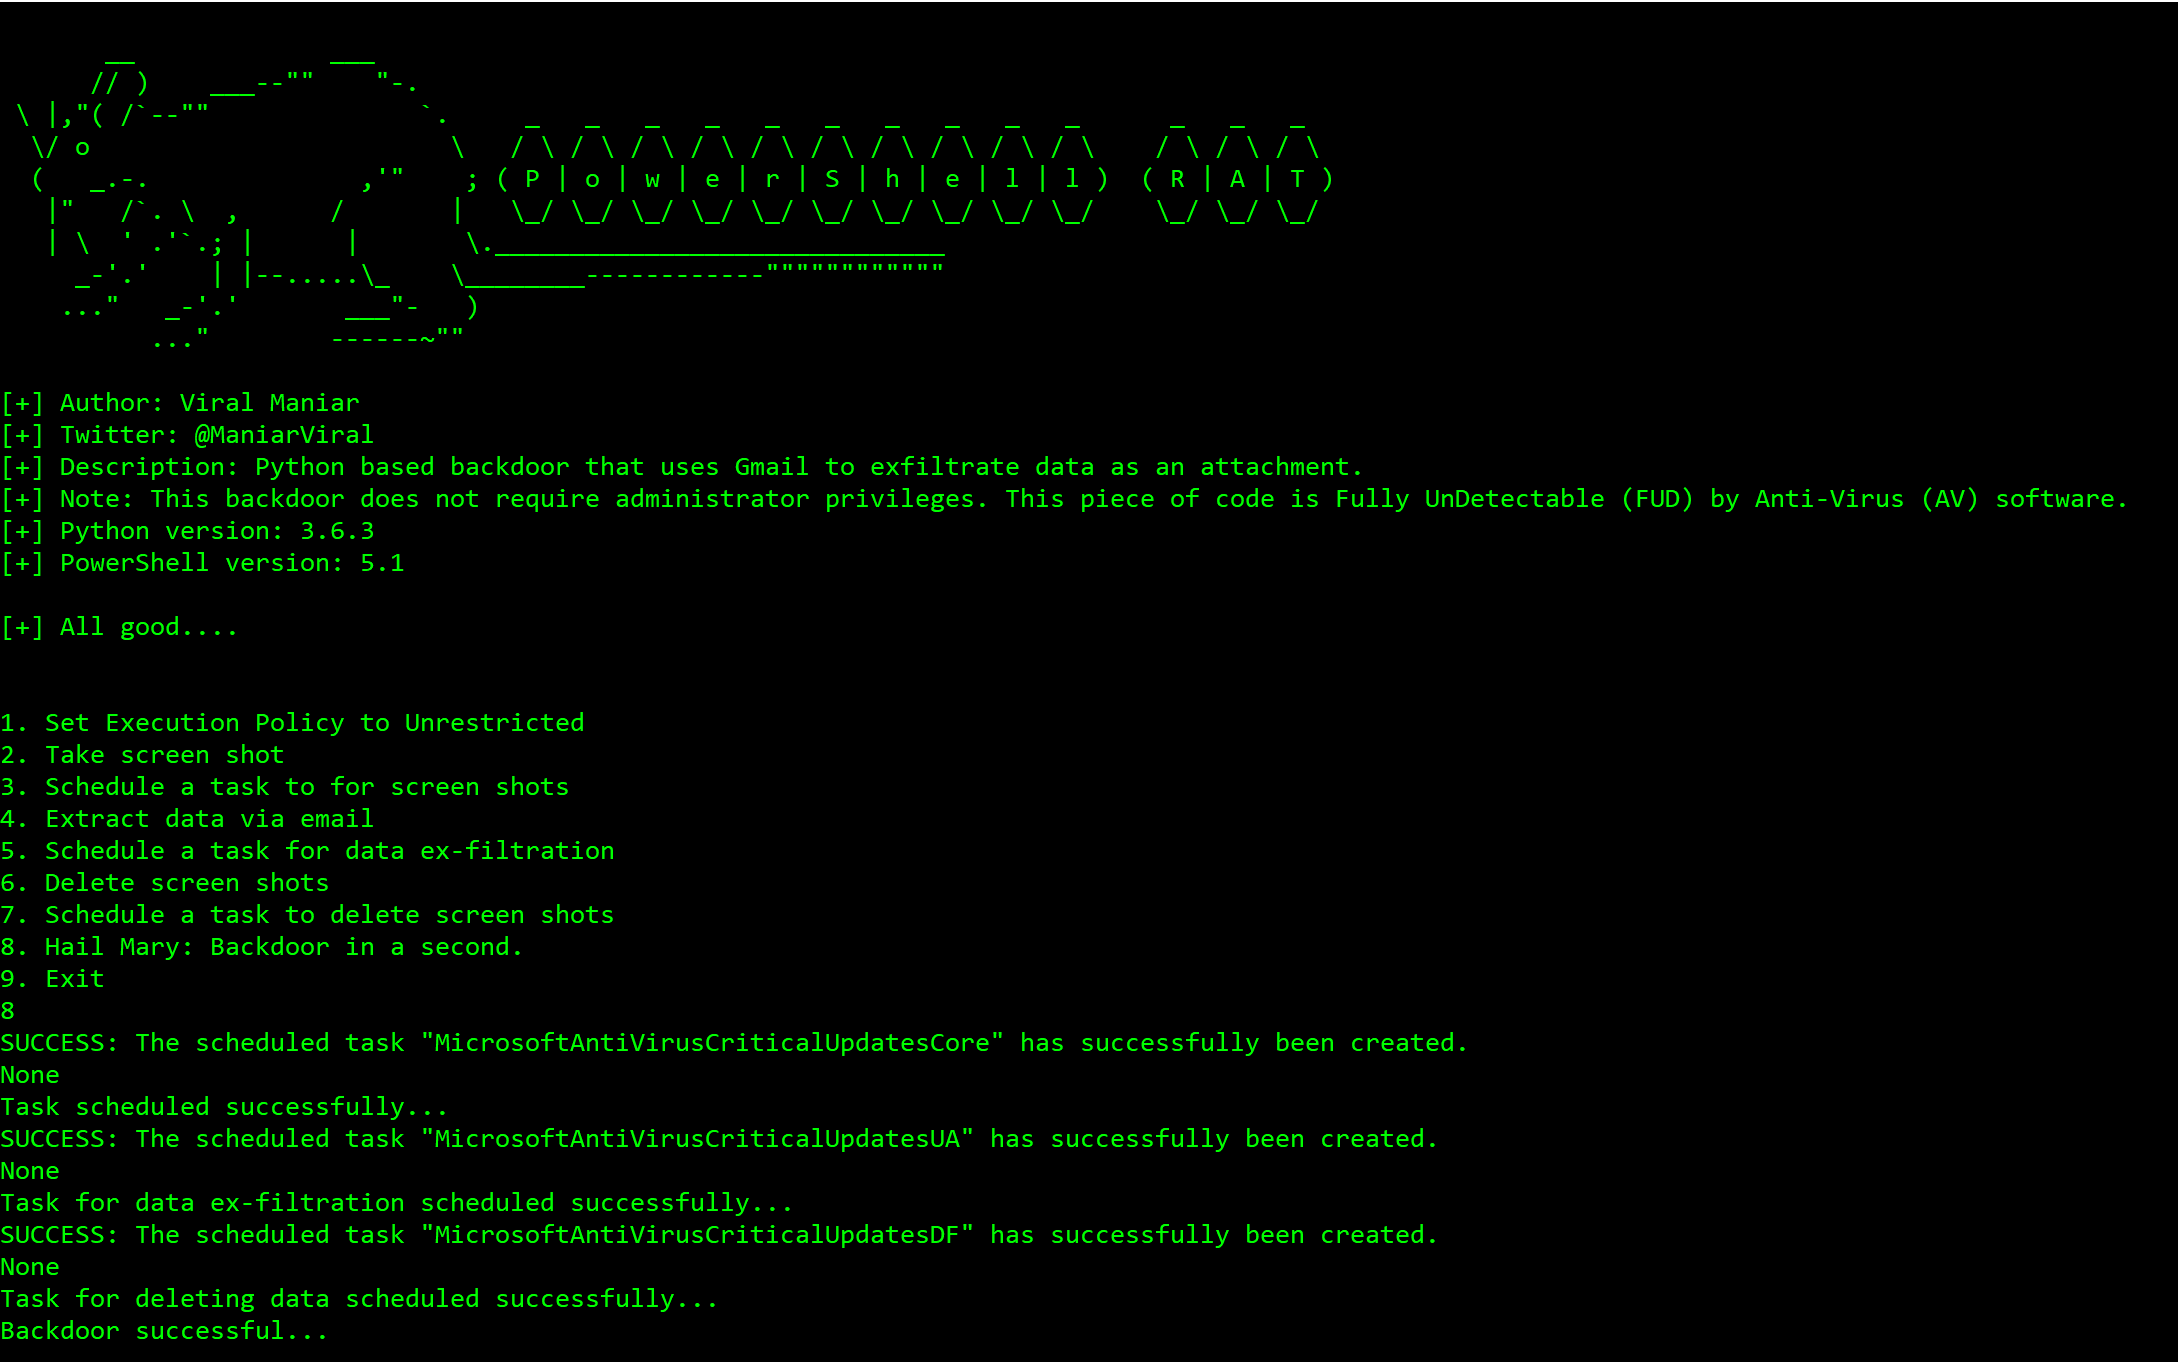
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
data-exfiltrationeducationpayload-generation+4
1.2k
viralmaniar/powershell-ratPython based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
 nyan-x-cat/asyncrat-c-sharp
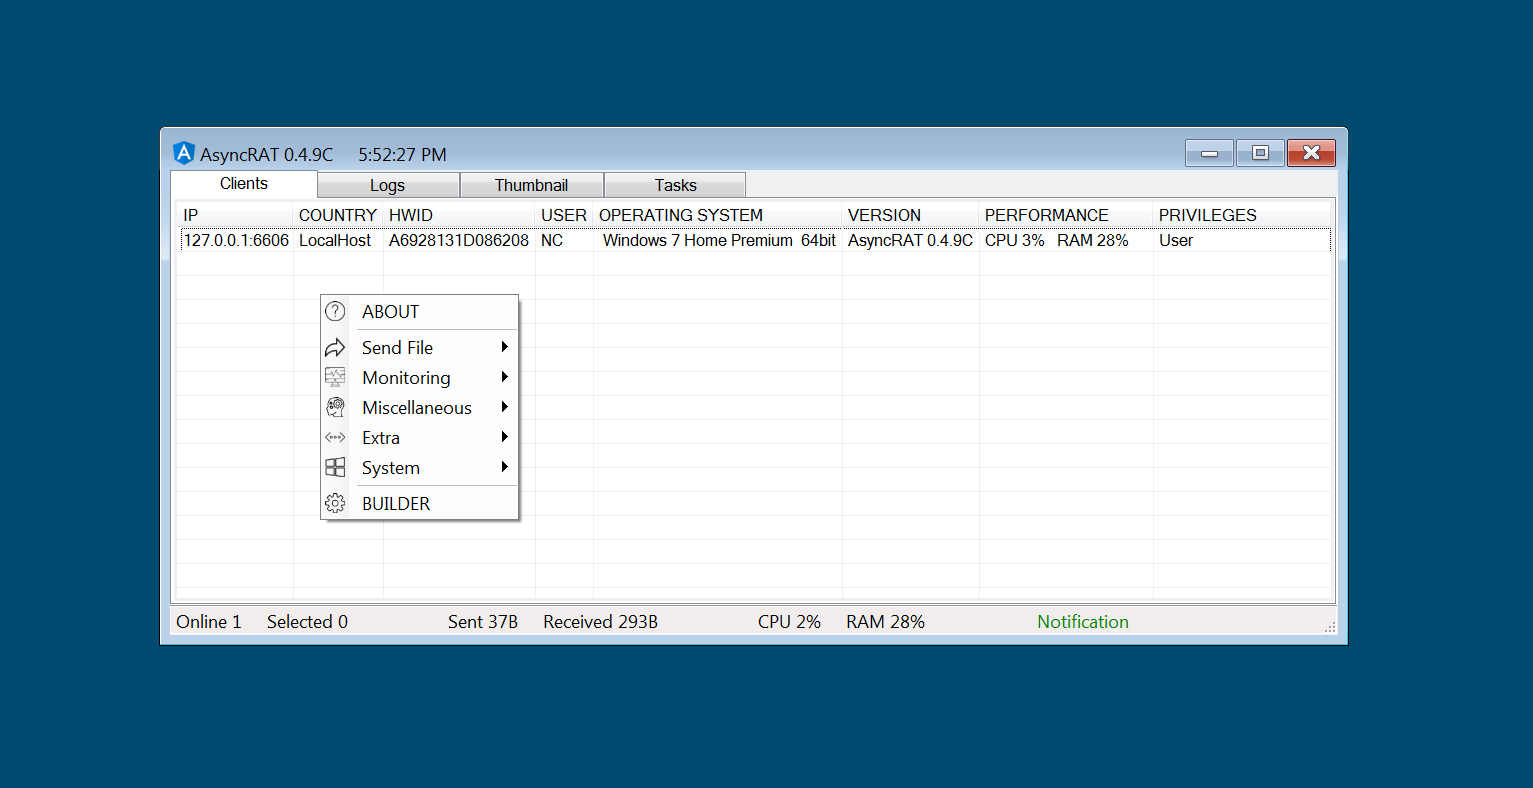
Open-Source Remote Administration Tool For Windows C# (RAT)
 igh0st/gh0st3.6_src
Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
 de3vil/stealing
The SteaLinG is an open-source penetration testing framework designed for social engineering
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 catatonicprime/tospovirus
A WiFi Pineapple infecting worm.
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 tiagorlampert/saint
👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
 sshuttle/sshuttle
Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
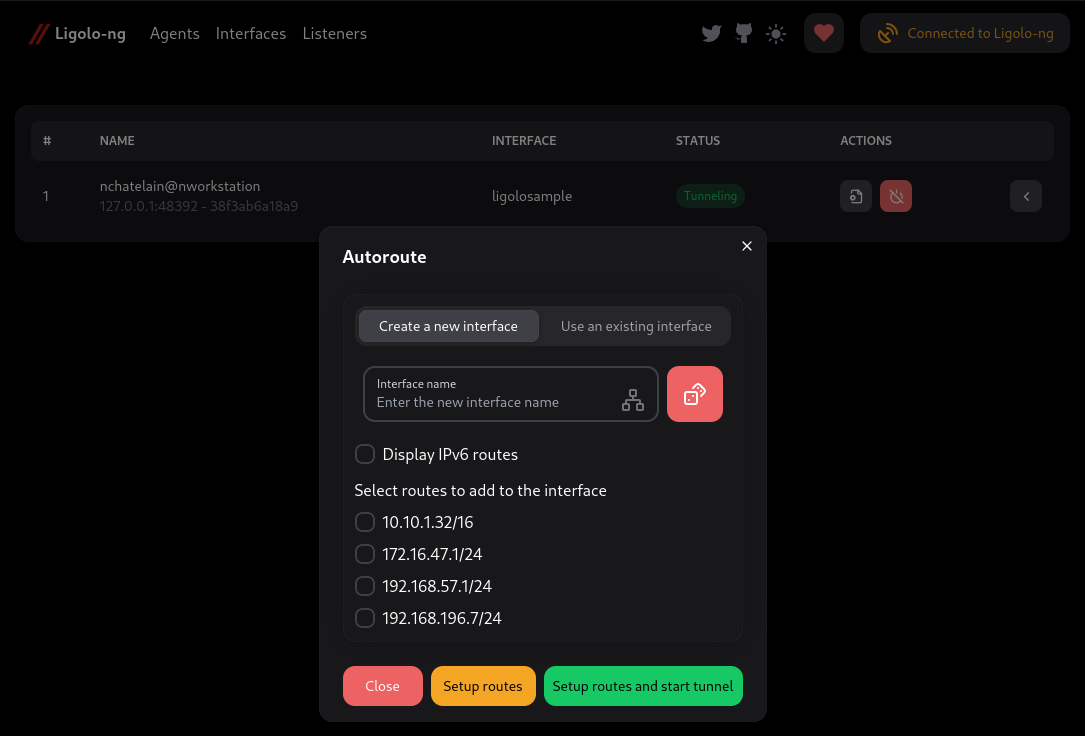 nicocha30/ligolo-ng
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 malwares/remote-access-trojan
Windows Remote-Access-Trojan
 xdnice/pcshare
PCShare是一款强大的远程控制软件,可以监视目标机器屏幕、注册表、文件系统等。
 mwsrc/plasmarat
Remote Access Trojan(RAT), Miner, DDoS