

emp3r0r
 jm33-m0/emp3r0r
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
anti-botcommand-and-controlids-ips-evasion+10
1.8k1 day ago
jm33-m0/emp3r0rSelf‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
 s3n4t0r-0x0/pixelcode-attack
Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
 maorbuskila/windows-x64-rat
Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 typetrait/pace
Remote Access Tool for Windows.
 nyan-x-cat/asyncrat-c-sharp
Open-Source Remote Administration Tool For Windows C# (RAT)
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 tiagorlampert/saint
👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
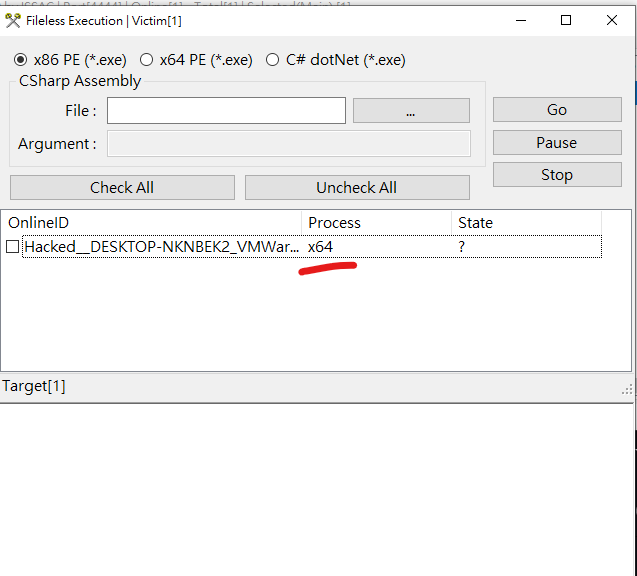 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 daddybigfish/cve-2025-59287-hawktrace
PoC for Remote Code Execution Vulnerability in Windows Server Update Service by Microsoft CVE-2025-59287 9.8 CRITICAL
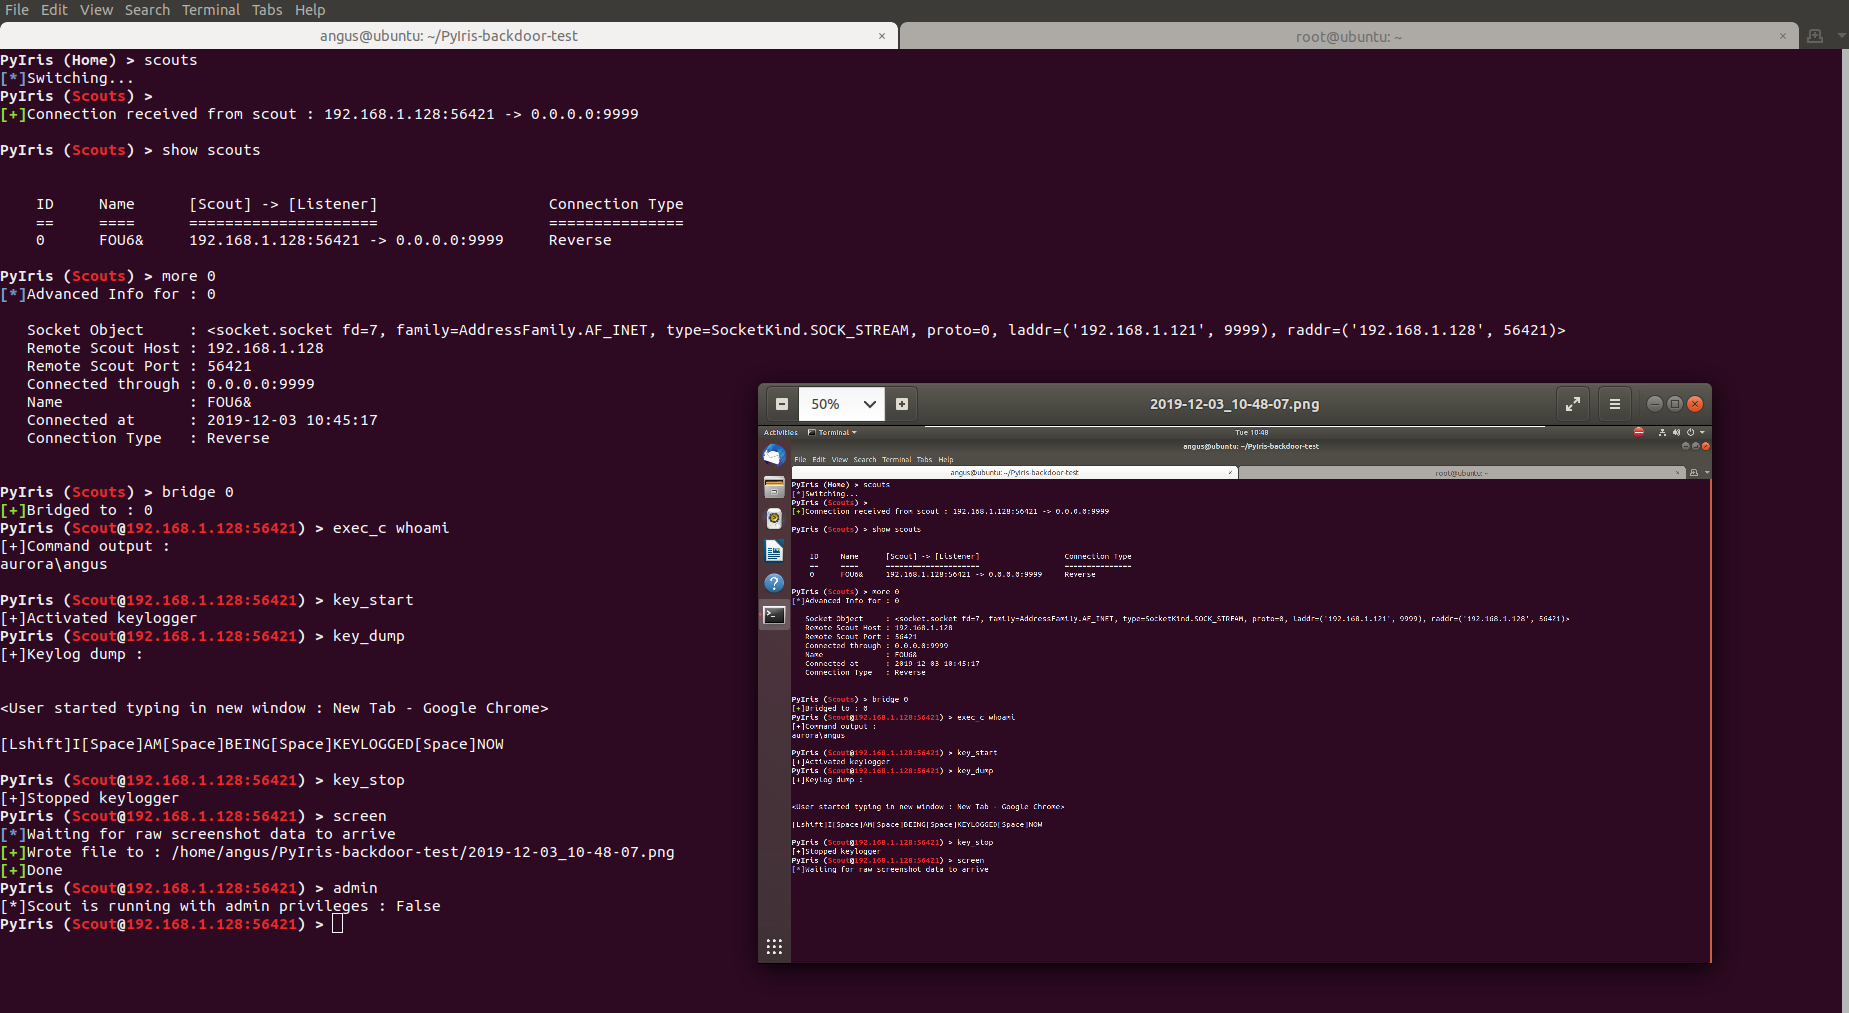 not-sekiun/pyiris
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 igh0st/gh0st3.6_src
Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
 rafabd1/cve-2026-75604-poc
Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…
 stphivos/rat-shell
Windows Remote Access Trojan (RAT)
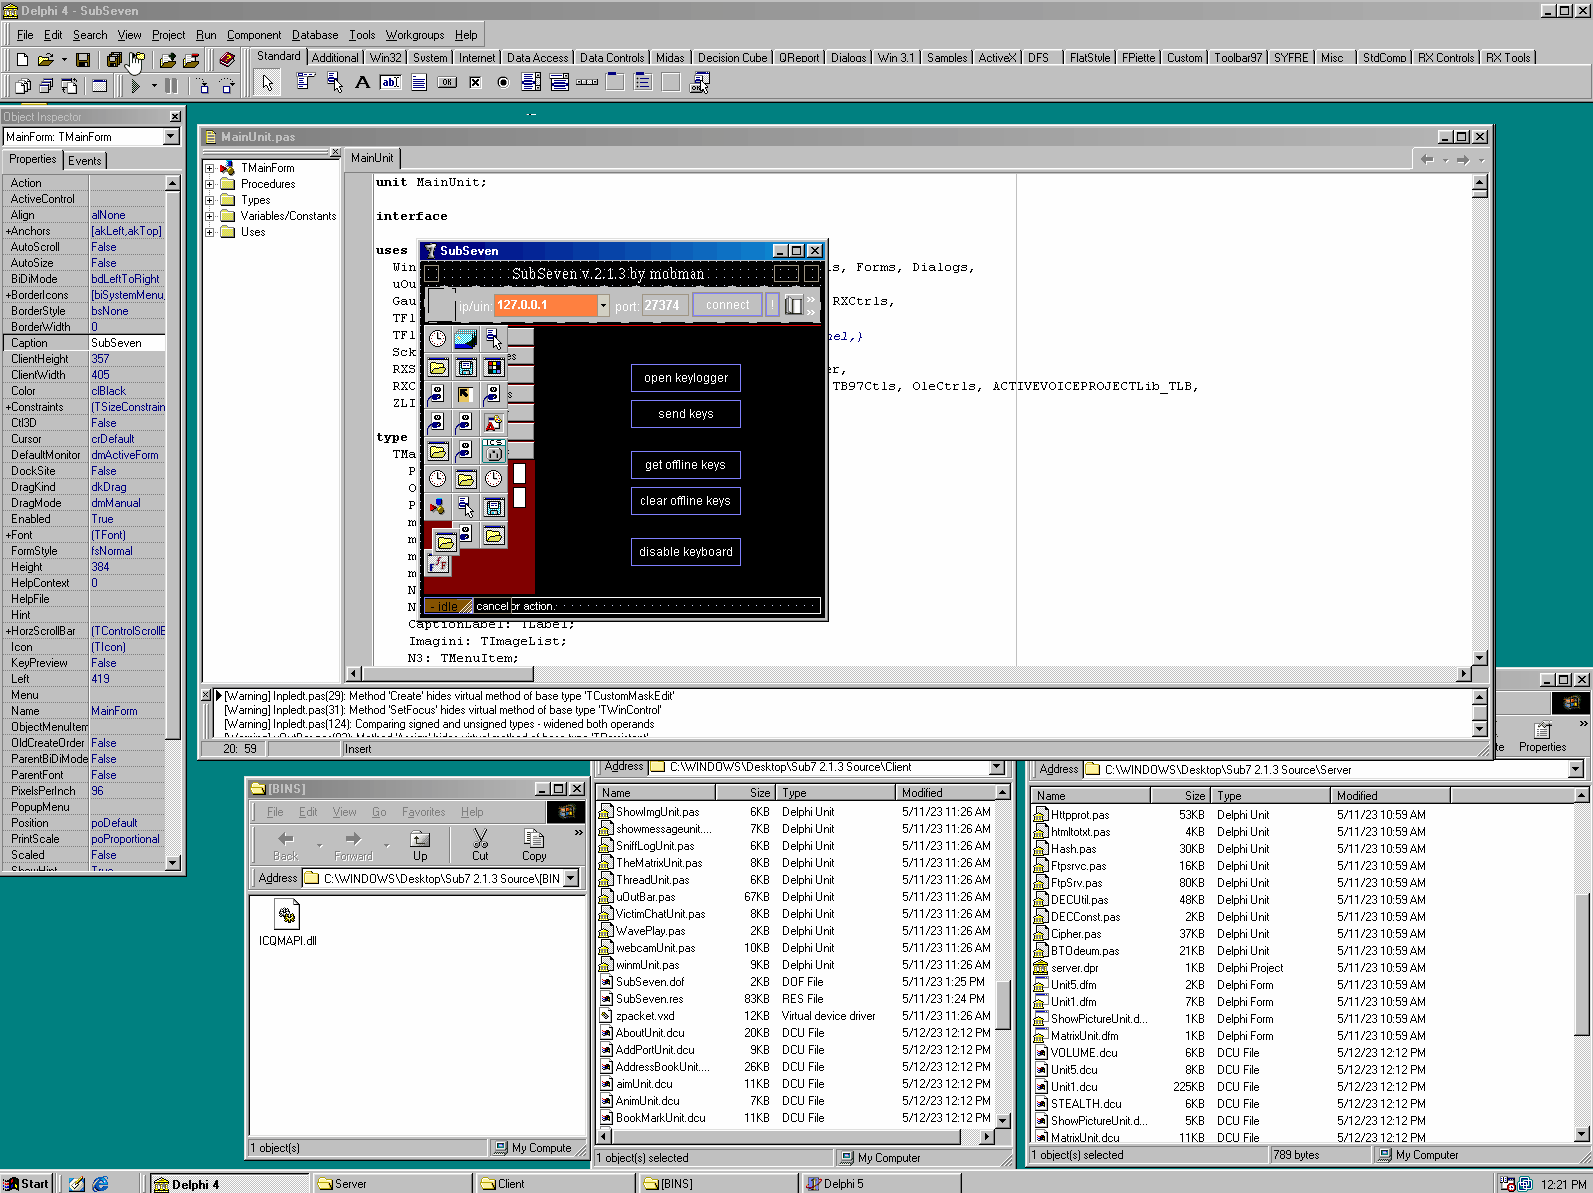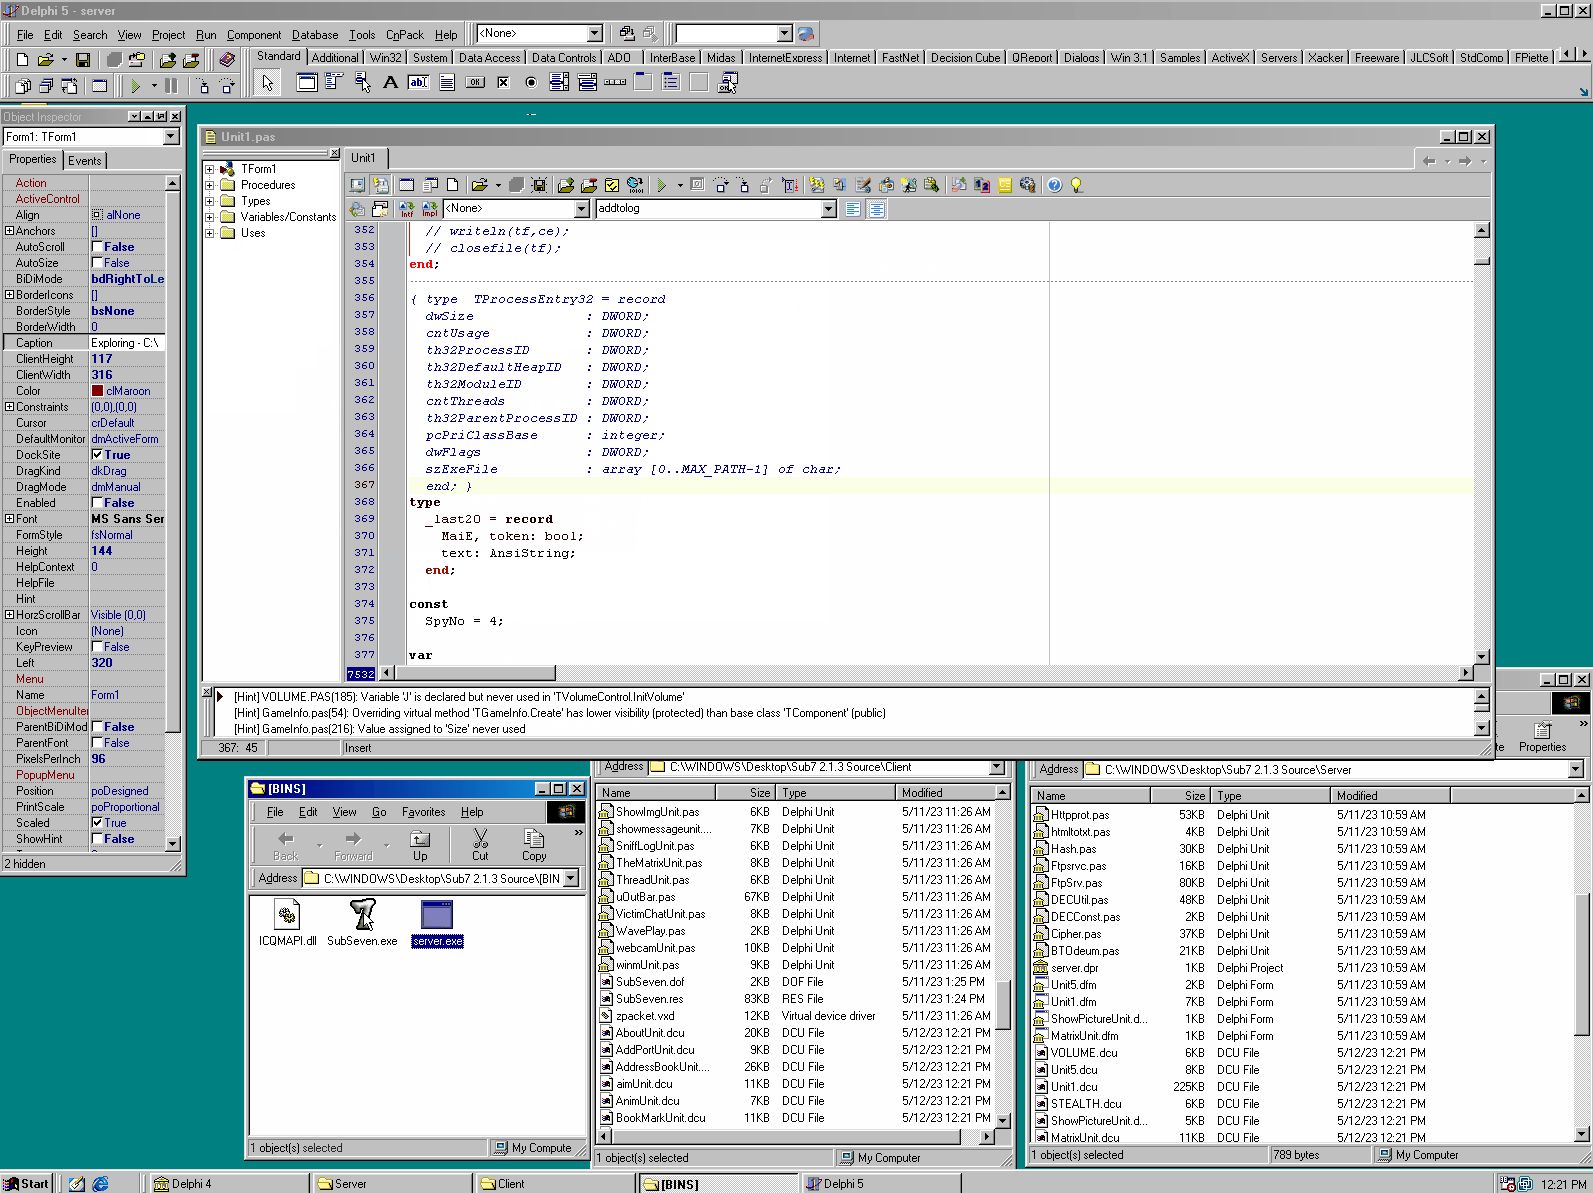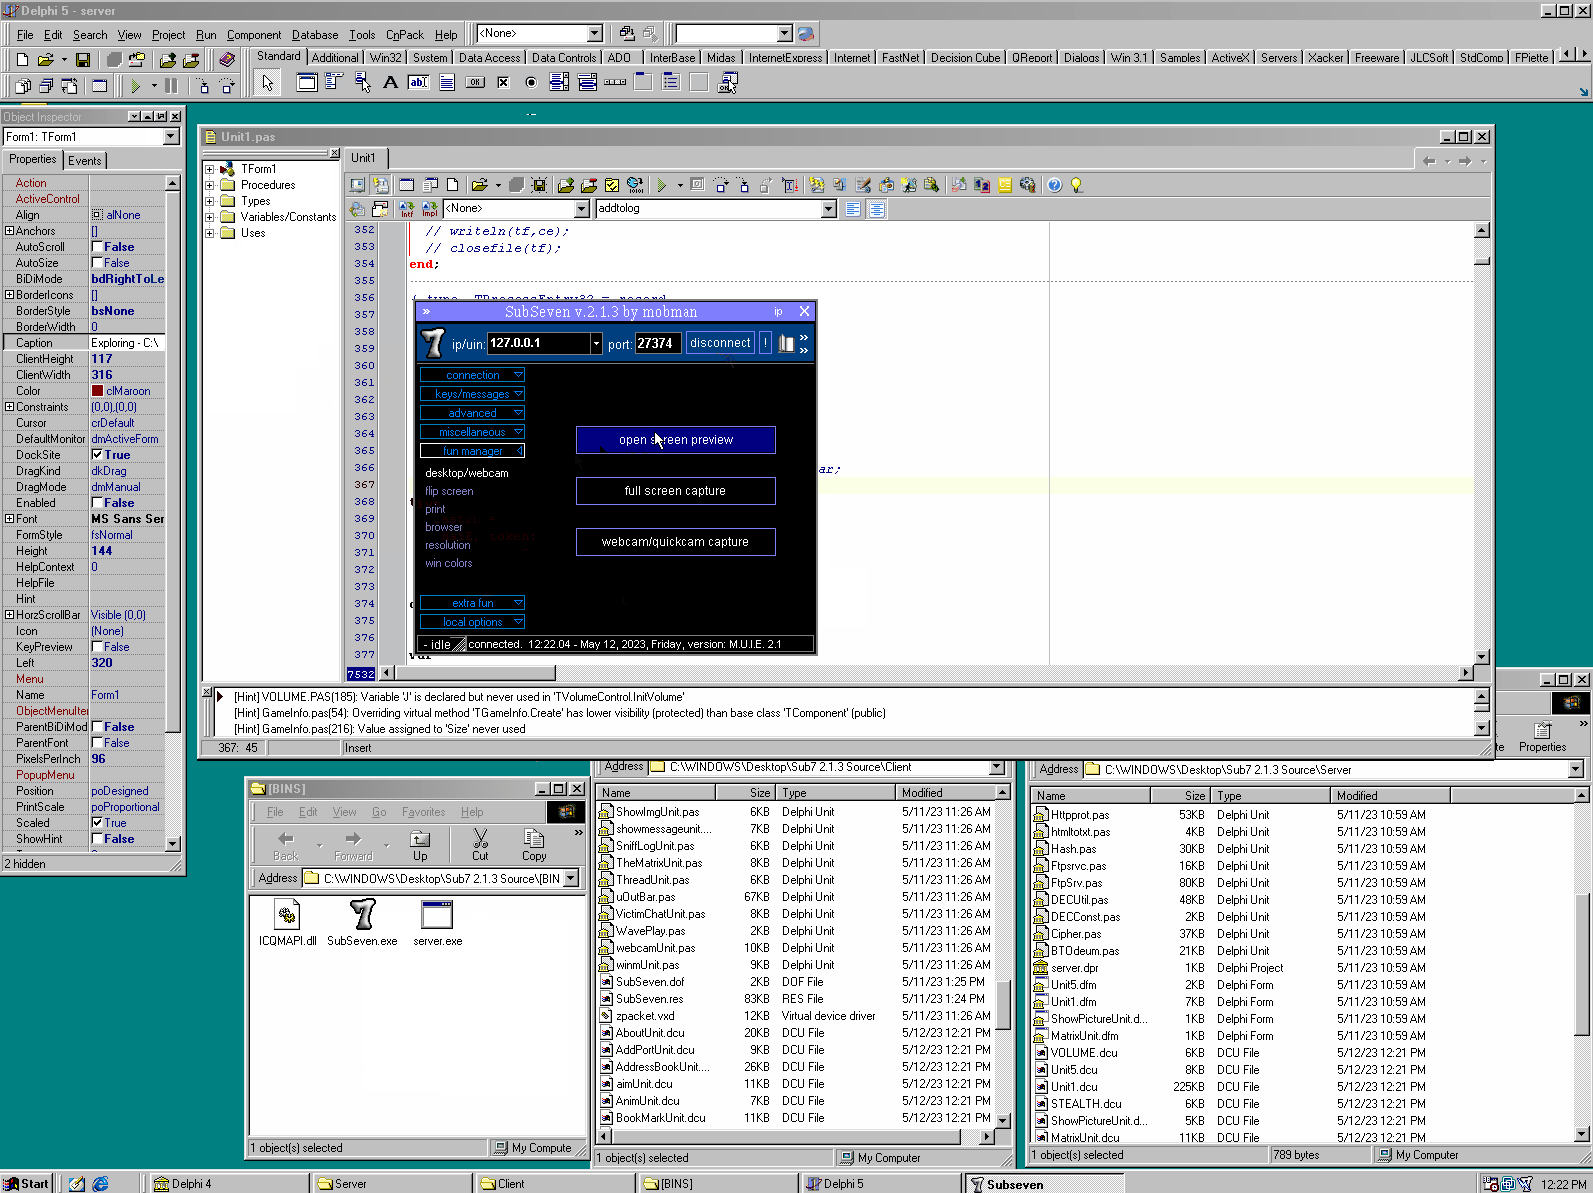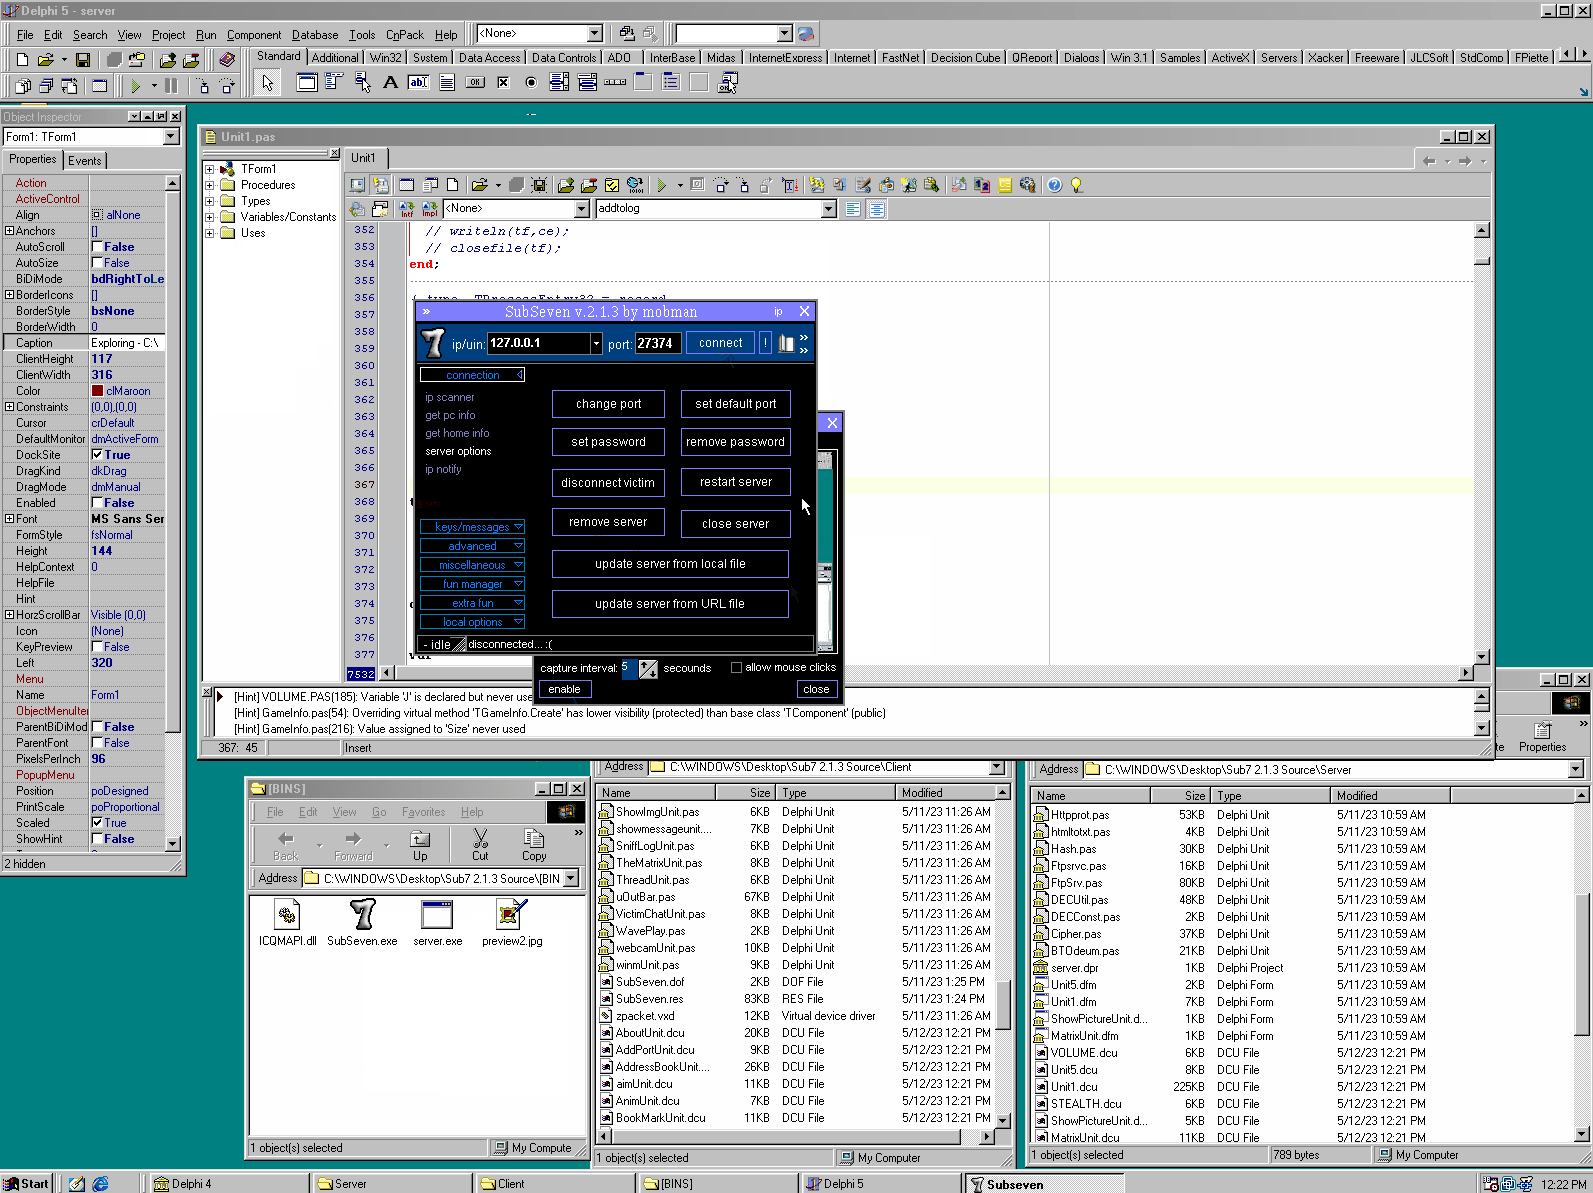
 illwill/sub7
Source code for SubSeven 2.1.3