

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
116 results
njRAT preview

njRAT

GitHubmwsrc/njrat

njRAT SRC Extract

command-and-controldata-exfiltrationexploitation+9
3159 years ago
emp3r0r preview

emp3r0r

GitHubjm33-m0/emp3r0r

Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.

anti-botcommand-and-controlids-ips-evasion+10
1.8k2 days ago
voidsyscall preview

voidsyscall

GitHubvoidsecsoftwares/voidsyscall

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
6427 days ago
C2-Pwn preview

C2-Pwn

GitHublukebob-zz/c2-pwn

Uses Shodan API to pull down C2 servers to run known exploits on them.

command-and-controlexploitationosint+3
198 years ago
lockjaw preview

lockjaw

GitHubg13net/lockjaw

Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
command-and-controldns-analysisexploit-frameworks+9
269 days ago
antnium preview
Archived

antnium

GitHubdobin/antnium

A C2 framework for initial access in Go
command-and-controldata-exfiltrationpayload-development+3
1994 years ago
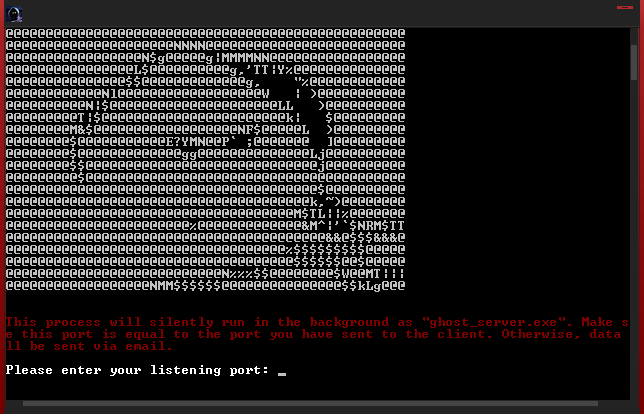
ghost preview

ghost

GitHubahxr/ghost

Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…

command-and-controleducationmalware-analysis+5
1.1k8 years ago
LazyOwn preview

LazyOwn

GitHubgrisuno/lazyown

Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…

ai-securitycommand-and-controlexploit-frameworks+8
2854 days ago
gh0st3.6_src preview

gh0st3.6_src

GitHubigh0st/gh0st3.6_src

Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.

command-and-controldata-exfiltrationpayload-development+3
17012 years ago
FUD-C2-Framework preview

FUD-C2-Framework

GitHubx3r0day/fud-c2-framework

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

command-and-controlencryption-decryption-toolsids-ips-evasion+9
75 months ago
Amaranth-Project preview

Amaranth-Project

GitHublewis-ricardo/amaranth-project

CVE-2025-8088 exploitation chain + Quasar C2 multi-stage payload delivery

command-and-controleducationexploitation+6
3 months ago
Discord-Rat preview

Discord-Rat

GitHubgmh5225/discord-rat

Python-based Discord RAT with remote command panel for webcam capture, audio recording, keylogging, file exfiltration, and persistence via Discord…

command-and-controldata-exfiltrationencryption-decryption-tools+7
1 year ago
DesckVB-RAT preview

DesckVB-RAT

GitHubshadowopcode/desckvb-rat

Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
command-and-controldigital-forensicseducation+8
98 months ago
zeek-asyncrat-detector preview

zeek-asyncrat-detector

GitHubcorelight/zeek-asyncrat-detector

A Zeek based AsyncRAT malware detector.

anomaly-detectioncommand-and-controlintrusion-detection+3
31 year ago
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework

adversarial-attackcommand-and-controldata-exfiltration+16
12.0k3 days ago
merlin preview

merlin

GitHubne0nd0g/merlin

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

command-and-controldata-exfiltrationexploit-frameworks+10
5.6k4 days ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k1 month ago
PyIris preview

PyIris

GitHubnot-sekiun/pyiris

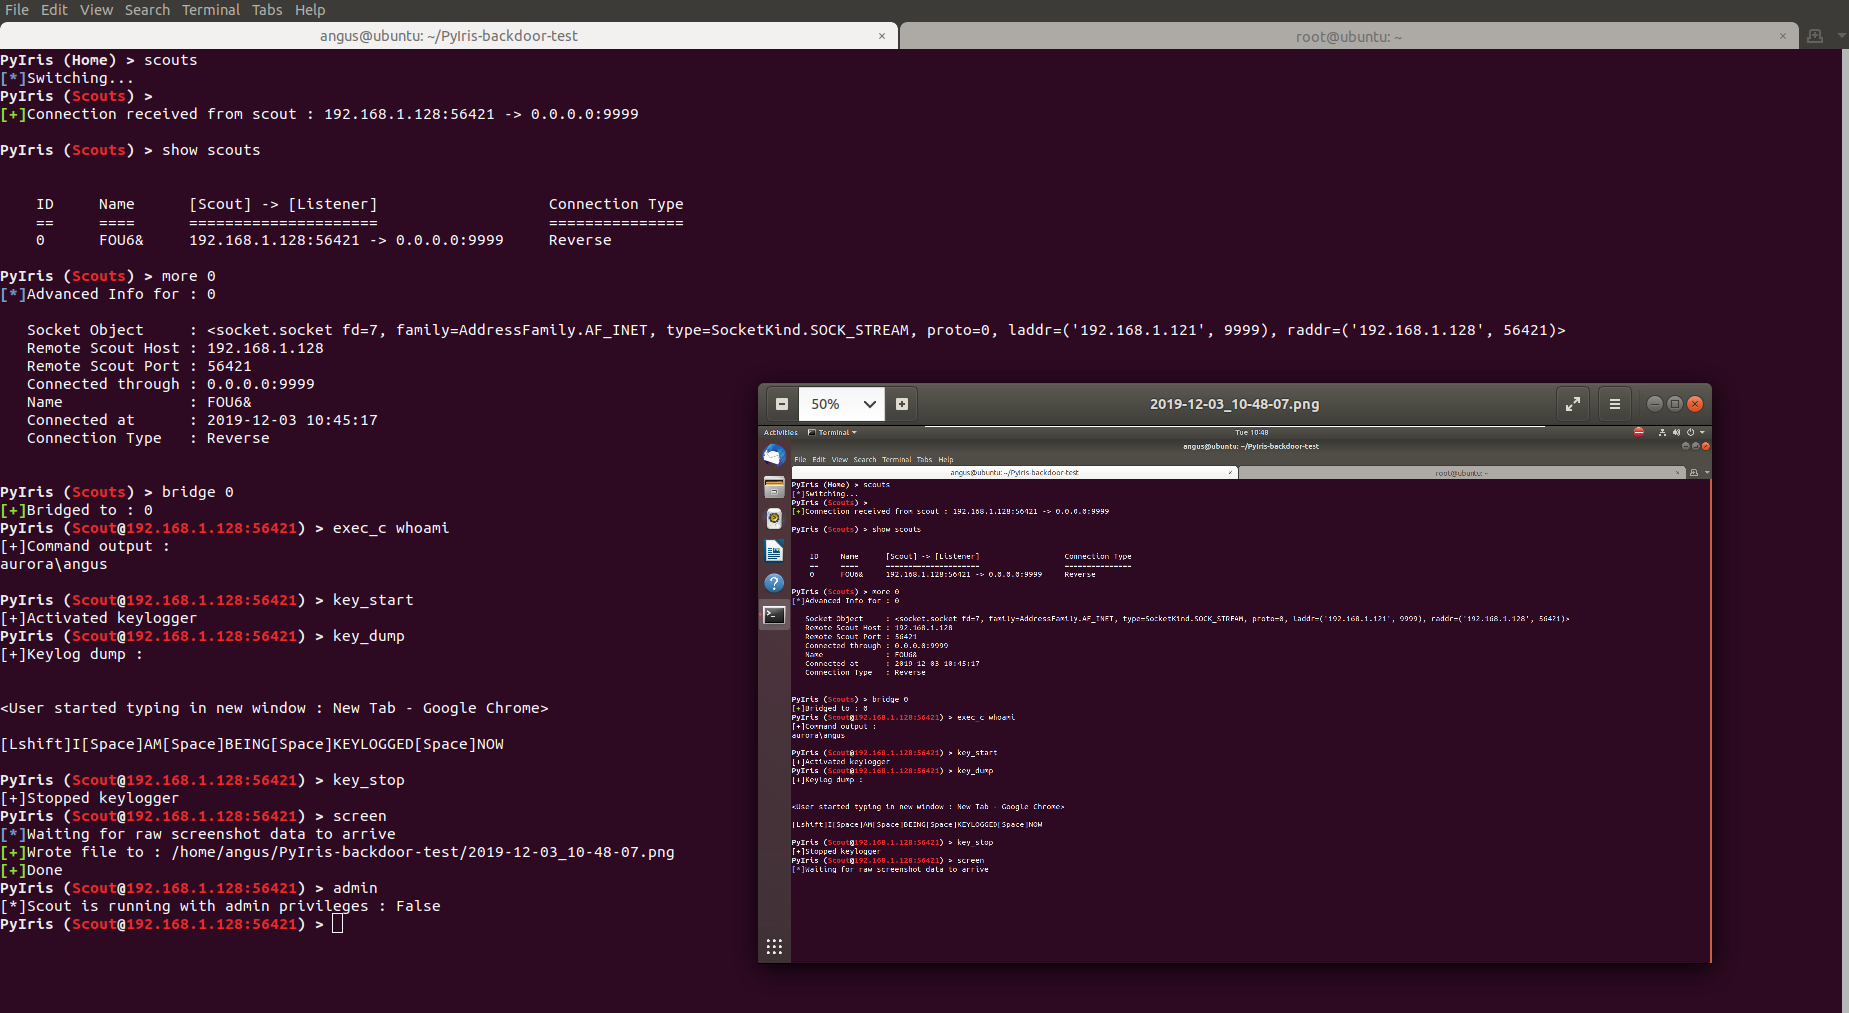
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.

command-and-controlexploitationpayload-generation+4
32722 days ago
Previous1234567Next