
Schwarze-Sonne-RAT
 mwsrc/schwarze-sonne-rat
SS-RAT (Schwarze-Sonne-Remote-Access-Trojan)
command-and-controldata-exfiltrationlateral-movement+6
29
mwsrc/schwarze-sonne-ratSS-RAT (Schwarze-Sonne-Remote-Access-Trojan)
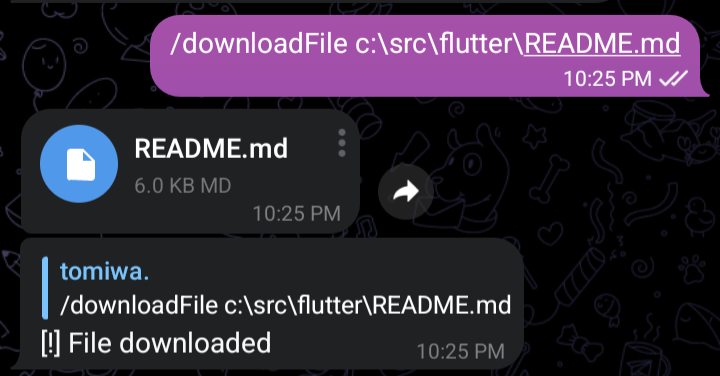 tomiwa-ot/telegram-c2
Control a system remotely via telegram
 correcthorsebatterystaple-sudo/orwell-rat-and-botnet
Orwell is a RAT and Botnet designed as a trio of programs.
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 chebuya/cve-2024-30850-chaos-rat-rce-poc
CHAOS RAT web panel path RCE PoC
 gbrn1/pirate
Python Remote Access Tool
 hakaioffsec/cve-2026-33725
Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…
 artbitrage/stealth-kid-rat
Stealth Kid RAT (SKR) is an open-source multi-platform Remote Access Trojan (RAT) written in C#. Released under MIT license. The SKR project is fully…
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.
 mranonymoustz/cve-2019-11932-whatsapp-exploit
Double-free vulnerability in DDGifSlurp in decoding.c in libpl_droidsonroids_gif can read more…
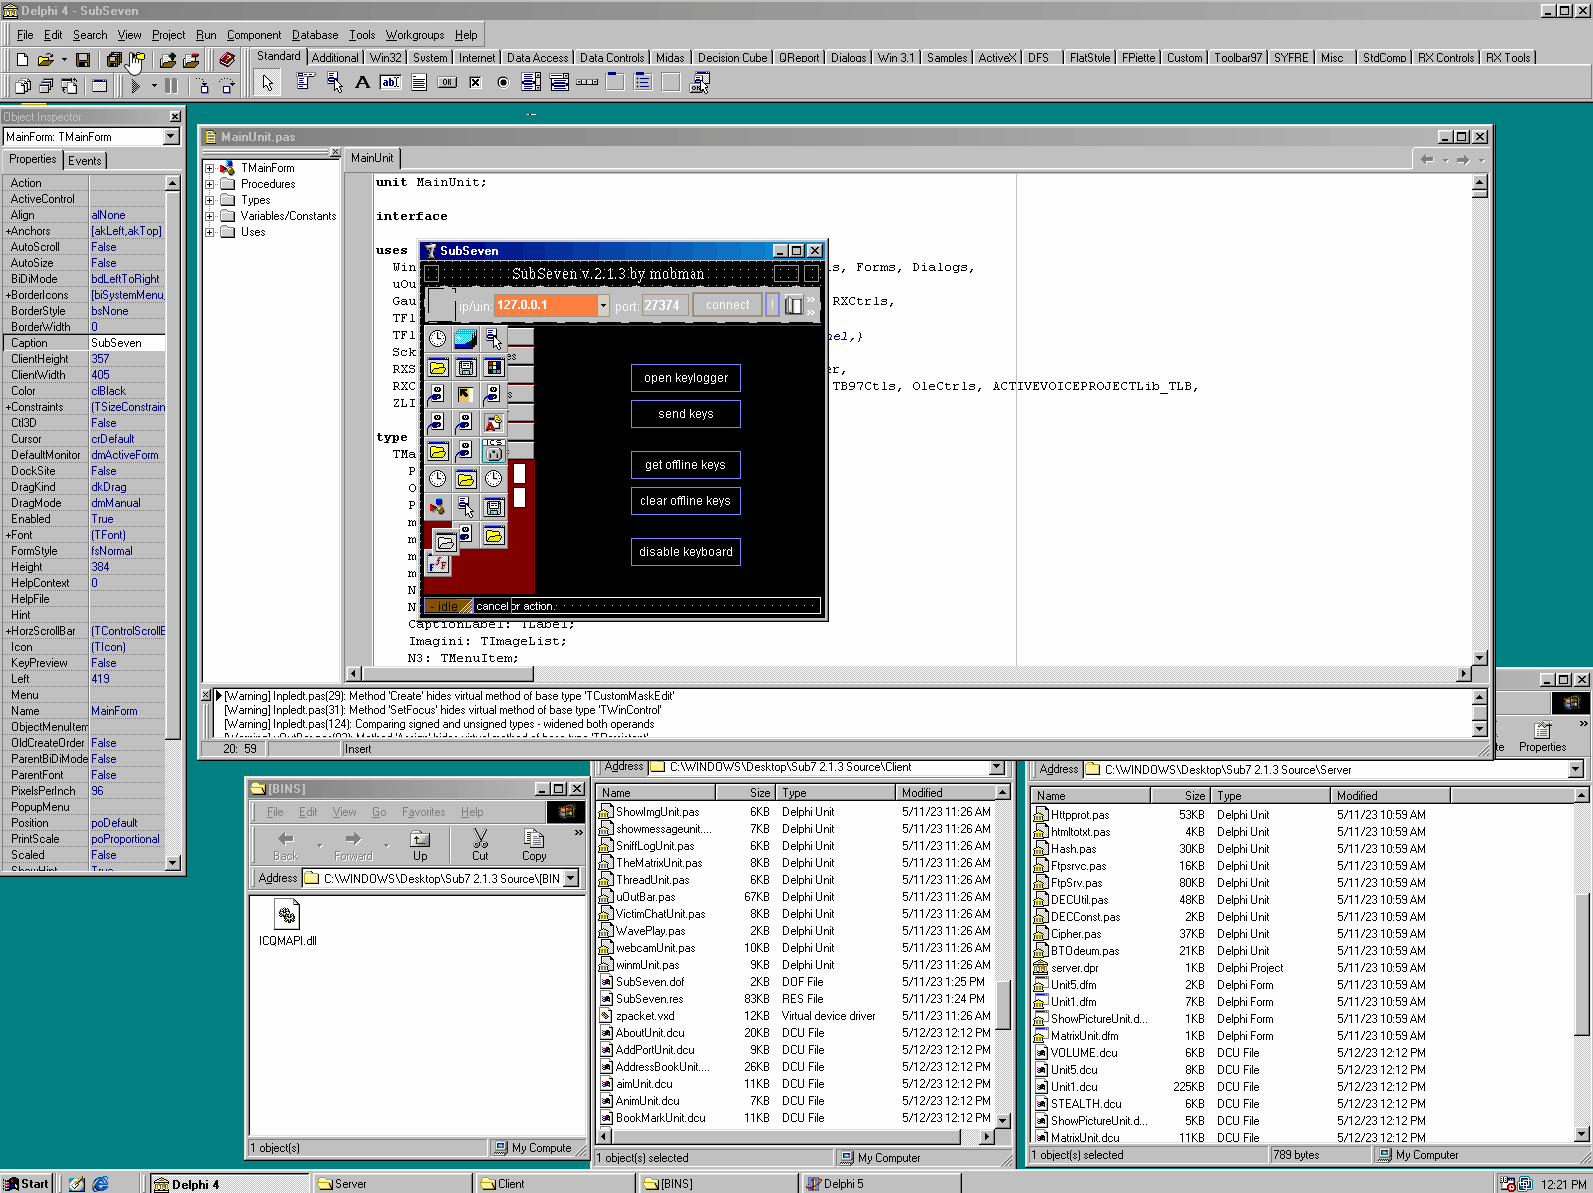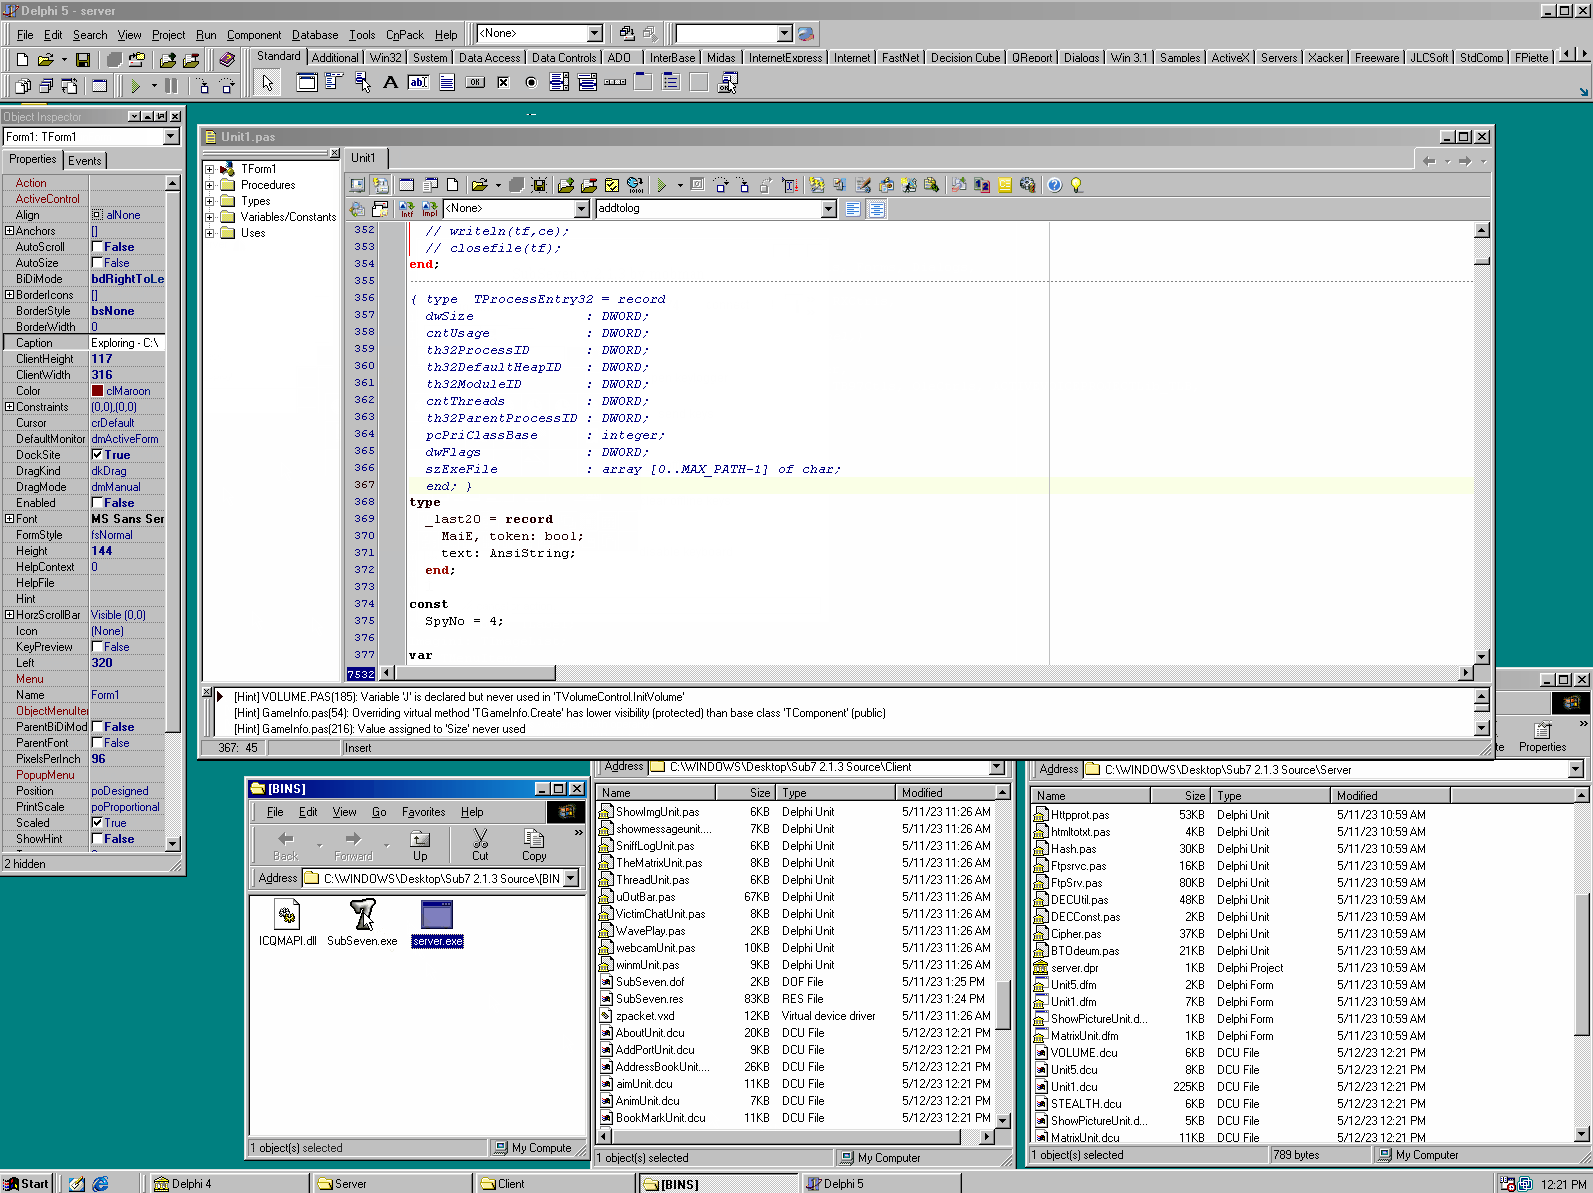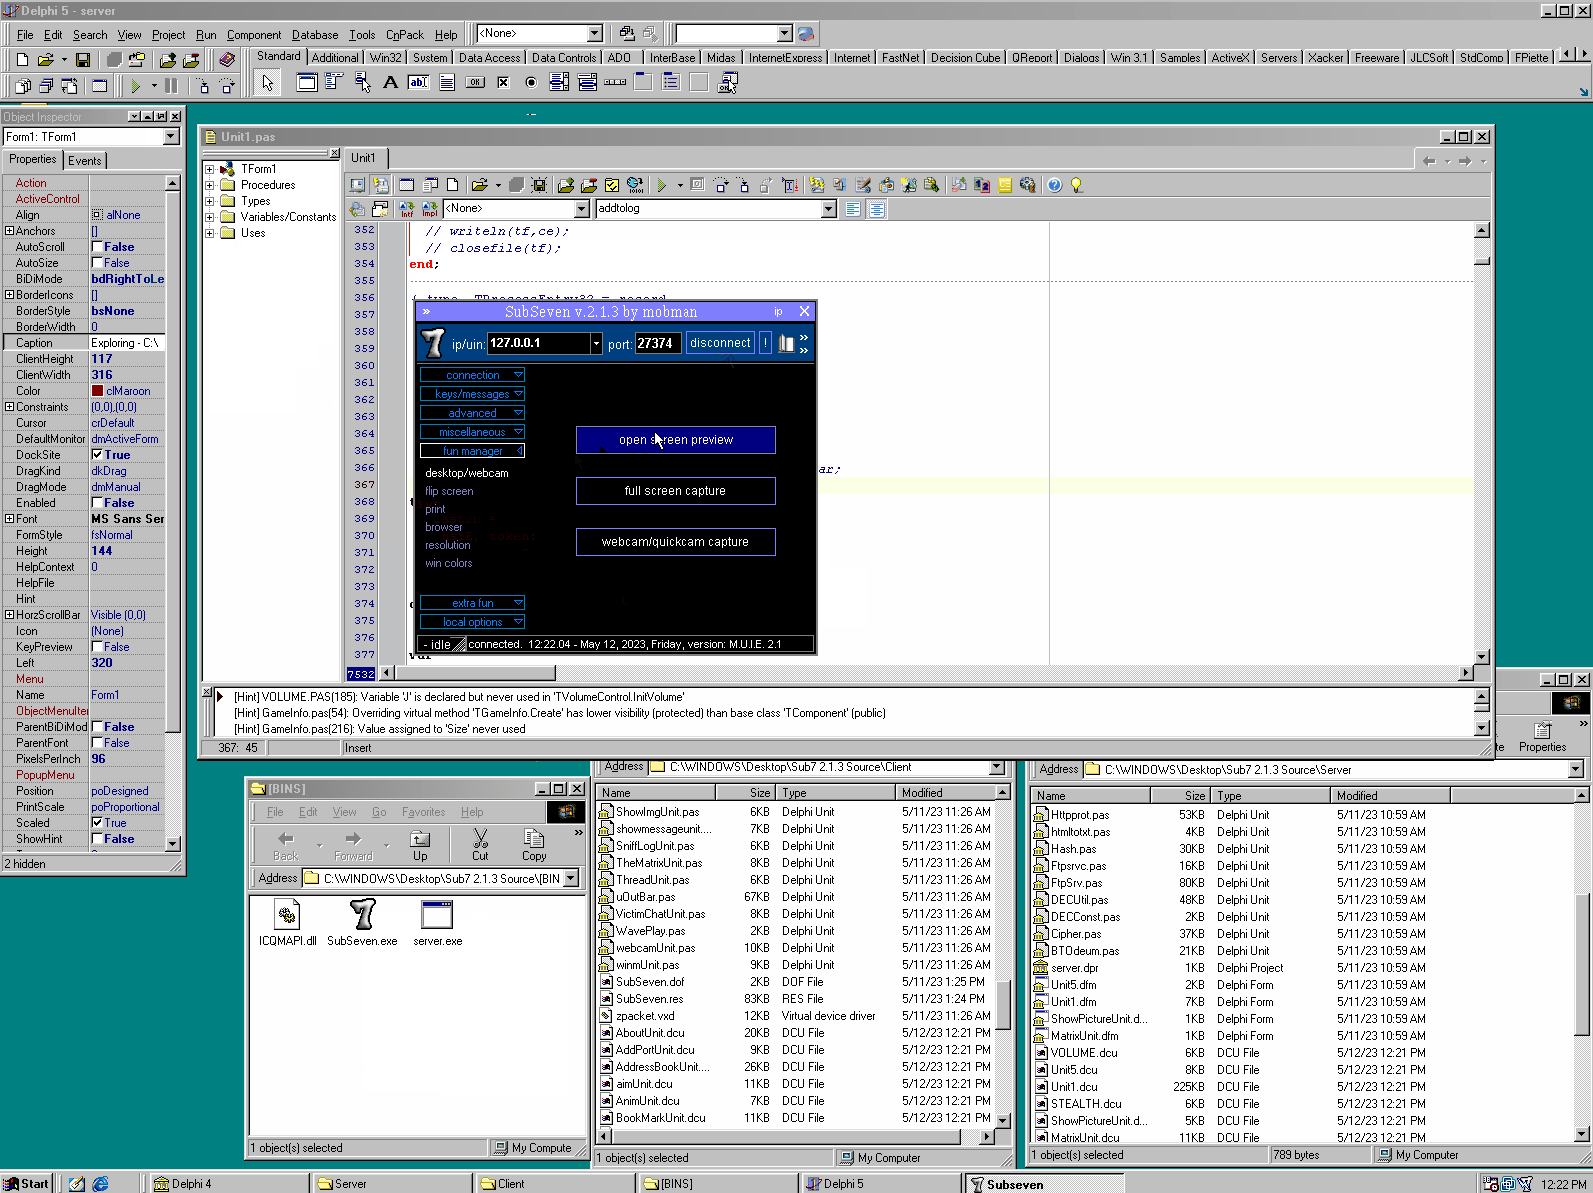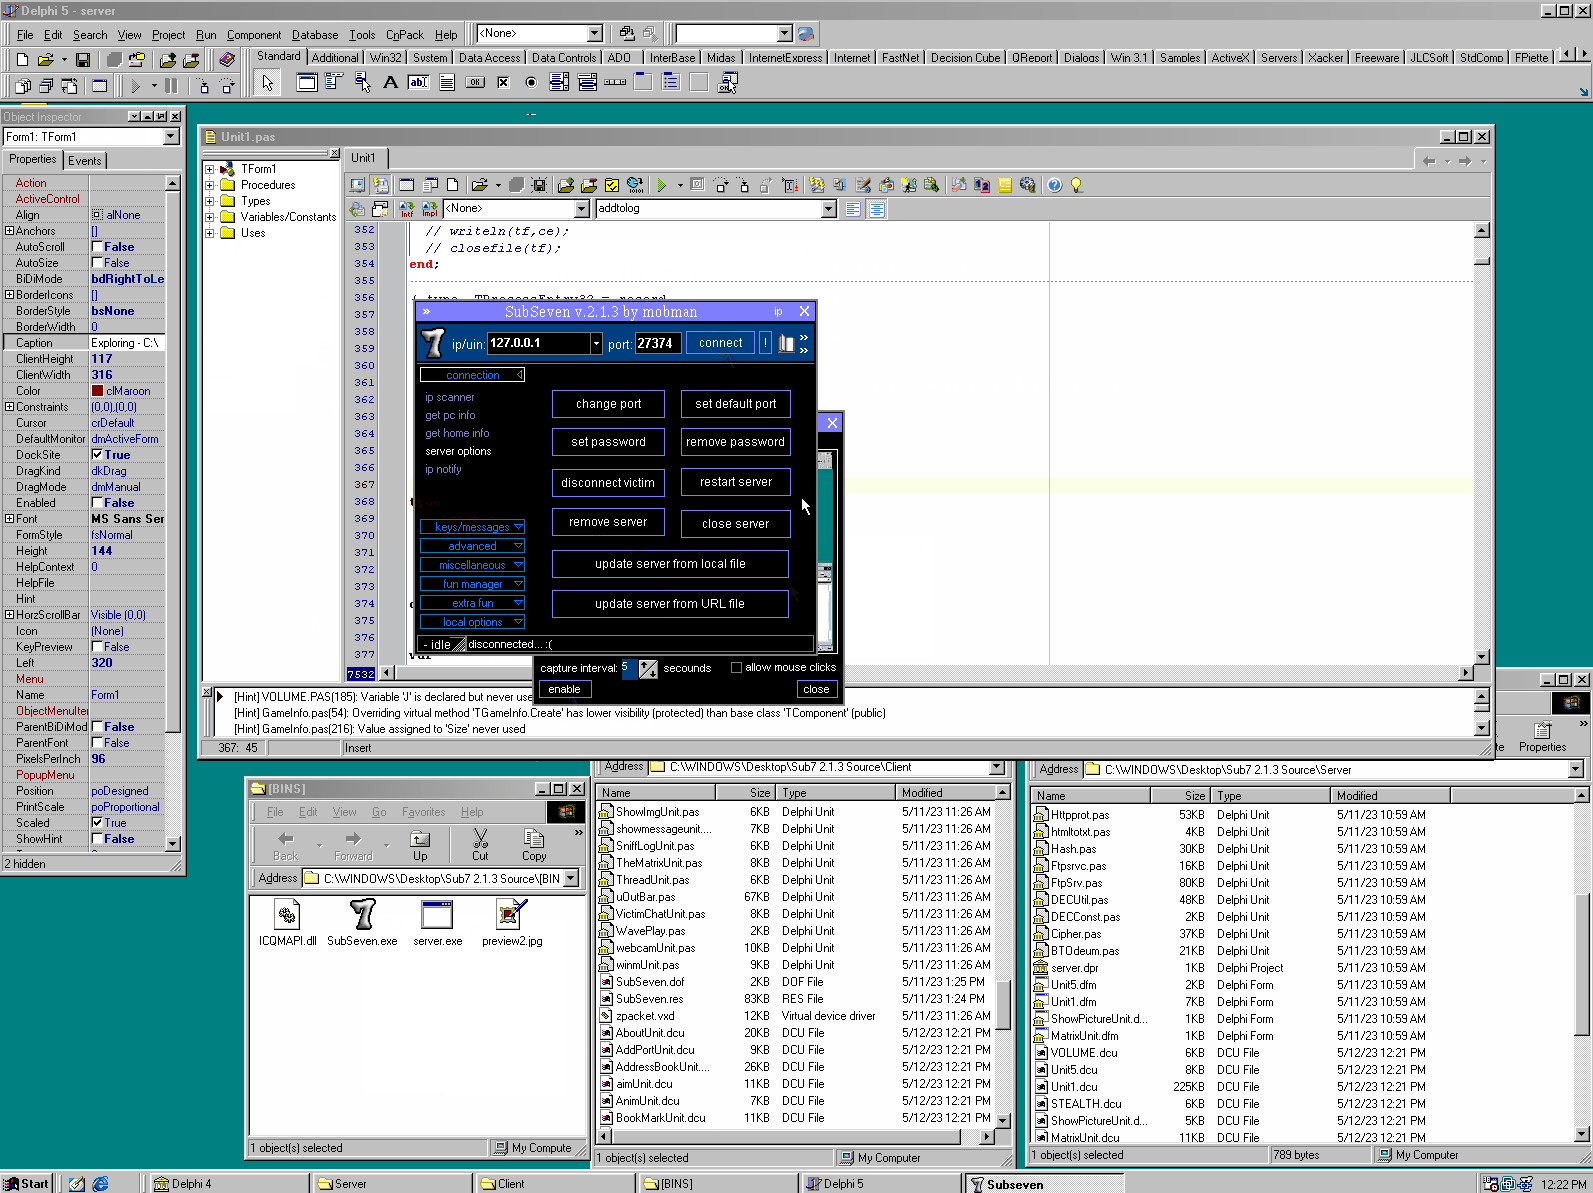
 illwill/sub7
Source code for SubSeven 2.1.3
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 catatonicprime/tospovirus
A WiFi Pineapple infecting worm.
 ianxtianxt/teamview
Generates TeamViewer ID and password payloads for remote access to target machines. Combines executable generation with third-party remote control…
 tam-k592/cve-2025-55752
Detects and exploits Apache Tomcat CVE-2025-55752 directory traversal via Rewrite Valve, enabling PUT-based JSP upload and remote code execution.
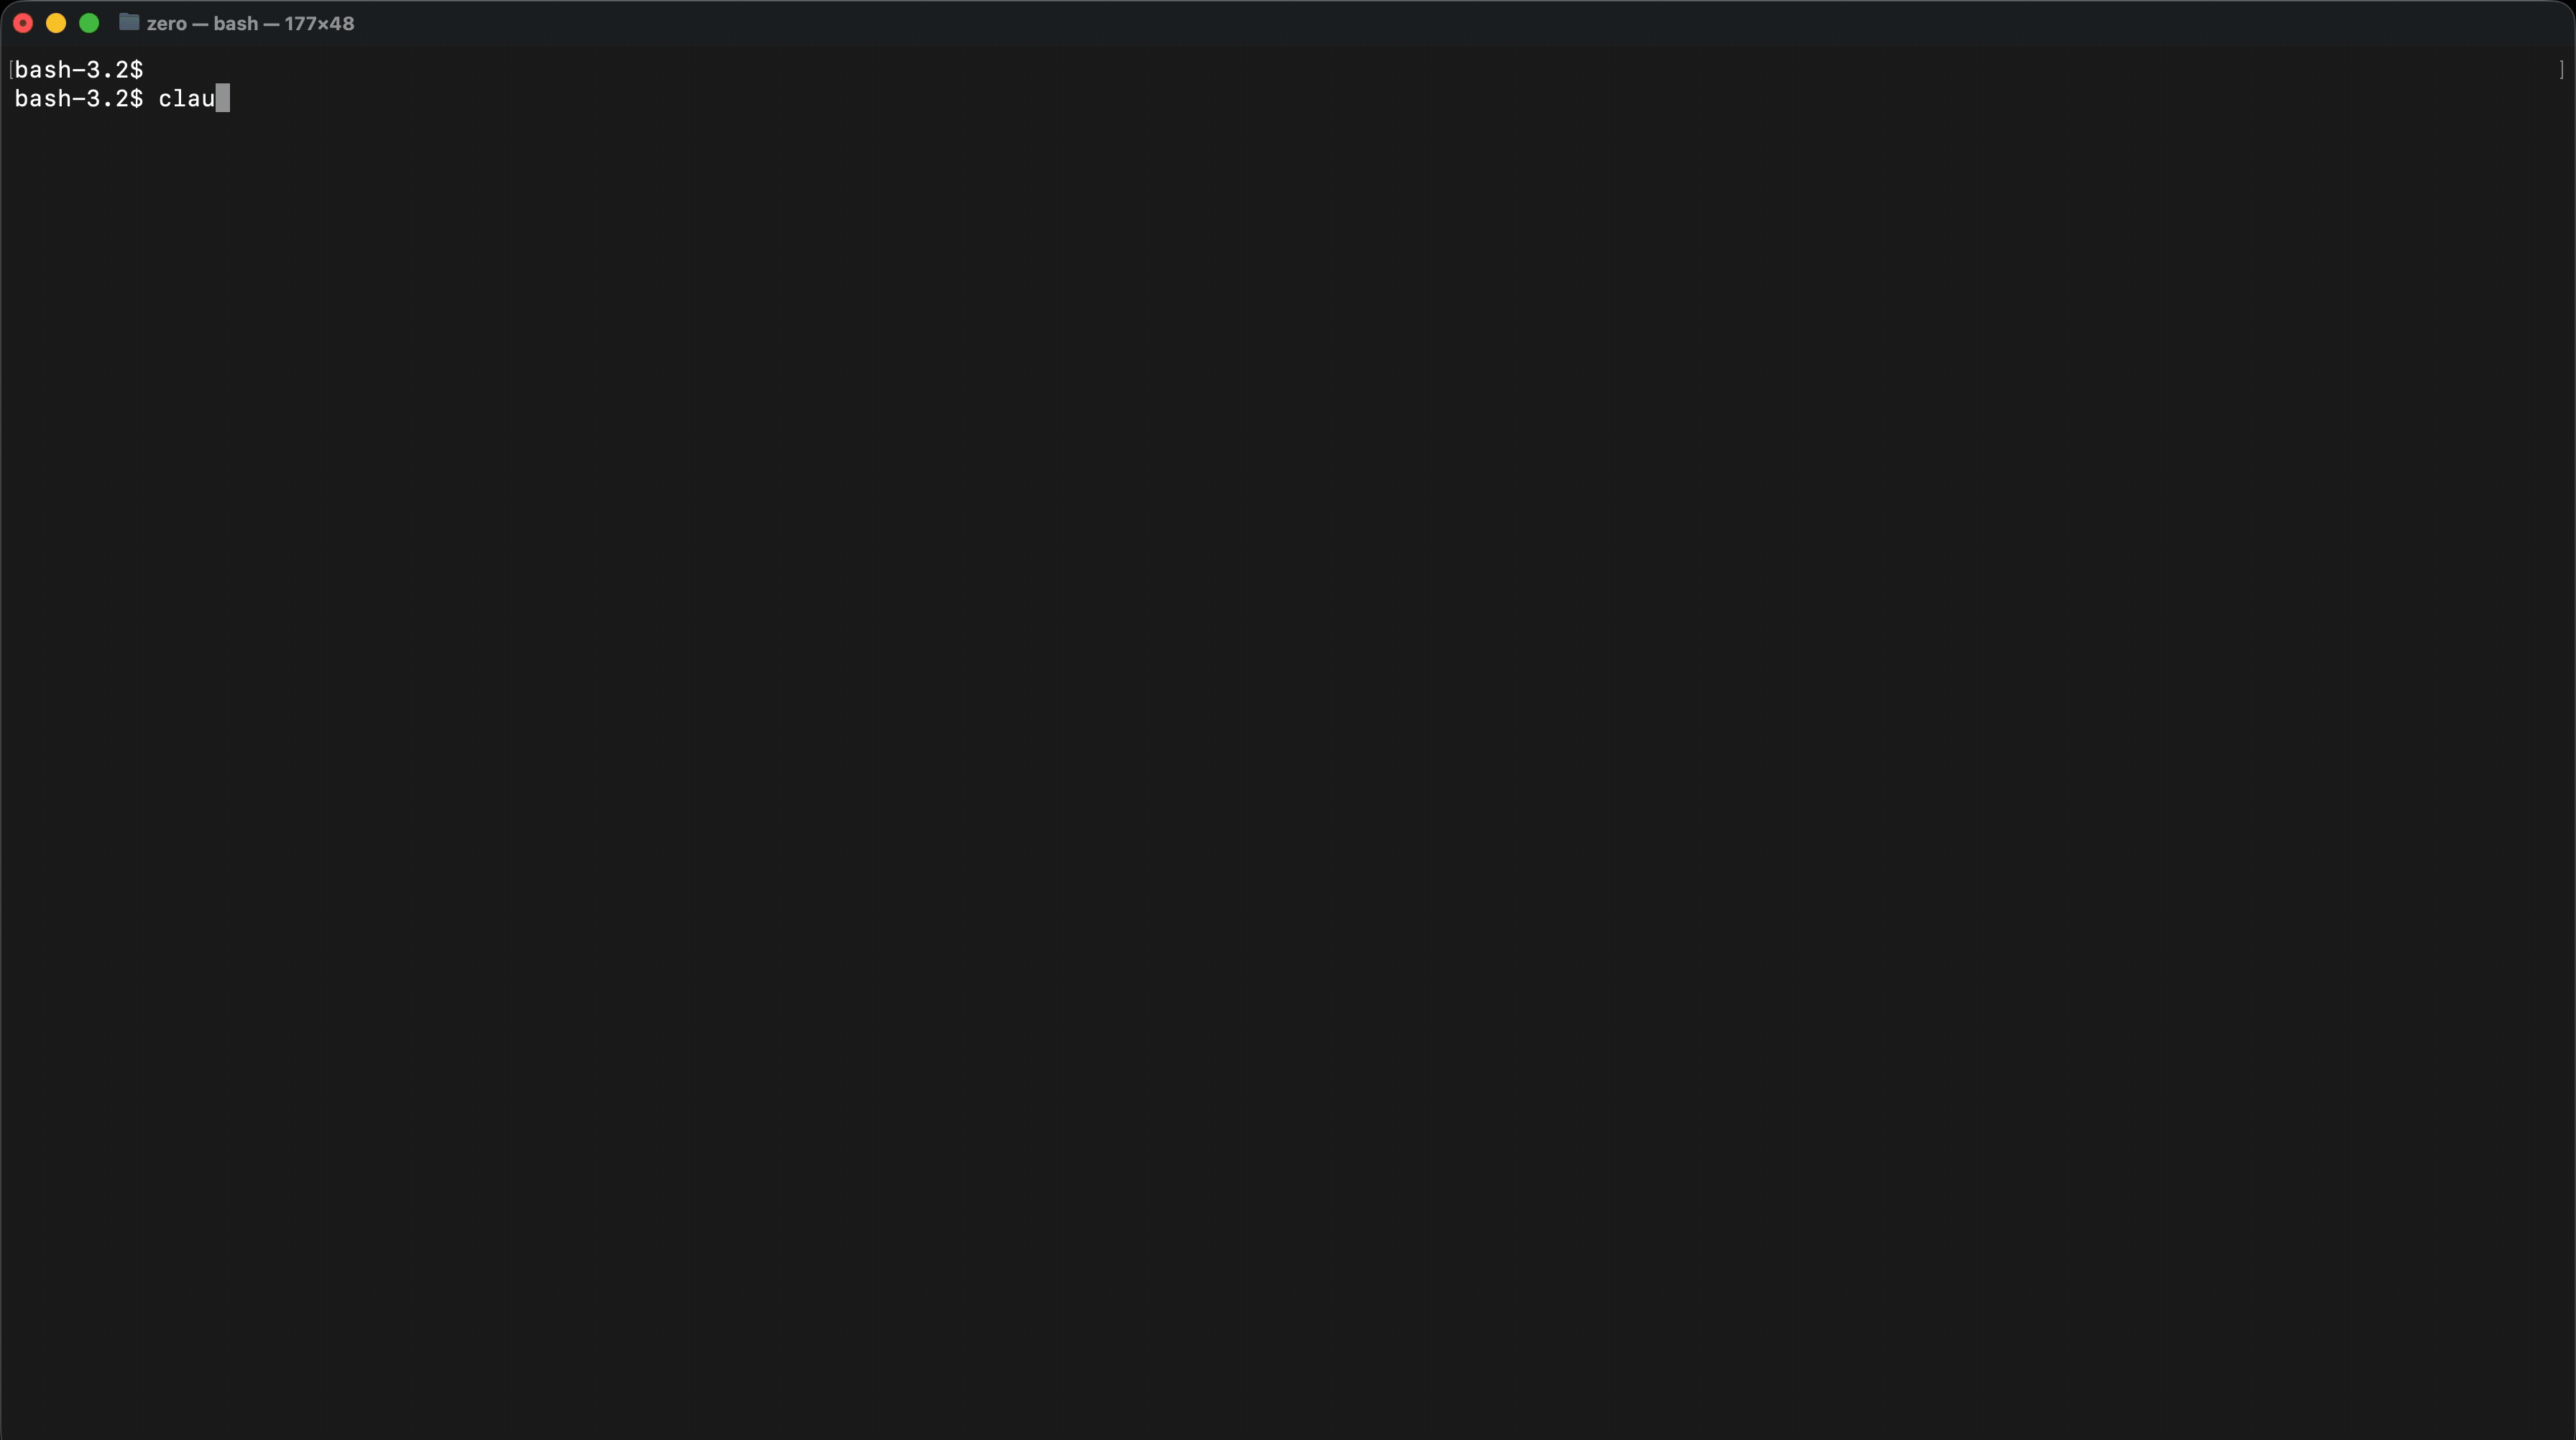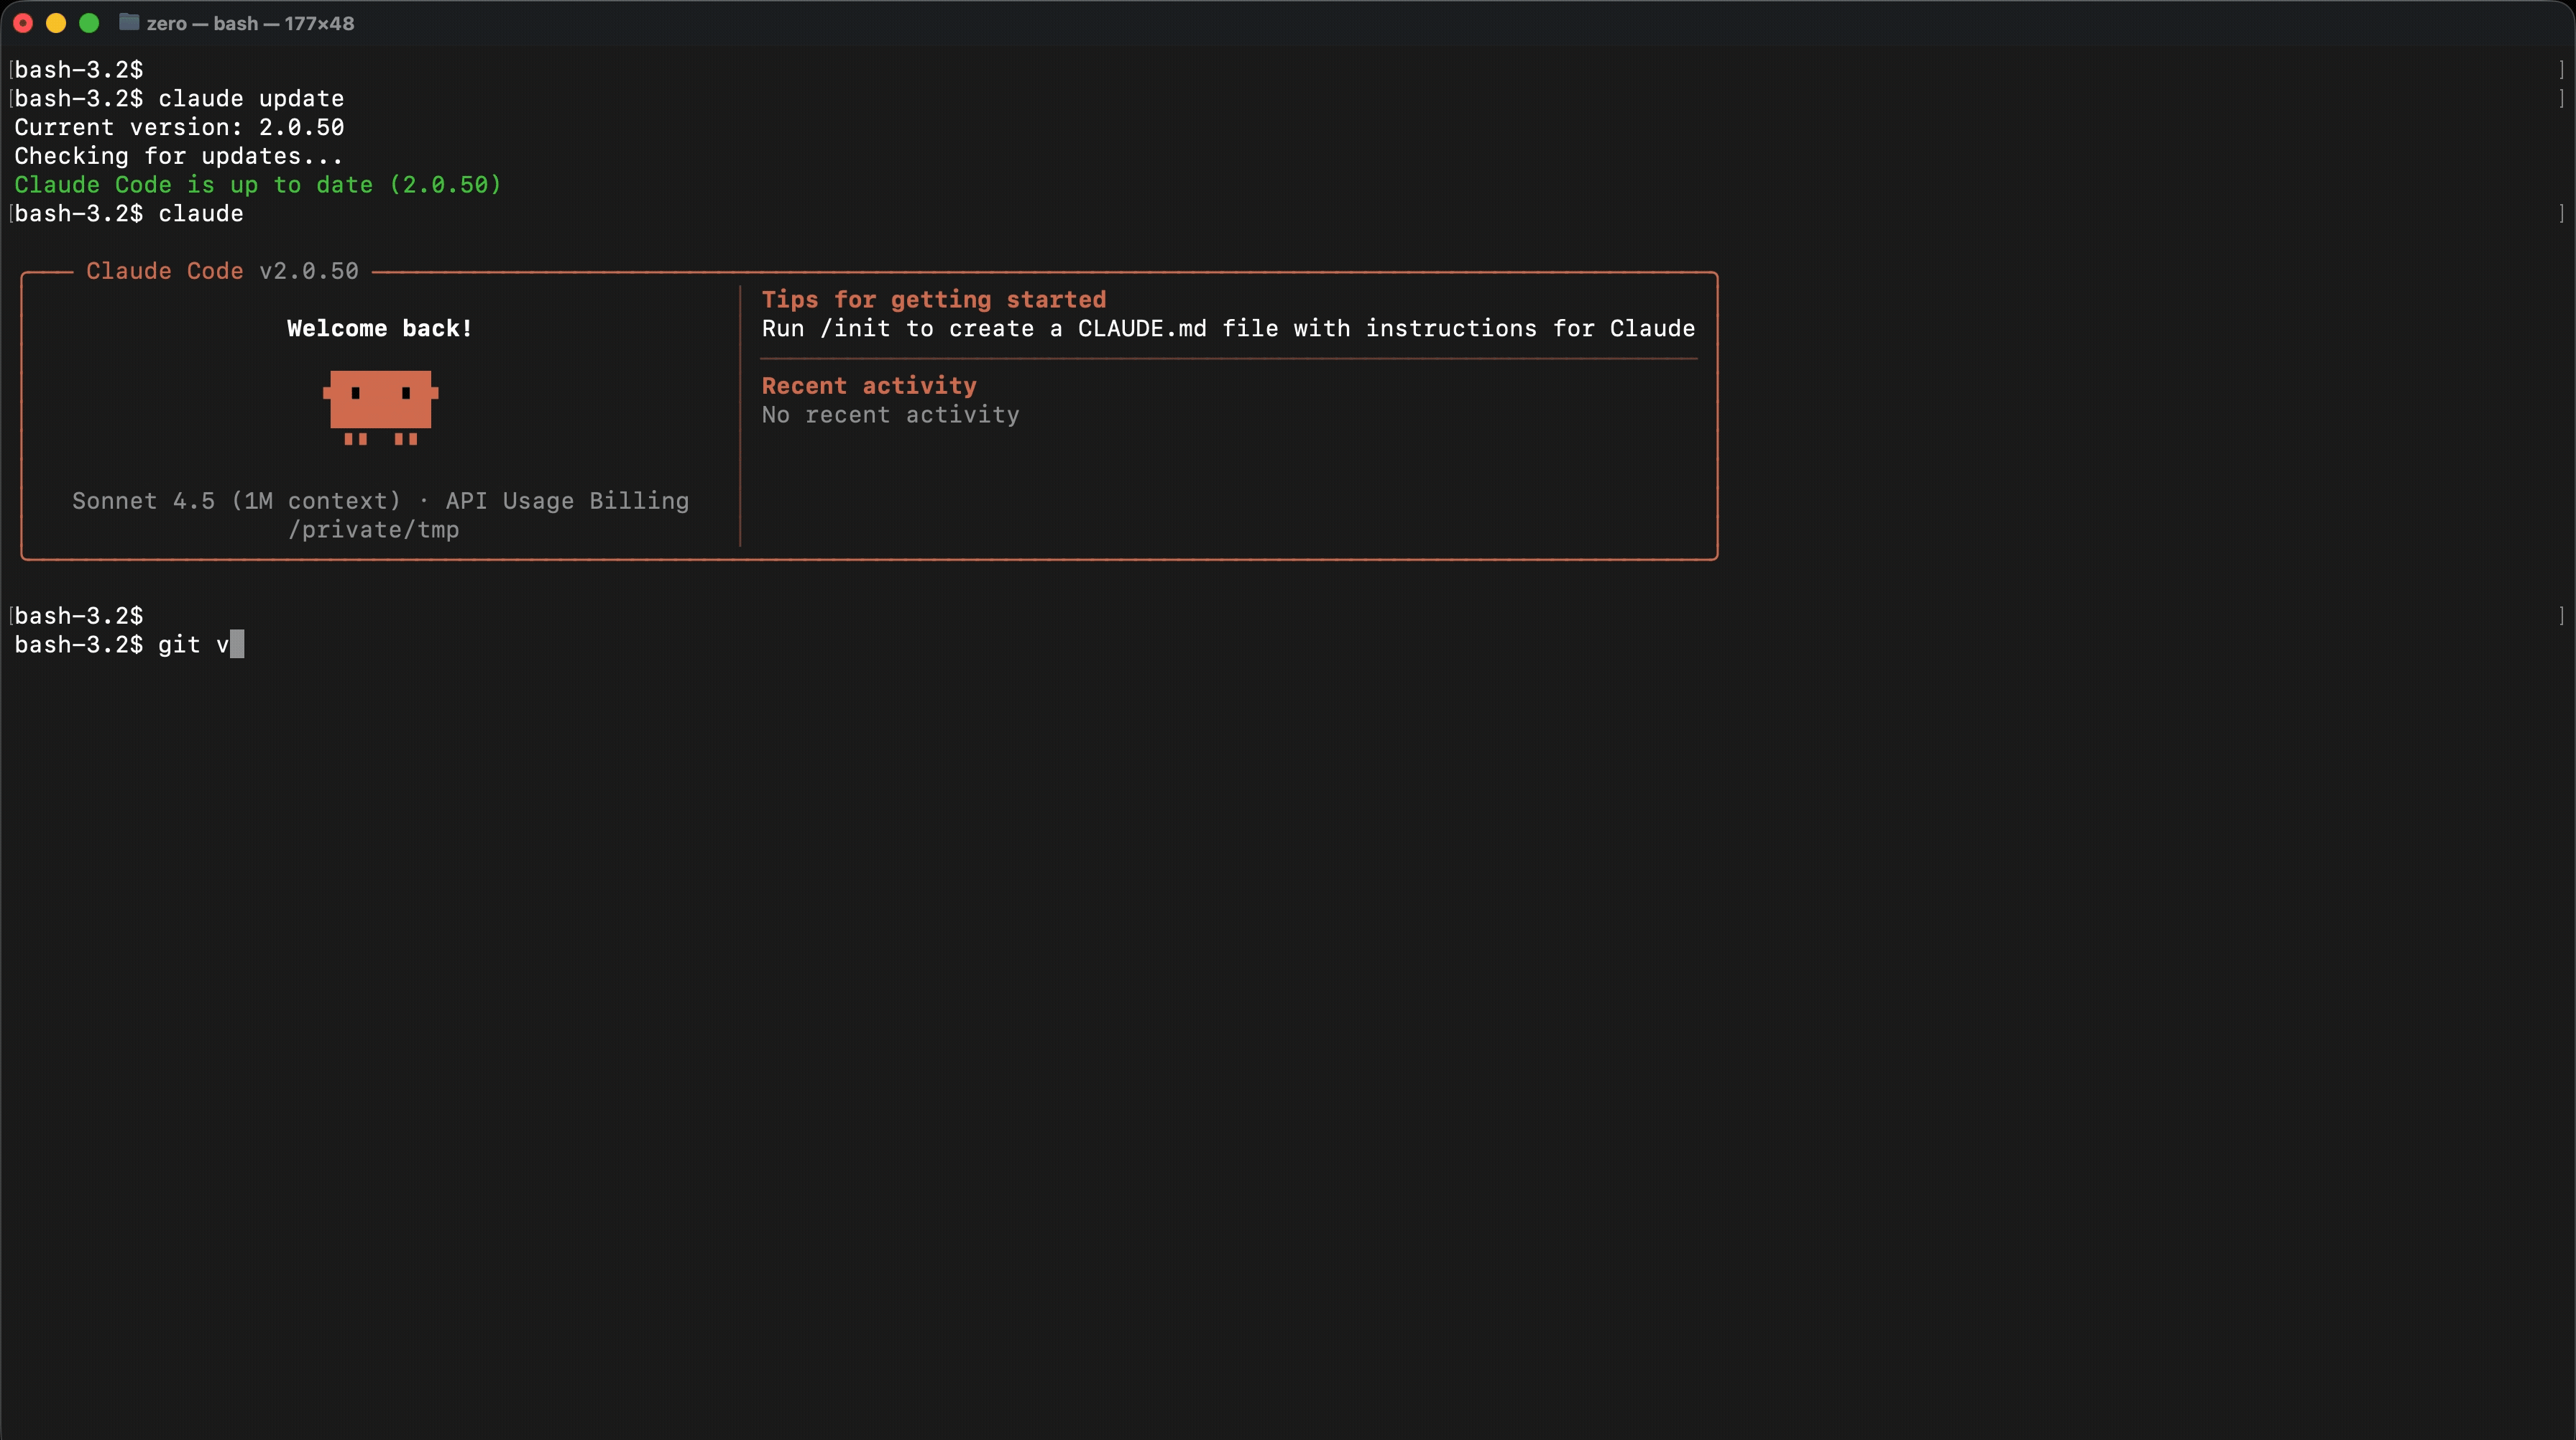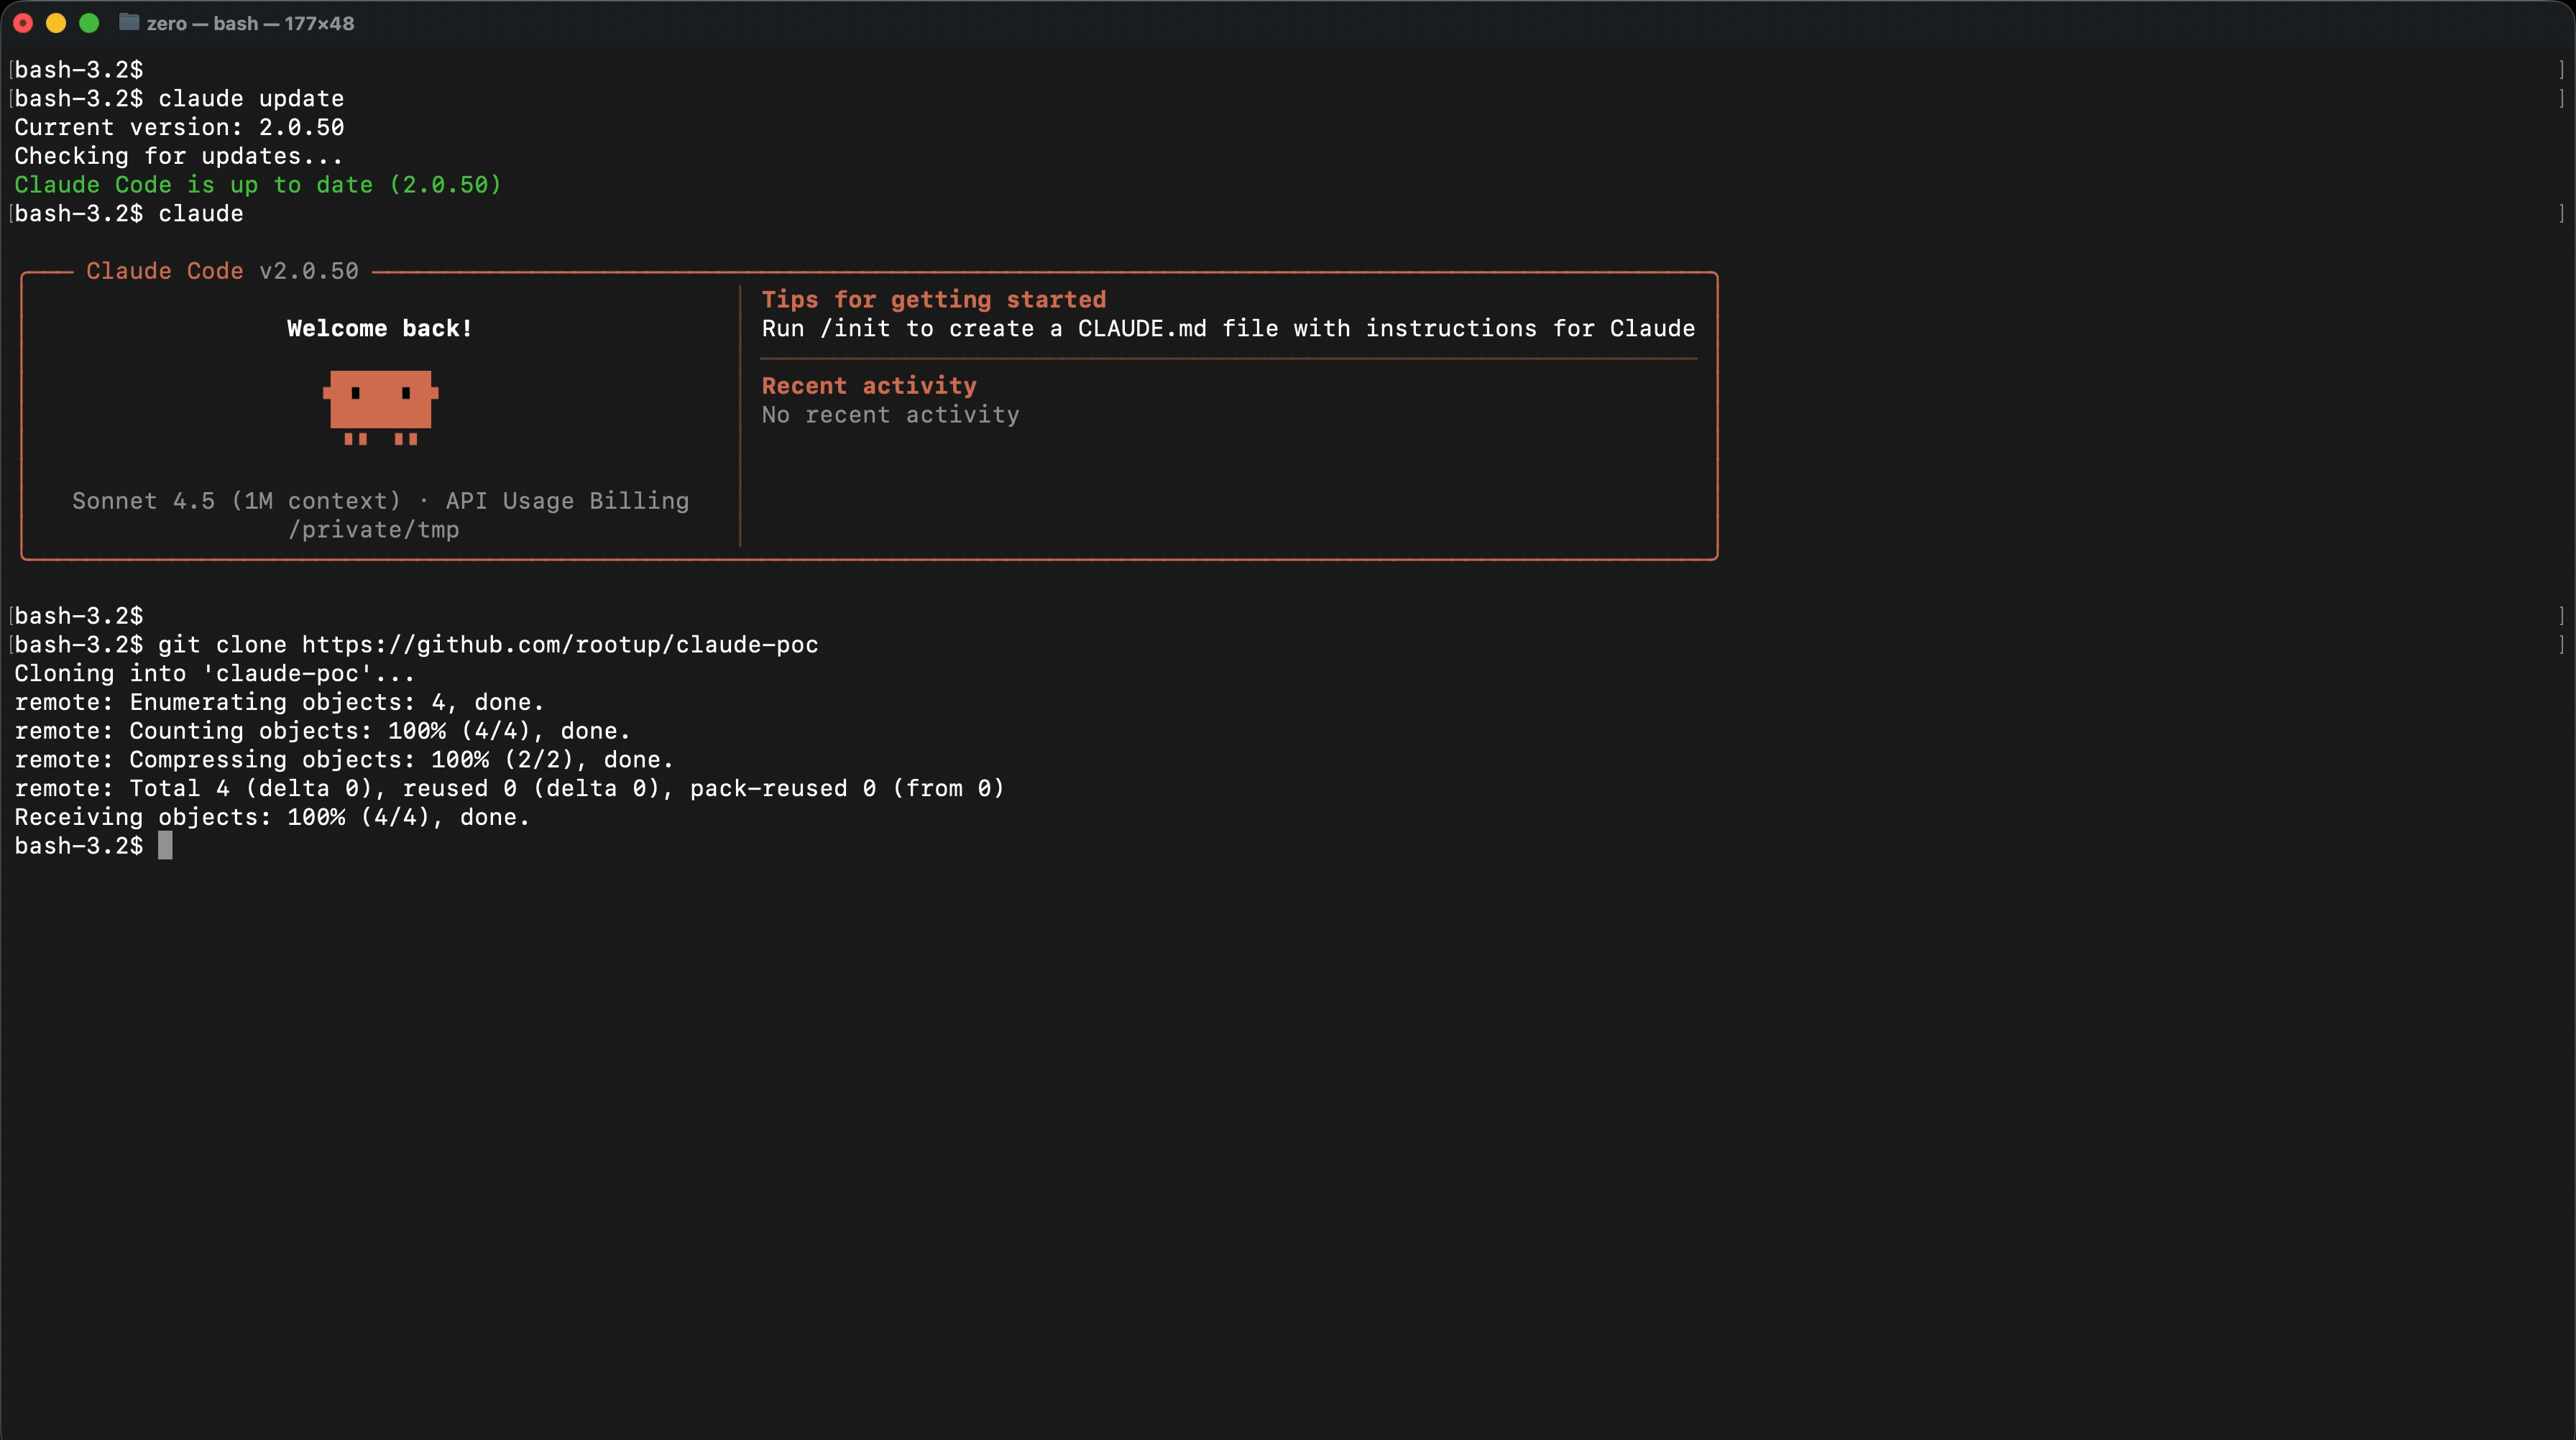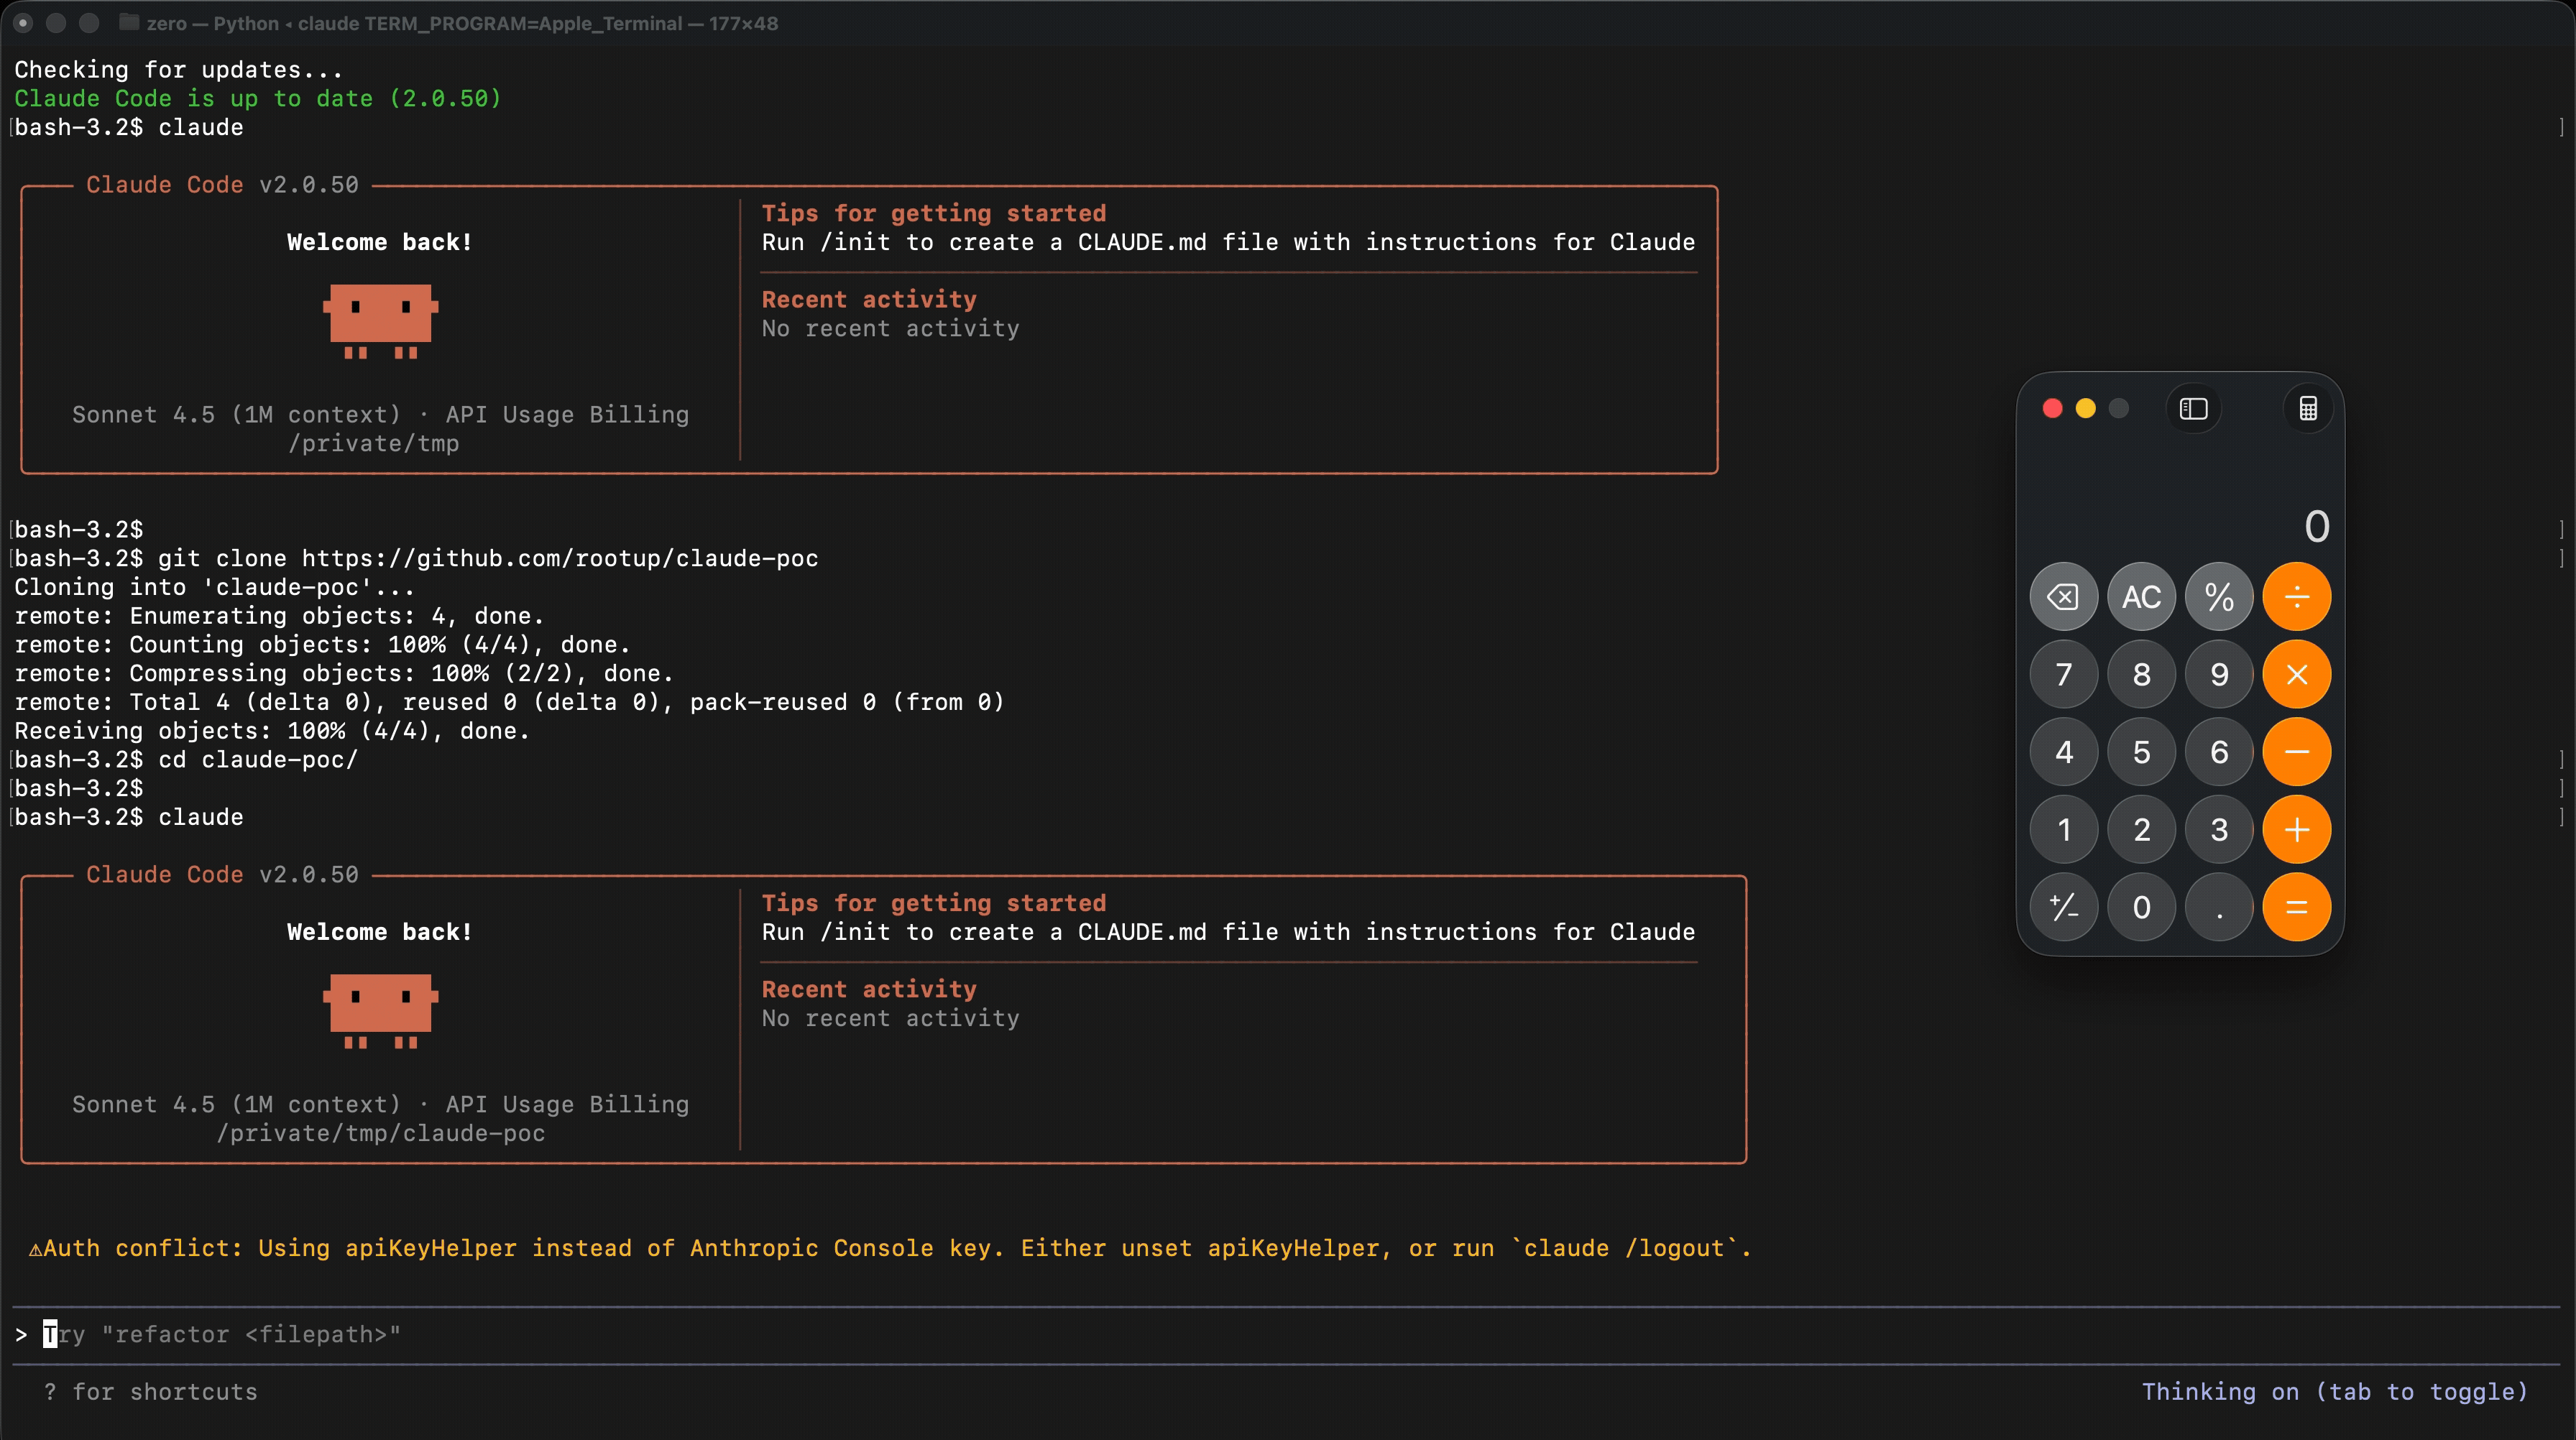 rootup/claude-poc
Claude Code Remote Code Execution
 ysrc/pil-rce-by-ghostbutt
Exploiting Python PIL Module Command Execution Vulnerability