

zoshrinkC2
 demon-i386/zoshrinkc2
DNS over HTTPS targeted malware (only runs once)
command-and-controlcryptographyids-ips-evasion+3
demon-i386/zoshrinkc2DNS over HTTPS targeted malware (only runs once)

 correcthorsebatterystaple-sudo/orwell-rat-and-botnet
Orwell is a RAT and Botnet designed as a trio of programs.
 gsoffmarket/malvinci
This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.
 tam-k592/cve-2025-55752
Detects and exploits Apache Tomcat CVE-2025-55752 directory traversal via Rewrite Valve, enabling PUT-based JSP upload and remote code execution.
 ysrc/pil-rce-by-ghostbutt
Exploiting Python PIL Module Command Execution Vulnerability
 shadowopcode/desckvb-rat
Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 rockmelodies/cve-2026-23524
Laravel Reverb 为 Laravel 应用提供实时 WebSocket 通信后端。在 1.6.3 及更早版本中,Reverb 将来自 Redis 通道的数据直接传递给 PHP 的 unserialize() 函数,且未对可实例化的类进行限制,导致用户面临远程代码执行风险。
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
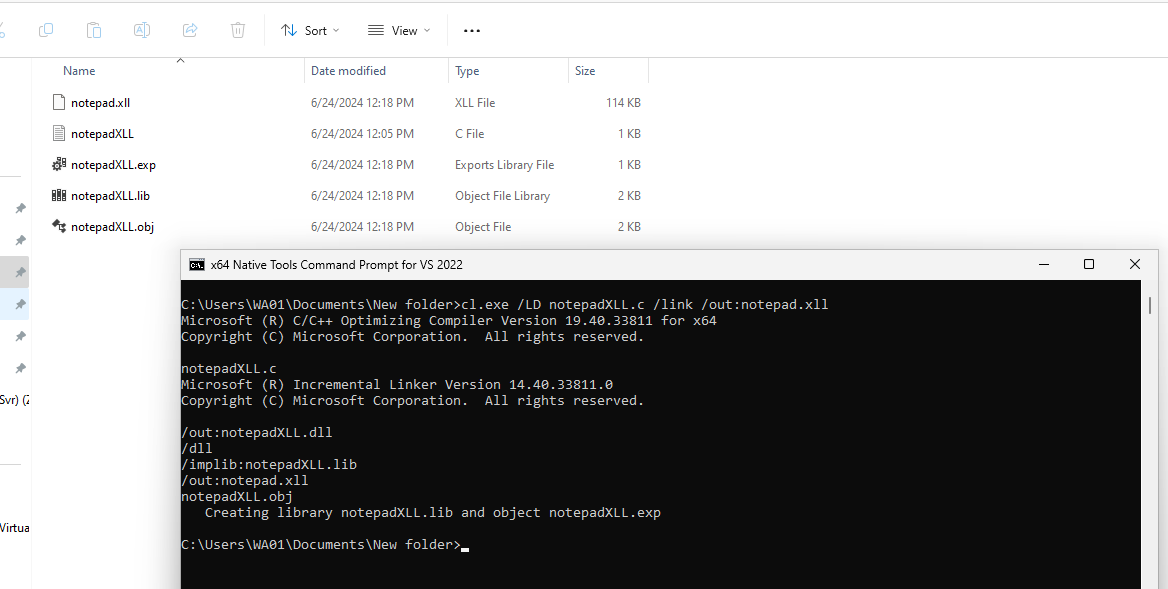 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 d4kw1n/cve-2026-102607-zoneminder
Python PoC exploiting CVE-2026-102607, an authenticated OS command injection in ZoneMinder <= 1.38.1 exportEvents() enabling RCE, command output…
 tennc/webshell
This is a webshell open source project