

DarkFox
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
command-and-controlmalware-analysispayload-development+2
25
federicochieregato/darkfoxRemote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 chebuya/cve-2024-30850-chaos-rat-rce-poc
CHAOS RAT web panel path RCE PoC
 gbrn1/pirate
Python Remote Access Tool
 artbitrage/stealth-kid-rat
Stealth Kid RAT (SKR) is an open-source multi-platform Remote Access Trojan (RAT) written in C#. Released under MIT license. The SKR project is fully…
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.
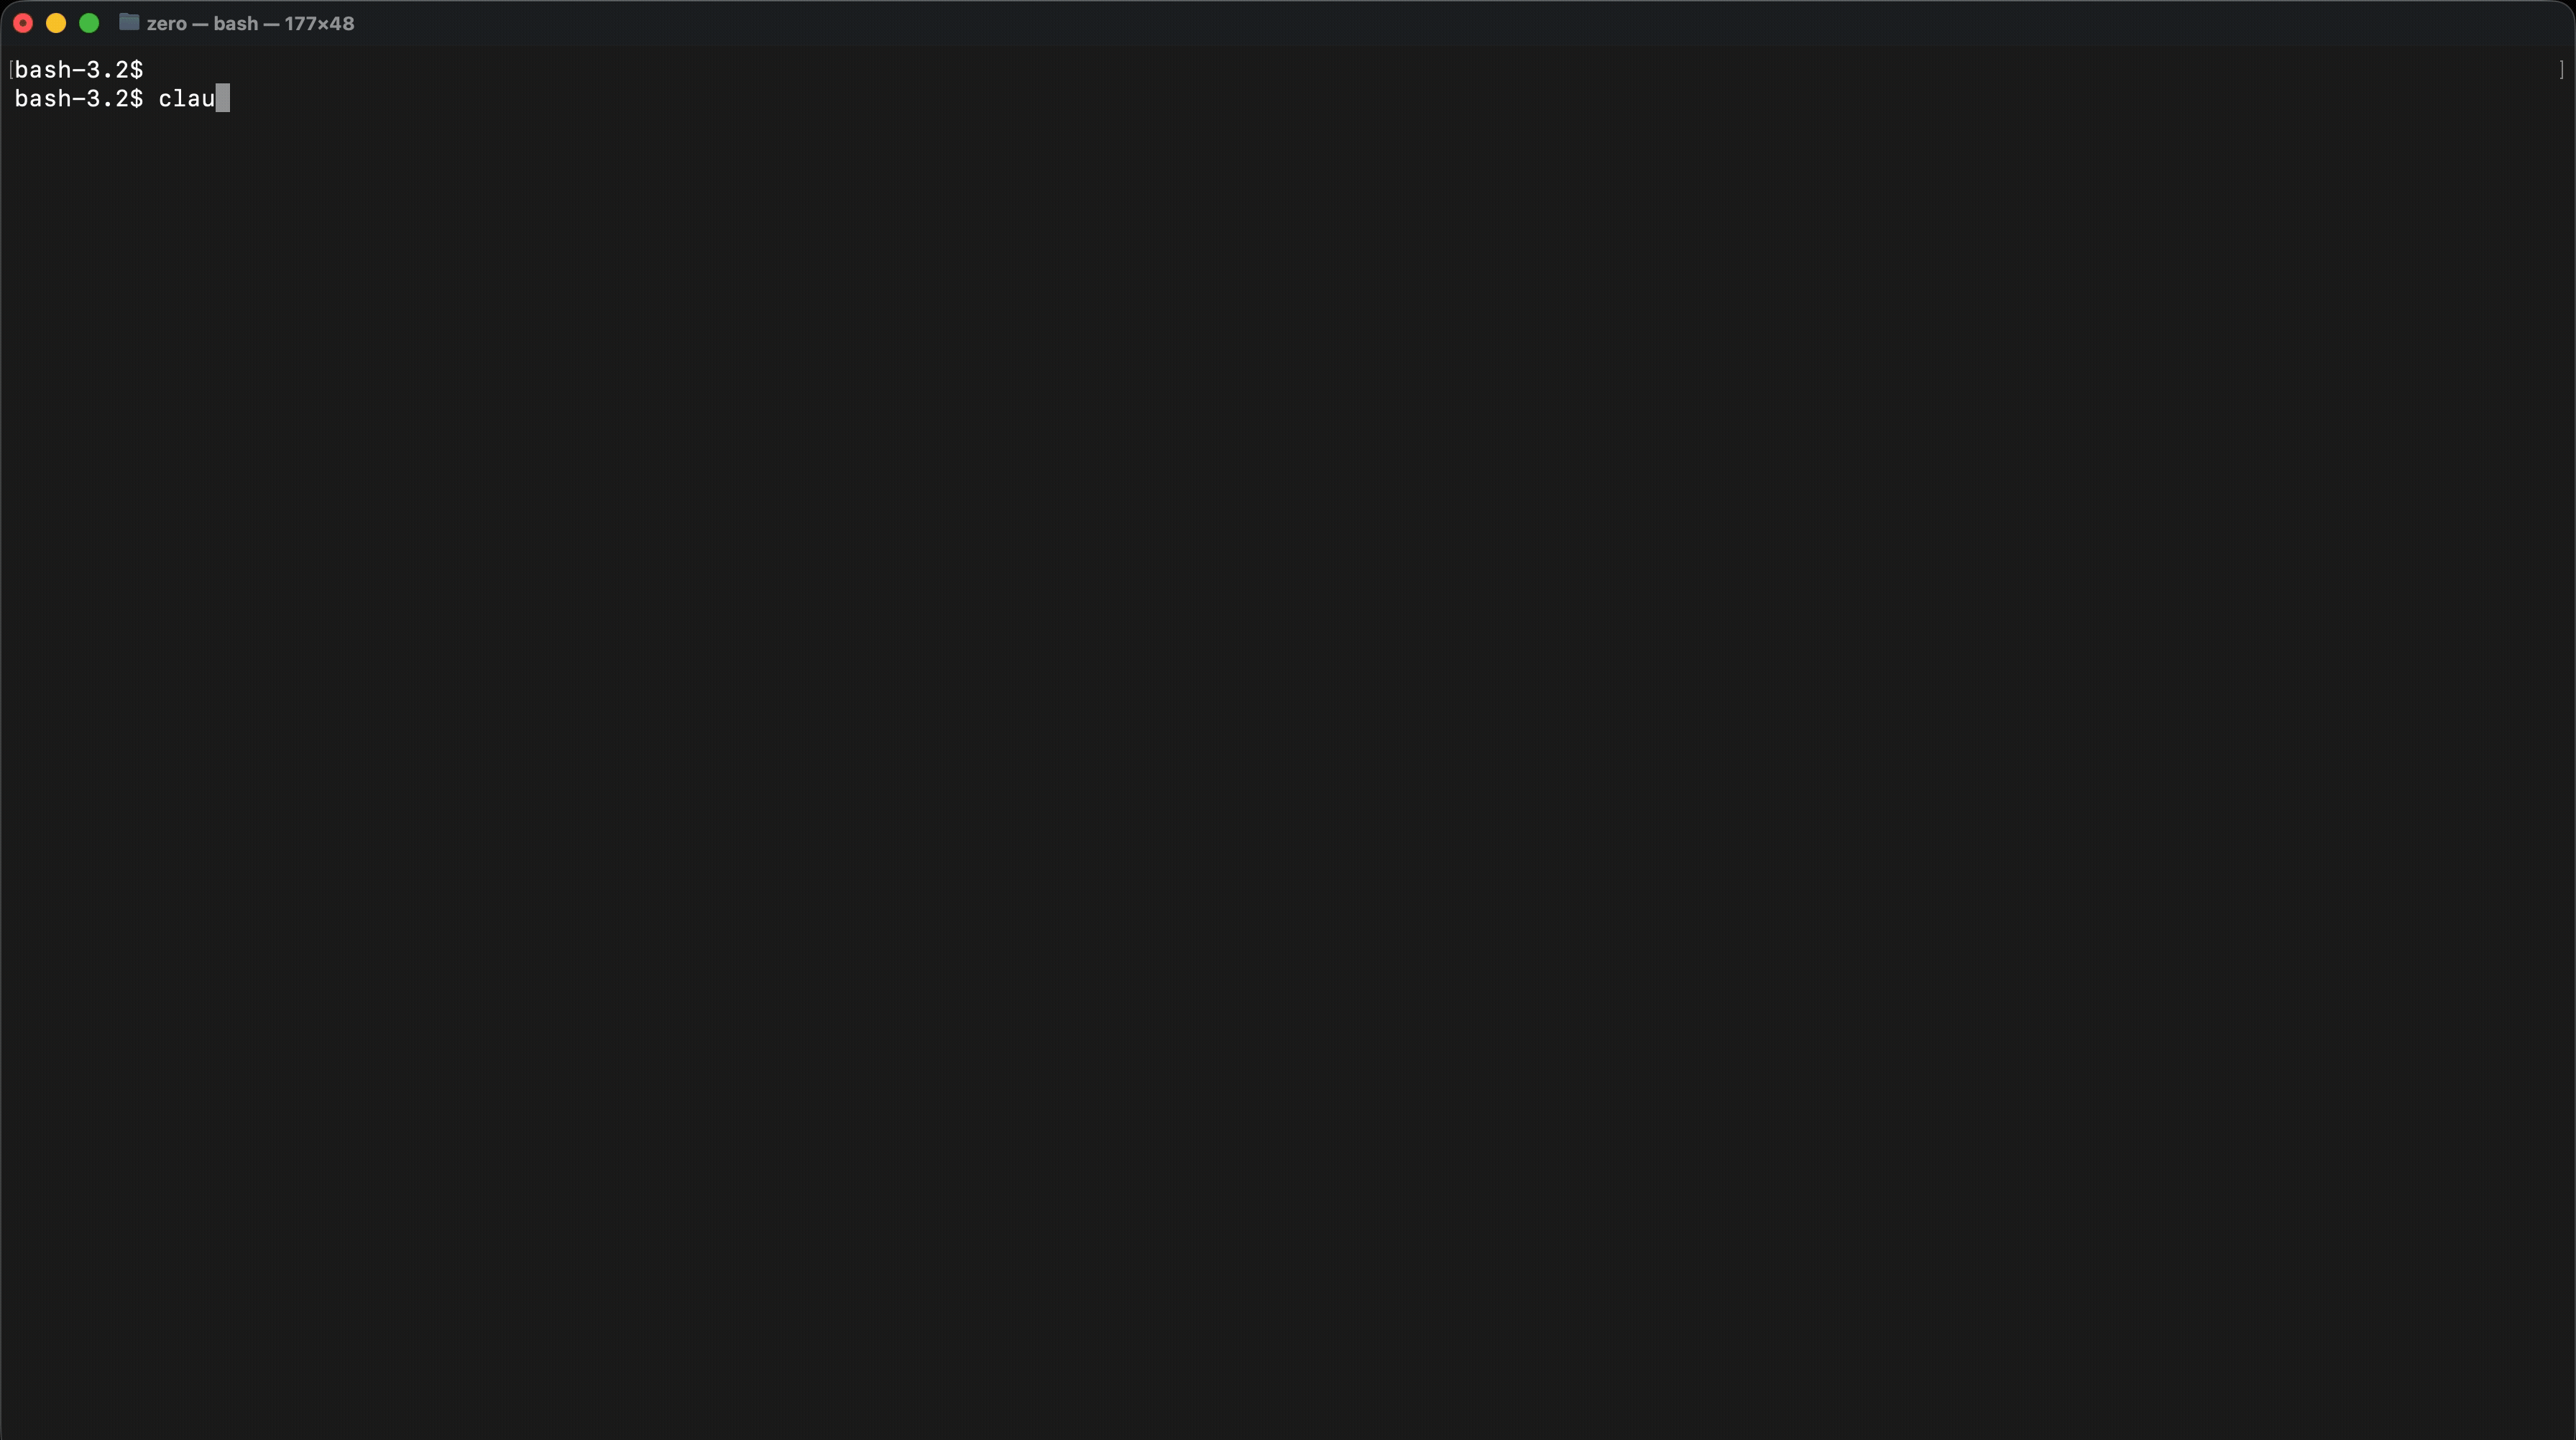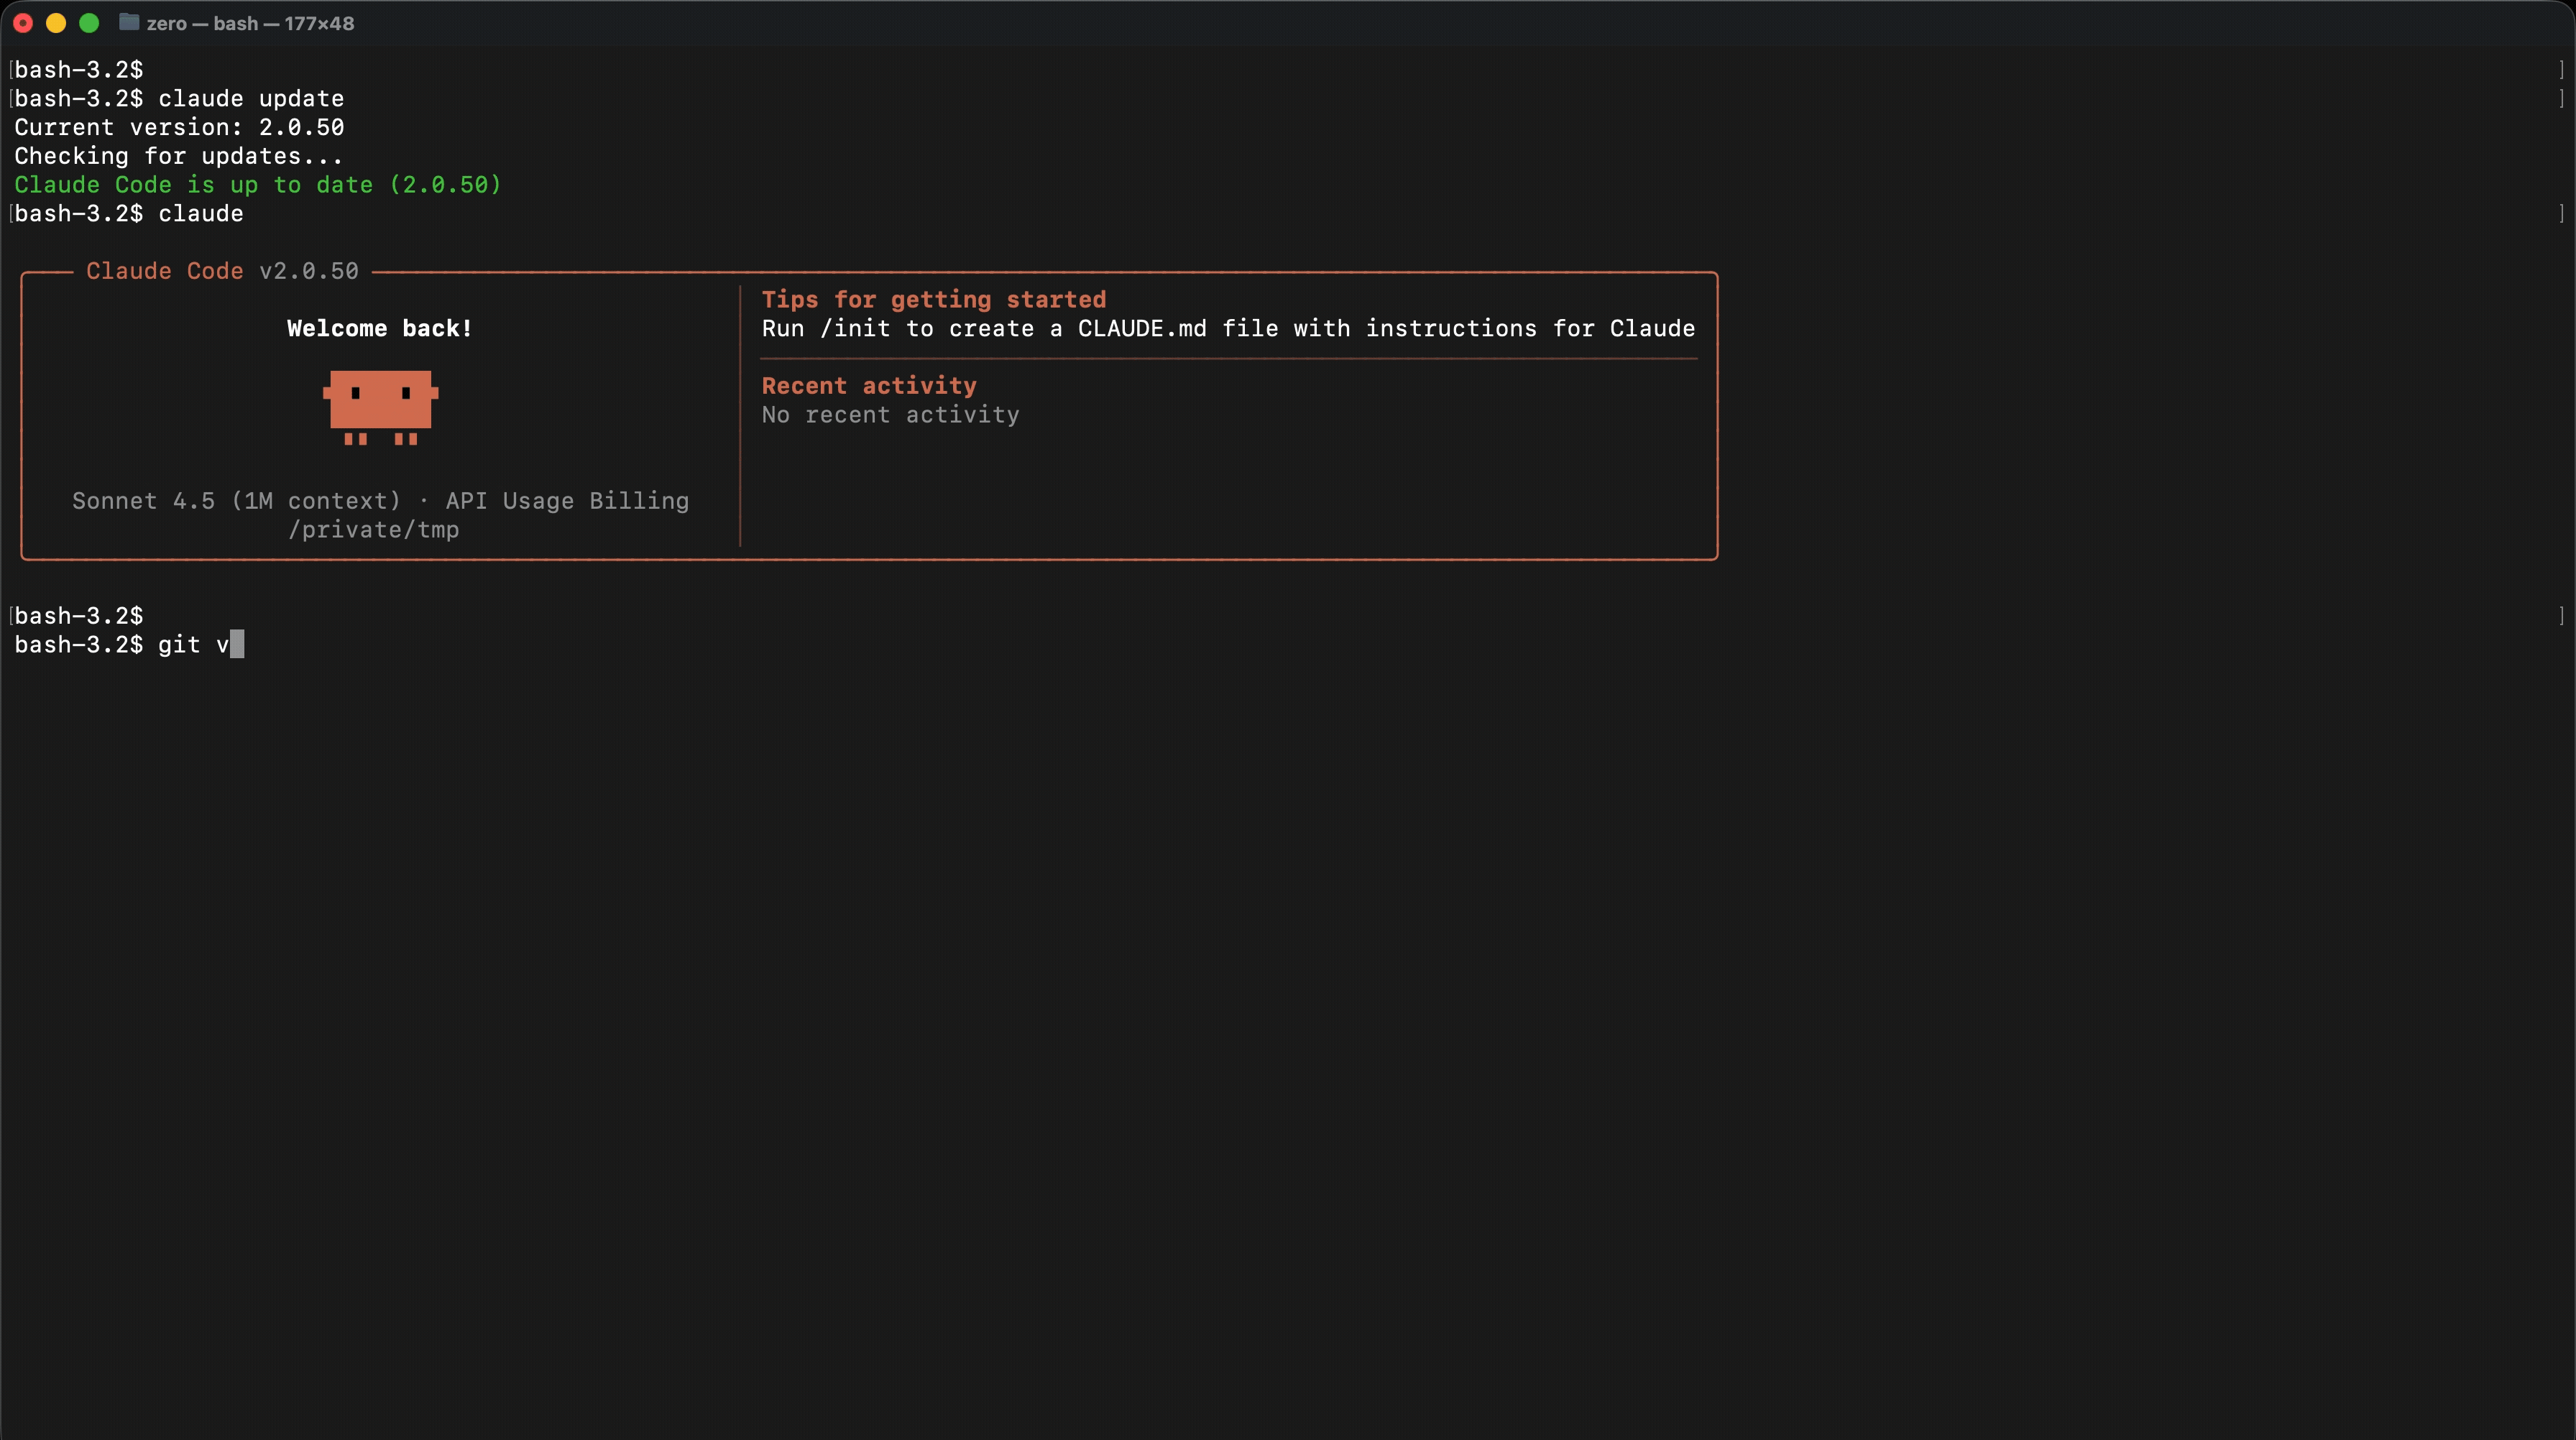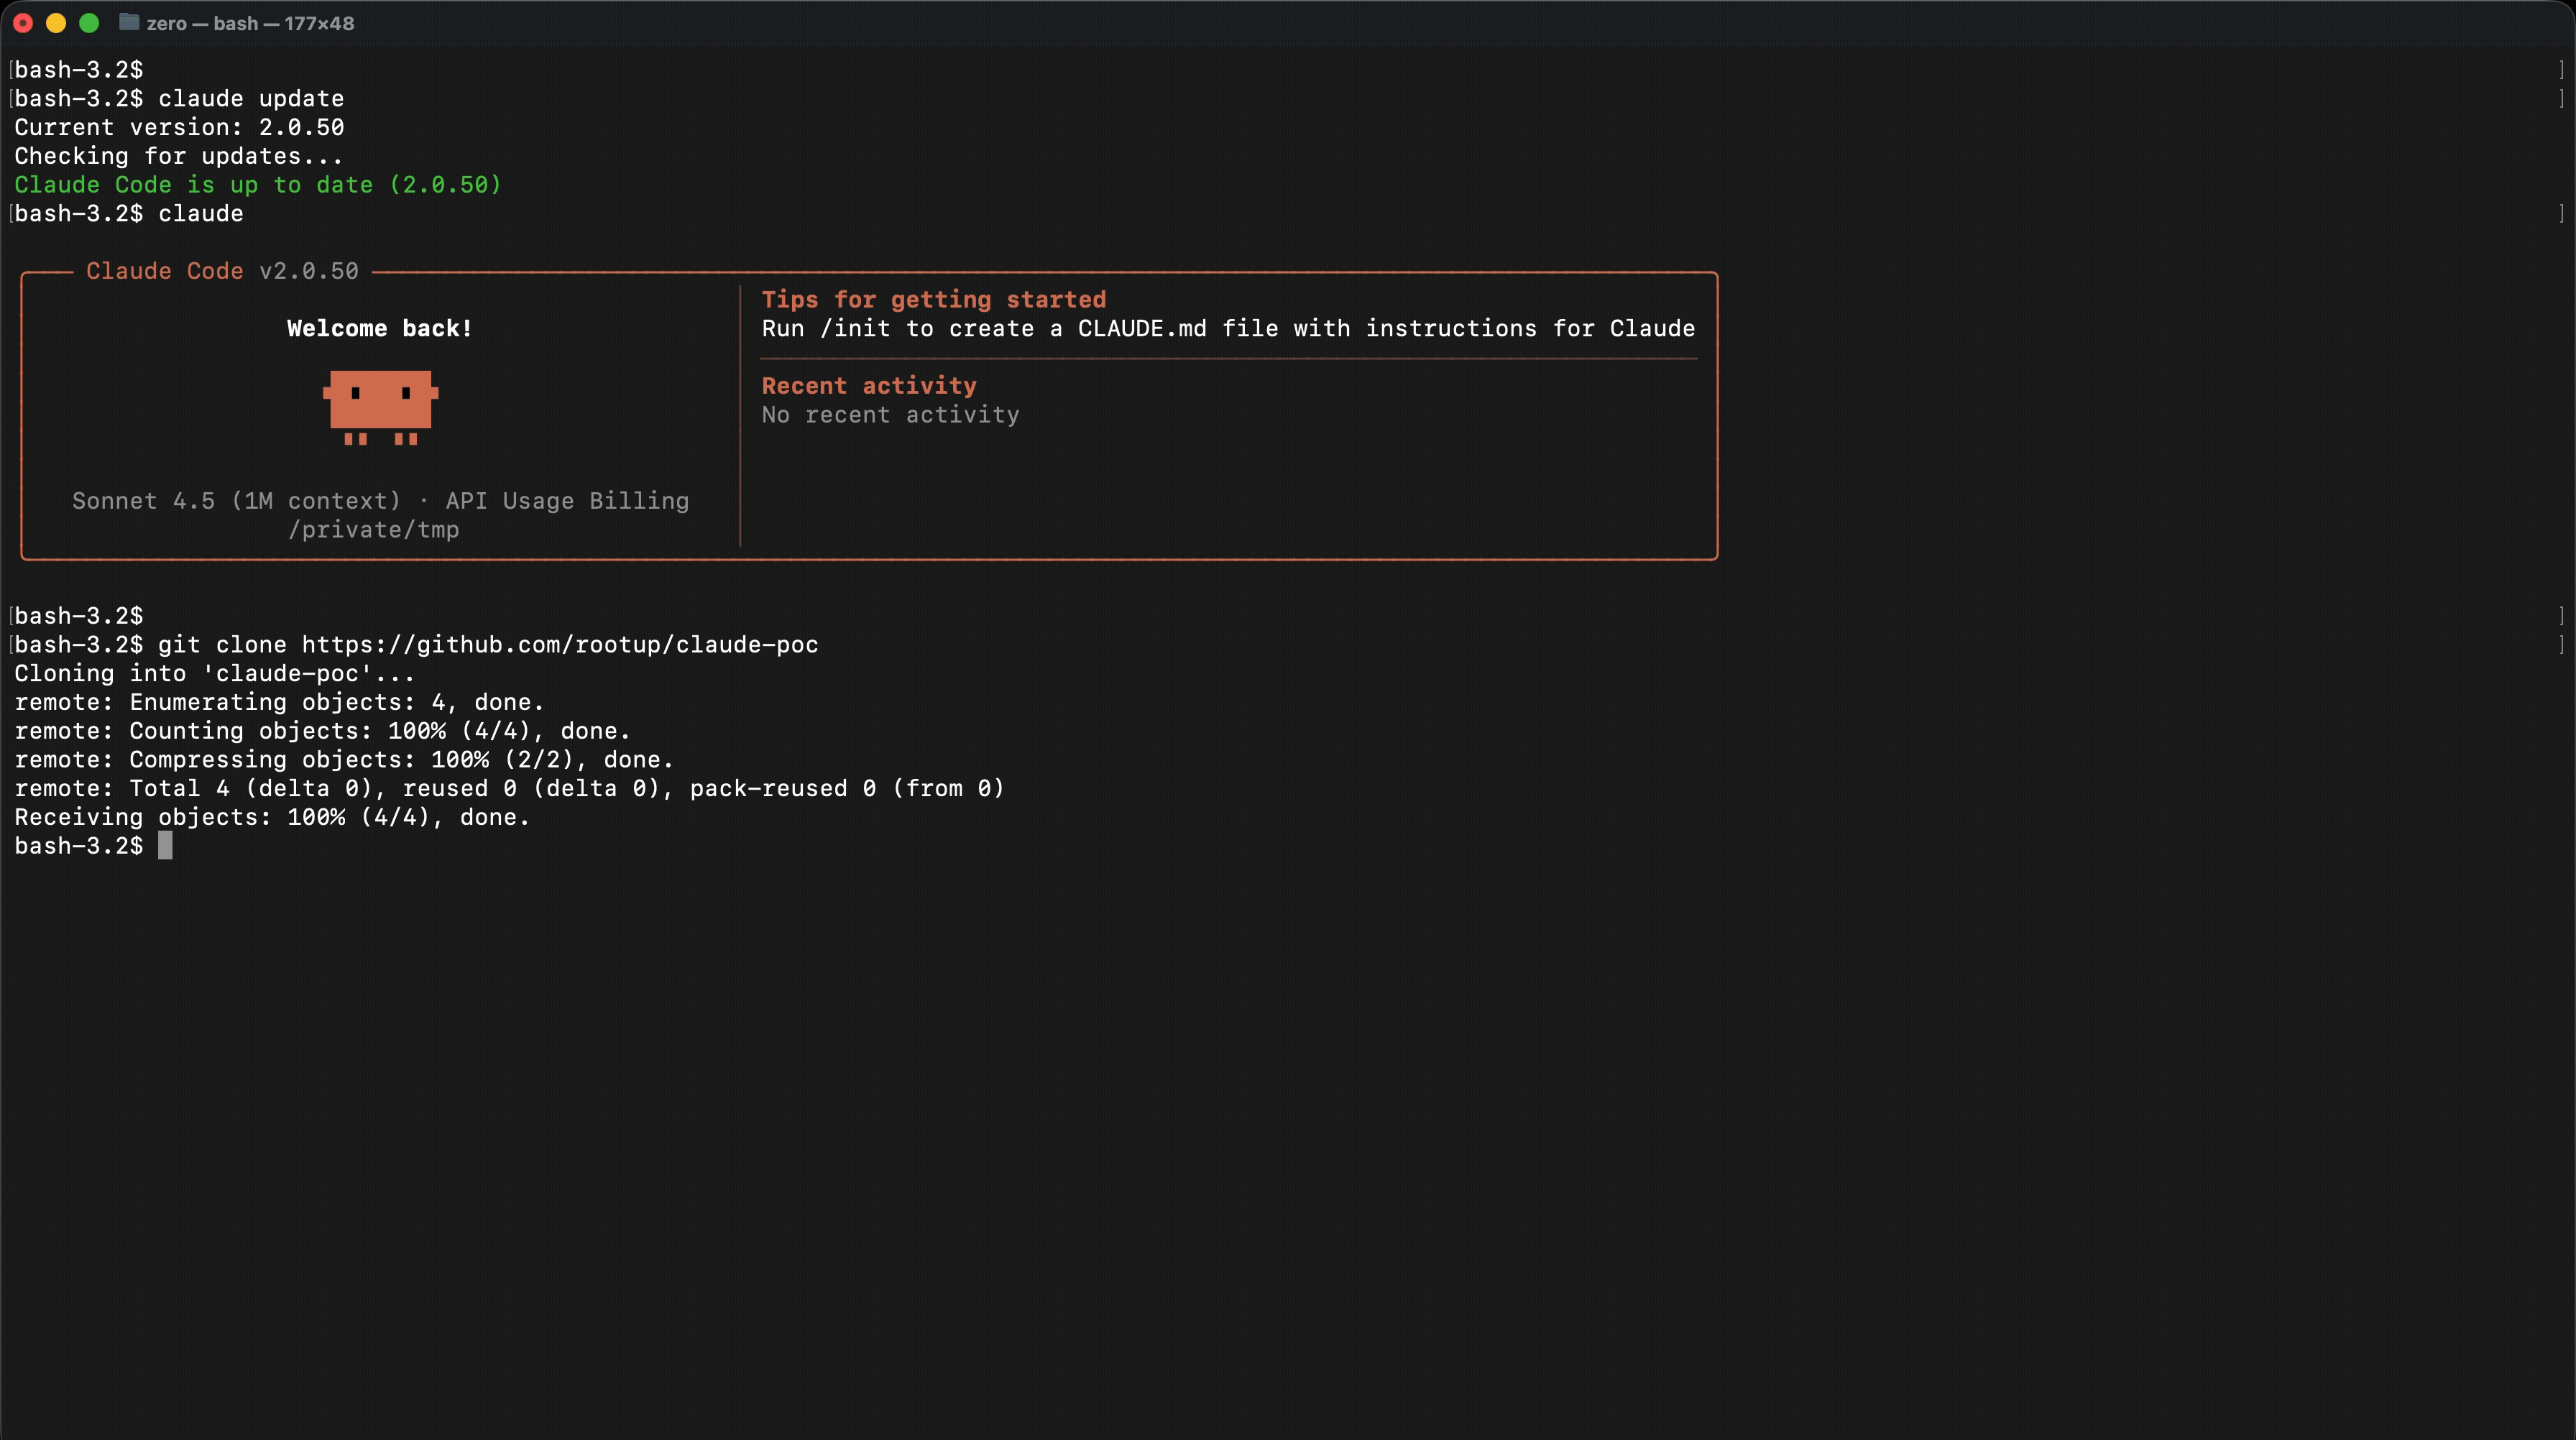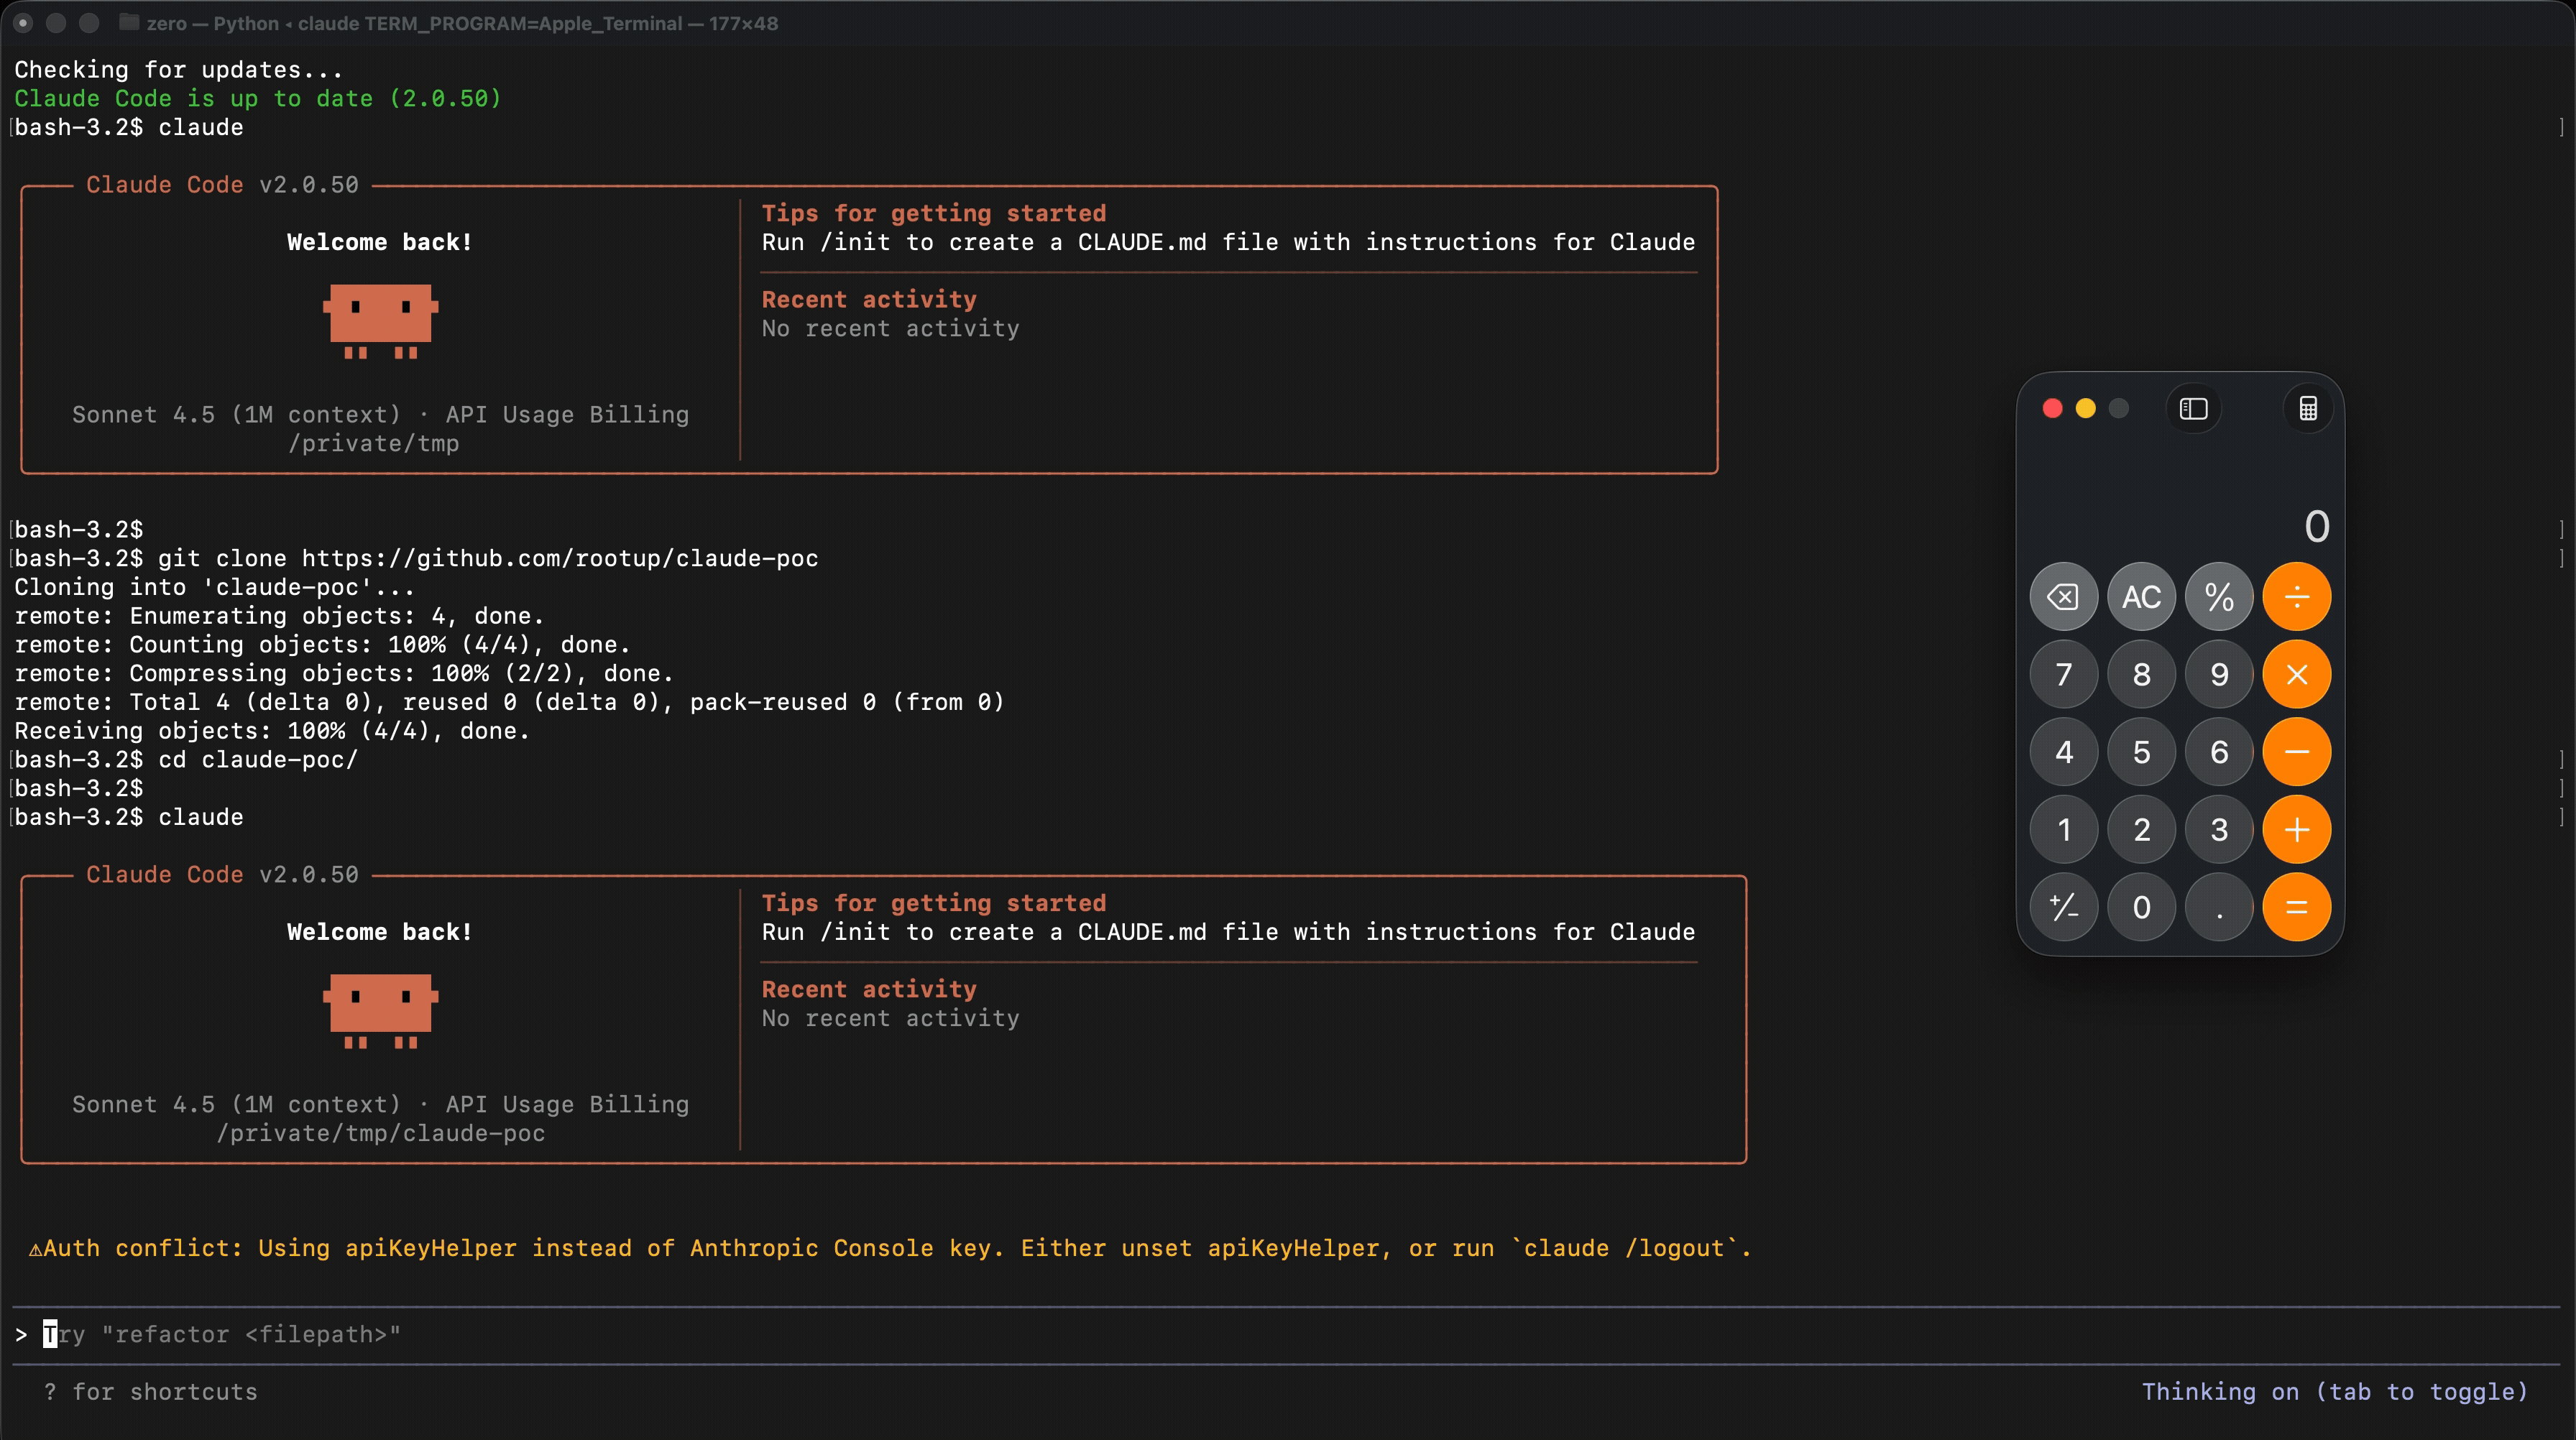 rootup/claude-poc
Claude Code Remote Code Execution
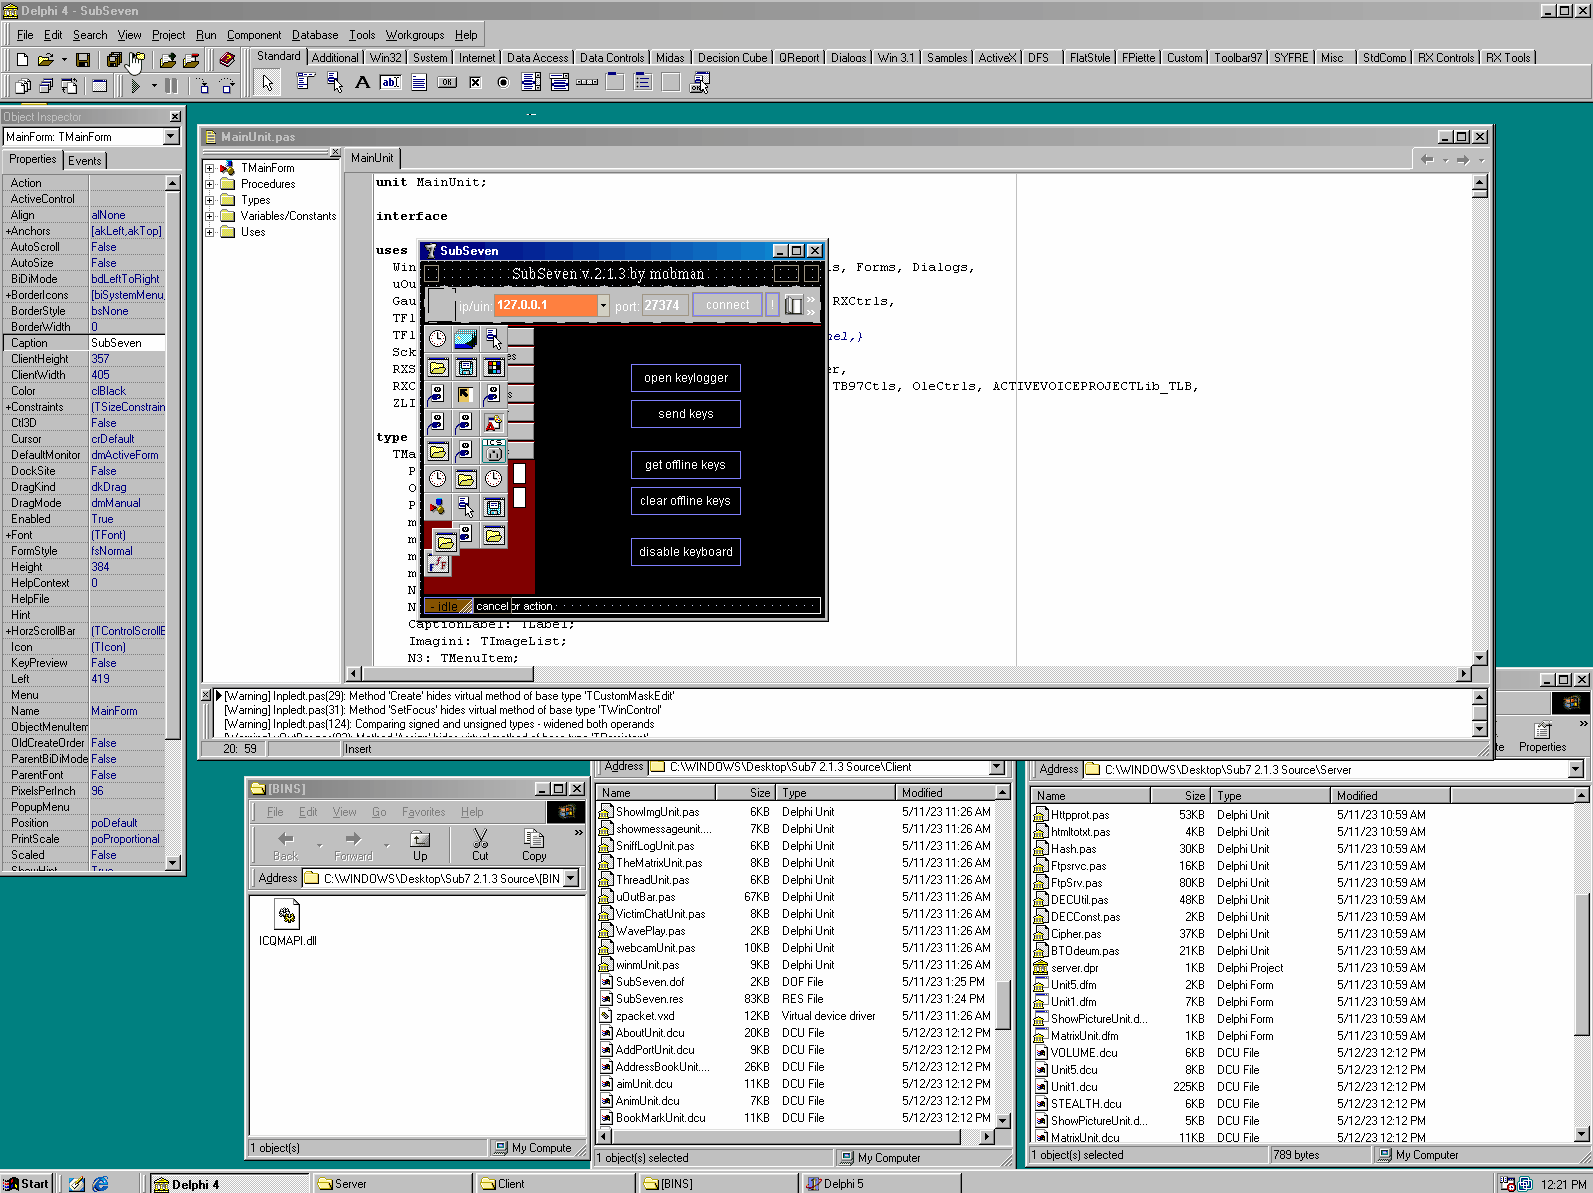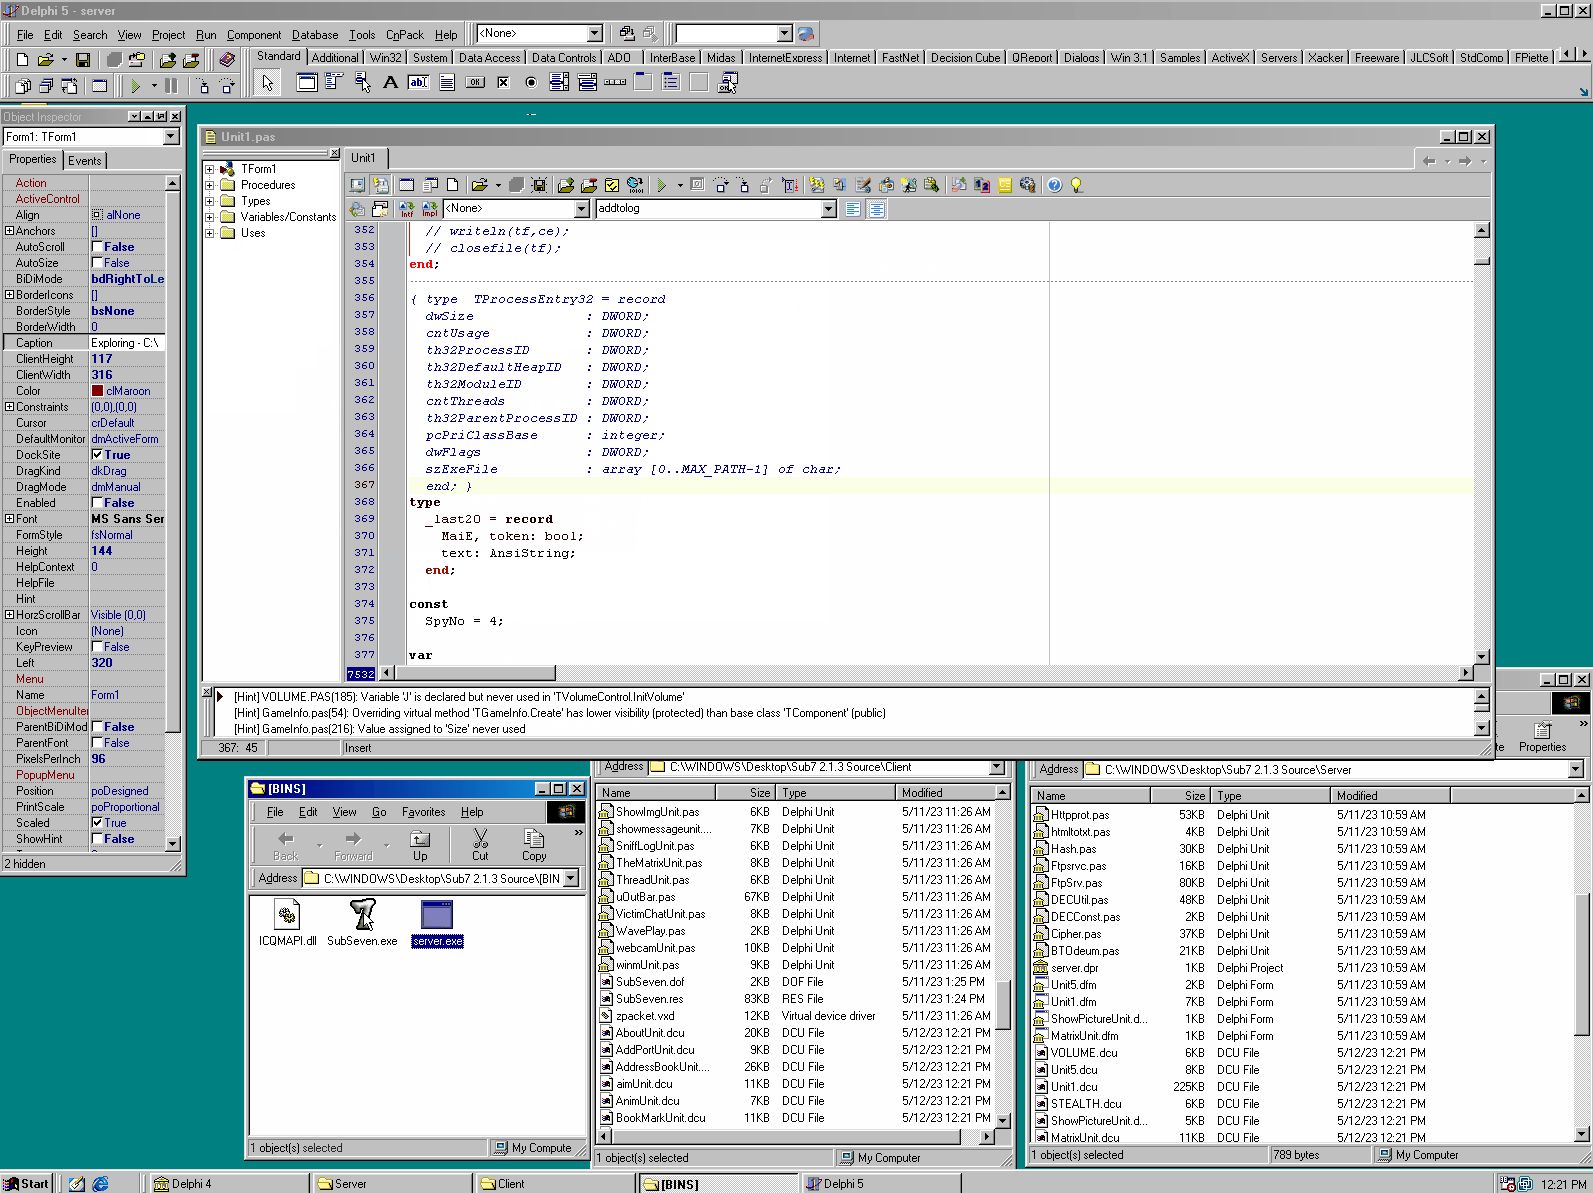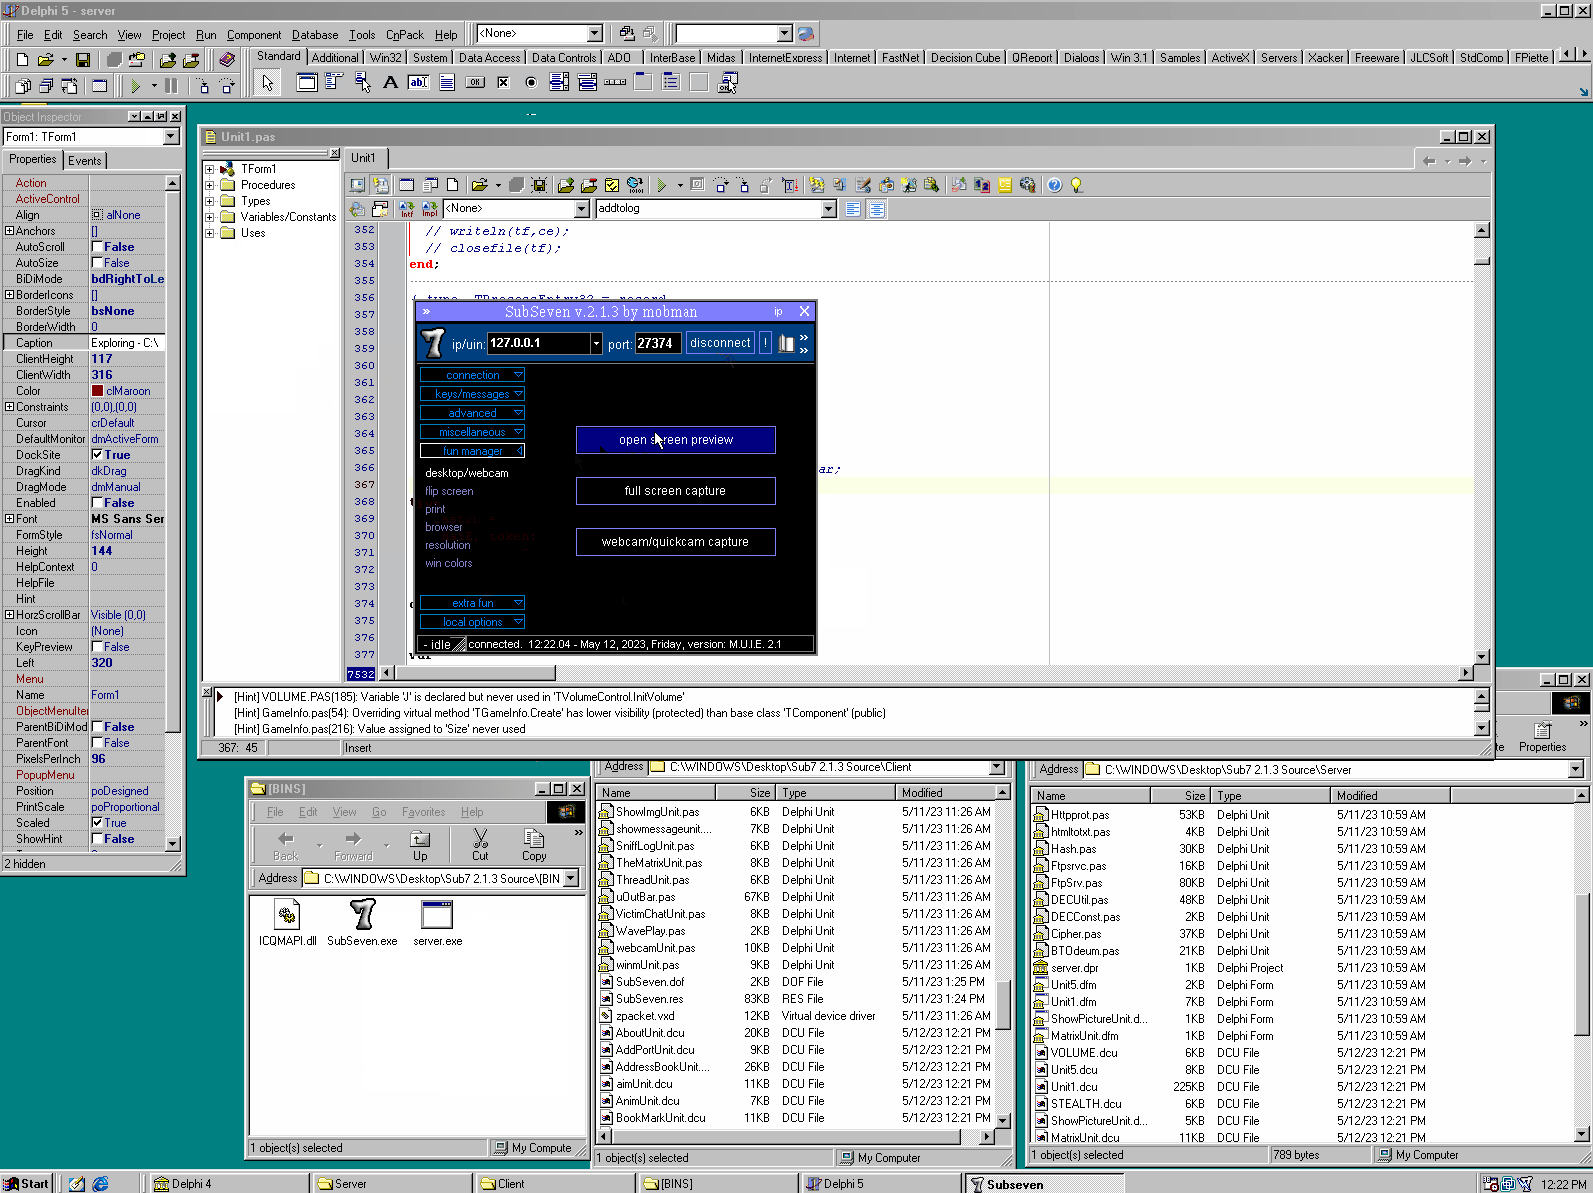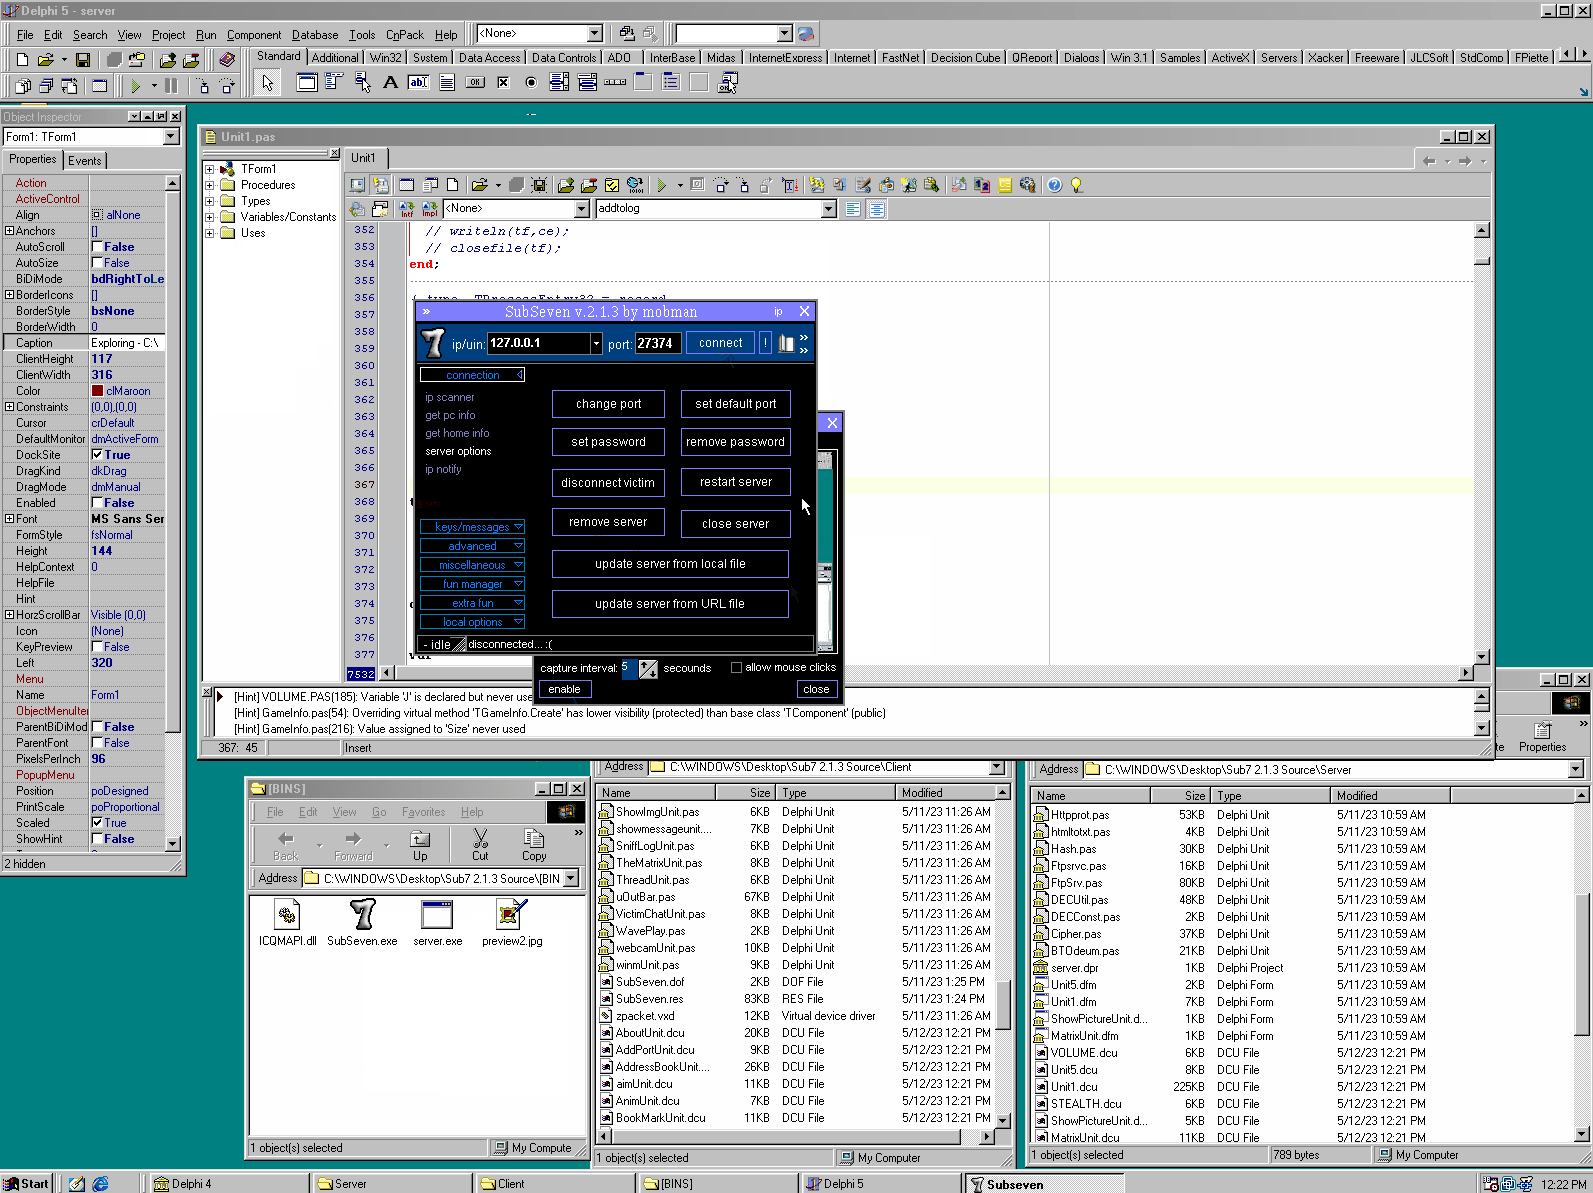
 illwill/sub7
Source code for SubSeven 2.1.3
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 catatonicprime/tospovirus
A WiFi Pineapple infecting worm.
 shadowopcode/desckvb-rat
Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
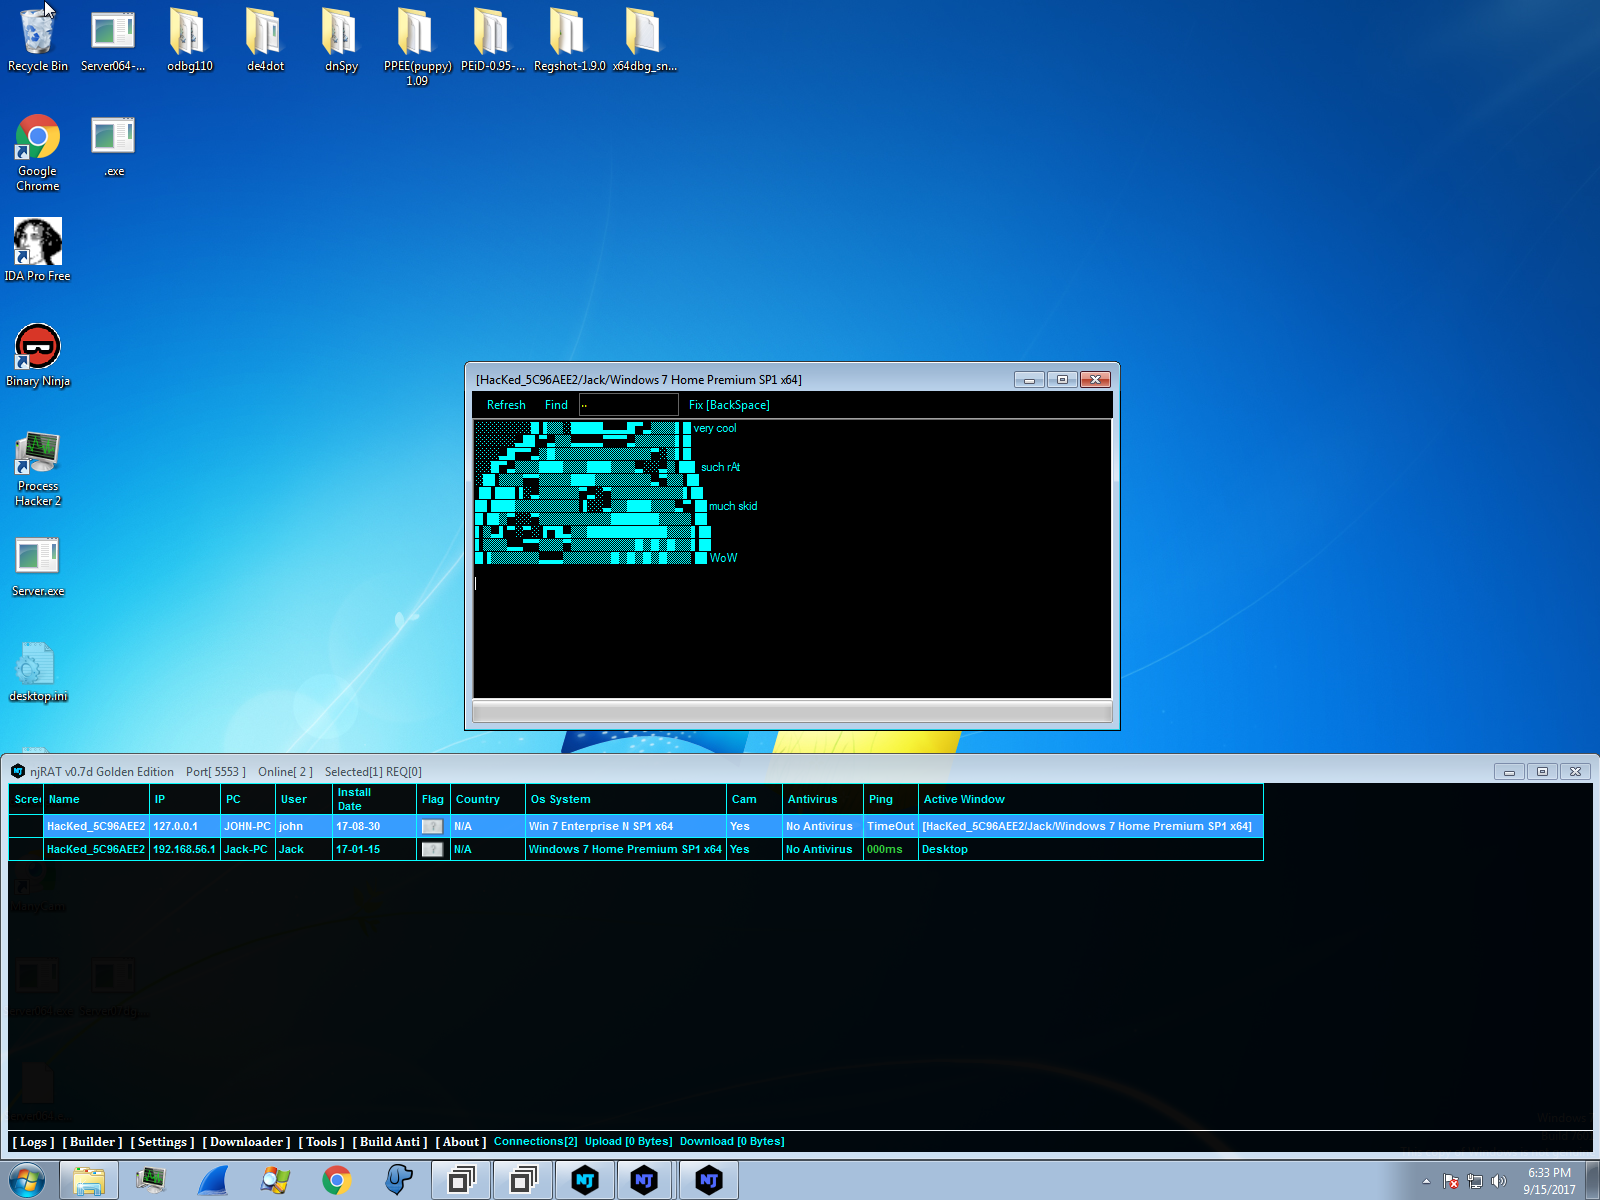 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 retrobyte/shadowtech-rat
An example of a remote administration tool.

 sorcerio/code-roulette
Code Roulette is a terminal interface based (TUI), online multiplayer, Russian Roulette game where the loser executes the winner's Python payload…
 dakotanelson/multicat
PoC RAT using the sneaky-creeper data exfiltration library
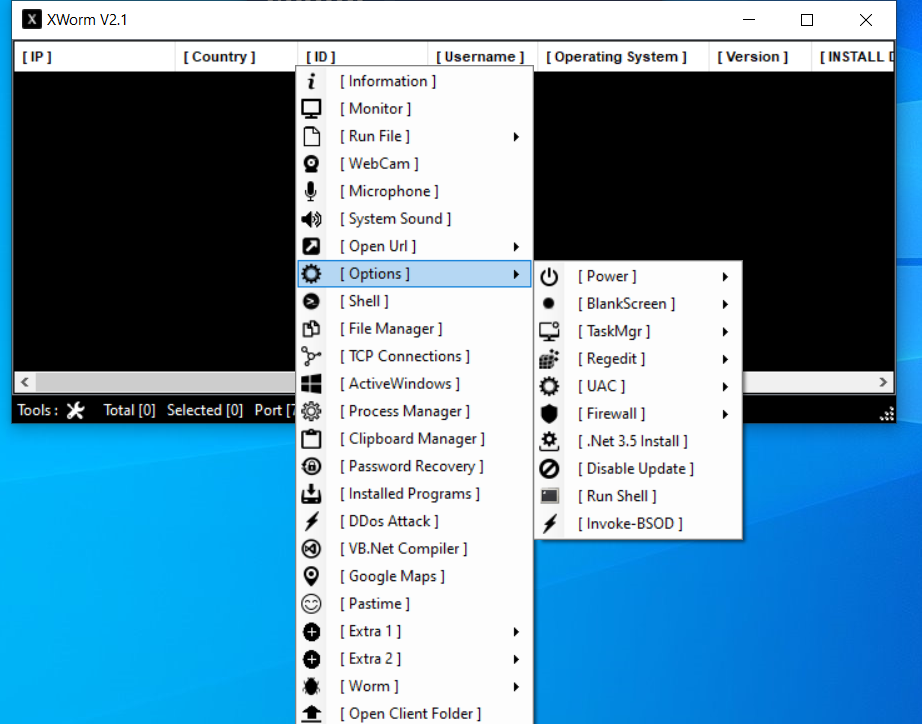 manturever/xworm-rat
⭐️The famous XWorm RAT, version 2.1. Educational purposes only
 lewis-ricardo/amaranth-project
CVE-2025-8088 exploitation chain + Quasar C2 multi-stage payload delivery