
ghost
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
command-and-controleducationmalware-analysis+5
1.1k
ahxr/ghostLightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 igh0st/gh0st3.6_src
Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 catatonicprime/tospovirus
A WiFi Pineapple infecting worm.
 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
 maorbuskila/windows-x64-rat
Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…
 typetrait/pace
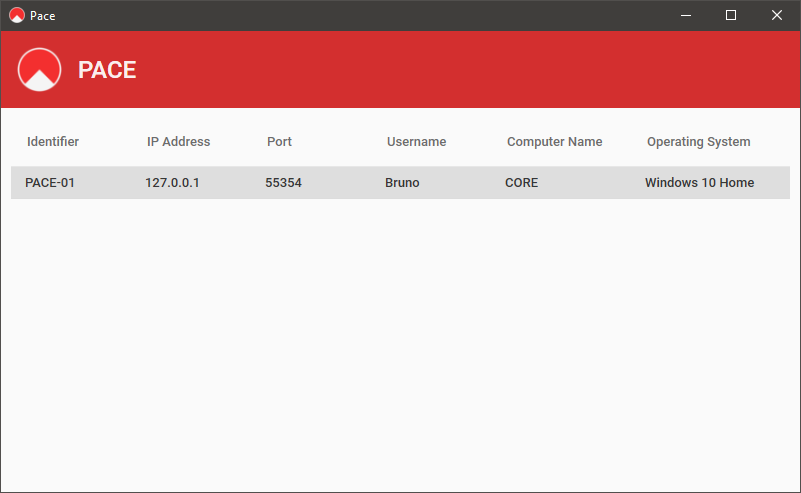
Remote Access Tool for Windows.
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 hash3lizer/sillyrat
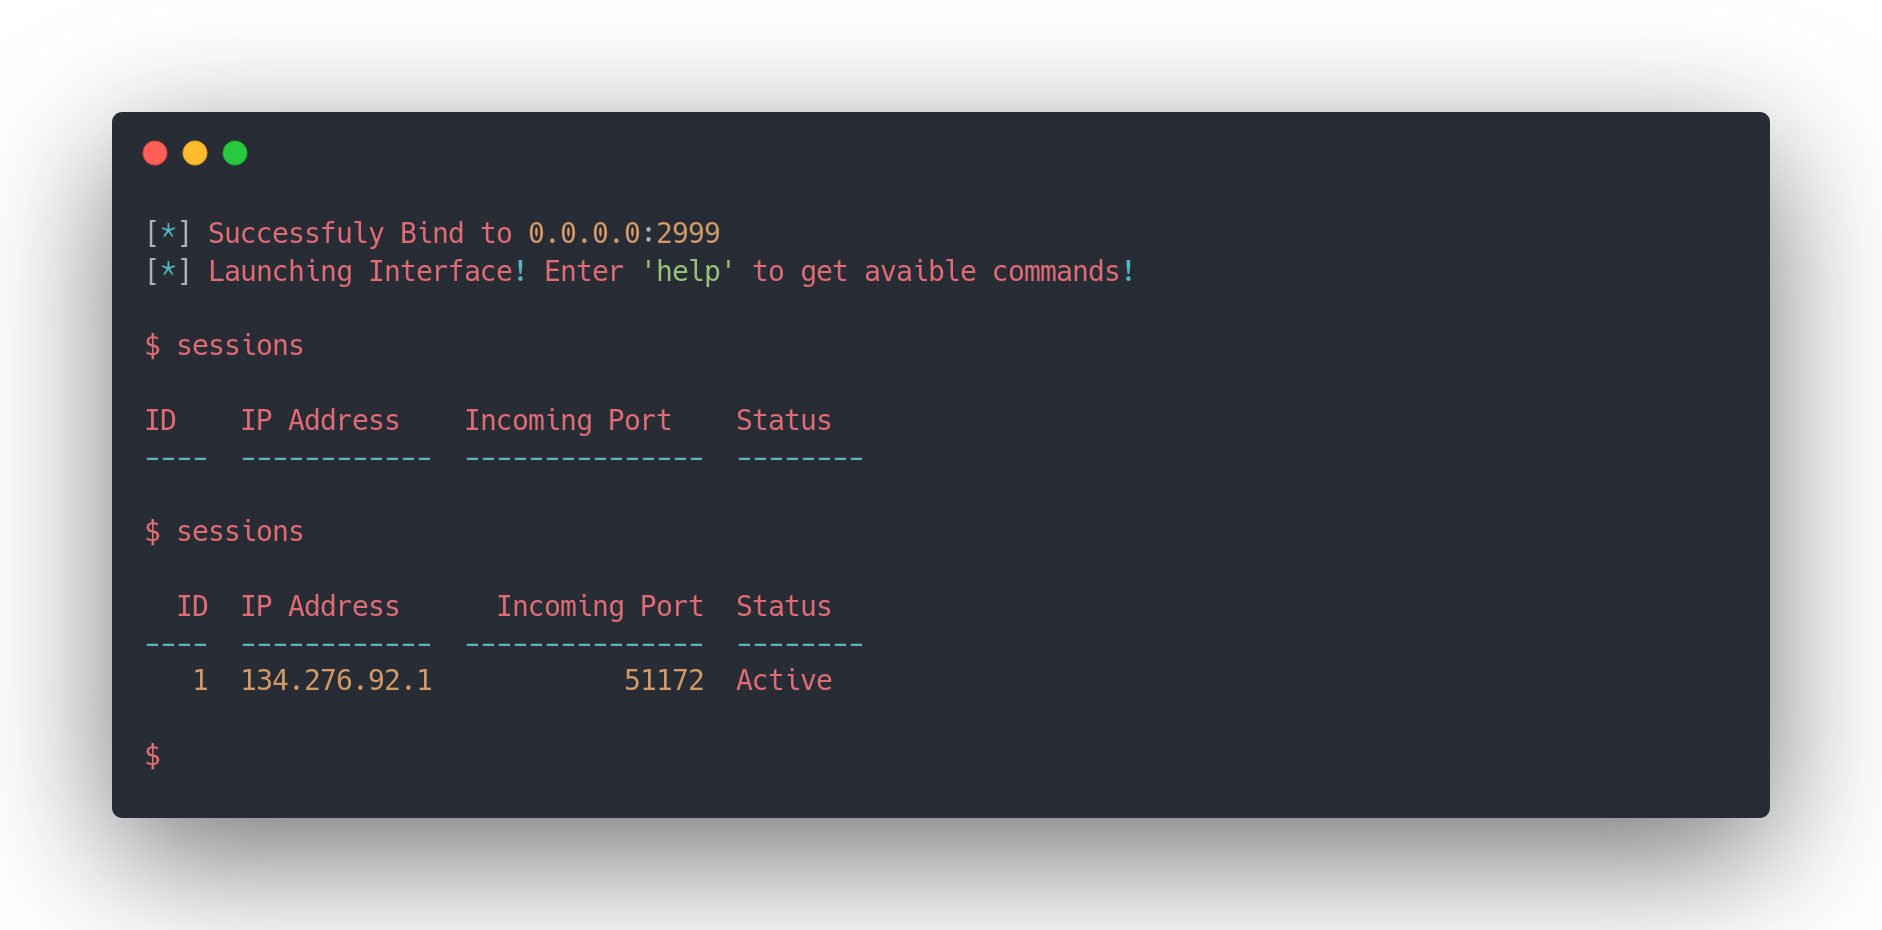
A Python based RAT 🐀 (Remote Access Trojan) for getting reverse shell 🖥️
 darkcodersc/subseven
SubSeven Legacy Official Source Code Repository
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
 rafabd1/cve-2026-75604-poc
Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
 nyan-x-cat/njrat-0.7d-stub-csharp
njRAT C# Stub - Fixed For PowerShell