Orwell-RAT-and-Botnet
 correcthorsebatterystaple-sudo/orwell-rat-and-botnet
Orwell is a RAT and Botnet designed as a trio of programs.
command-and-controlpayload-generationpost-exploitation+2
31
correcthorsebatterystaple-sudo/orwell-rat-and-botnetOrwell is a RAT and Botnet designed as a trio of programs.

 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 chebuya/cve-2024-30850-chaos-rat-rce-poc
CHAOS RAT web panel path RCE PoC
 gbrn1/pirate
Python Remote Access Tool
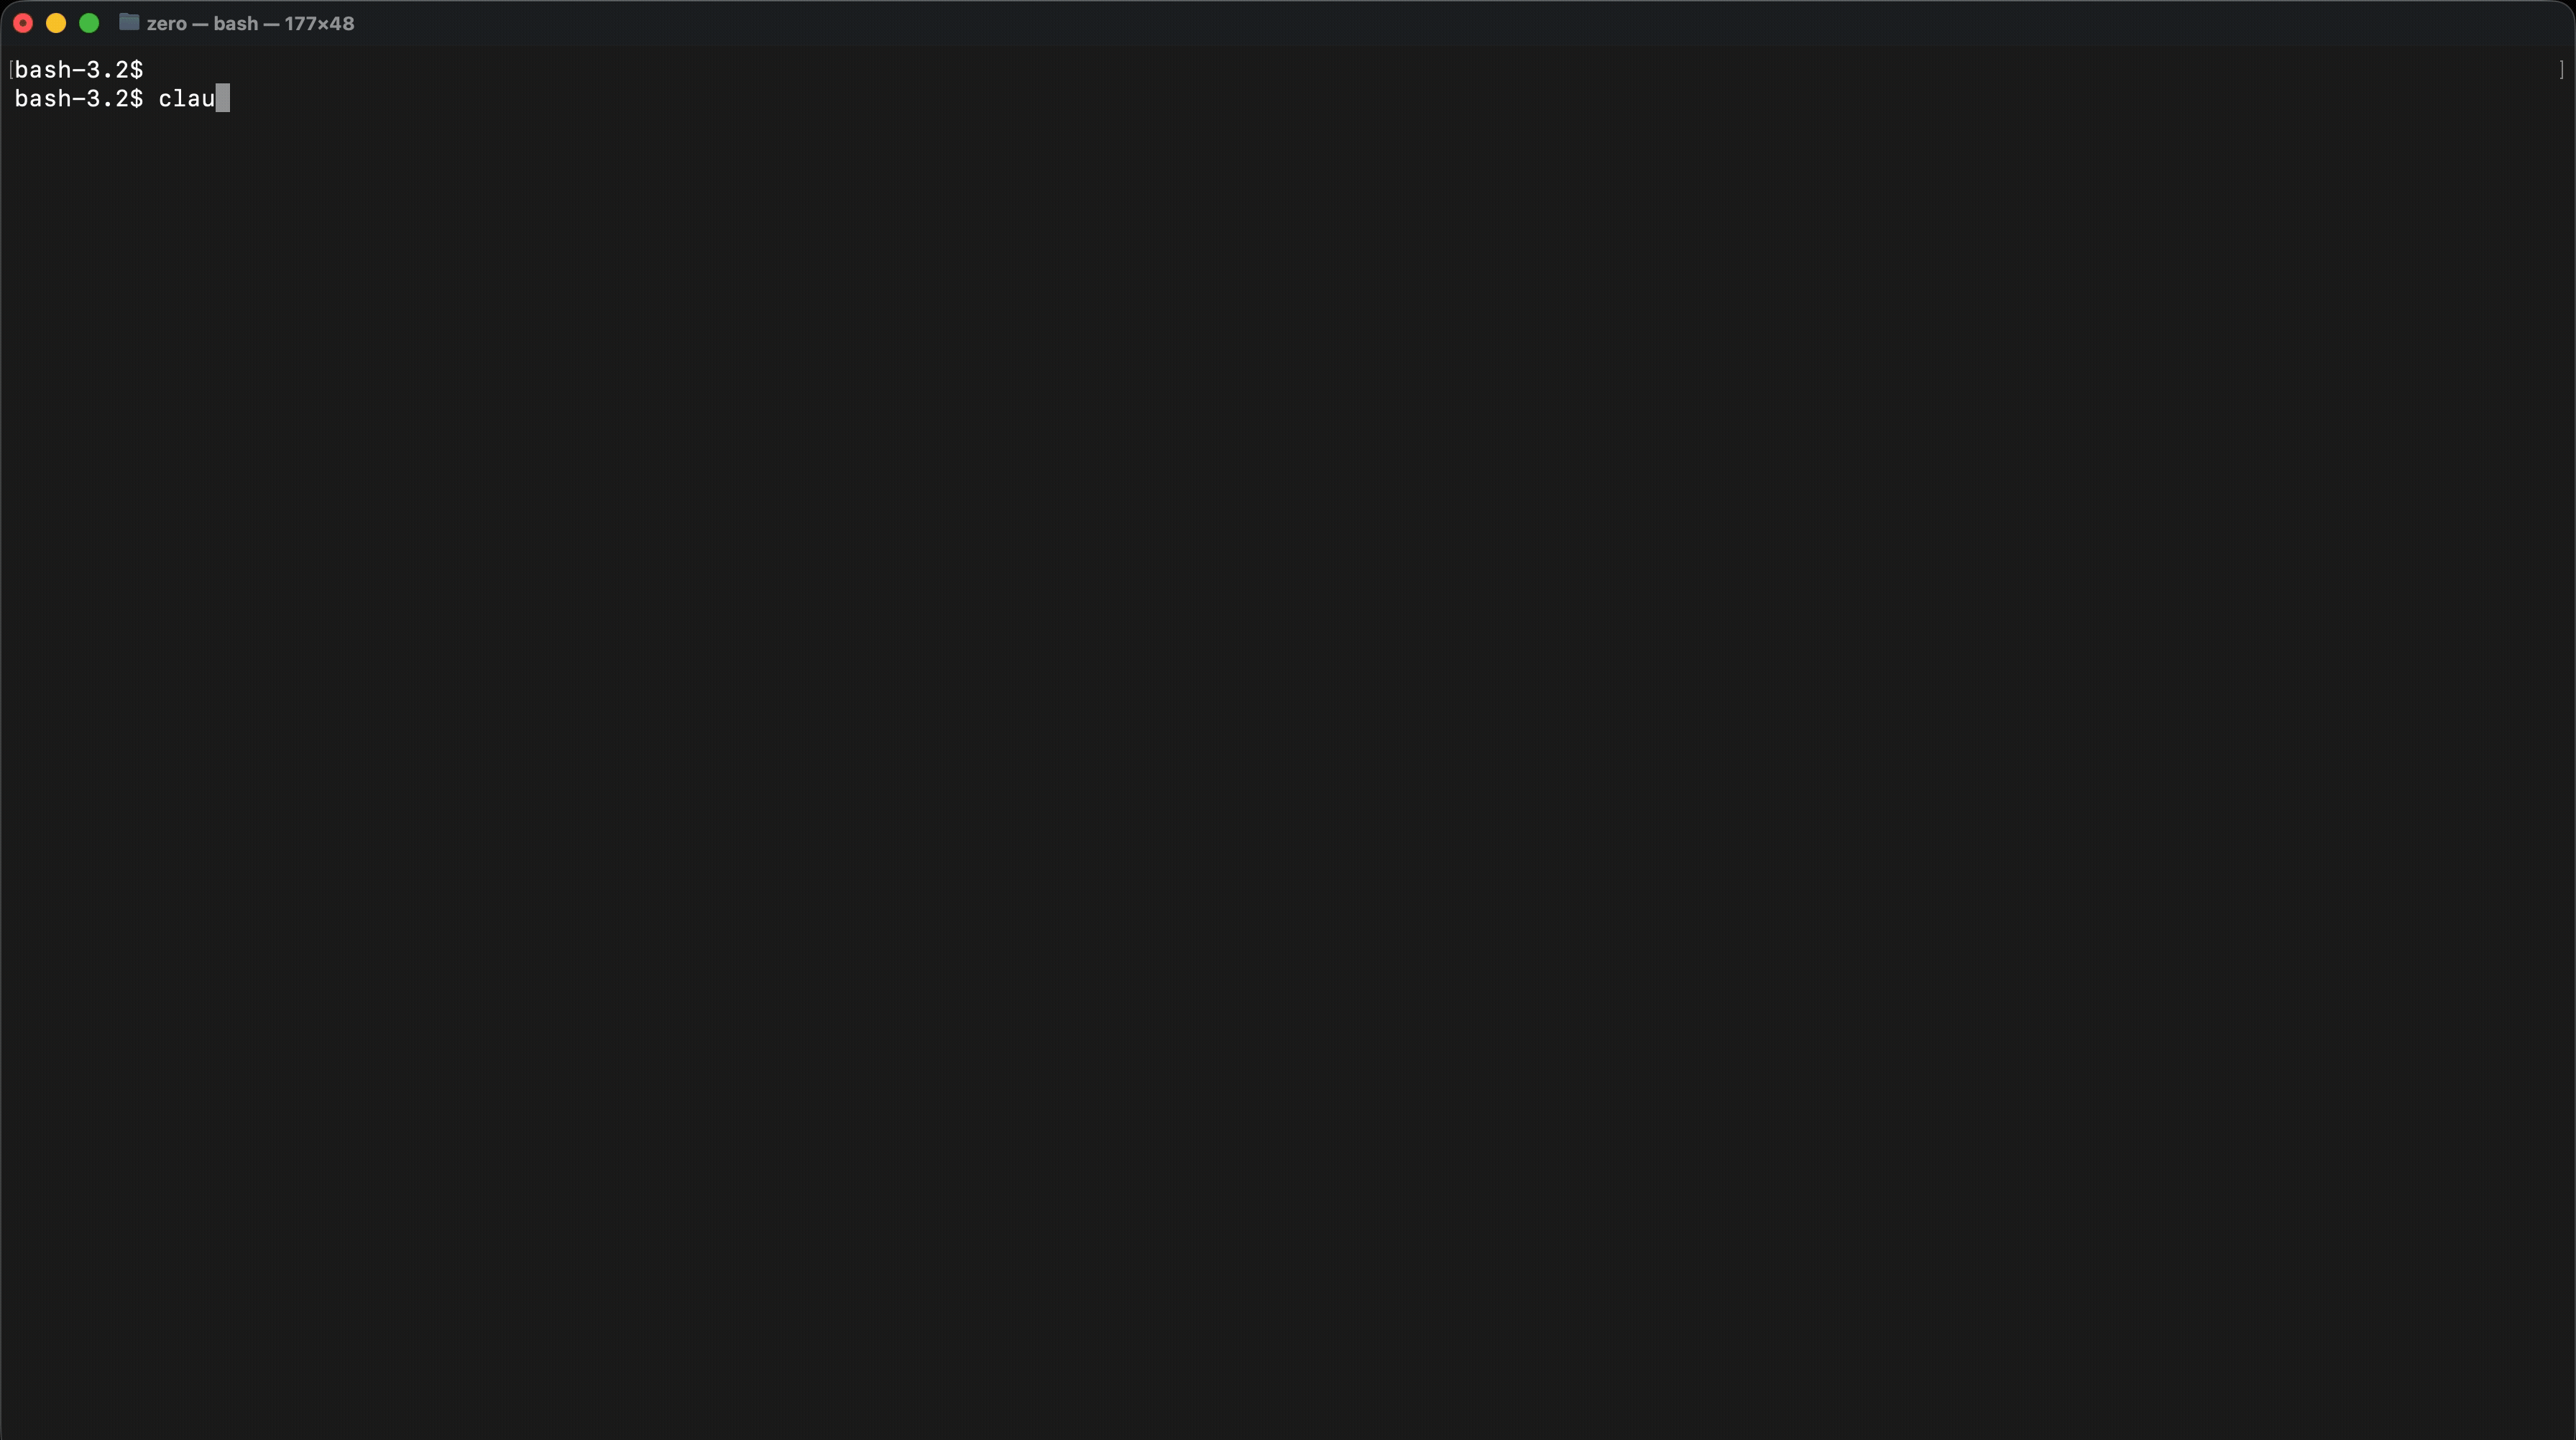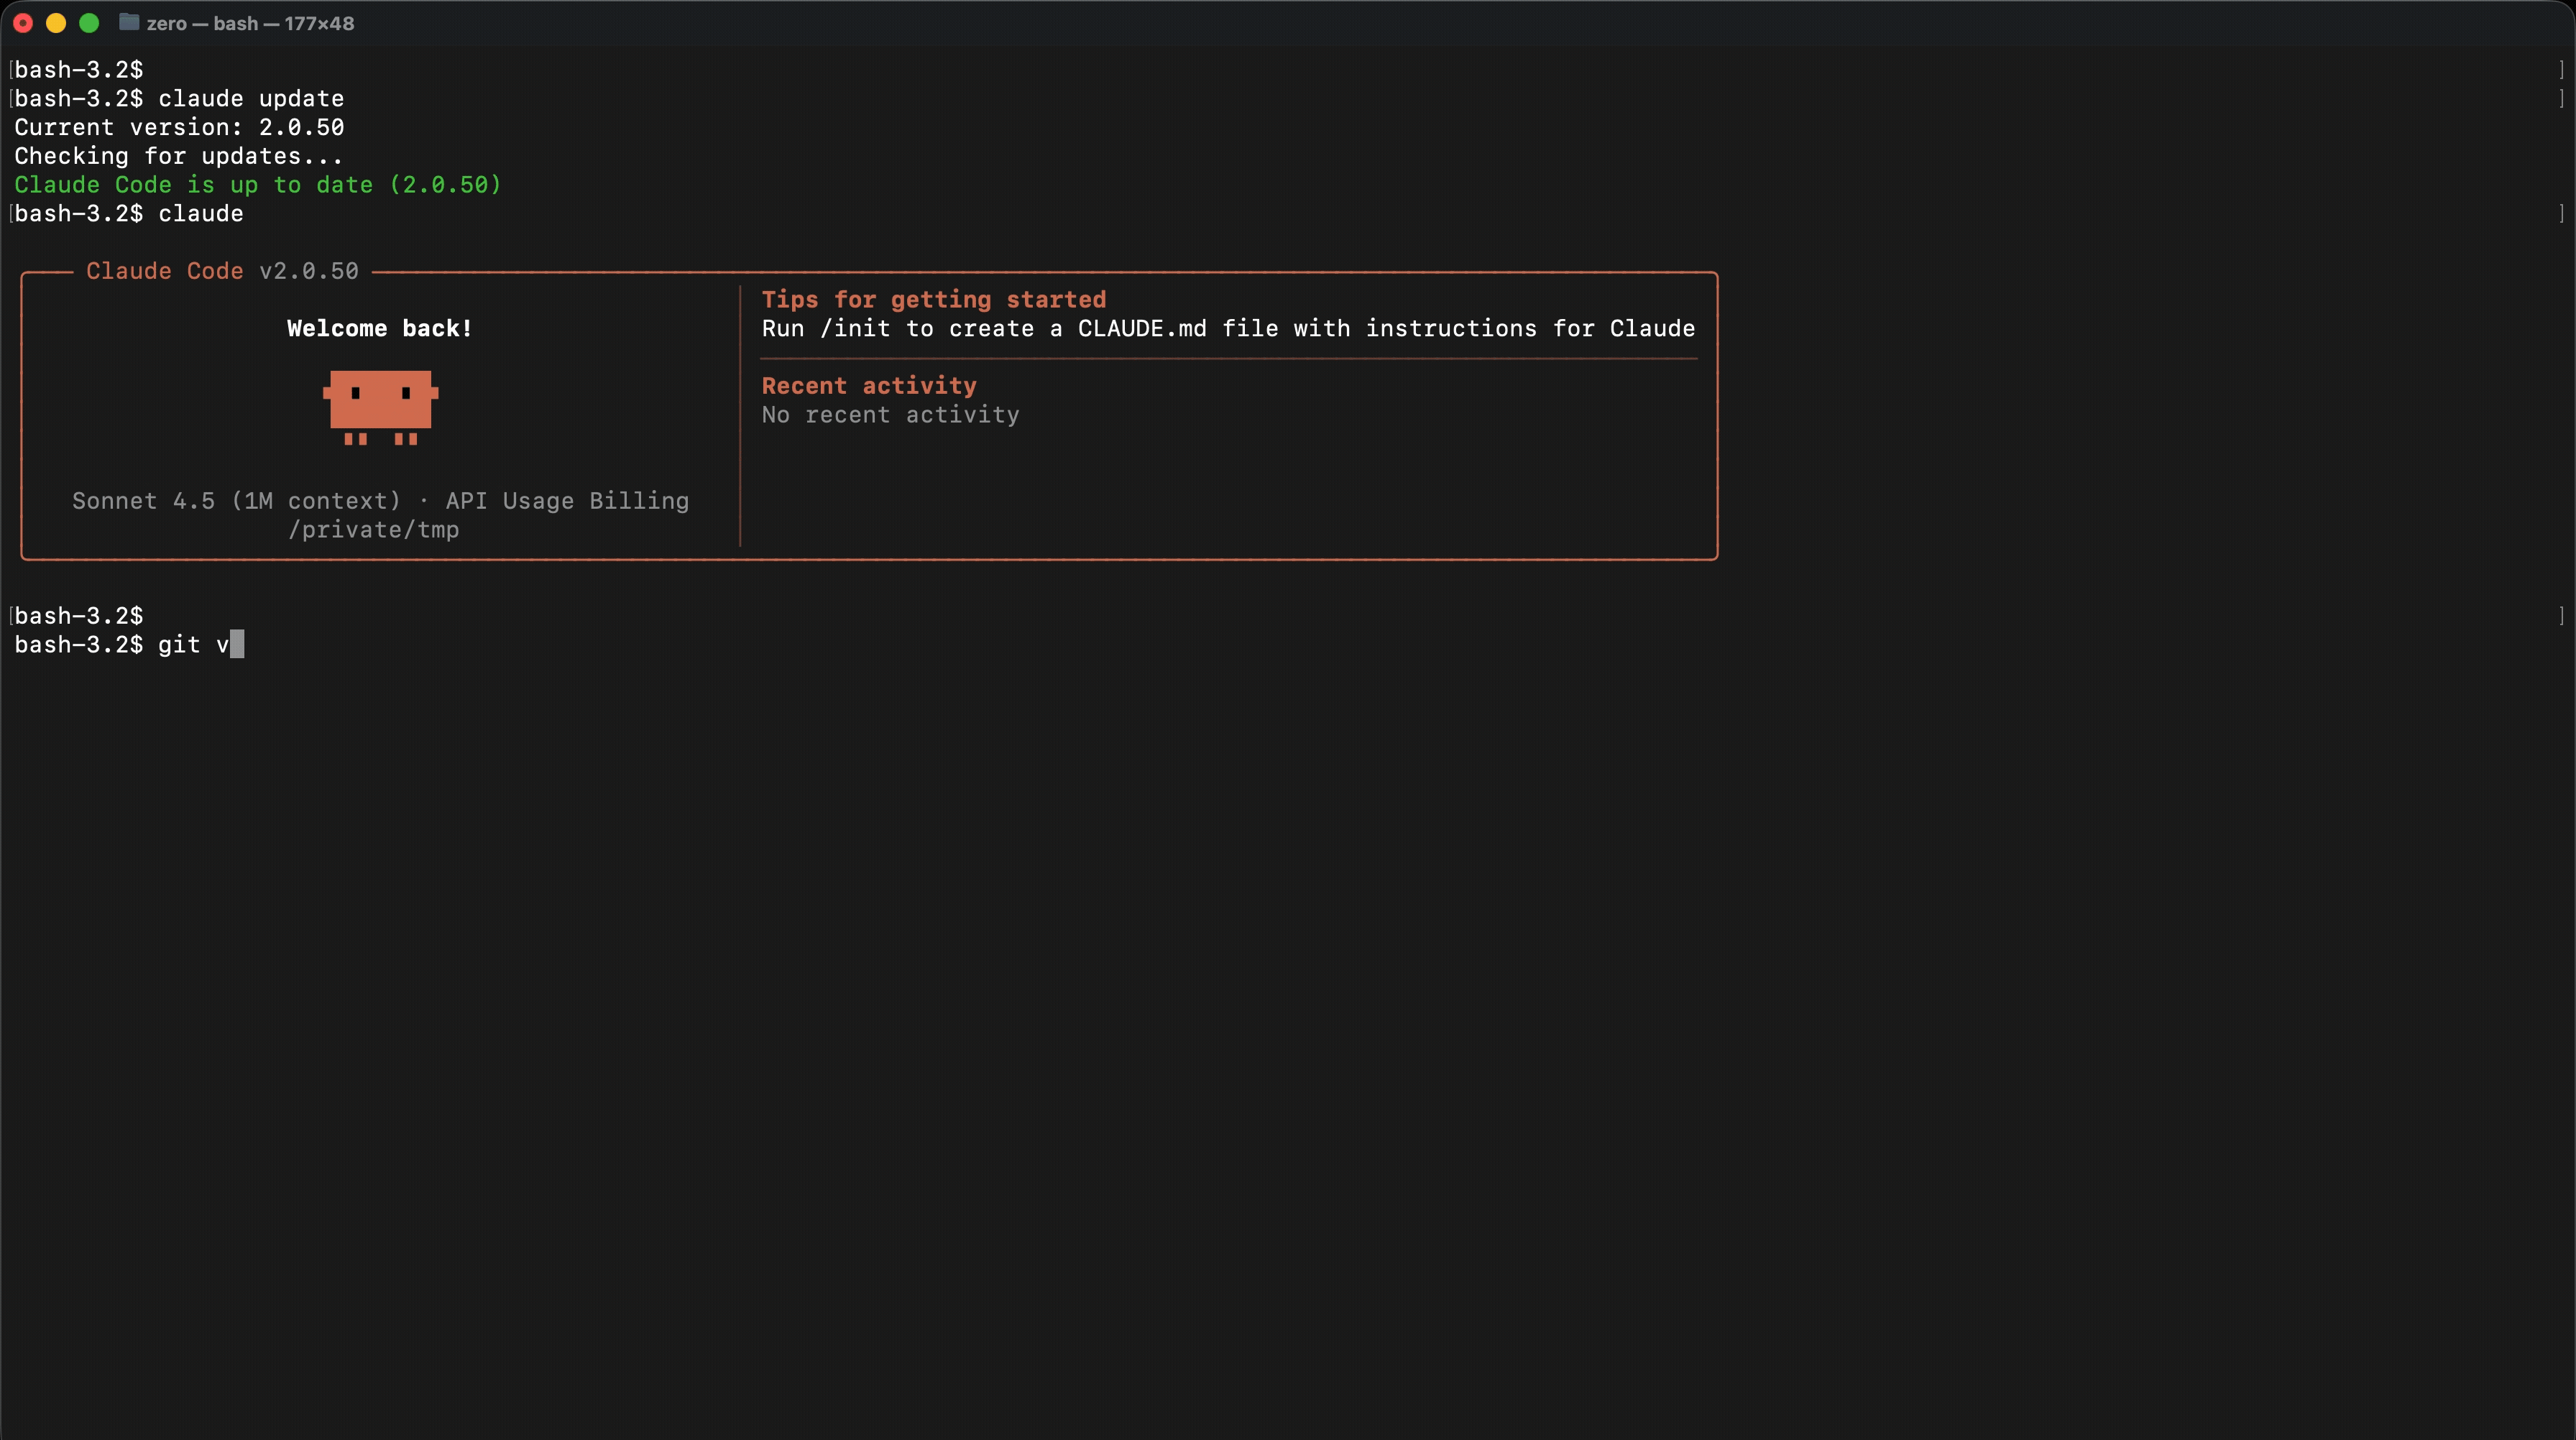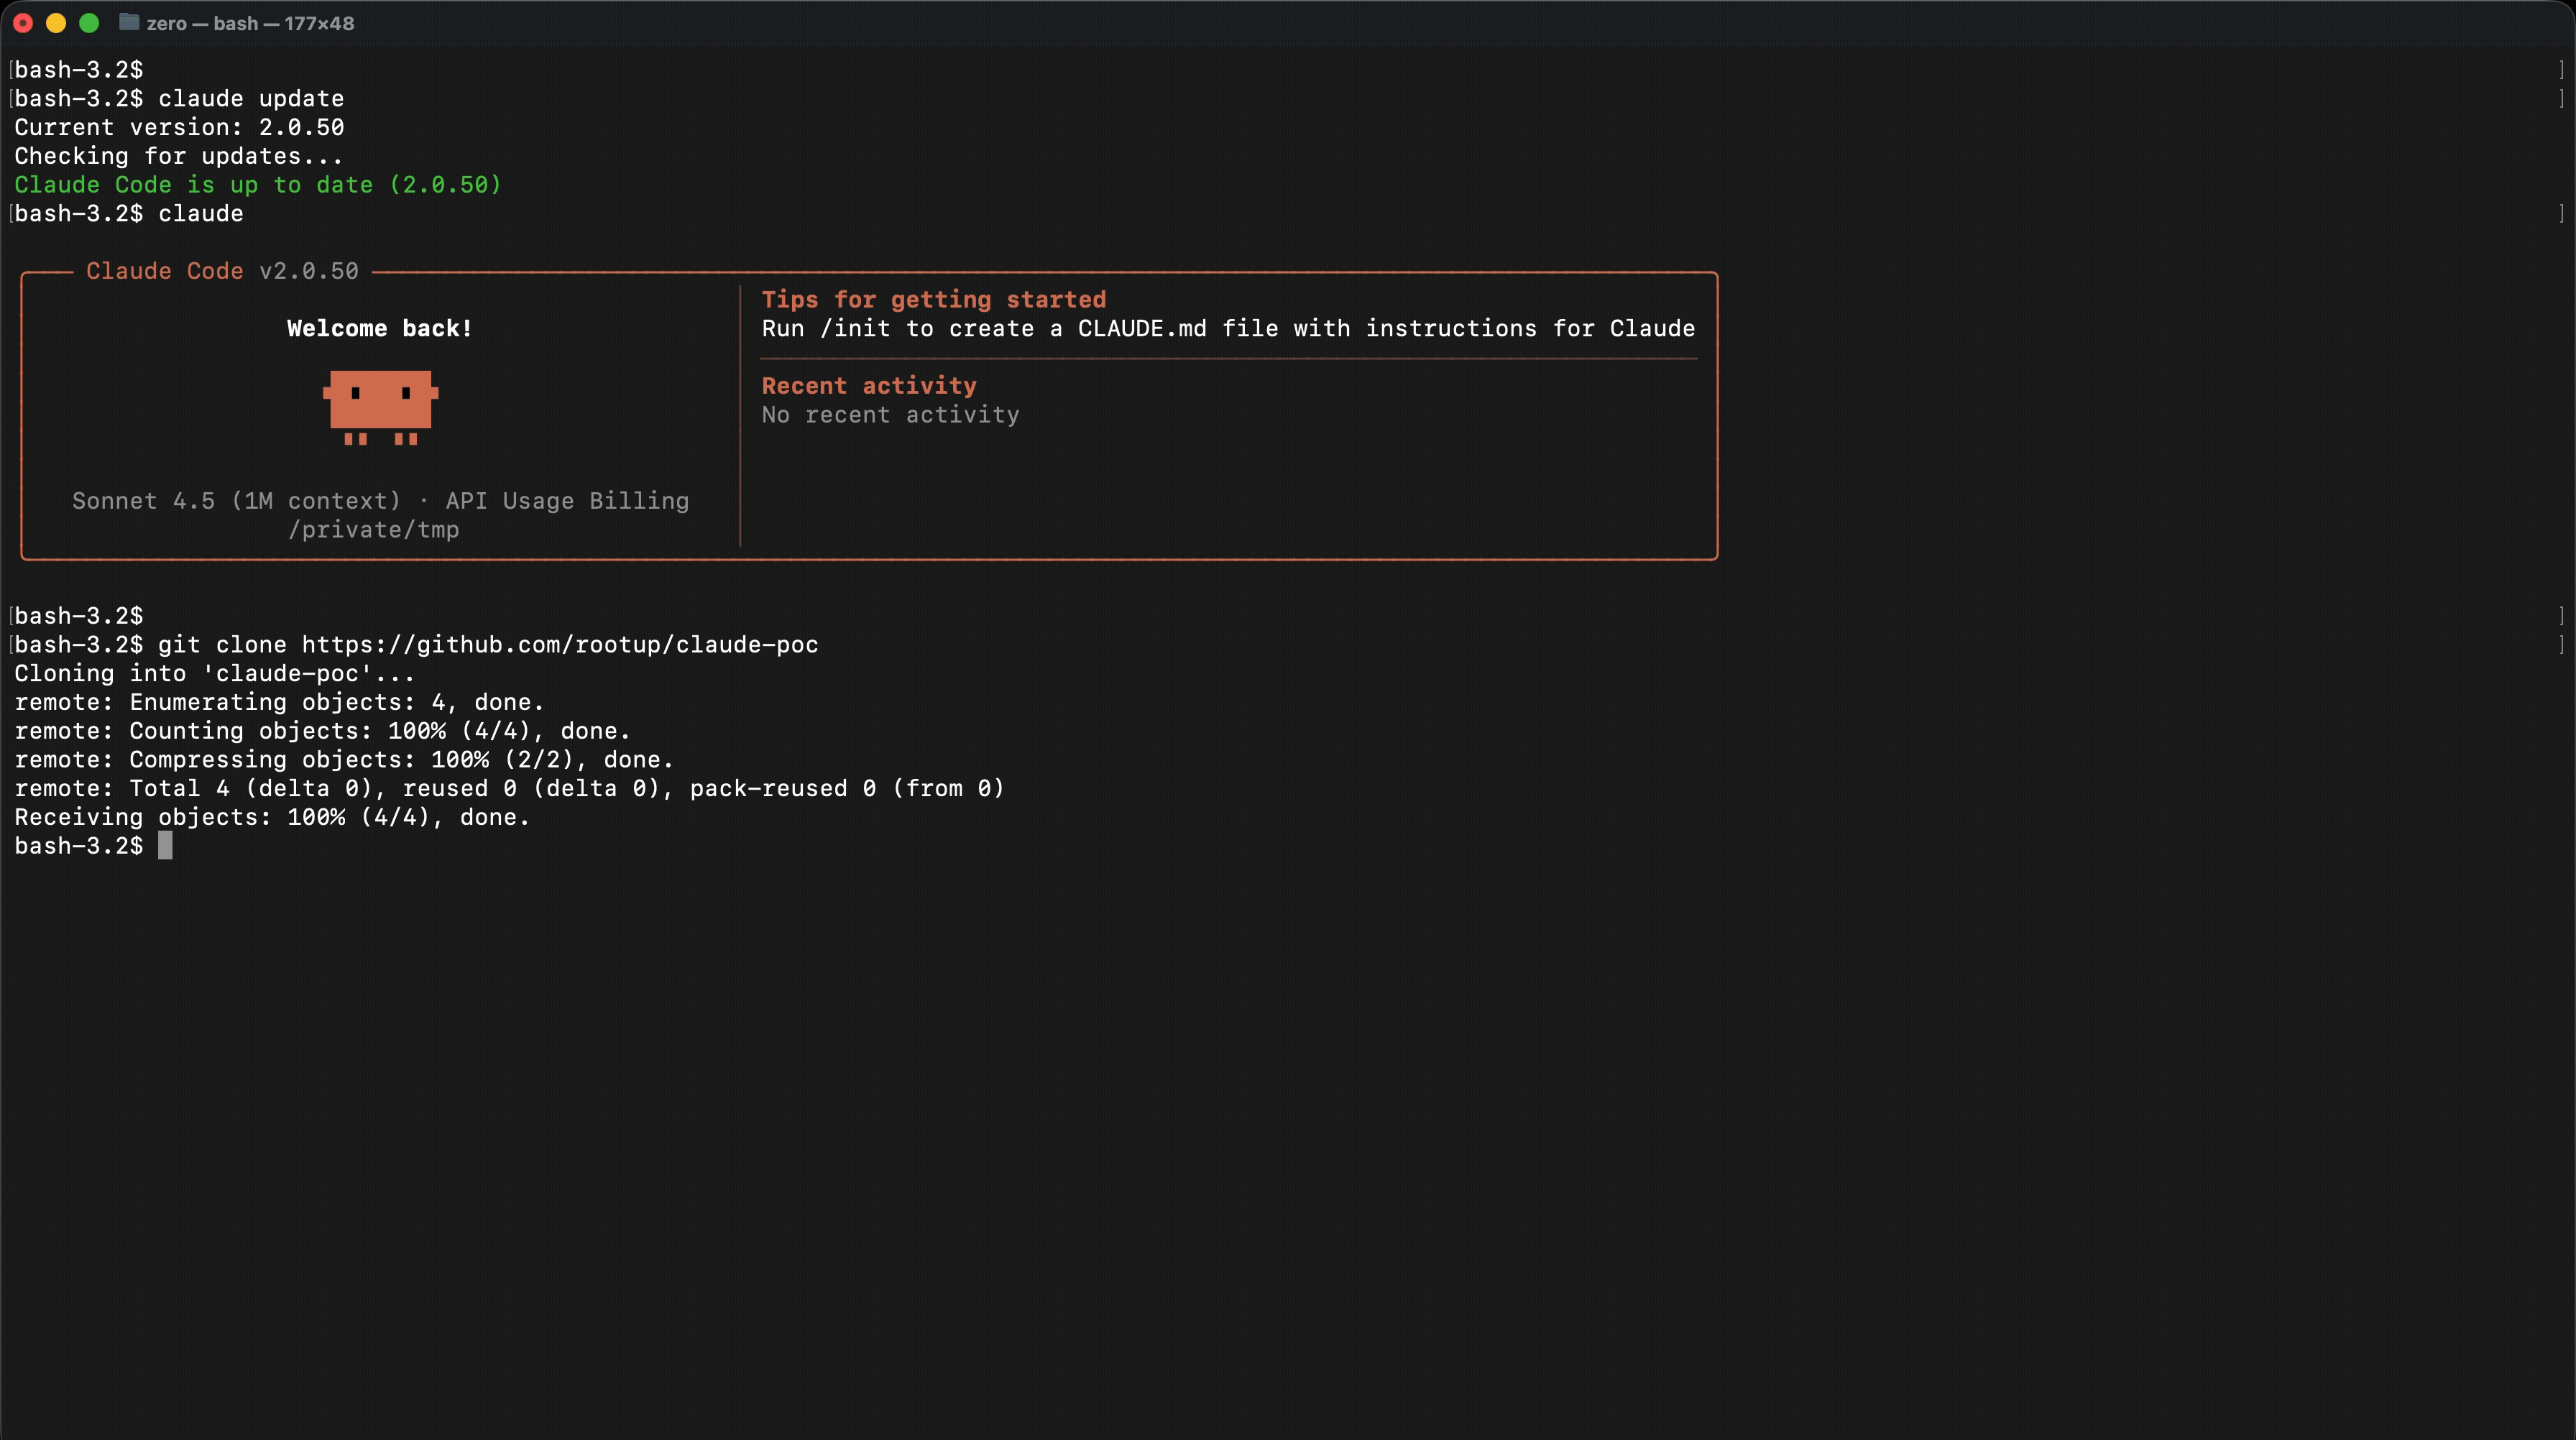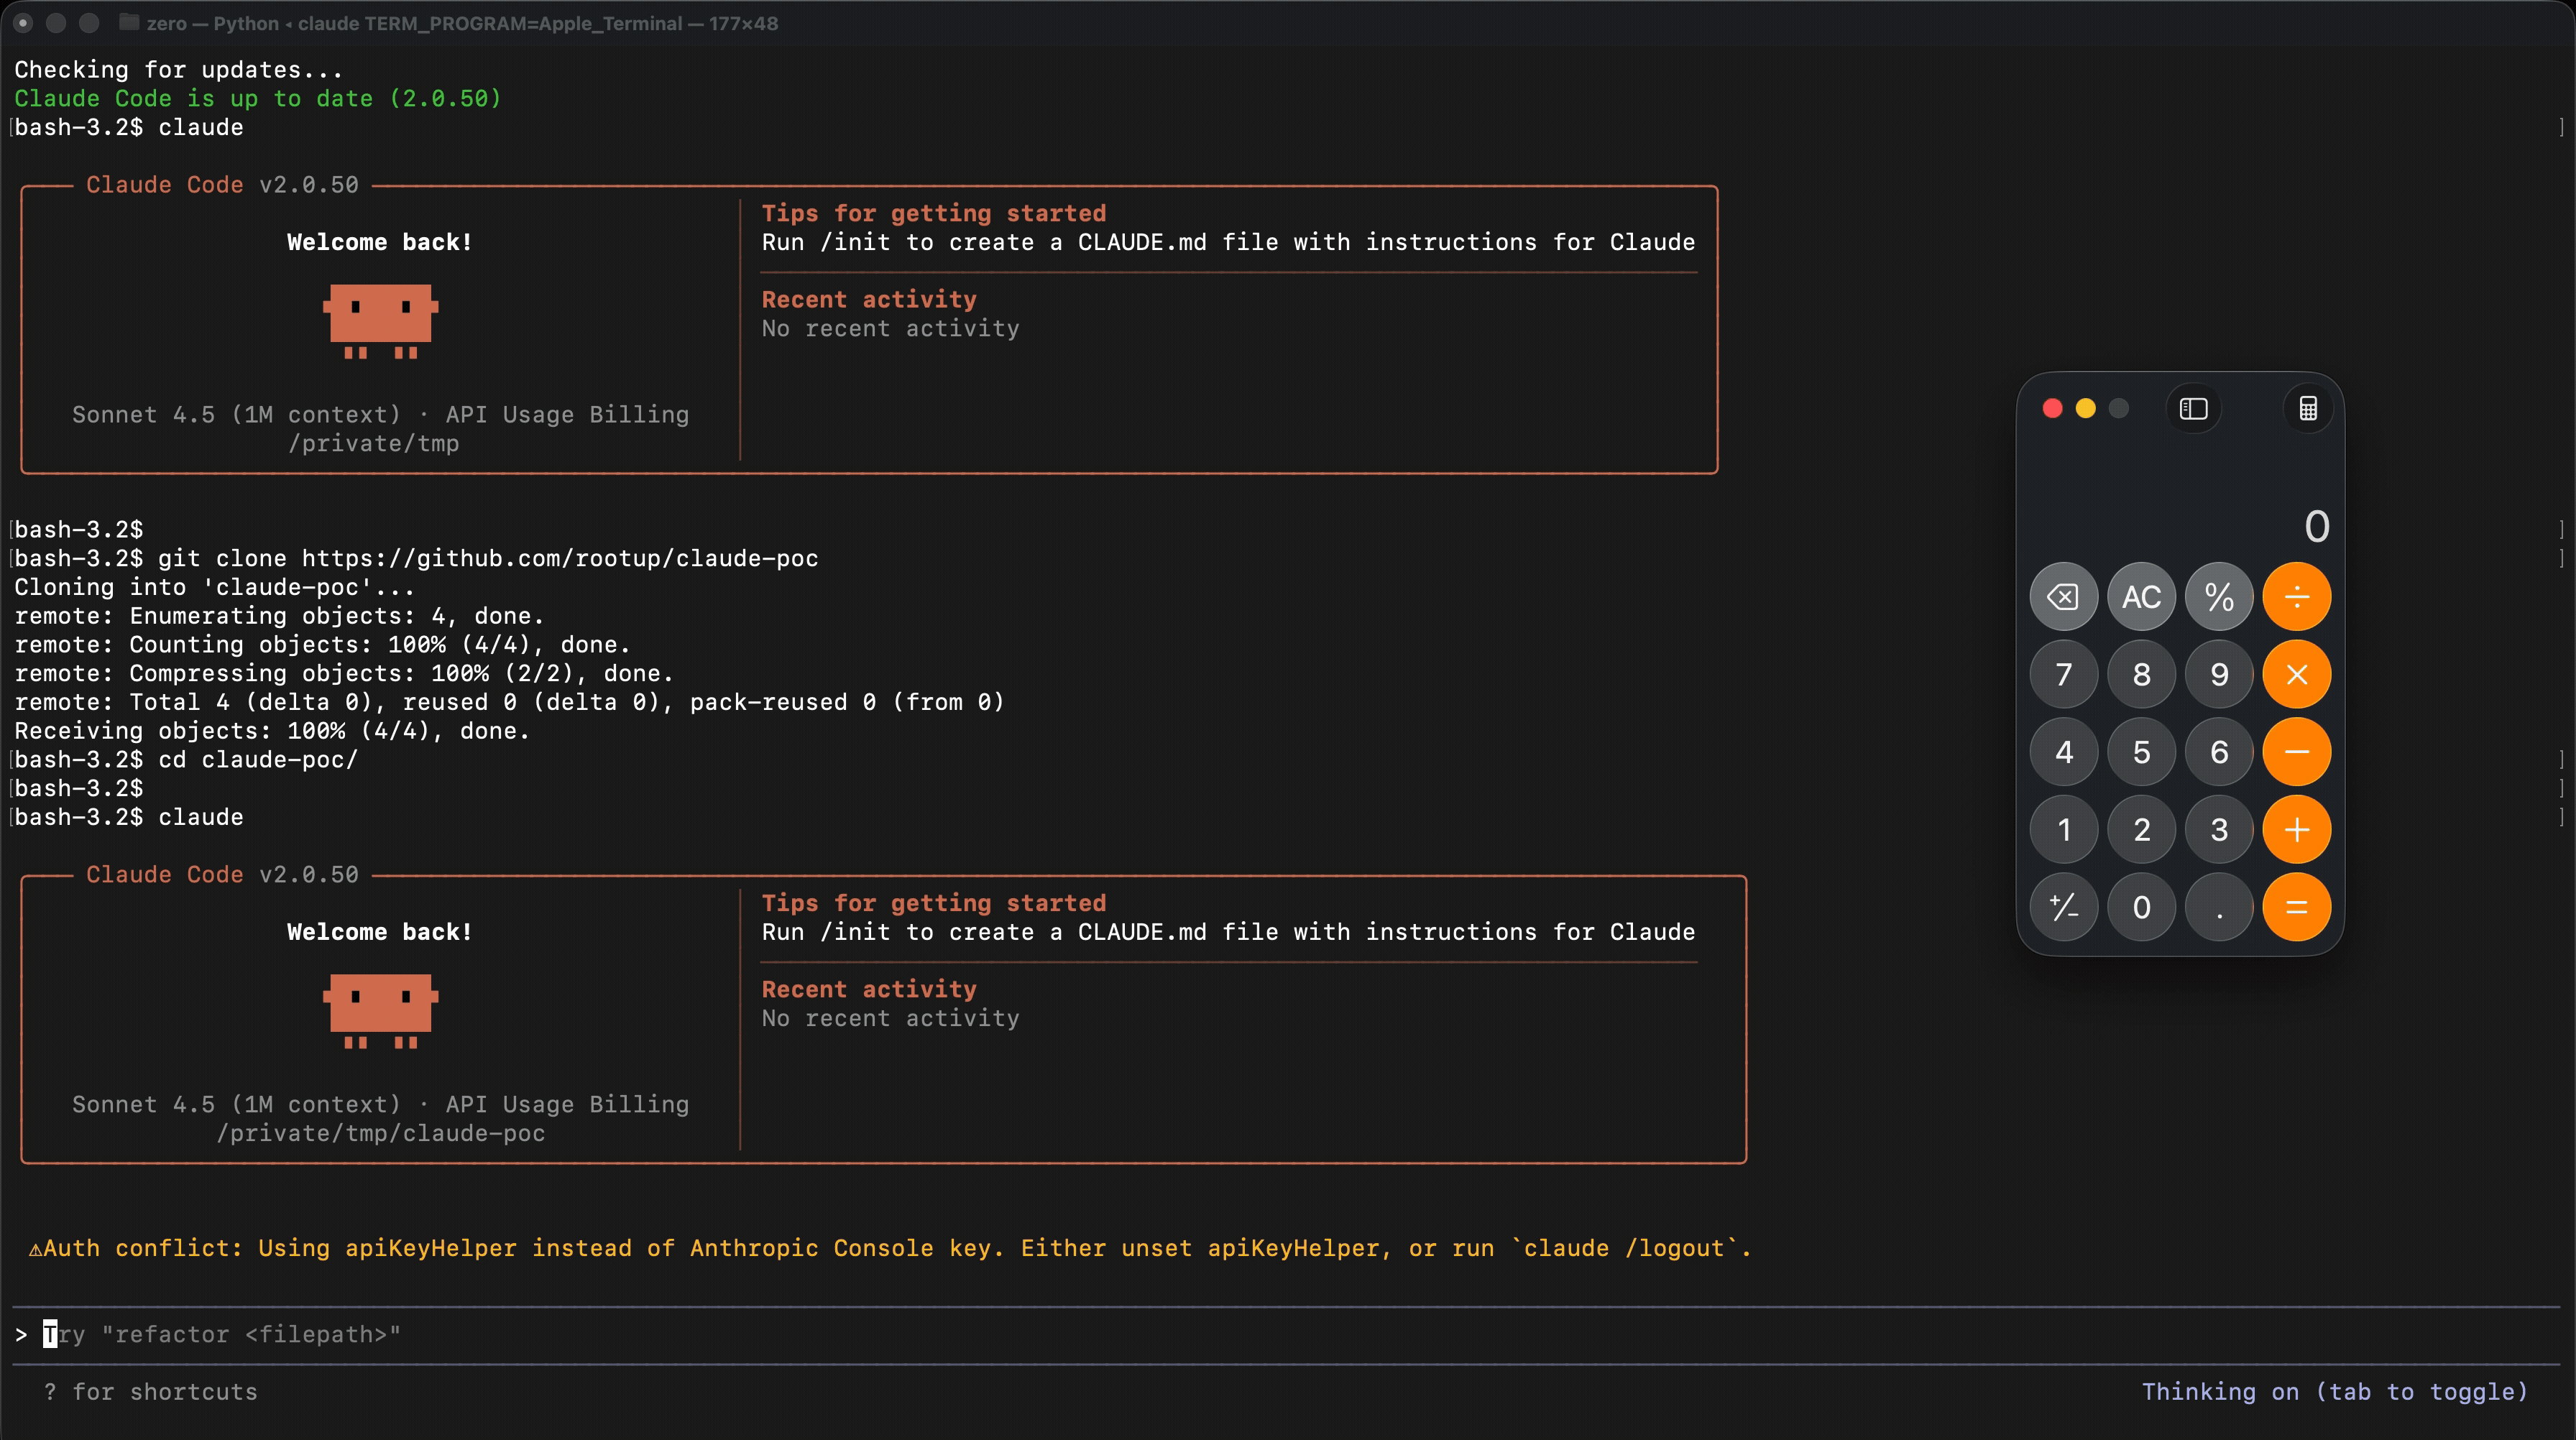 rootup/claude-poc
Claude Code Remote Code Execution
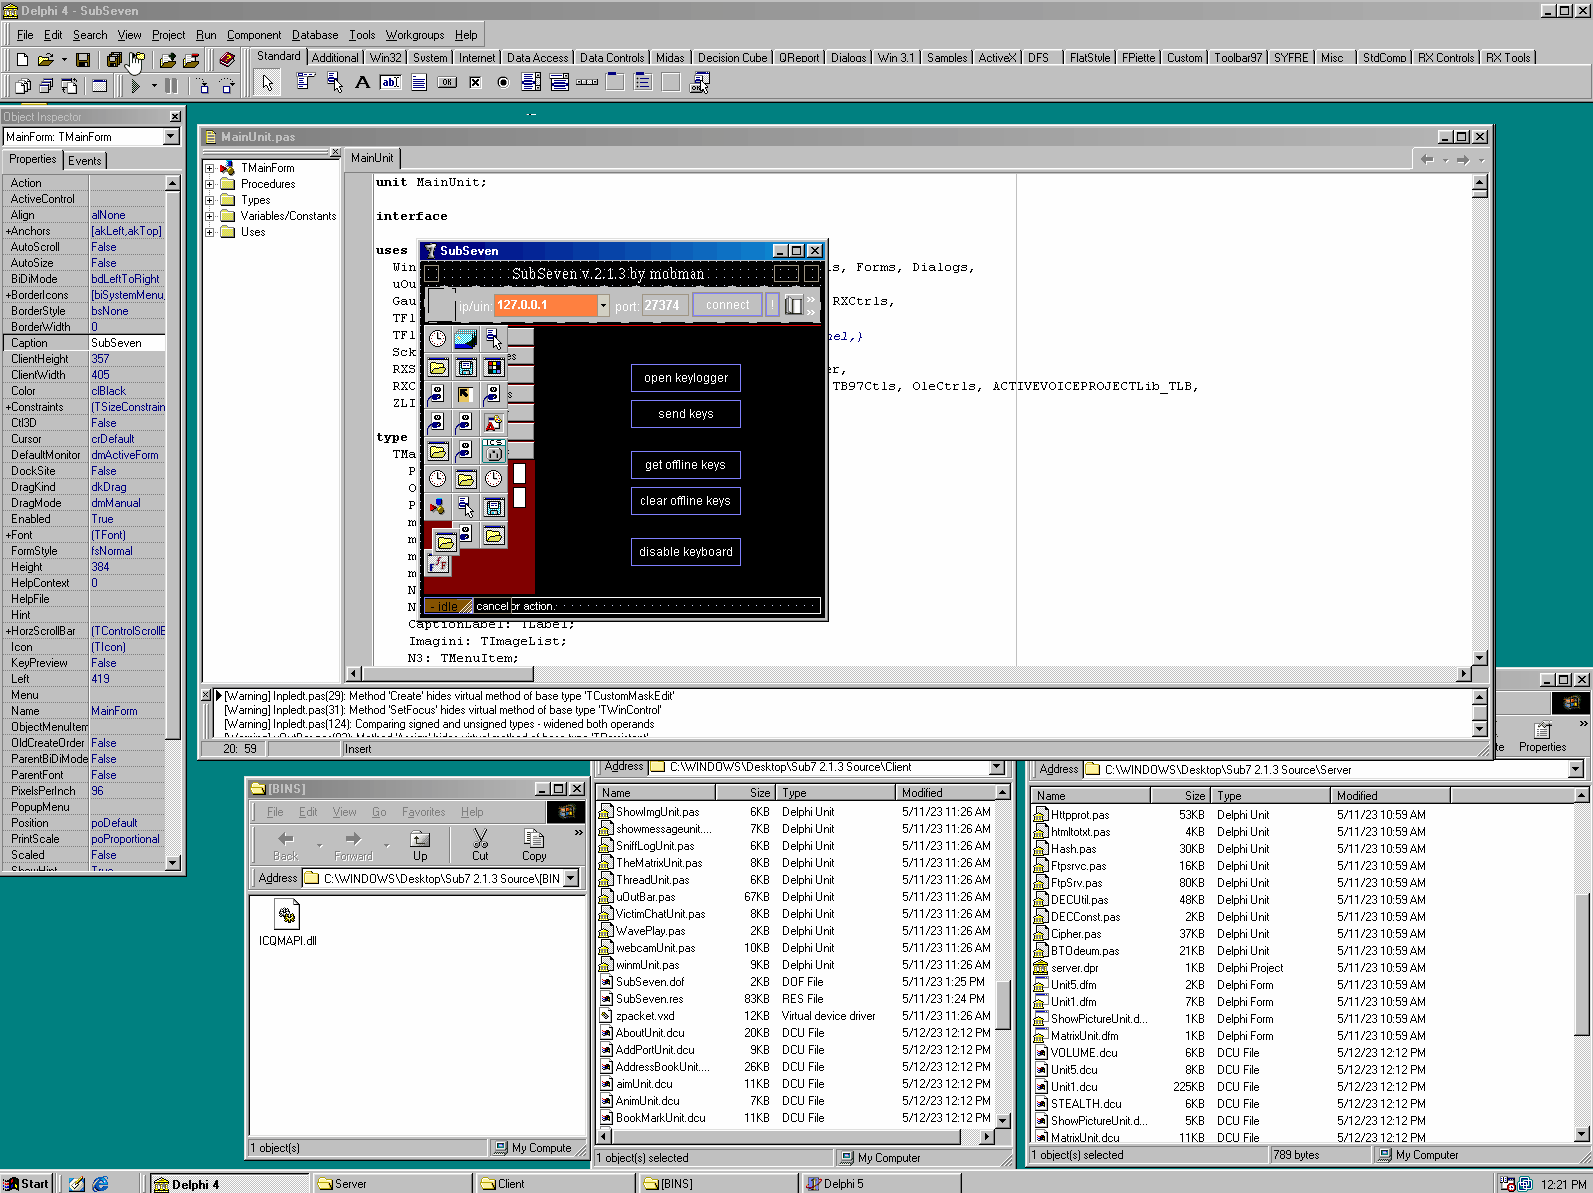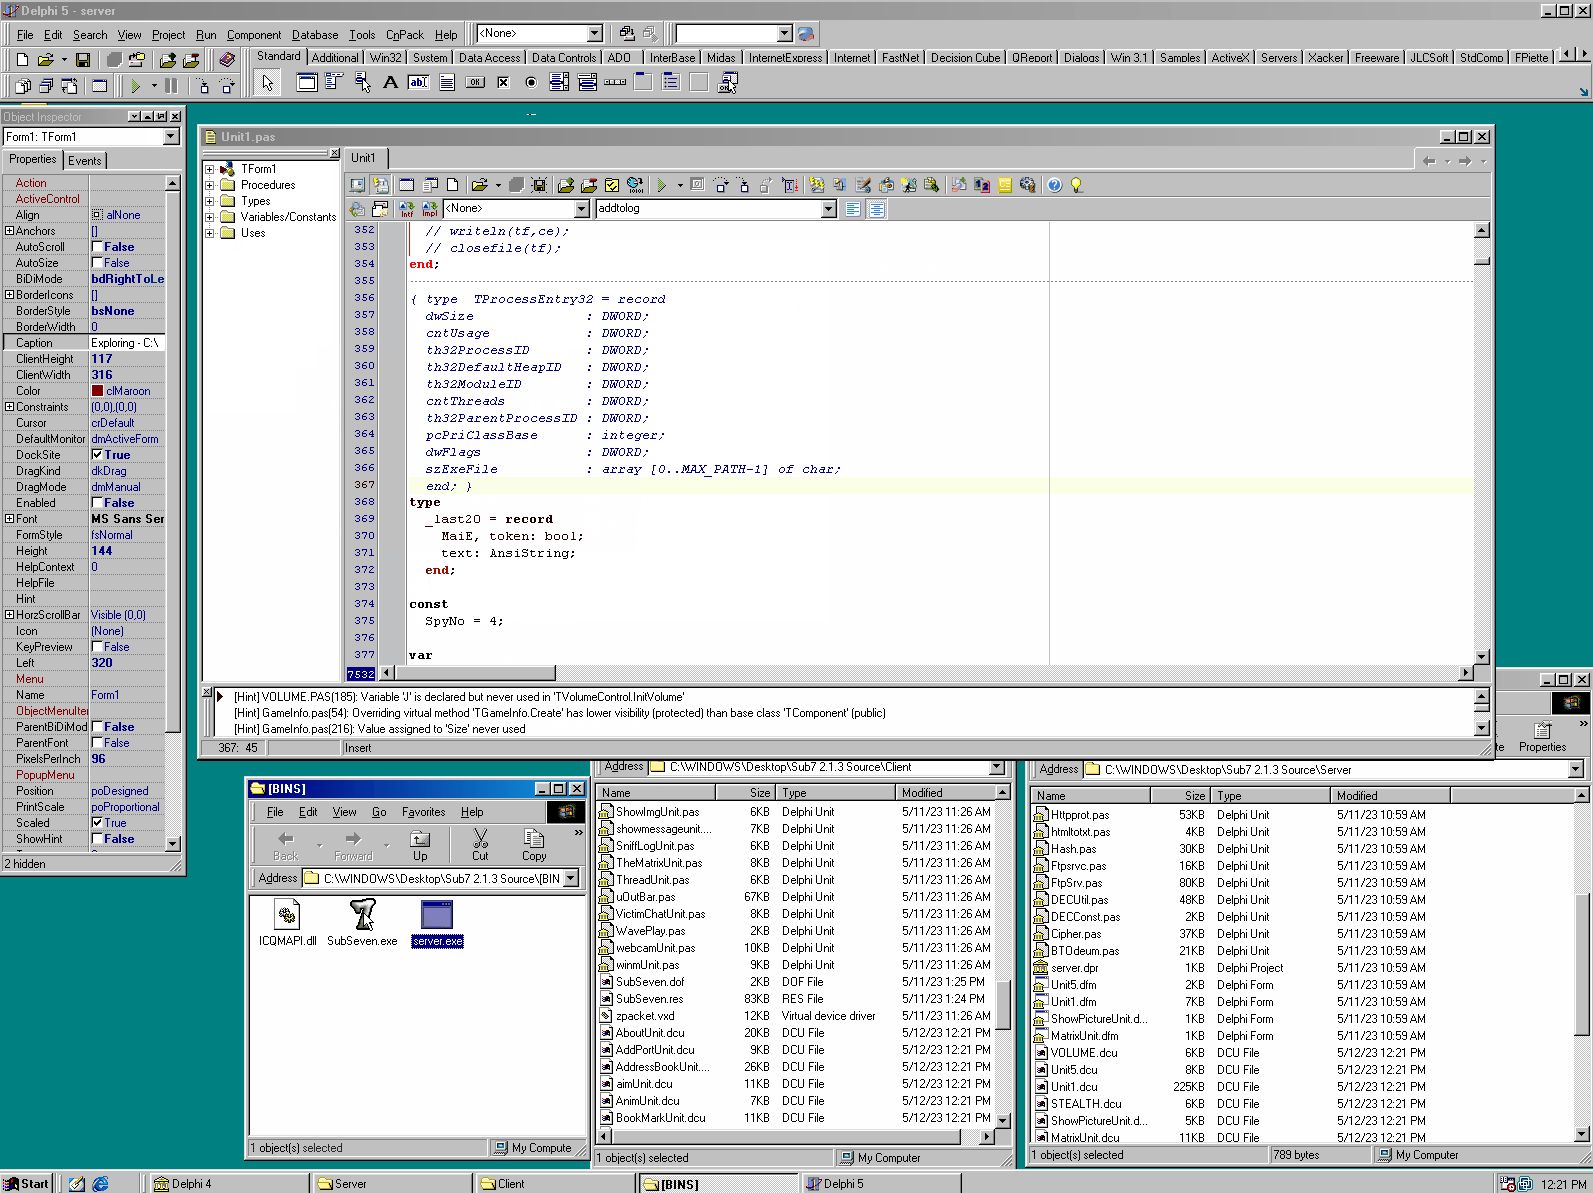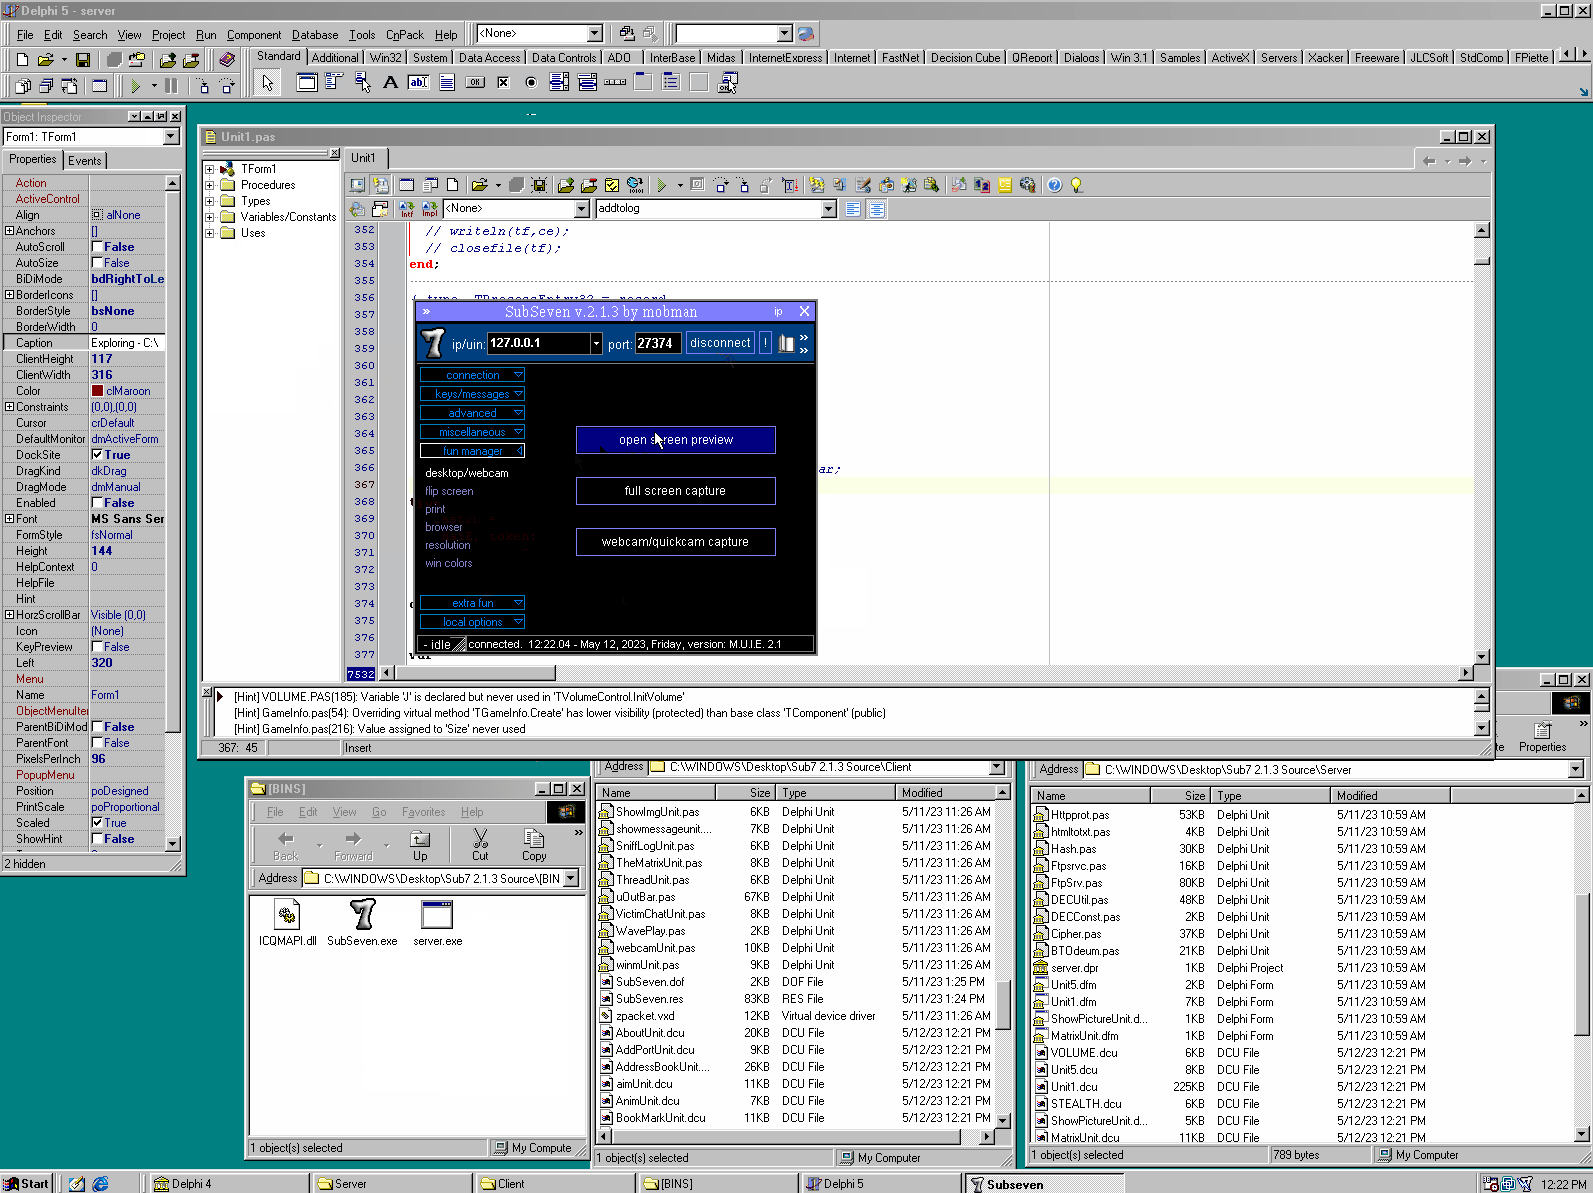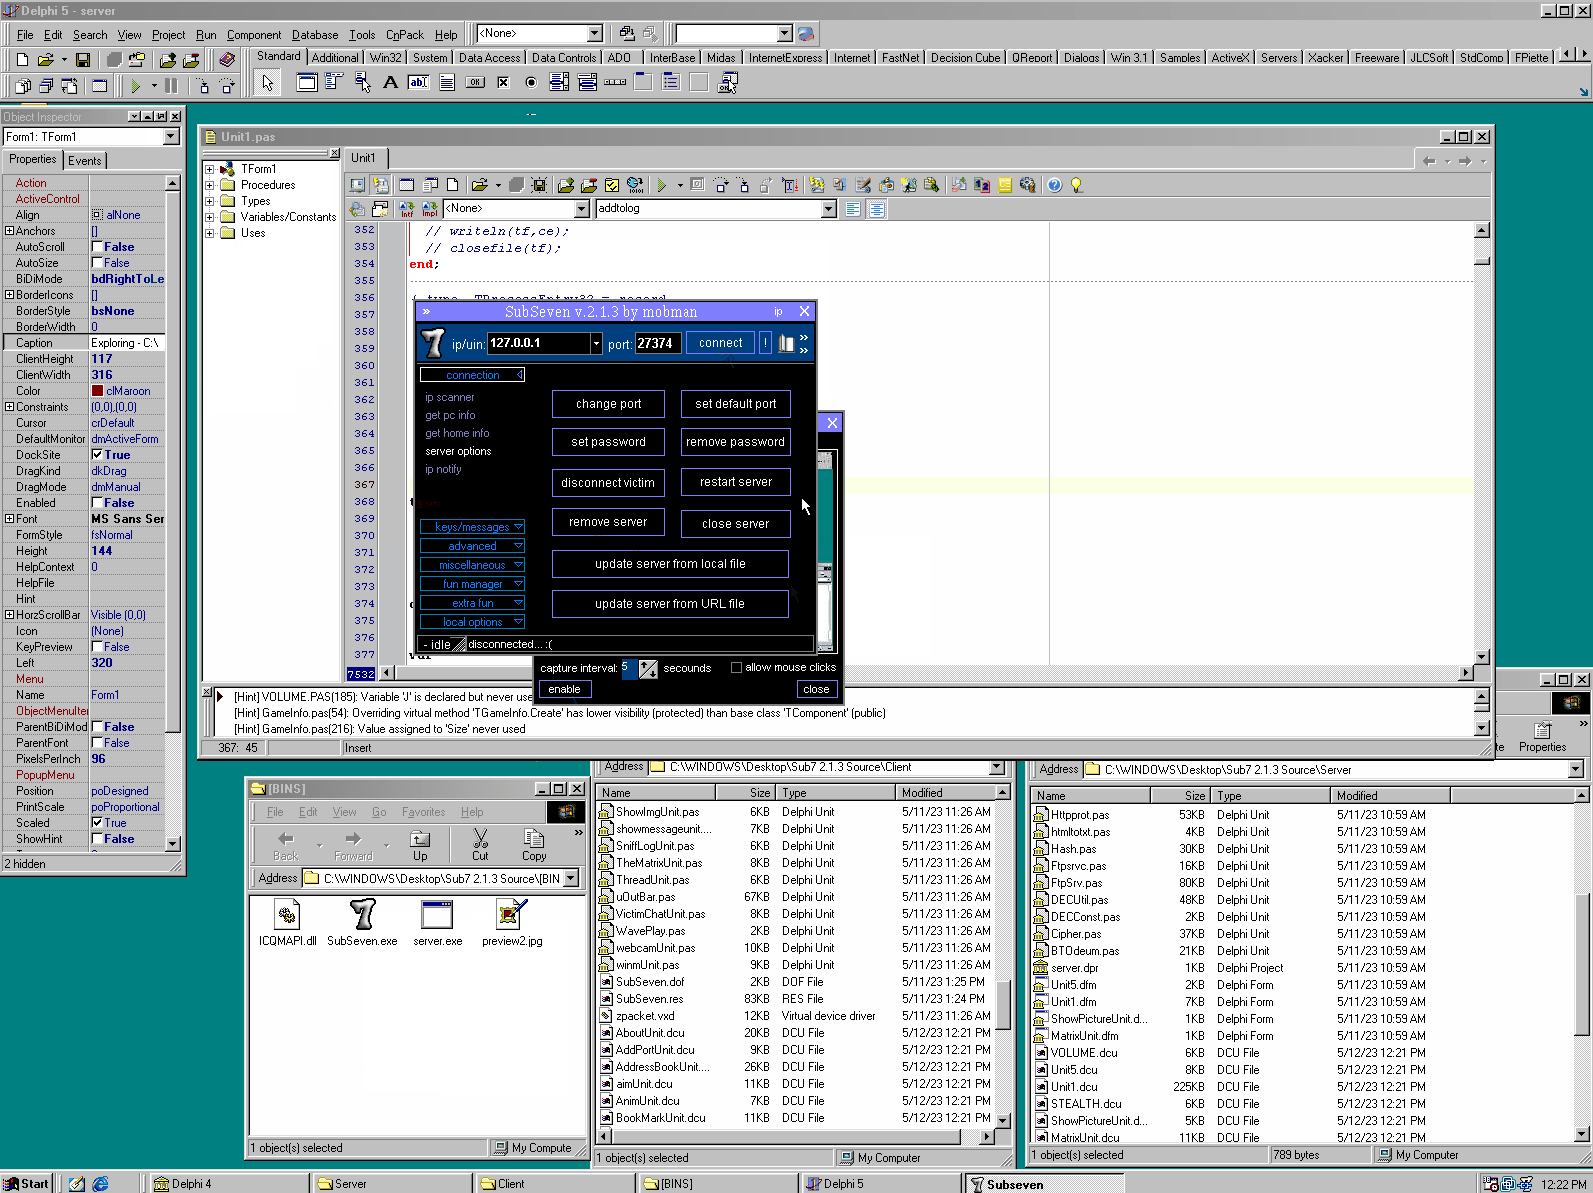
 illwill/sub7
Source code for SubSeven 2.1.3
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 ianxtianxt/teamview
Generates TeamViewer ID and password payloads for remote access to target machines. Combines executable generation with third-party remote control…
 ysrc/pil-rce-by-ghostbutt
Exploiting Python PIL Module Command Execution Vulnerability
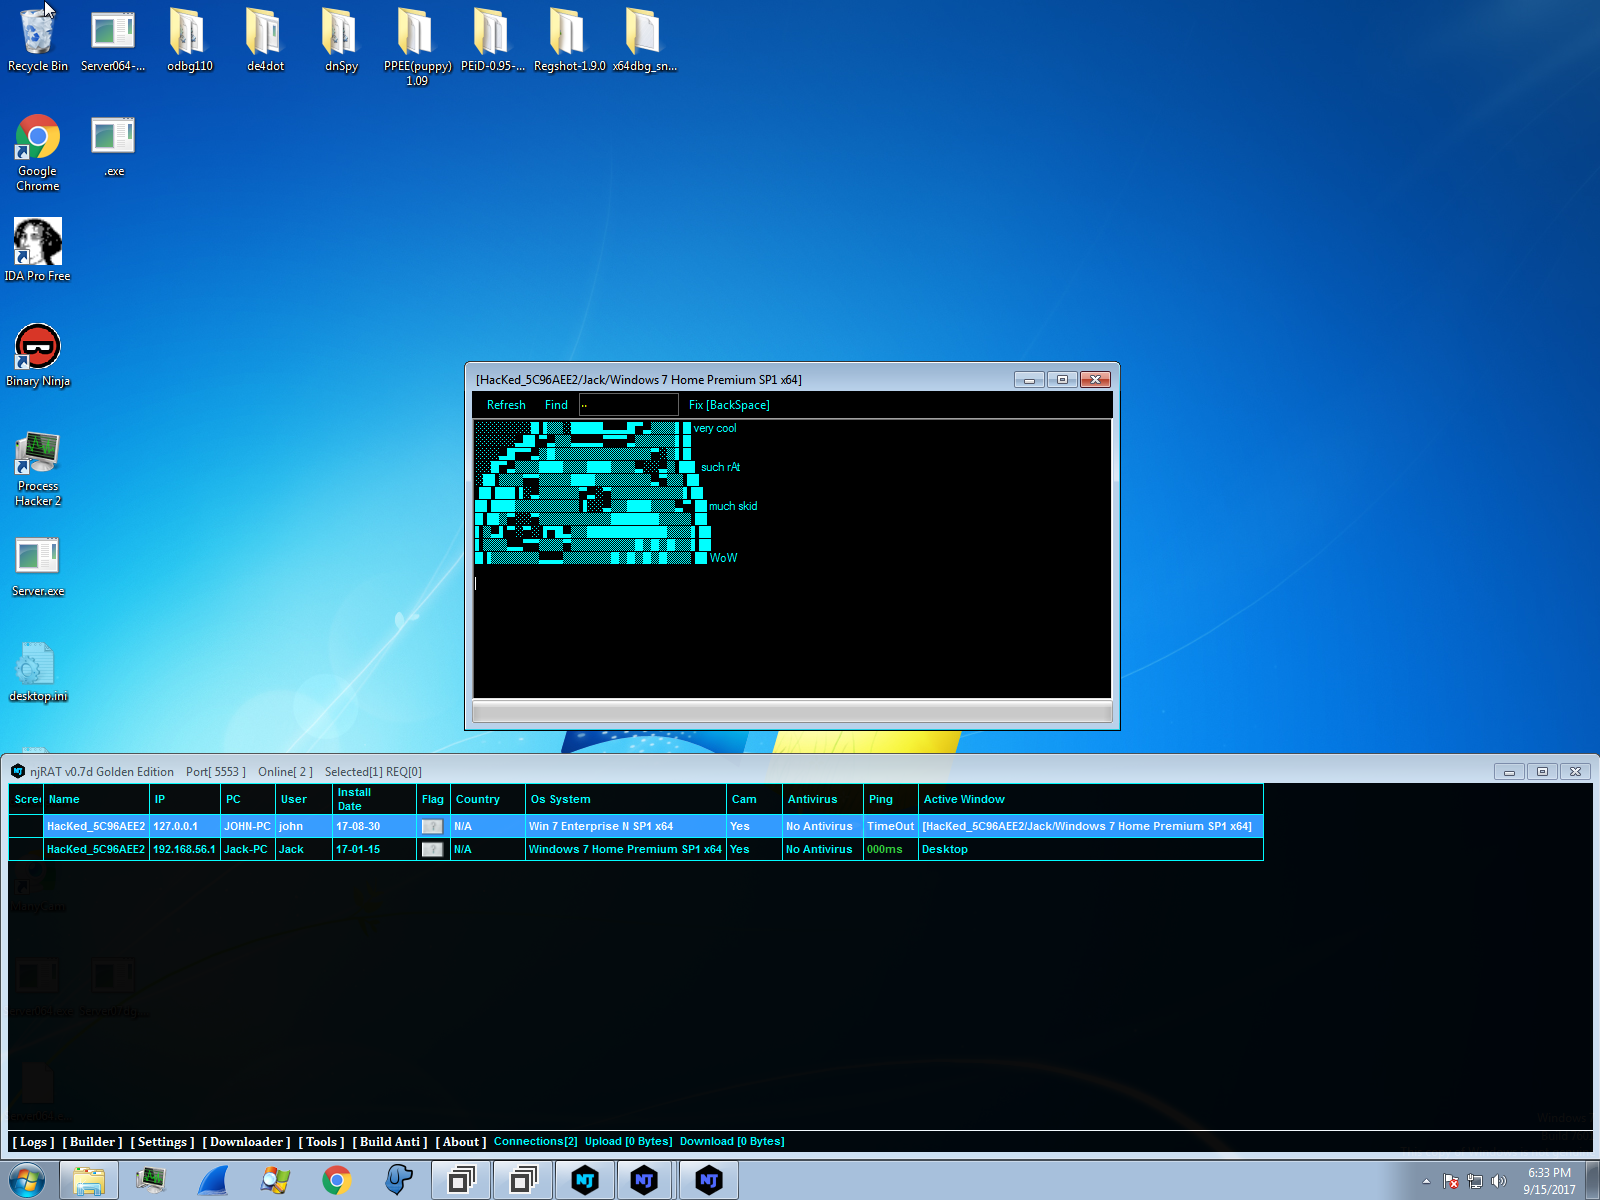 seep1959/njutils
A client and chat program for njrat 0.6.4, 0.7d, and 0.7d golden edition.
 simoesctt/ctt-enhanced-cve-2026-46339-exploit-engine
Python framework exploiting CVE-2026-46339 for unauthenticated RCE on 9Router via MCP bridge, using temporal sharding and dispersion to evade…
 theexploiters/cve-2024-27115-exploit
Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)
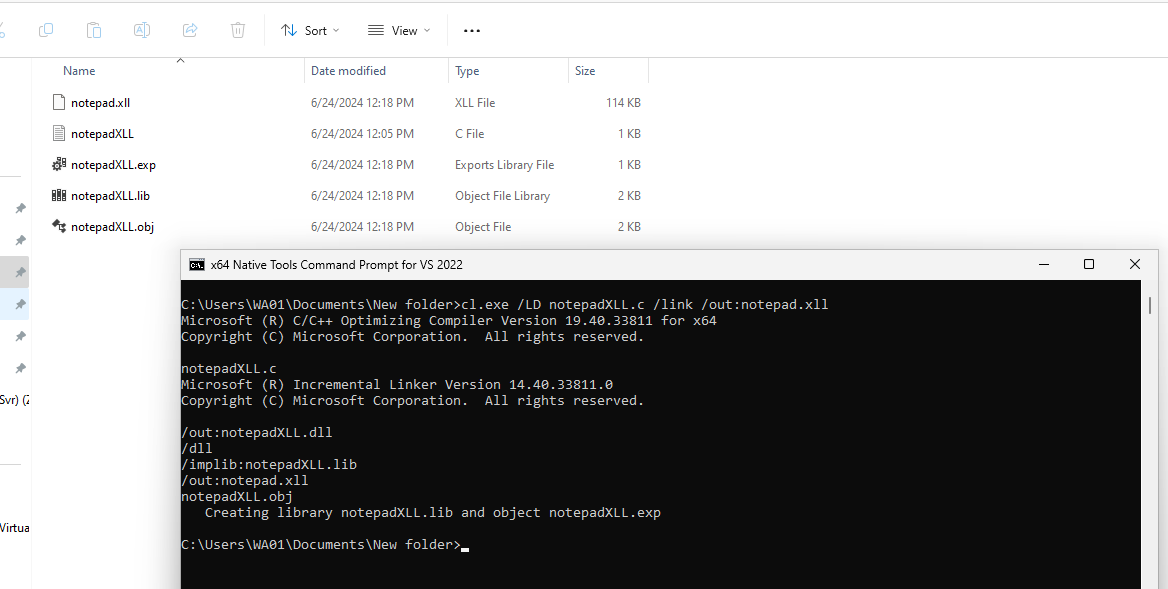 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…