

veneficus
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
command-and-controldata-exfiltrationids-ips-evasion+8
2
abraxas/veneficusSuper elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 mythicagents/xenon
A Mythic agent for Windows written in C
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 rafabd1/cve-2026-75604-poc
Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…
 daddybigfish/cve-2025-59287-hawktrace
PoC for Remote Code Execution Vulnerability in Windows Server Update Service by Microsoft CVE-2025-59287 9.8 CRITICAL
 darkcodersc/subseven
SubSeven Legacy Official Source Code Repository
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 idov31/venom
Venom is a library that meant to perform evasive communication using stolen browser socket
 rvrsh3ll/rendezvousrat
Self-healing RAT utilizing libp2p
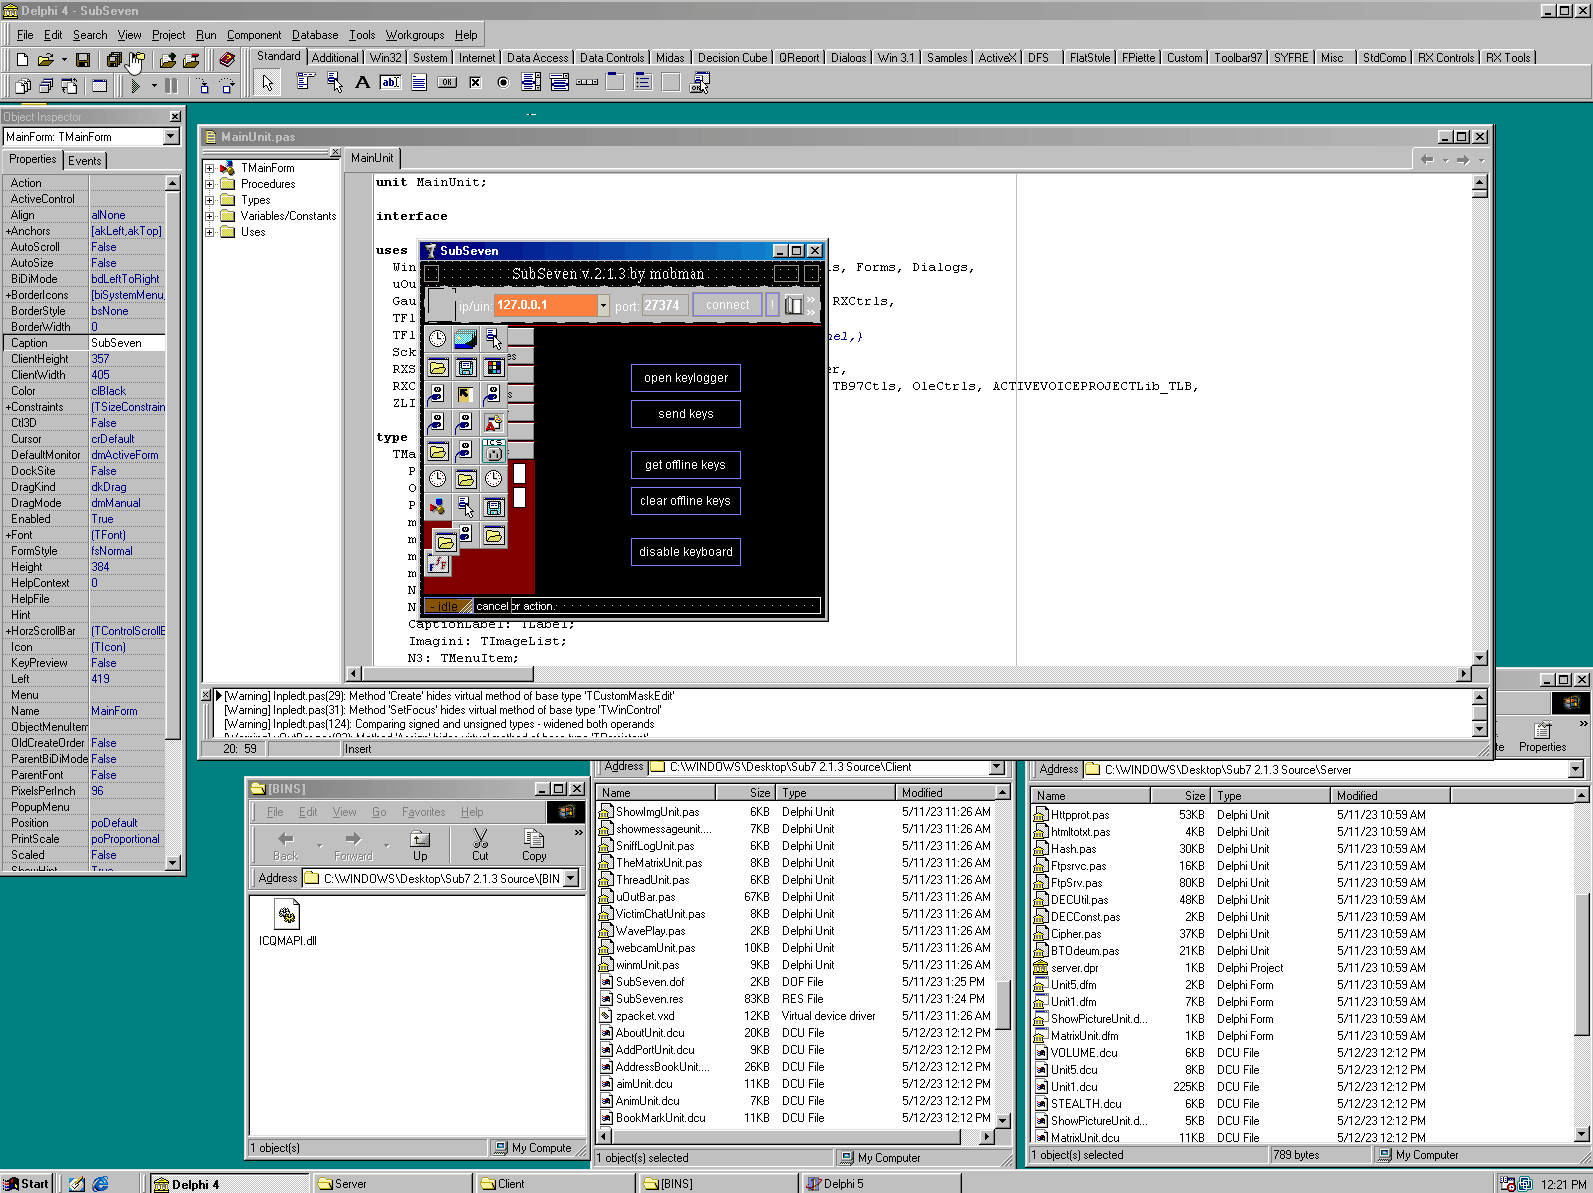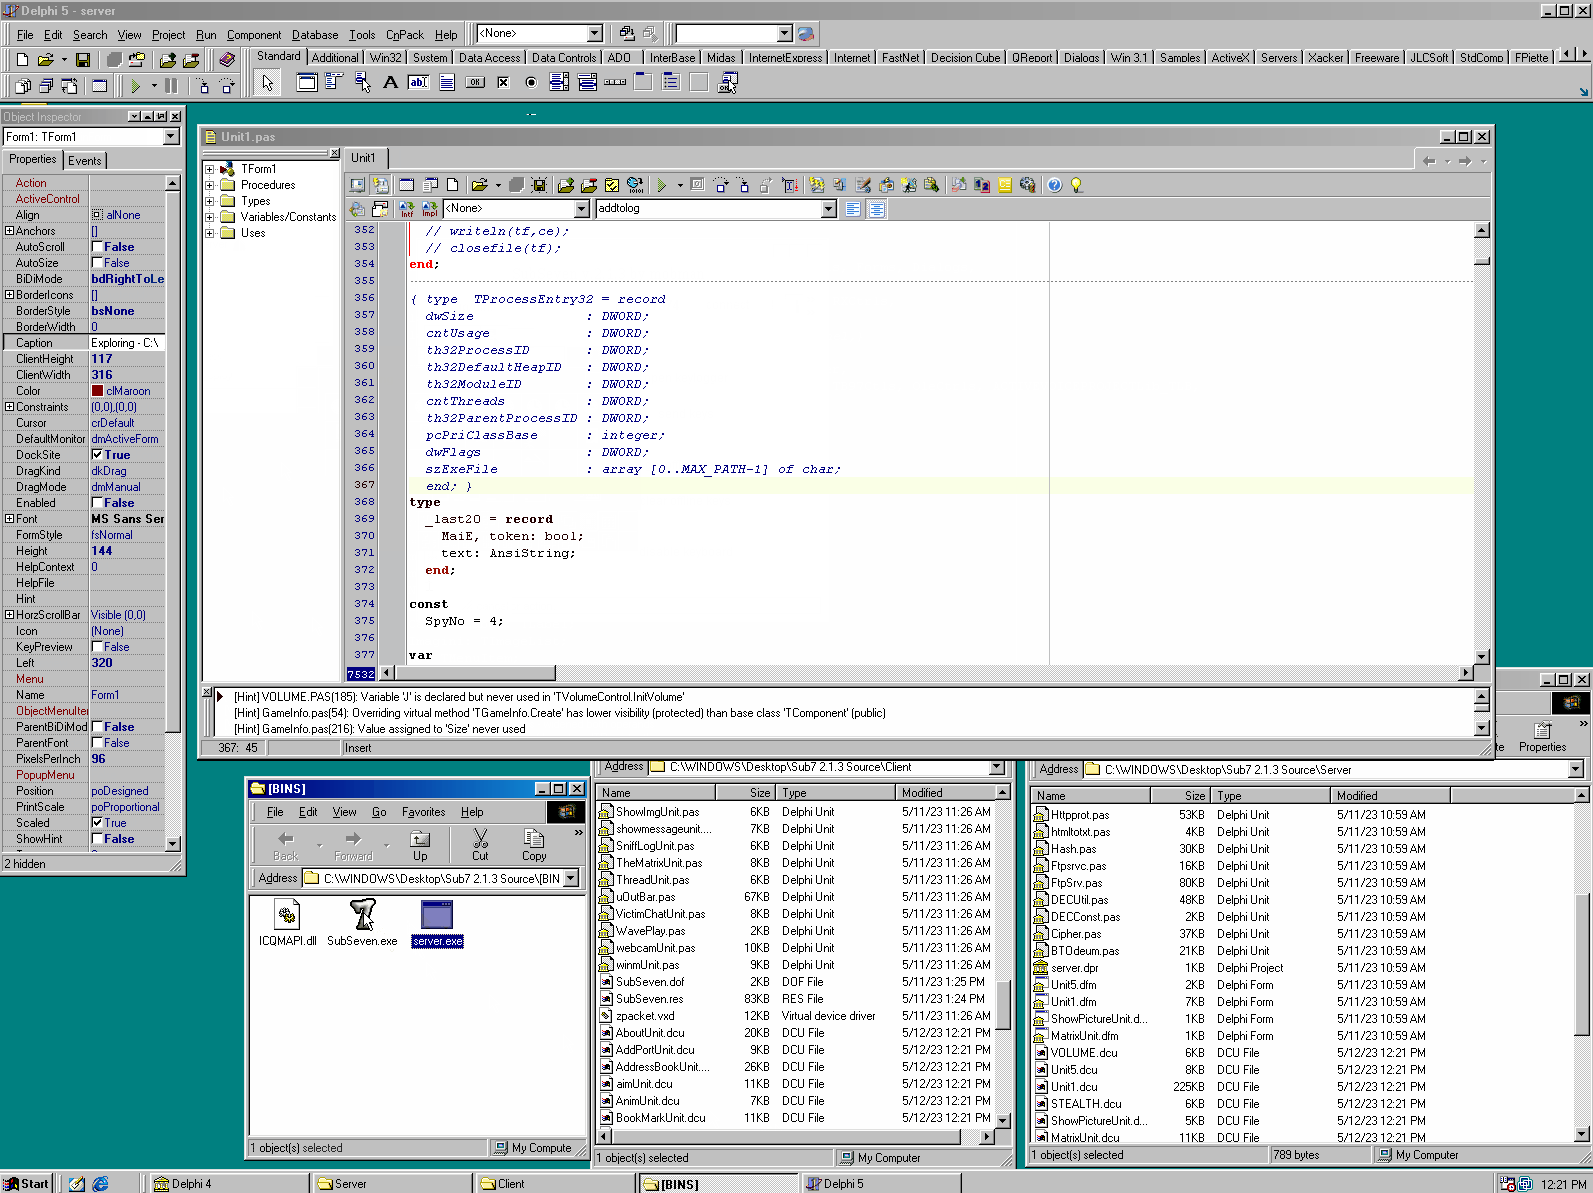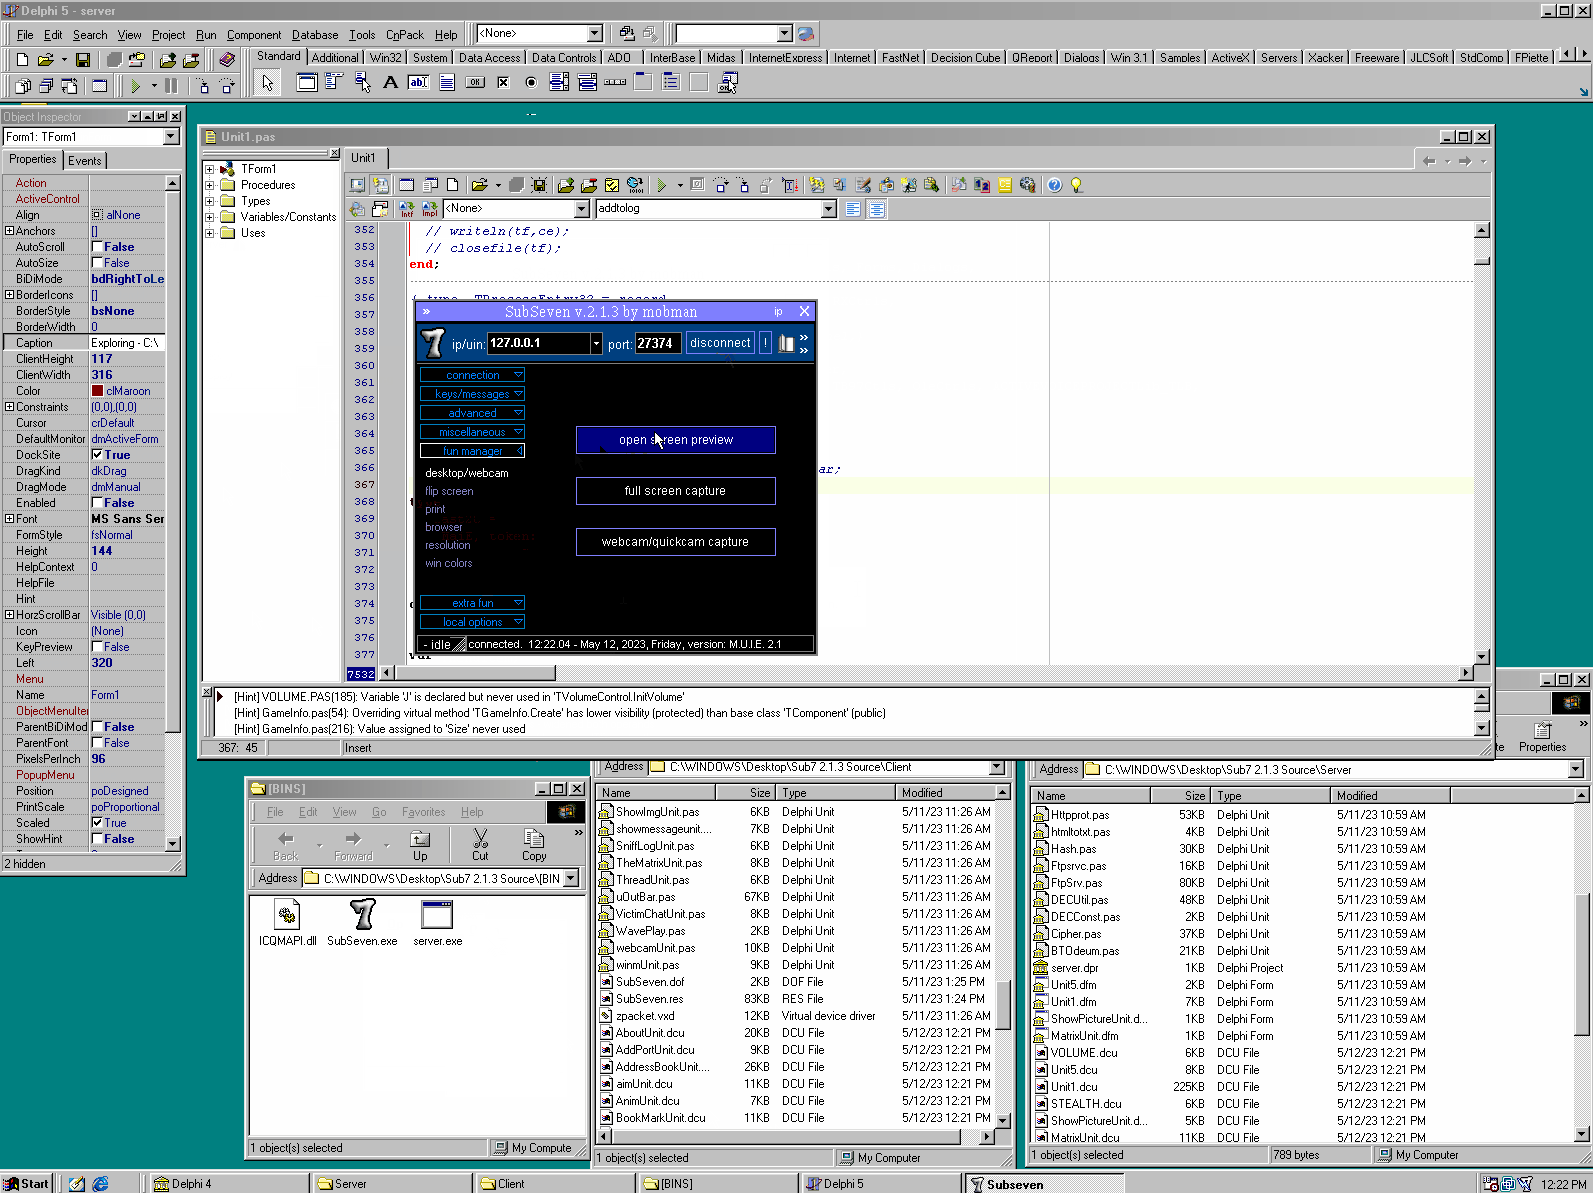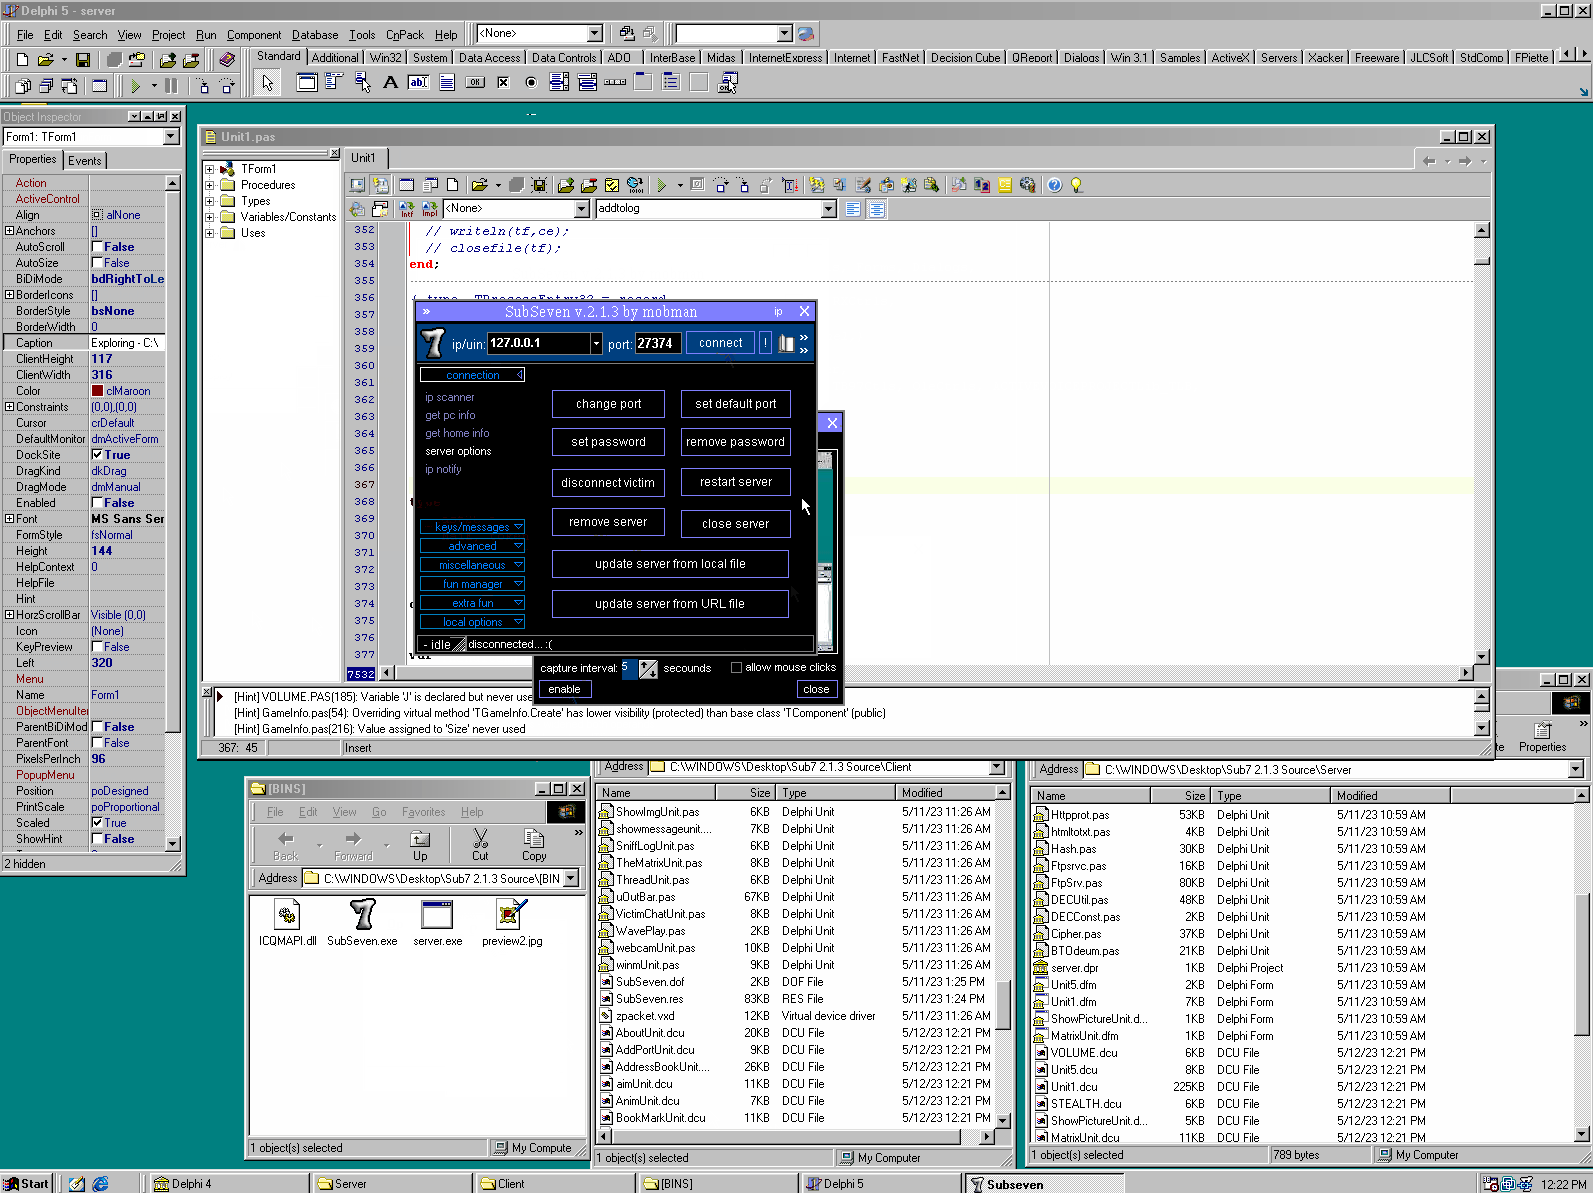
 illwill/sub7
Source code for SubSeven 2.1.3
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
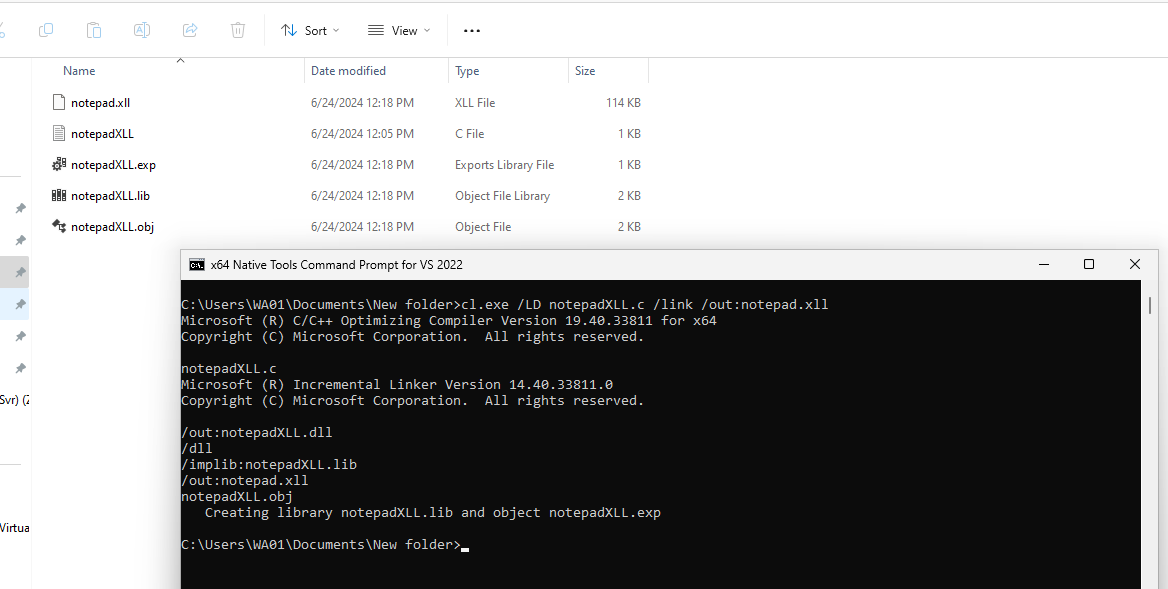 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 gbrn1/pirate
Python Remote Access Tool
 hood3drob1n/jsrat-py
This is my implementation of JSRat.ps1 in Python so you can now run the attack server from any OS instead of being limited to a Windows OS with…