

veneficus
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
command-and-controldata-exfiltrationids-ips-evasion+8
2
abraxas/veneficusSuper elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 lukebob-zz/c2-pwn
Uses Shodan API to pull down C2 servers to run known exploits on them.
 rwhitcroft/dnschan
A remote access trojan over DNS
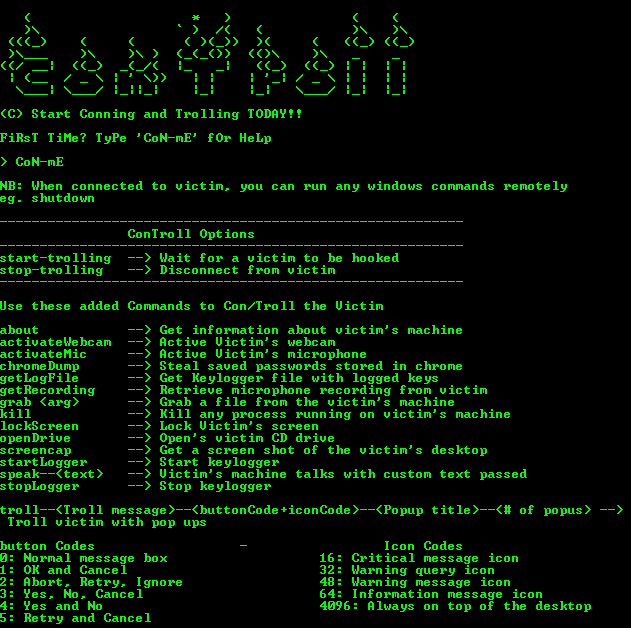 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
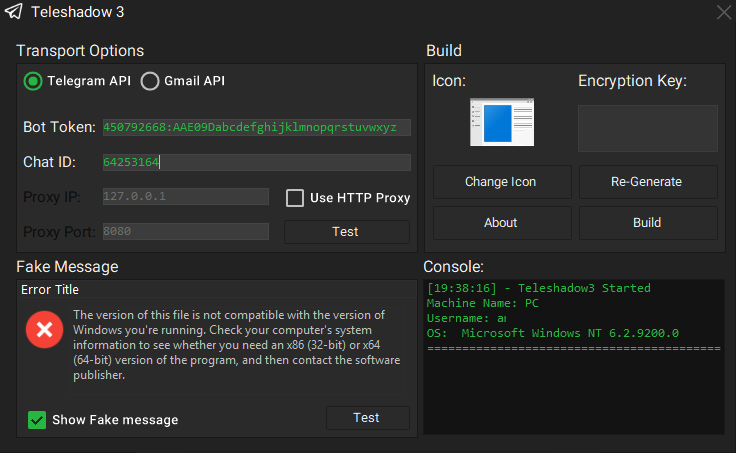 eternalc0der/teleshadow3
Telegram Desktop Session Stealer
 sshuttle/sshuttle
Transparent proxy server that works as a poor man's VPN. Forwards over ssh. Doesn't require admin. Works with Linux and MacOS. Supports DNS…
 cryst4linqq/turkorat
Fully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)
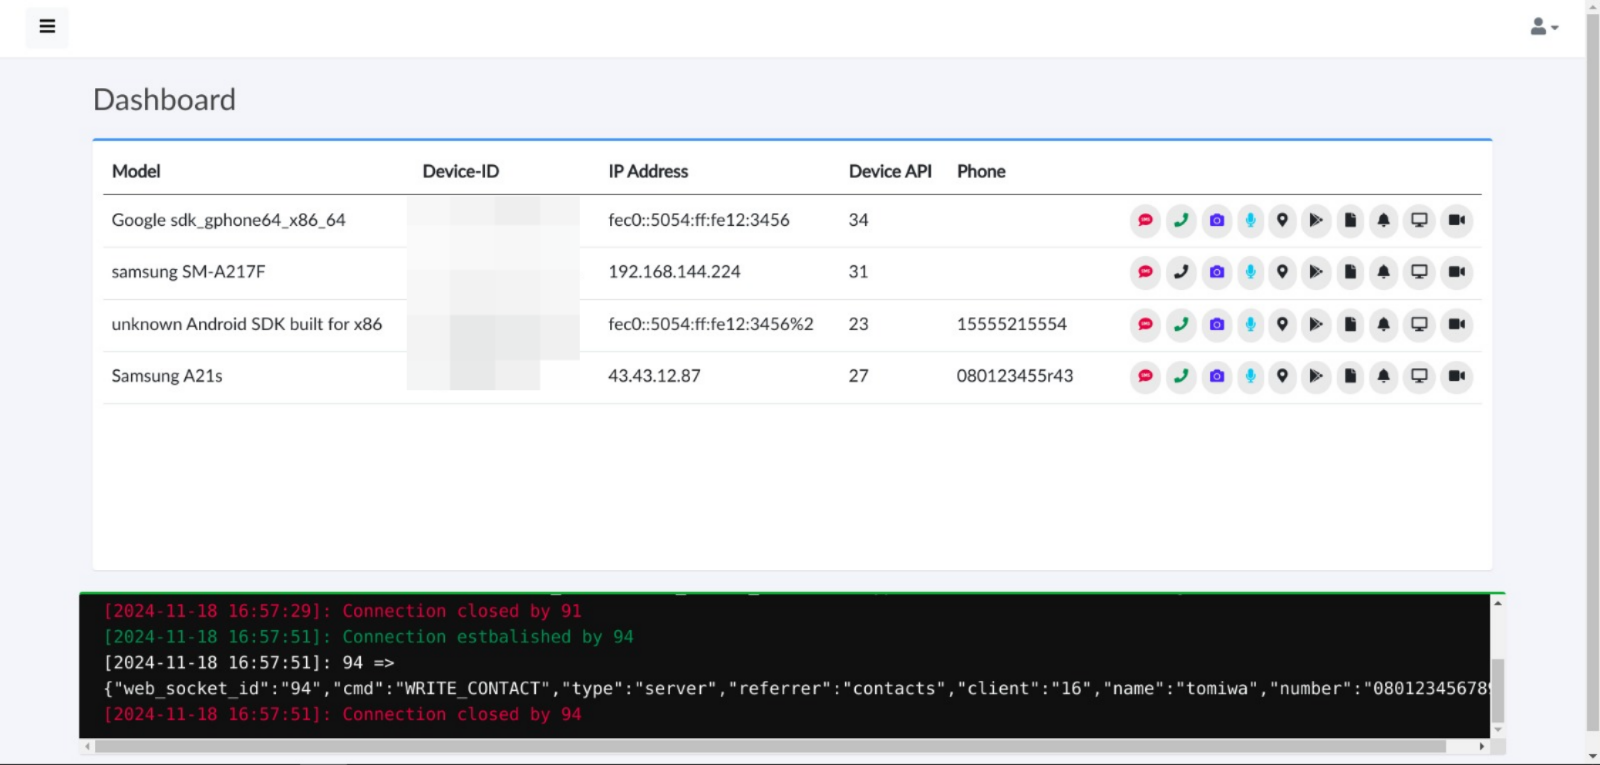 tomiwa-ot/moukthar
Android remote administration tool
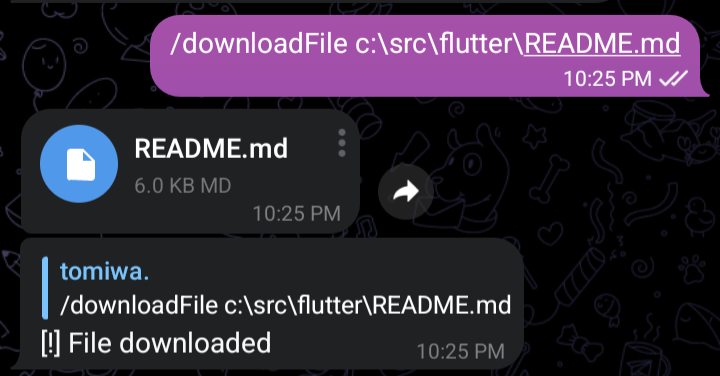 tomiwa-ot/telegram-c2
Control a system remotely via telegram
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…