
CVE-2026-78006-POC
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
defensive-toolsexploitationpayload-development+7
4
deadexpl0it/cve-2026-78006-pocPOC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 ysrc/pil-rce-by-ghostbutt
Exploiting Python PIL Module Command Execution Vulnerability
 simoesctt/ctt-enhanced-cve-2026-46339-exploit-engine
Python framework exploiting CVE-2026-46339 for unauthenticated RCE on 9Router via MCP bridge, using temporal sharding and dispersion to evade…
 theexploiters/cve-2024-27115-exploit
Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
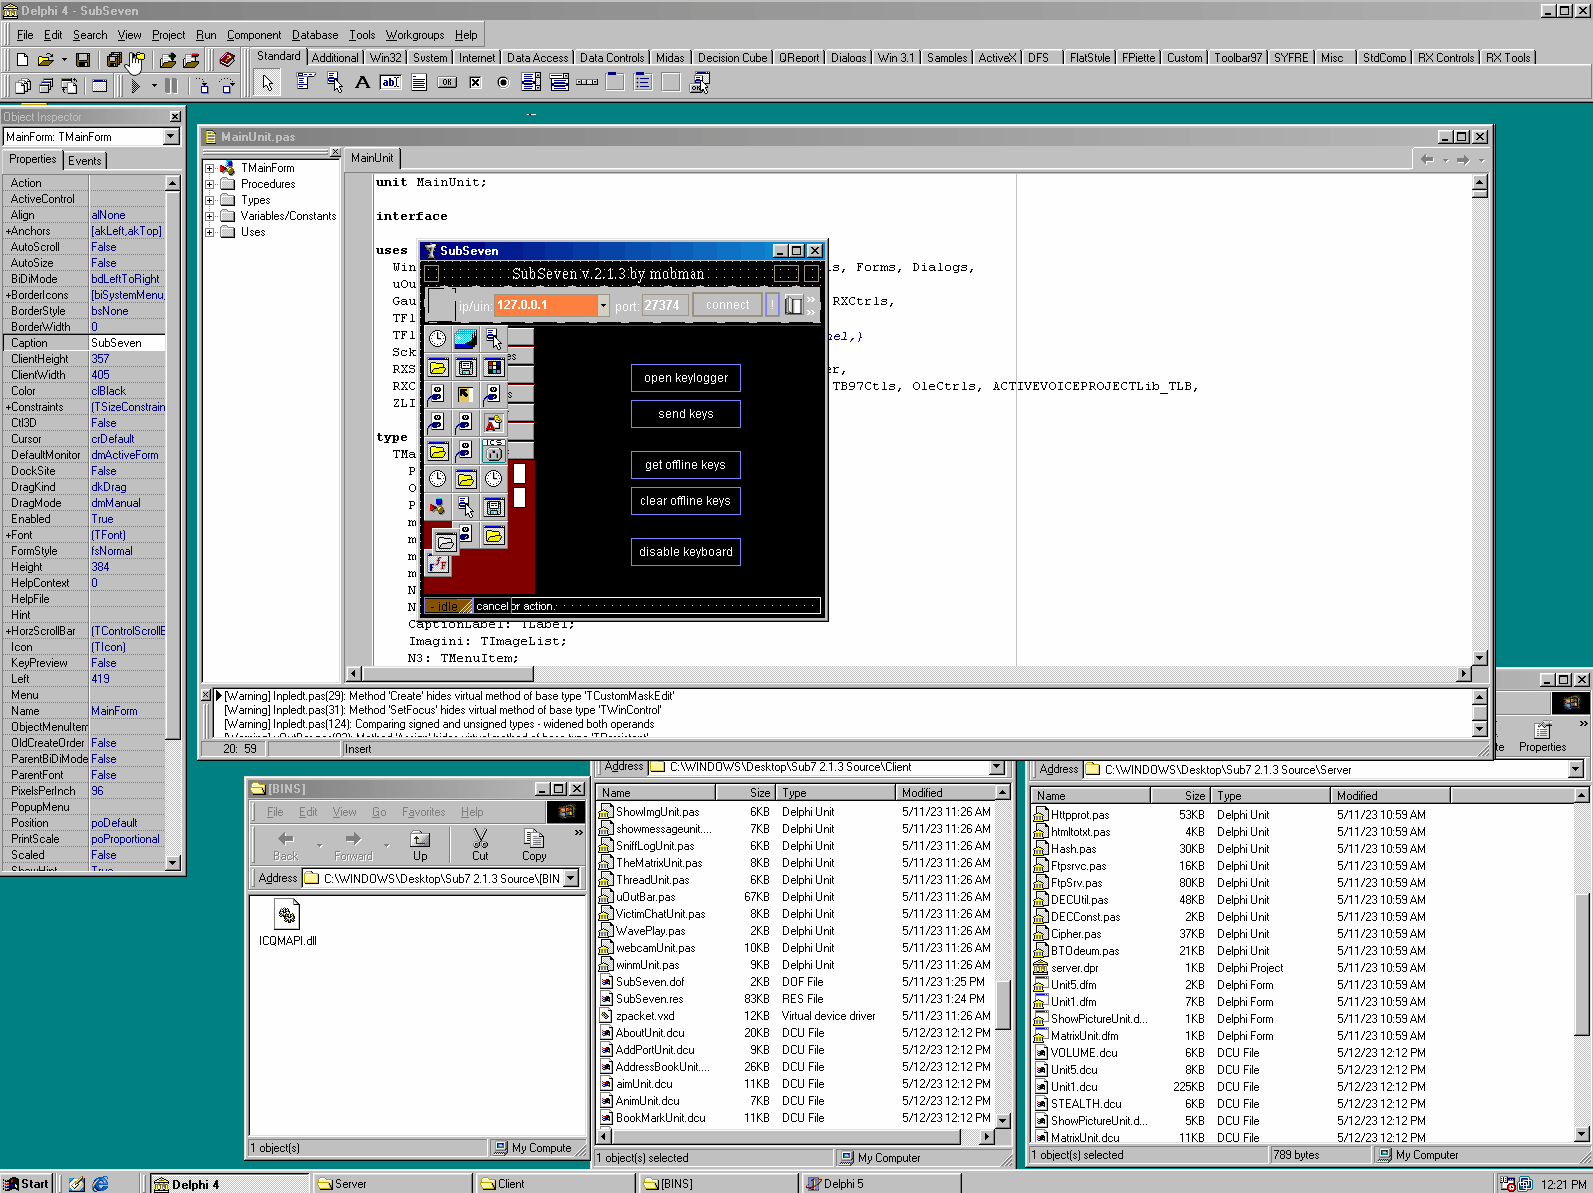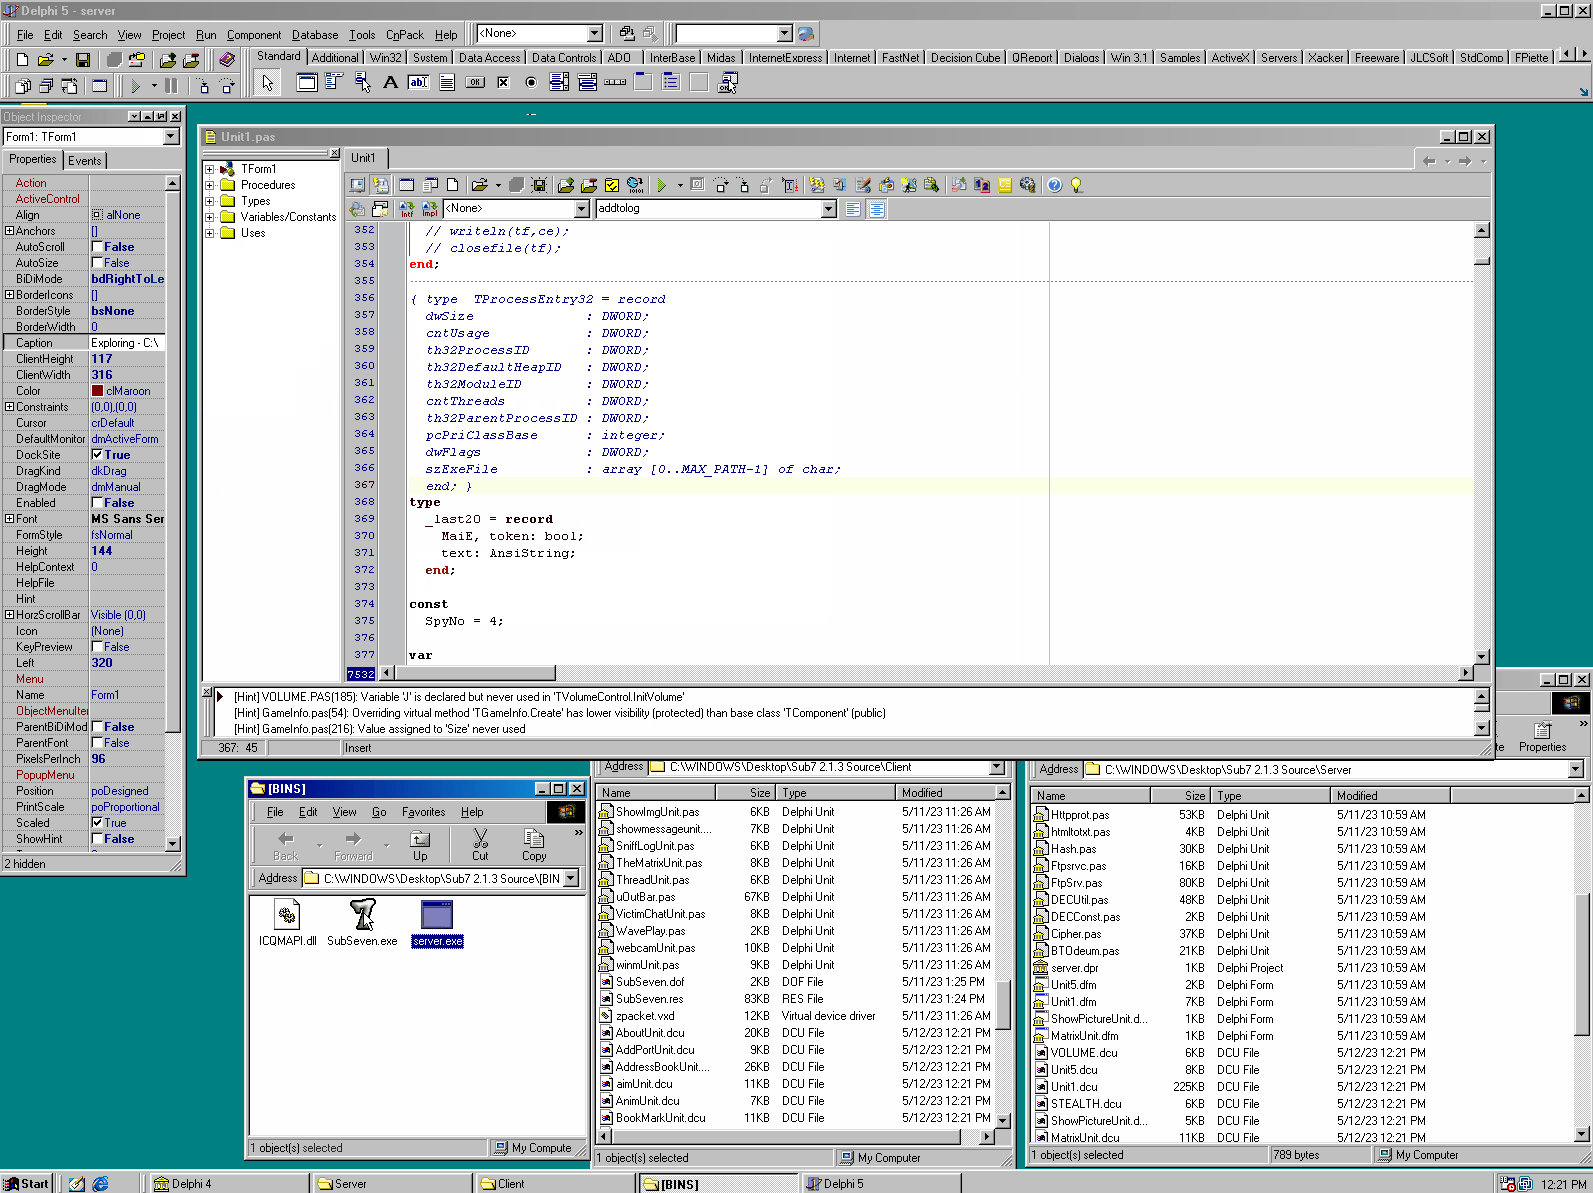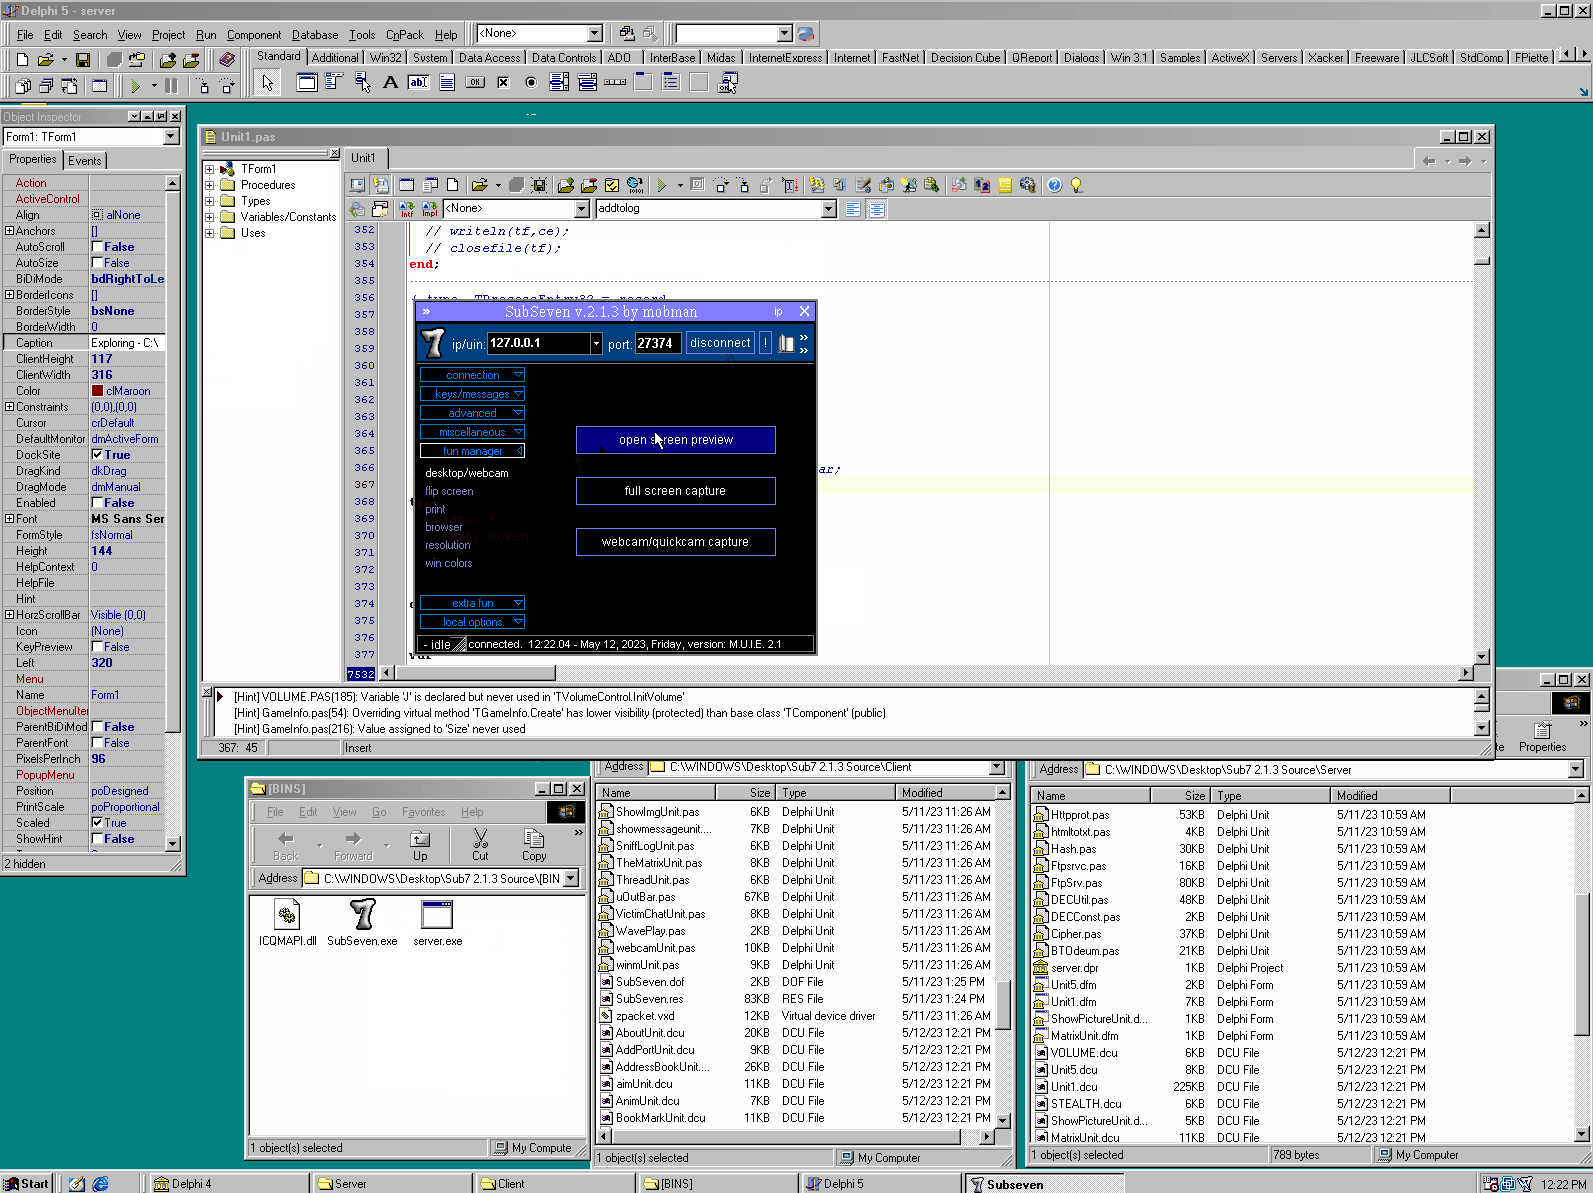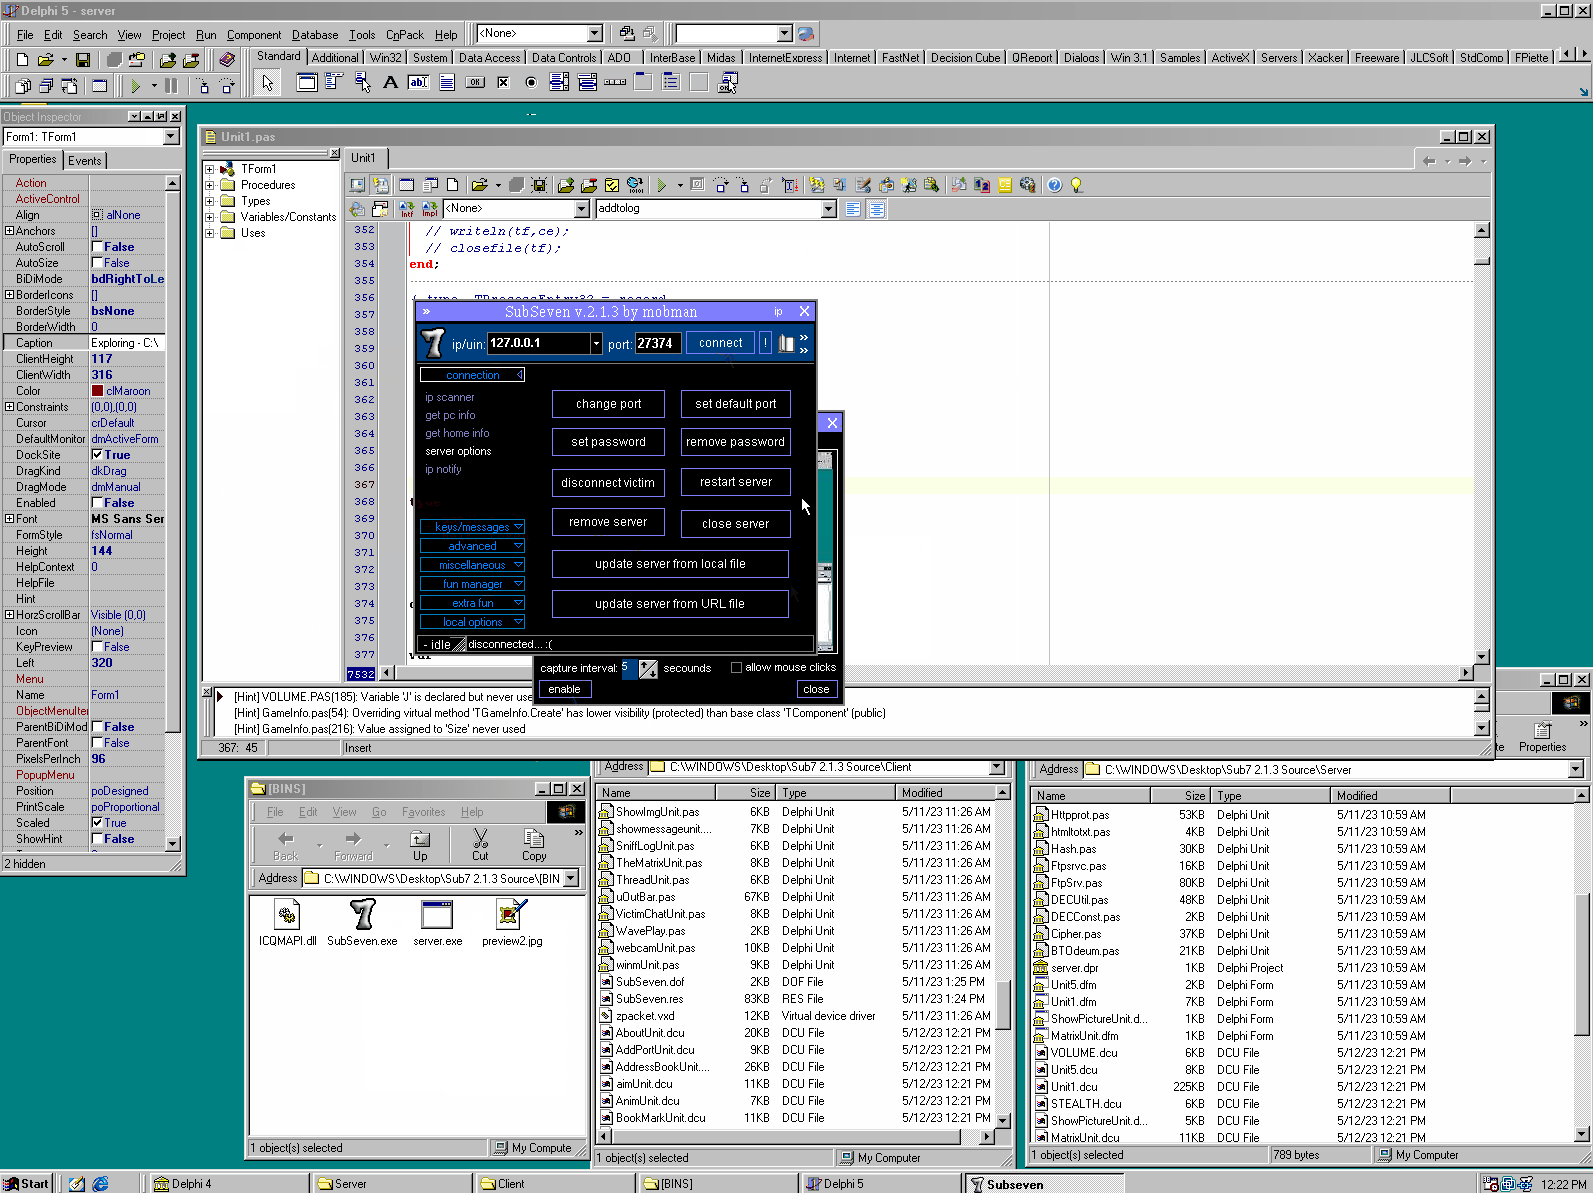
 illwill/sub7
Source code for SubSeven 2.1.3
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 tennc/webshell
This is a webshell open source project
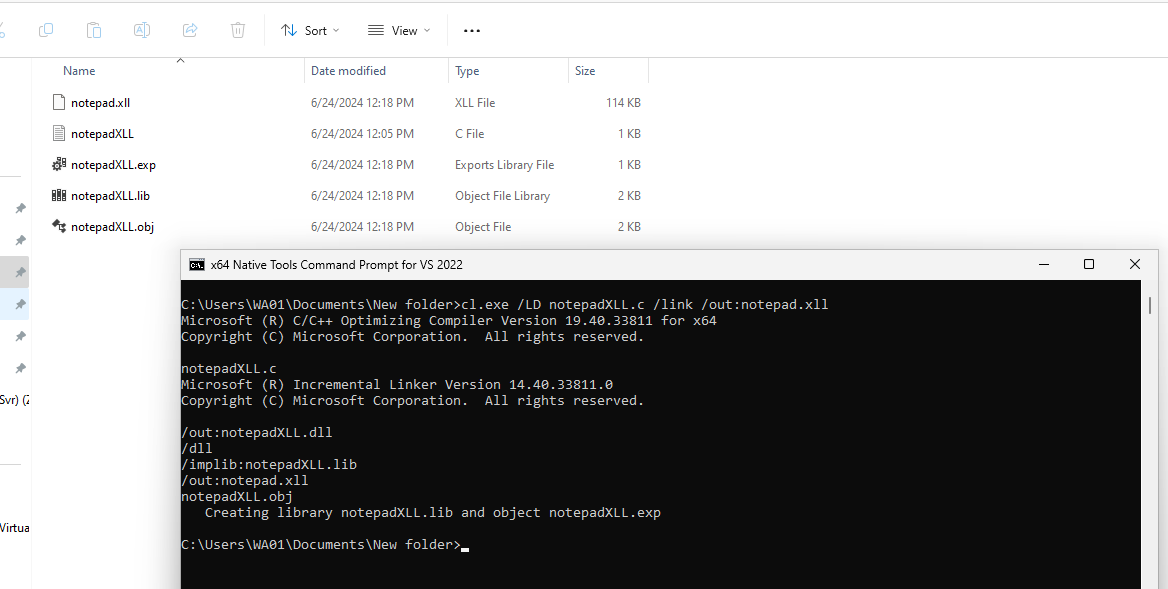 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell
 ianxtianxt/teamview
Generates TeamViewer ID and password payloads for remote access to target machines. Combines executable generation with third-party remote control…

 jofpin/backcookie
Small backdoor using cookie.
 ahhh/ntp_trojan
Reverse NTP remote access trojan in python, for penetration testers
 ahhh/reverse_https_bot
A python based https remote access trojan for penetration testing
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 gbrn1/pirate
Python Remote Access Tool