
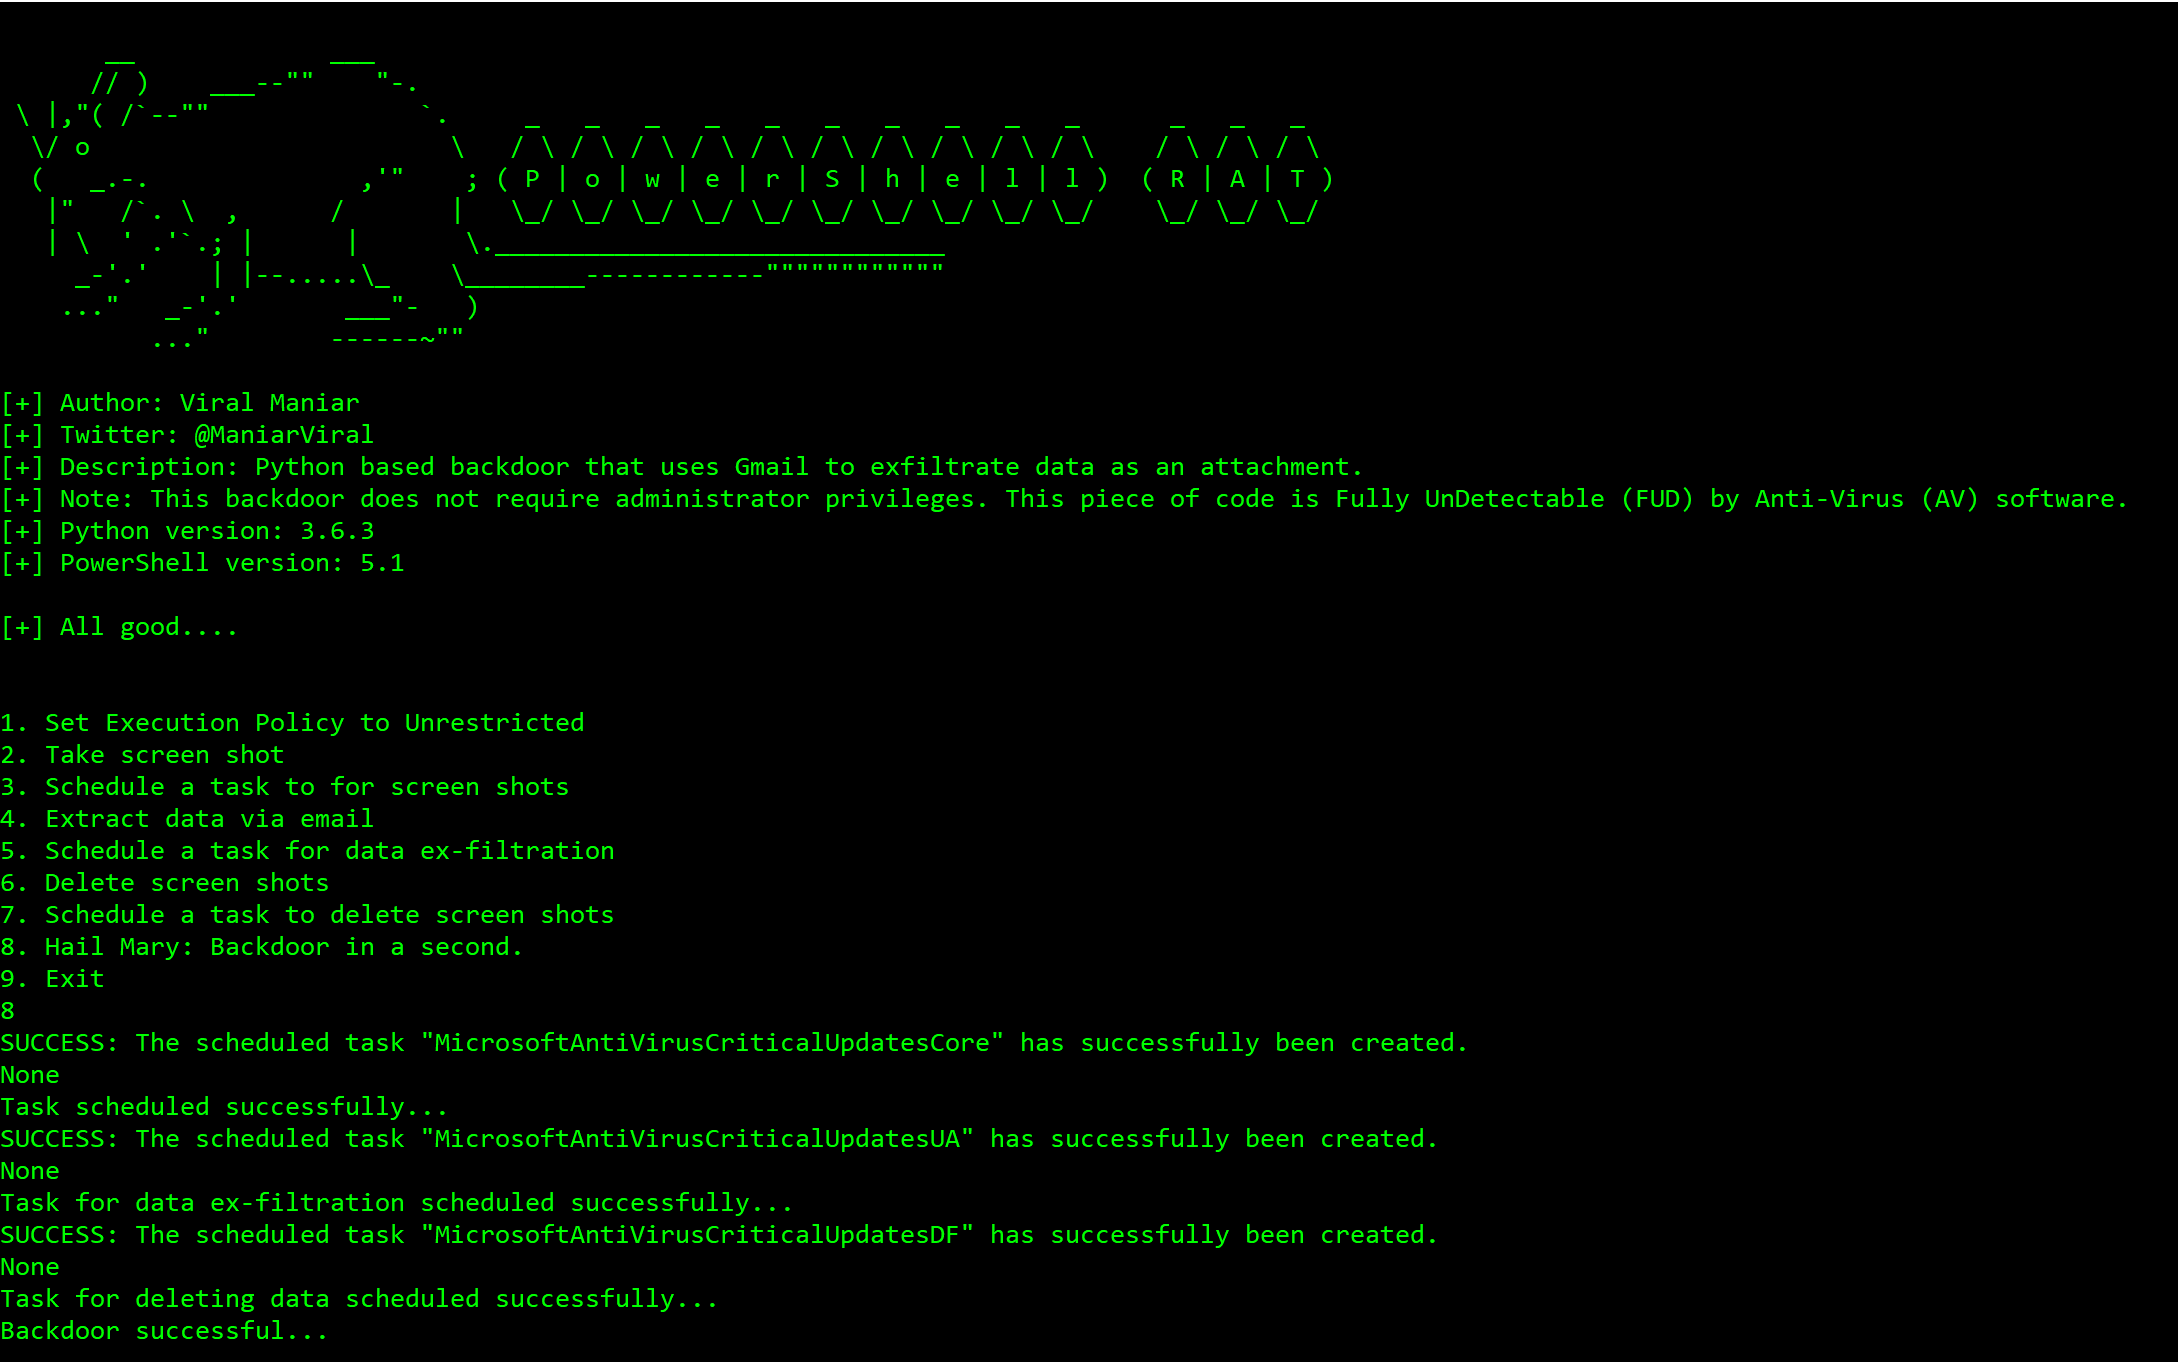
Powershell-RAT
 viralmaniar/powershell-rat
Python based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
data-exfiltrationeducationpayload-generation+4
1.2k
viralmaniar/powershell-ratPython based backdoor that uses Gmail to exfiltrate data through attachment. This RAT will help during red team engagements to backdoor any Windows…
 parsingteam/teleshadow2
TeleShadow - Telegram Desktop Session Stealer (Windows)
 byt3bl33d3r/gcat
A PoC backdoor that uses Gmail as a C&C server
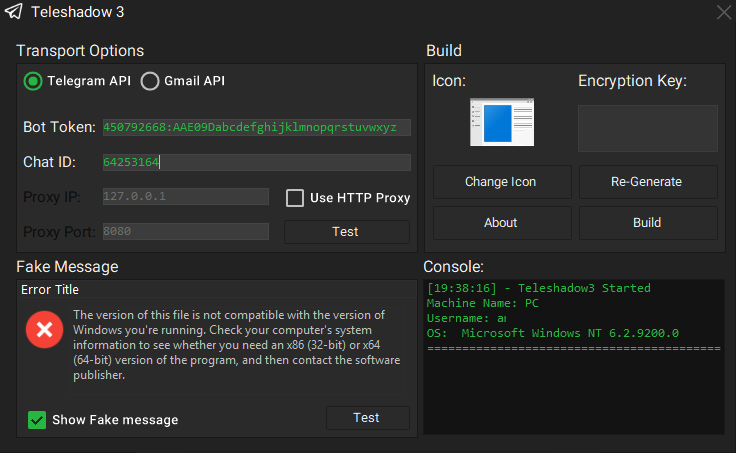 eternalc0der/teleshadow3
Telegram Desktop Session Stealer
 shadowopcode/desckvb-rat
Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell