

LazyOwn
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
ai-securitycommand-and-controlexploit-frameworks+8
300
grisuno/lazyownRed team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 machine1337/telegramrat
Cross Platform Telegram based RAT that communicates via telegram to evade network restrictions
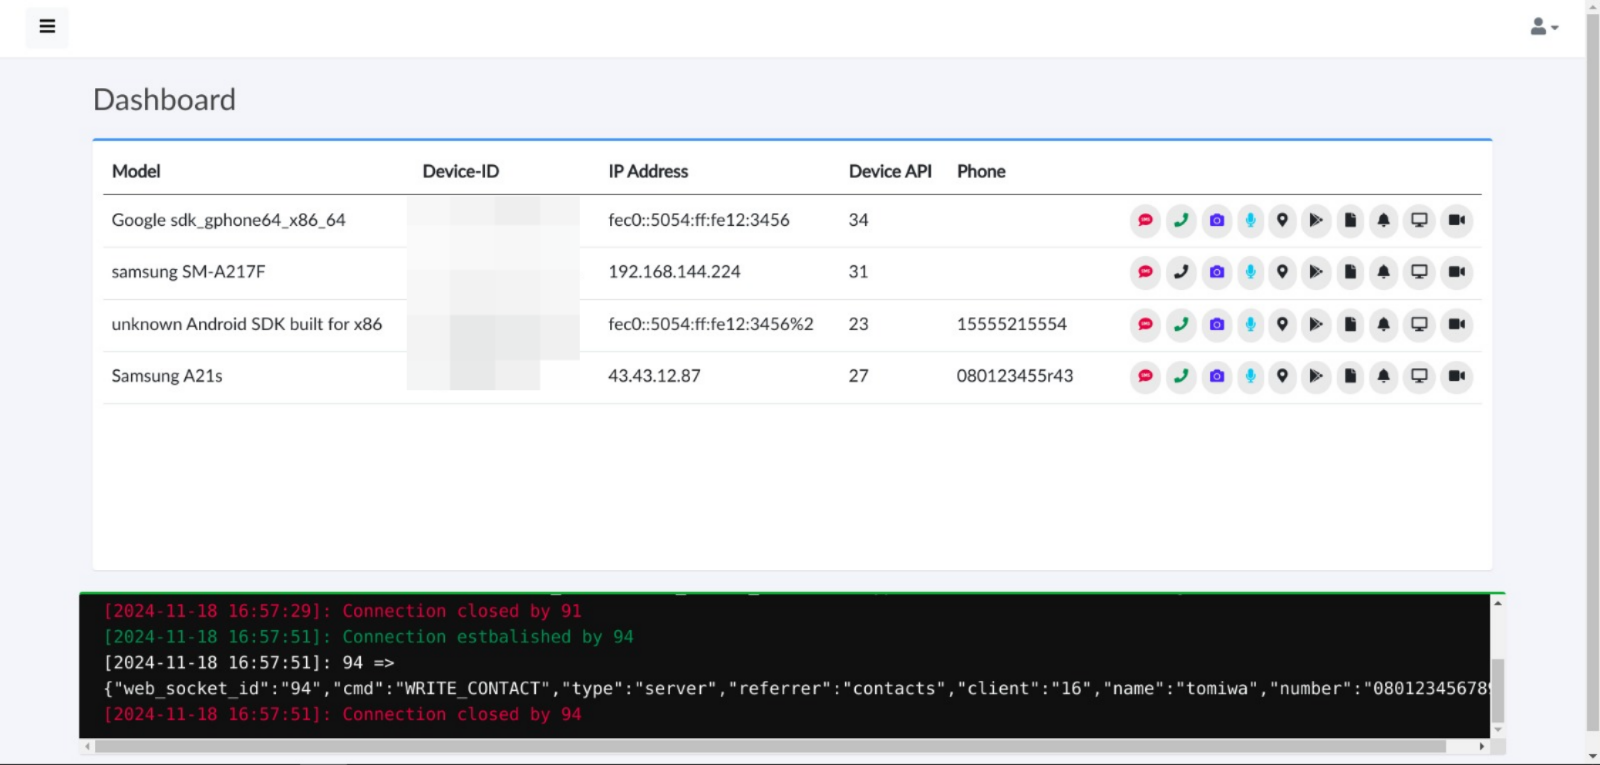 tomiwa-ot/moukthar
Android remote administration tool
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 nicocha30/ligolo-ng
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 cryst4linqq/turkorat
Fully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 sp00kyskelet0n/discordrat
Discord Remote Administration Tool fully written in Python3
 them4hd1/vayne-rat
An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
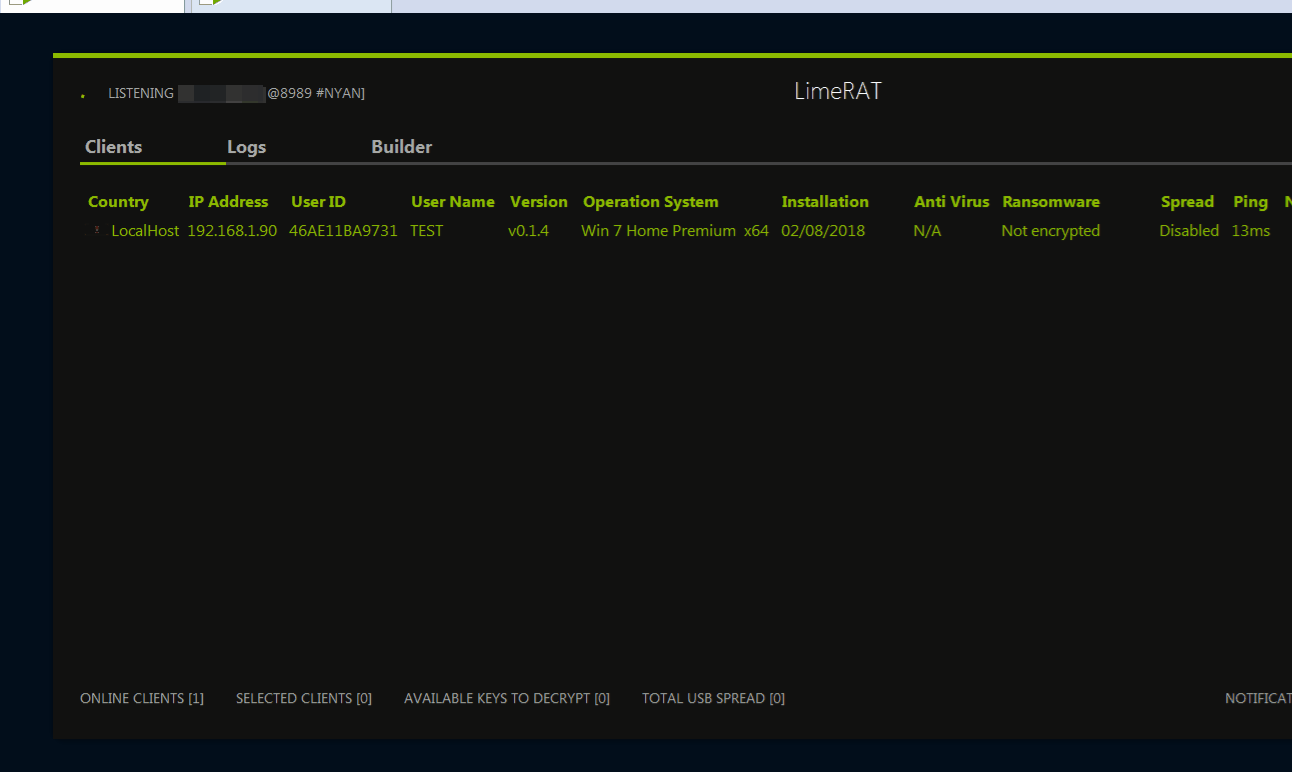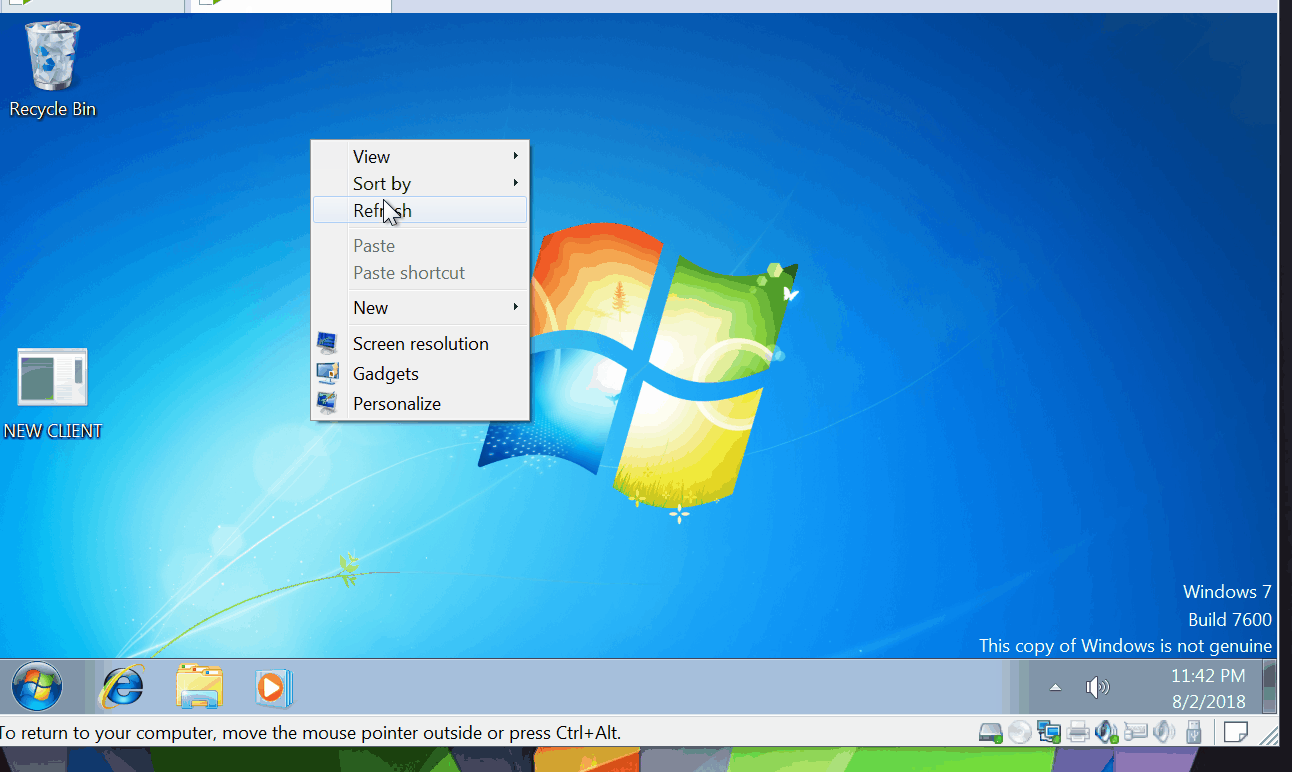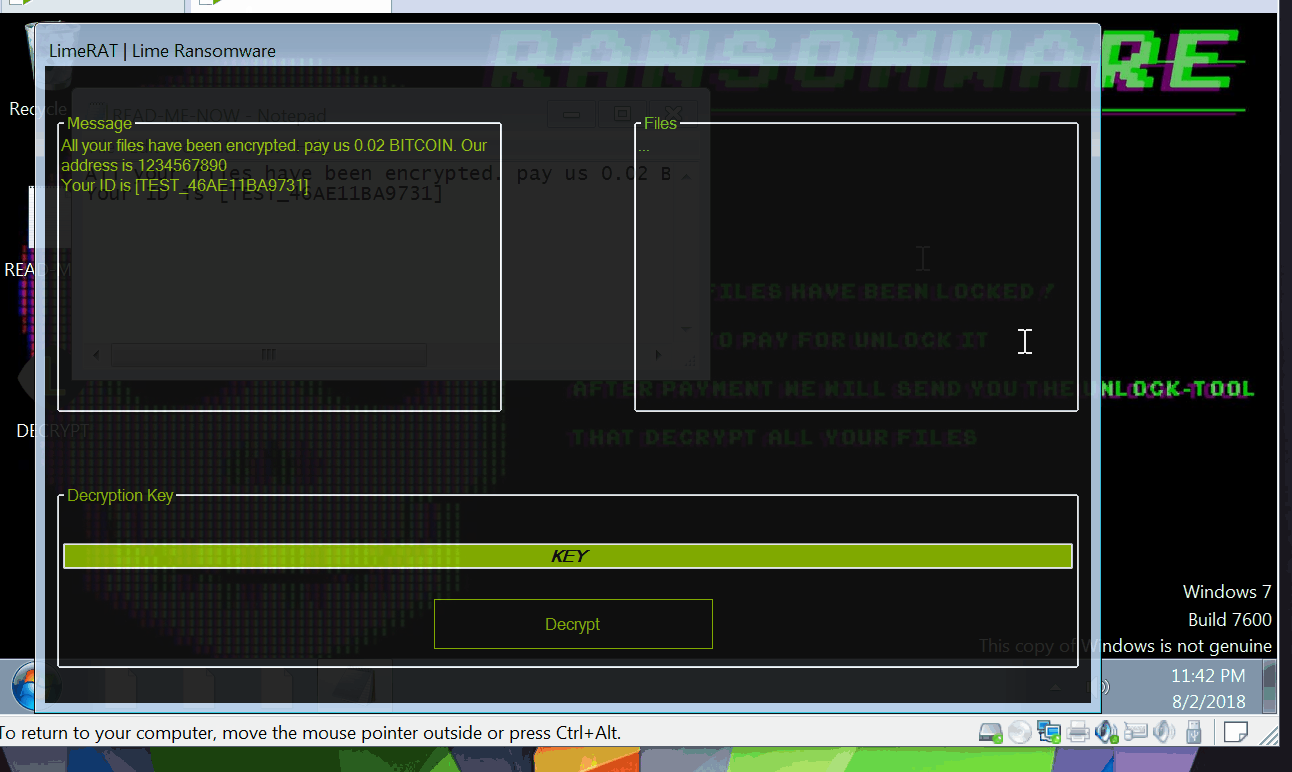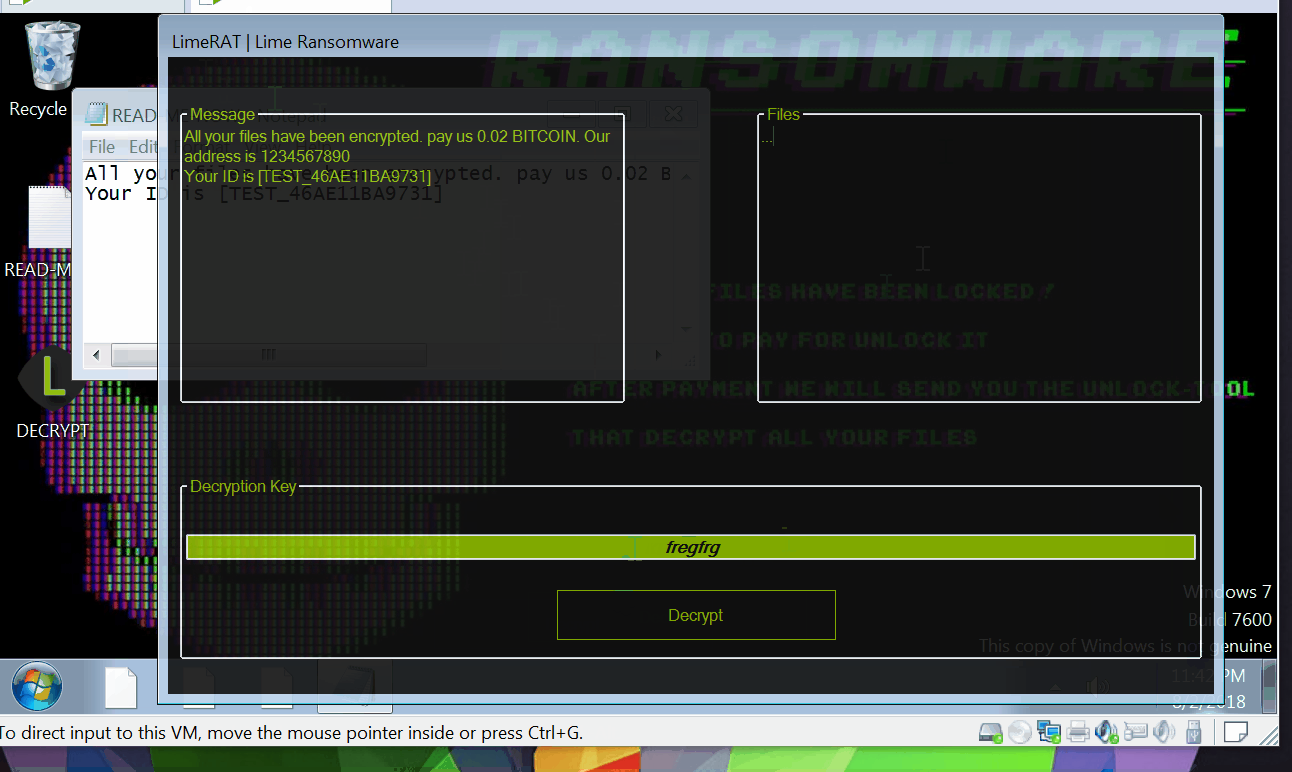 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 langz337/cve-2026-63030
Python exploit tool chaining CVE-2026-63030 REST batch-route confusion with CVE-2026-60137 SQL injection to achieve unauthenticated WordPress RCE,…
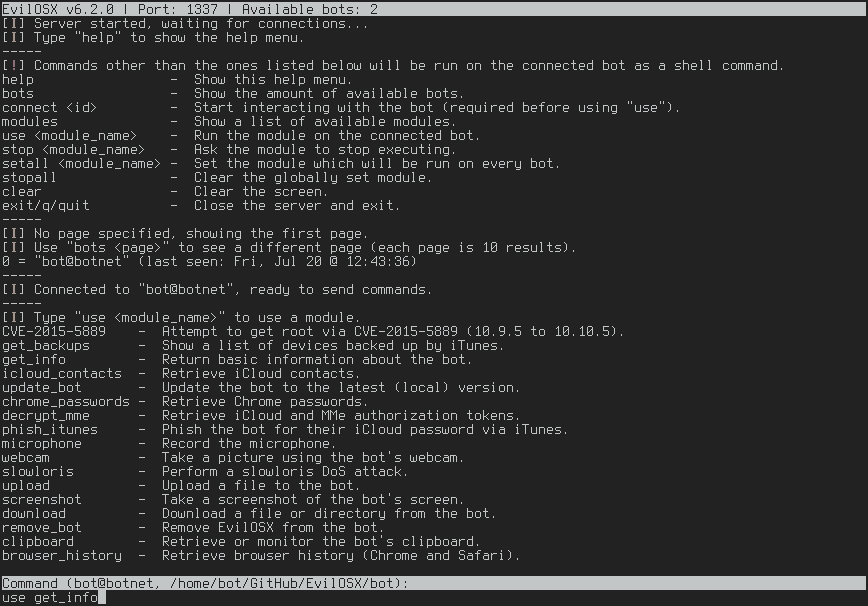 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.