

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 gsoffmarket/malvinci
This simple but powerful script will introduce a new type of malware that will turn off the firewall, start an HTTP server, forward its port through…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 qwqdanchun/dcrat
A simple remote tool in C#.
 mwsrc/betterrat
Better Remote Access Trojan
 cryst4linqq/turkorat
Fully undetected grabber (grabs wallets, passwords, cookies, modifies discord client etc.)
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
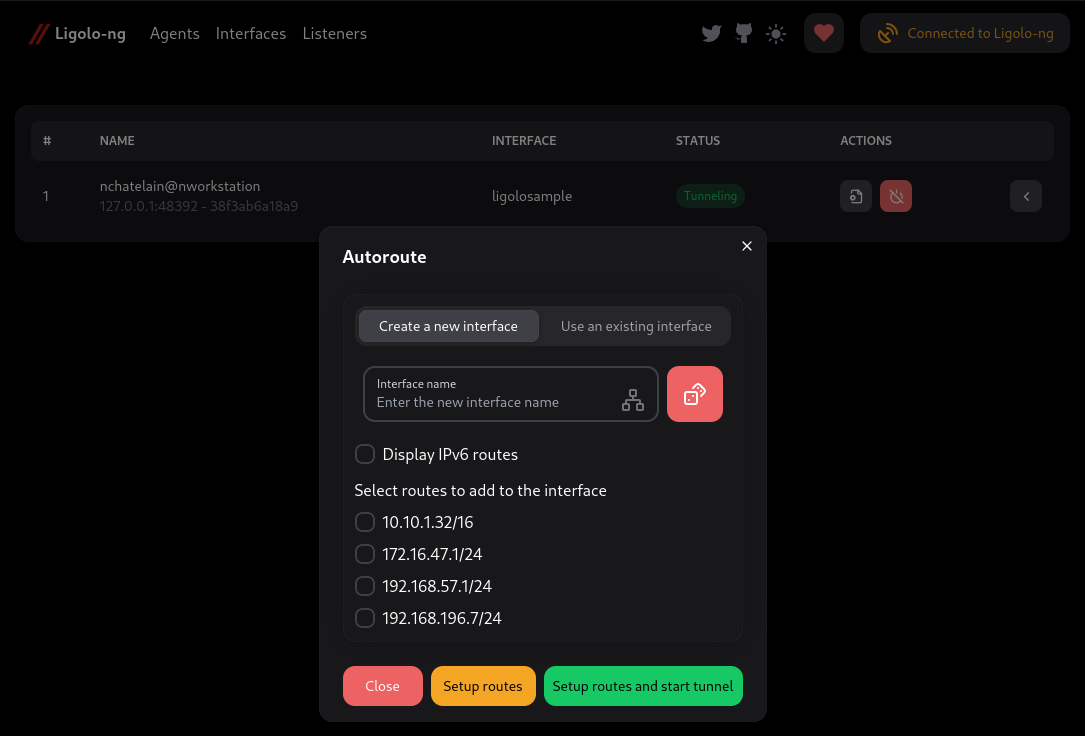 nicocha30/ligolo-ng
An advanced, yet simple, tunneling/pivoting tool that uses a TUN interface.
 cenobyte-vincit/slot2
UEFI GRUB2 bootkit that installs a pre-boot networked implant via NVRAM boot option, chainloads a UKI, executes a dracut payload, and kexecs the…
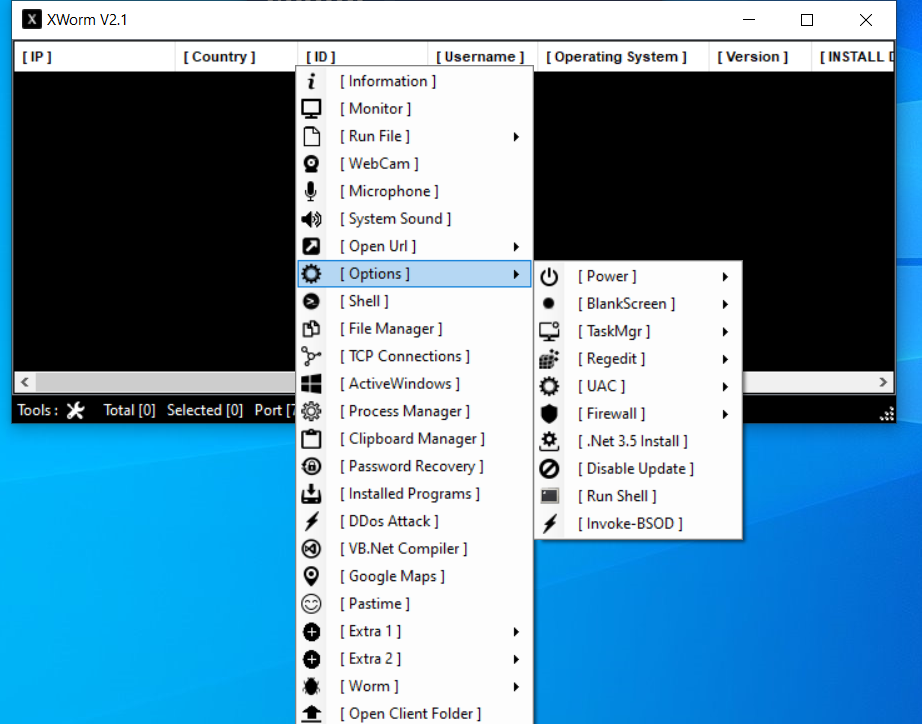
 manturever/xworm-rat
⭐️The famous XWorm RAT, version 2.1. Educational purposes only
 mwsrc/plasmarat
Remote Access Trojan(RAT), Miner, DDoS
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 malwares/remote-access-trojan
Windows Remote-Access-Trojan
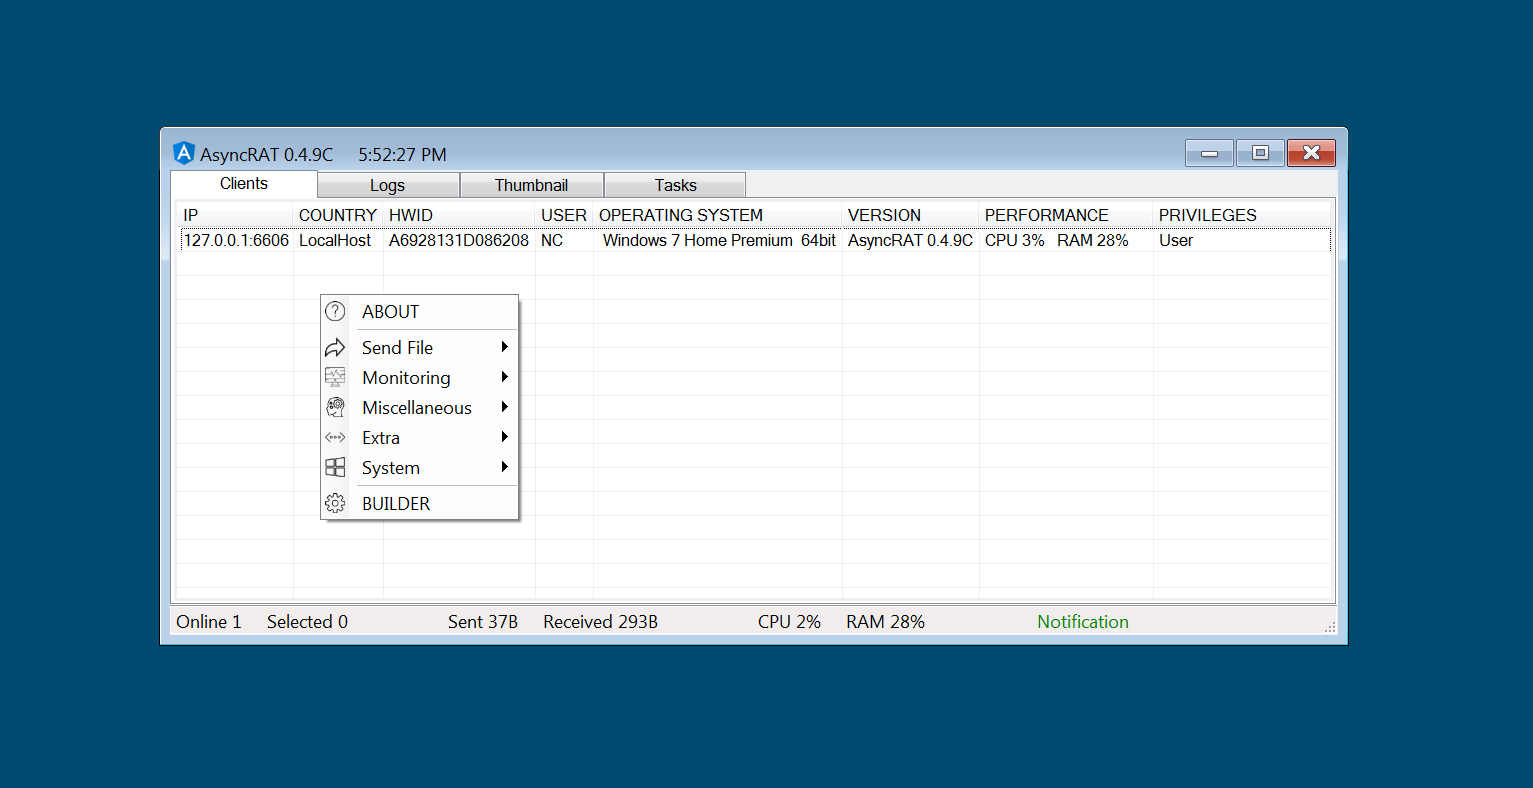 nyan-x-cat/asyncrat-c-sharp
Open-Source Remote Administration Tool For Windows C# (RAT)
 sp00kyskelet0n/discordrat
Discord Remote Administration Tool fully written in Python3