
pinky
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
command-and-controlencryption-decryption-toolspayload-generation+6
davidtavarez/pinkypinky - The PHP mini RAT (Remote Administration Tool)
 aiminsun/cve-2021-36260
command injection vulnerability in the web server of some Hikvision product. Due to the insufficient input validation, attacker can exploit the…
 jagg3rsec/cve-2014-6287
Exploit implementation for CVE-2014-6287, targeting a remote code execution vulnerability in a web application. Provides a proof-of-concept for…
 daedalus/cve-2021-30461
Proof-of-concept exploit for CVE-2021-30461, a remote code execution vulnerability in VoIPMonitor web interface. Demonstrates unauthenticated RCE via…
 e11i0t4lders0n/cve-2023-36845
Shell-based scanner for CVE-2023-36845, an unauthenticated remote code execution vulnerability in Juniper J-Web, enabling environment variable…
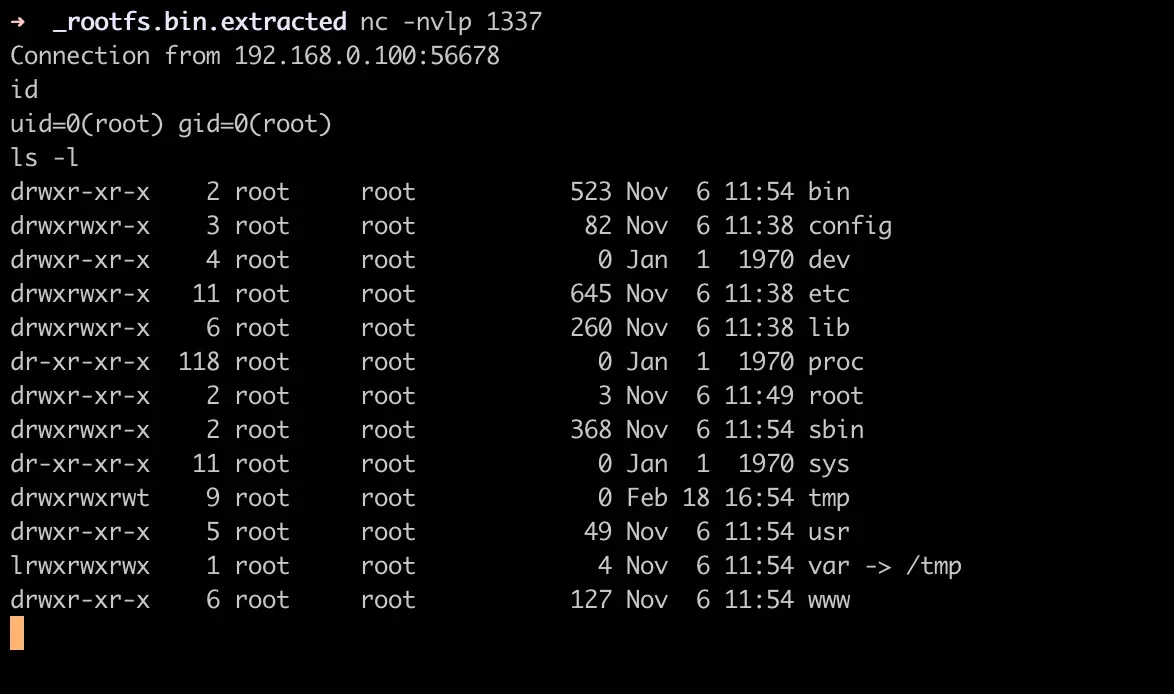 ii4gsp/cve-2026-1457
Provides a detailed analysis and proof-of-concept for CVE-2026-1457, an authenticated buffer overflow in TP-Link VIGI C385 web API leading to remote…
 adibna/cve-2021-31630
This is a automation of cve-2021-31630 exploitation
 sic4rio/cve-2015-3224
Ruby on Rails Web Console Exploit (CVE-2015-3224)
 safarchand/cve-2024-25641
PoC for CVE-2024-25641 Authenticated RCE on Cacti v1.2.26
 wqfh/cve-2024-27348
CVE-2024-27348 Exploitation Toolkit: Complete RCE exploit for Apache Huge-Graph-Server vulnerability.
 emcalv/tivoli-poc
Proof-of-concept exploit for CVE-2017-1635, a use-after-free vulnerability in IBM Tivoli Monitoring's KDH web server component enabling remote code…
 xh4h/satellian-cve-2020-7980
PoC script that shows RCE vulnerability over Intellian Satellite controller
 vulnmachines/confluence-cve-2022-26134
Proof-of-concept exploit for CVE-2022-26134, an unauthenticated OGNL injection vulnerability in Atlassian Confluence Server and Data Center, allowing…
 alexander-fernandes/cve-2019-16278
A quick python exploit for the Nostromo 1.9.6 remote code execution vulnerability. Only takes in host and port of web server as required arguments.
 zeop-cybersec/apache_normalize_path
Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)
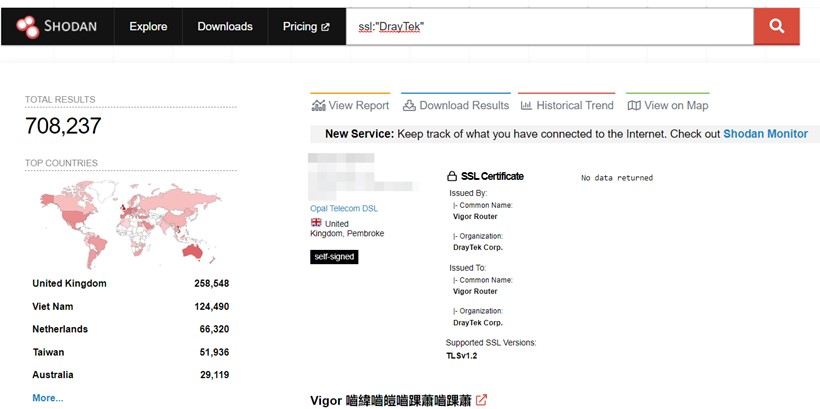 mosaedh/cve-2022-32548-rce-poc
Python-based proof-of-concept exploit for CVE-2022-32548, an unauthenticated remote code execution vulnerability in DrayTek routers via buffer…
 anubissec/cve-2019-16278
A quick python exploit for the Nostromo 1.9.6 remote code execution vulnerability. Simply takes a host and port that the web server is running on.
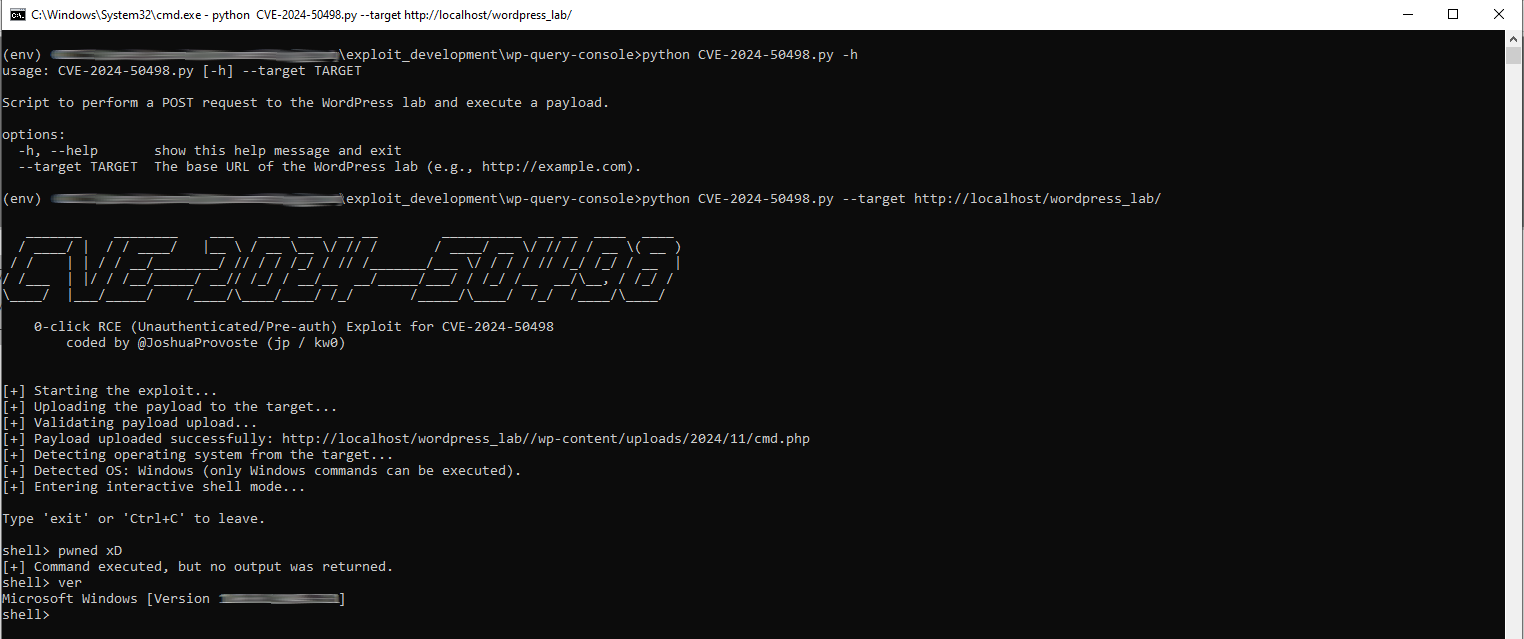 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…